Why Most Policy Docs End Up in /dev/null
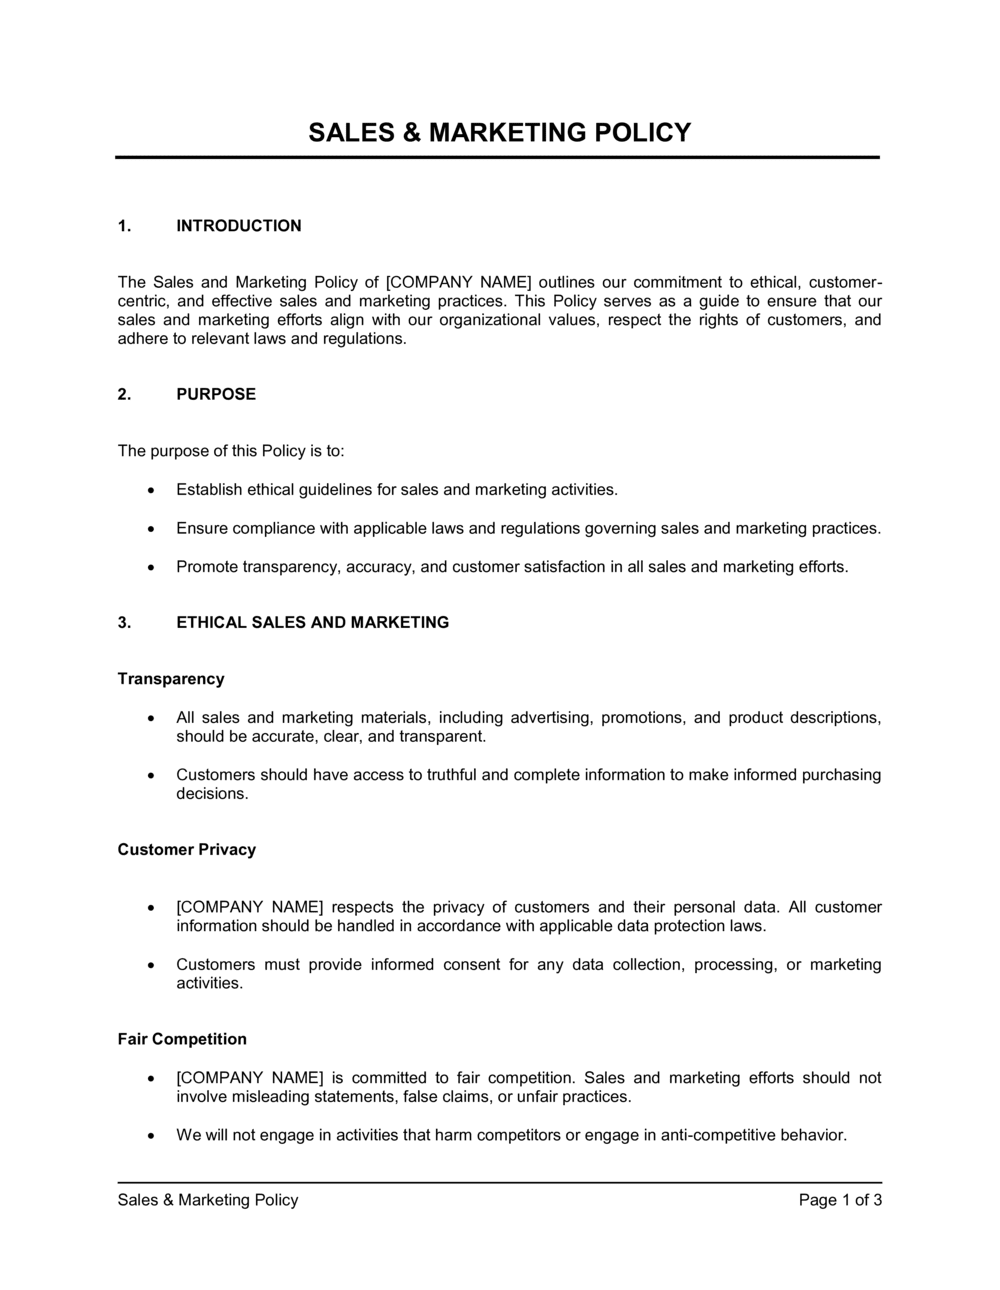
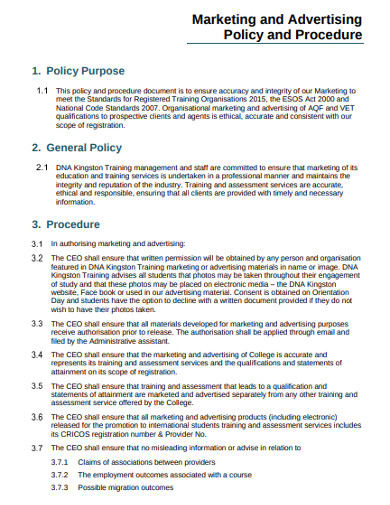
Two years ago I was brought in to clean up a marketing department that had been operating on tribal knowledge and Slack DMs. Approval workflows were non-existent. One campaign launched with unverified ROI claims because nobody knew who needed to sign off. Another ran a social media contest in violation of platform Terms of Service, which cost us a fine and a temporary platform restriction. The root issue wasn't malice. It was that nobody had ever written down who did what, under which circumstances, and by when. The core deliverable is a single source of truth document — usually a living wiki, Confluence space, or shared Notion database — that covers five mandatory sections: brand and tone guidelines, campaign approval workflows, compliance requirements, content publishing standards, and vendor/agency management. Everything else is optional fluff. Start with the approval workflow. This is where most teams break down. Map out three tiers. Tier 1 is low-risk, routine content — social posts, blog articles, standard email newsletters. These can go out with a single peer review. Tier 2 covers anything involving paid spend, new product announcements, partnerships, or messaging that touches regulatory territory. That requires a written sign-off from the relevant stakeholders — usually someone in legal, finance, or the C-suite depending on spend thresholds. Tier 3 is emergency or time-sensitive content that bypasses the full chain. Define the trigger conditions explicitly. Without them, everyone defaults to either paralysis or recklessness.
The compliance section should address GDPR for European audiences, FTC endorsement guidelines for influencer and affiliate content, CAN-SPAM for email, CCPA if you operate in California, and platform-specific policies for Meta, Google, TikTok, and LinkedIn. Do not just paste the policy links into your document. Translate them into checklists. A checklist is something you can actually follow. A link is something you can conveniently ignore when you are in a rush. I ran into a specific problem last year that illustrates why the translation matters. Our legal team flagged that one of our affiliate marketing partners was making income claims in their promotional material that violated FTC disclosure rules. The original policy document simply said "ensure influencer content complies with FTC guidelines." That was useless during a crisis. What actually worked was a one-page quick reference card that listed the exact FTC requirements — clear disclosure placement, dollar figure restrictions, material connection statements — formatted as a before-publishing checklist. I made the card fillable as a PDF so influencers could literally tick off each item before submitting their asset. It cut the back-and-forth review time from an average of three days to about four hours. Version control is another area where people fail repeatedly. Your procedures need a revision log at the top, or better yet, a linked change history section. Each update should record the date, the person who authorized it, and a brief summary of what changed. When someone inevitably asks why a campaign was rejected six months after the fact, you need to be able to say "this was approved under version 3.2, and version 4.0 added a new compliance requirement on October 12th." Without that trail, you are relying on memory, and memory is not a defensible position in any audit.
There is a tradeoff most teams ignore. The more comprehensive your policy document becomes, the less likely anyone is to read it. I have seen documents reach 80 pages. Nobody reads 80 pages. The solution is a tiered approach. Keep the full document for completeness and compliance audits. Create a separate one-page quick-start guide that covers the decisions a marketer actually makes on a daily basis — who to CC on an approval request, where to submit assets, which form to fill out for paid media, what the escalation path looks like. The quick-start guide gets distributed on day one of onboarding. The full document sits behind a link in the onboarding welcome email for people who want the details. Another counter-intuitive point: approval workflows should include default timeouts. If a stakeholder does not respond within a defined window — 24 hours for Tier 2, 4 hours for Tier 3 emergencies — the content auto-approves and moves forward. I know this feels risky, but consider the alternative. A campaign that misses its launch window because someone never clicked approve costs more revenue than the marginal risk of an unreviewed post. Set the timeout, document it in your policy, and communicate it clearly to all stakeholders. You will get pushback initially, but the team usually adapts once they see the campaigns launching on schedule again. Training and sign-off are mandatory, not optional. Every team member and agency partner needs to acknowledge they have read the current version. Use a simple acknowledgment system — a shared doc with a dated signature, or a form submission. Without documented acknowledgment, your policy document has no enforceability. During an audit or legal review, the question will always be "did they know the rules?" A signed acknowledgment answers that directly.
Get the Full Details
Here are the parts that do not work. Policy documents that live on a personal computer instead of a centralized platform. Workflows that require more approvals than there are working hours in a day. Templates that are impossible to customize without legal involvement. If your process requires someone to manually create a unique document for every single campaign variant, you are doing it wrong. Build reusable templates with conditional logic. A standard email template should handle 90 percent of use cases. The remaining 10 percent — special promotions, regulated products, cross-border campaigns — get flagged for manual review in the policy itself. For teams starting from zero, the minimum viable deliverable is this: a single shared page containing the approval matrix (Tier 1/2/3 with stakeholder assignments), a one-page compliance quick-reference card, a revision log, and a link to the acknowledgment form. Get that live before you write anything else. The other sections can be added iteratively as real gaps surface in your operations. Most teams skip straight to writing brand voice guidelines because those feel important and visible. They are not. They are decorative until your team understands who approves what, and under which circumstances. A downloadable template exists as a starting point for teams that want something more structured than a blank page. It includes the tiered approval matrix, the compliance checklist format, and the quick-reference card layout described above. Download the template here.
When to Scrap Your Policy Document Entirely
Small teams under five marketers sometimes waste weeks building elaborate systems that create more friction than they remove. In those cases, a lightweight procedure is better than nothing. A shared spreadsheet with columns for campaign name, owner, tier, approvers, status, and deadline serves the same function as a formal policy document for a small operation. The moment your team grows past five, or you begin running campaigns in multiple jurisdictions with different regulatory requirements, the spreadsheet collapses and you need the full system. The practical metric for whether your current setup is working is simple. If a new team member can publish their first piece of content within 48 hours without asking a senior person for clarification on who approved it, your system is functioning. If they cannot, you have a gap in the documentation or the training, not a gap in the individual's competence. Review the entire policy document quarterly. Any section that has not been referenced or updated in six months is a candidate for removal or consolidation. Dead policy text is worse than no policy text because it creates false confidence that everything is covered when half of it is irrelevant.