Why Most People Do Risk Matrices Wrong
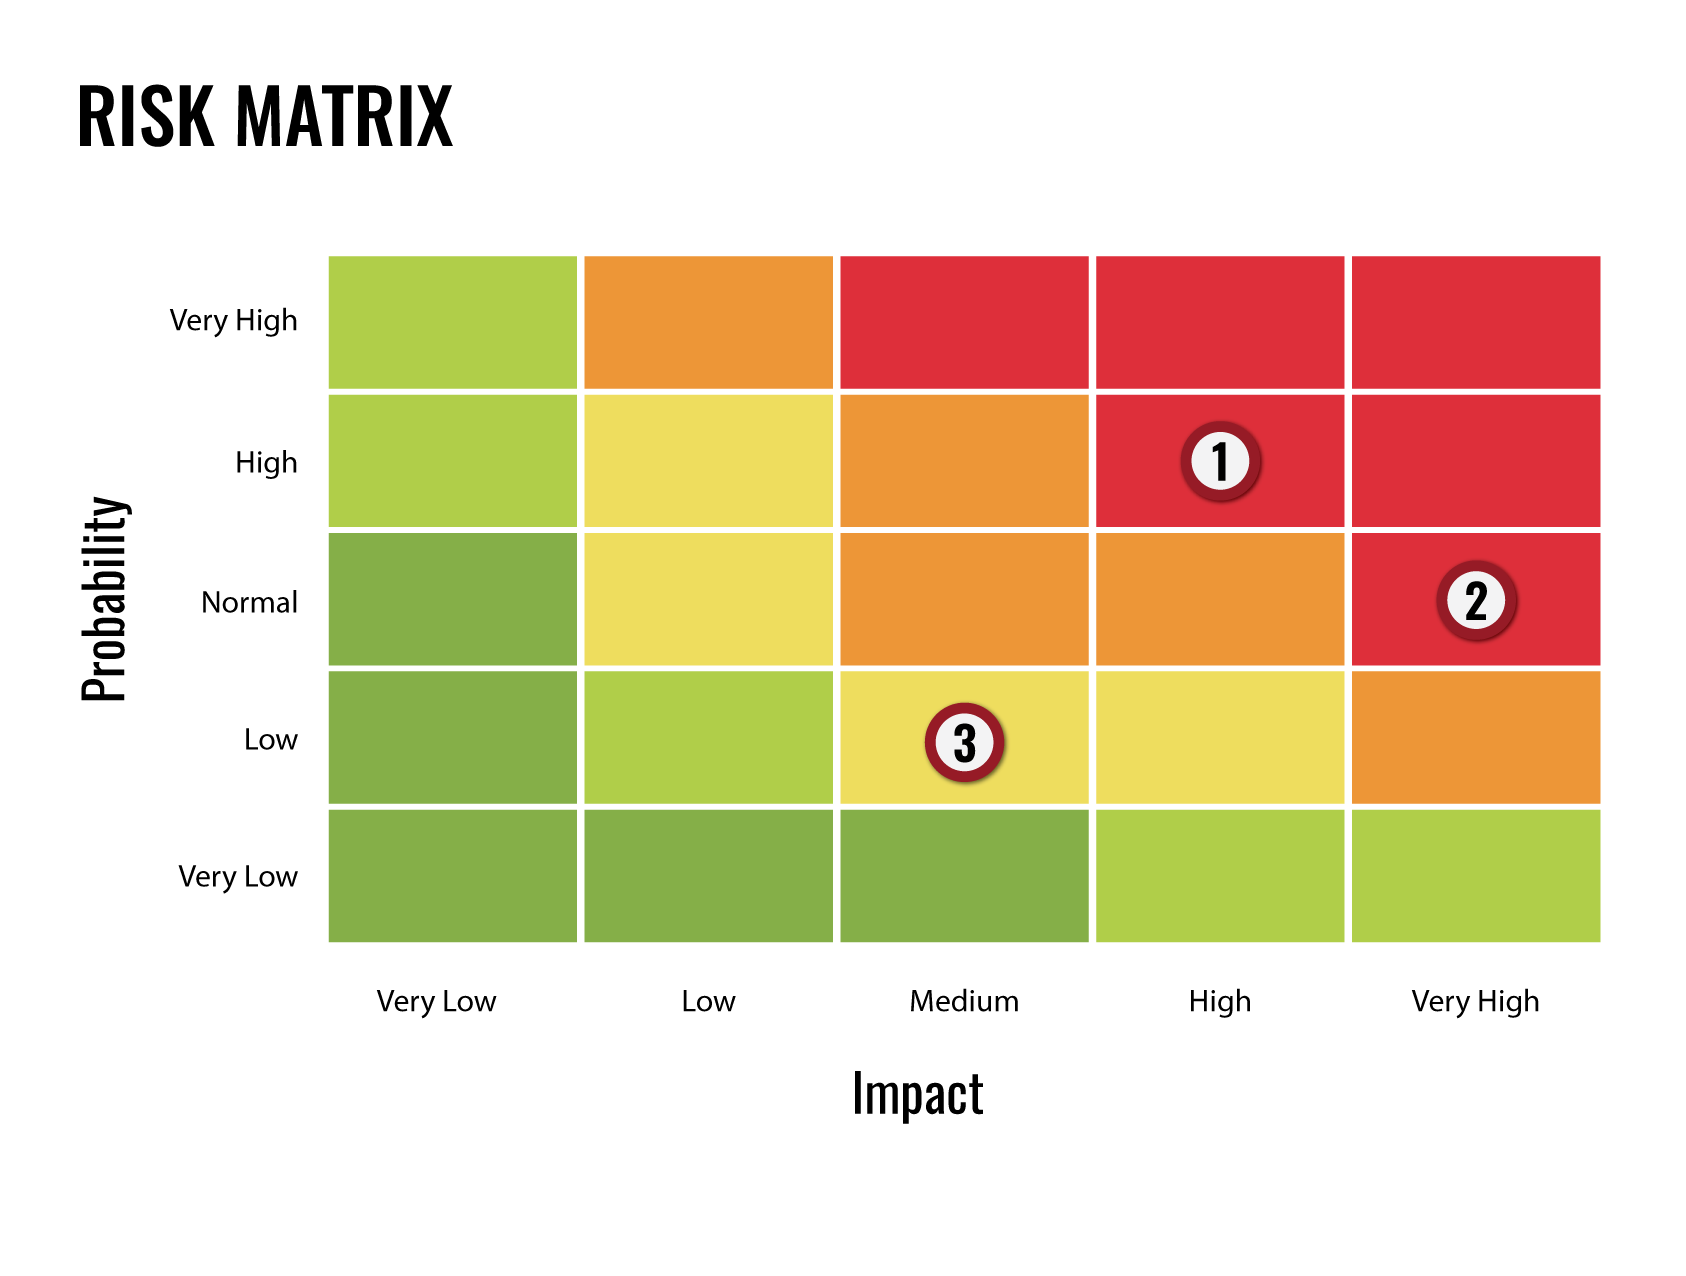
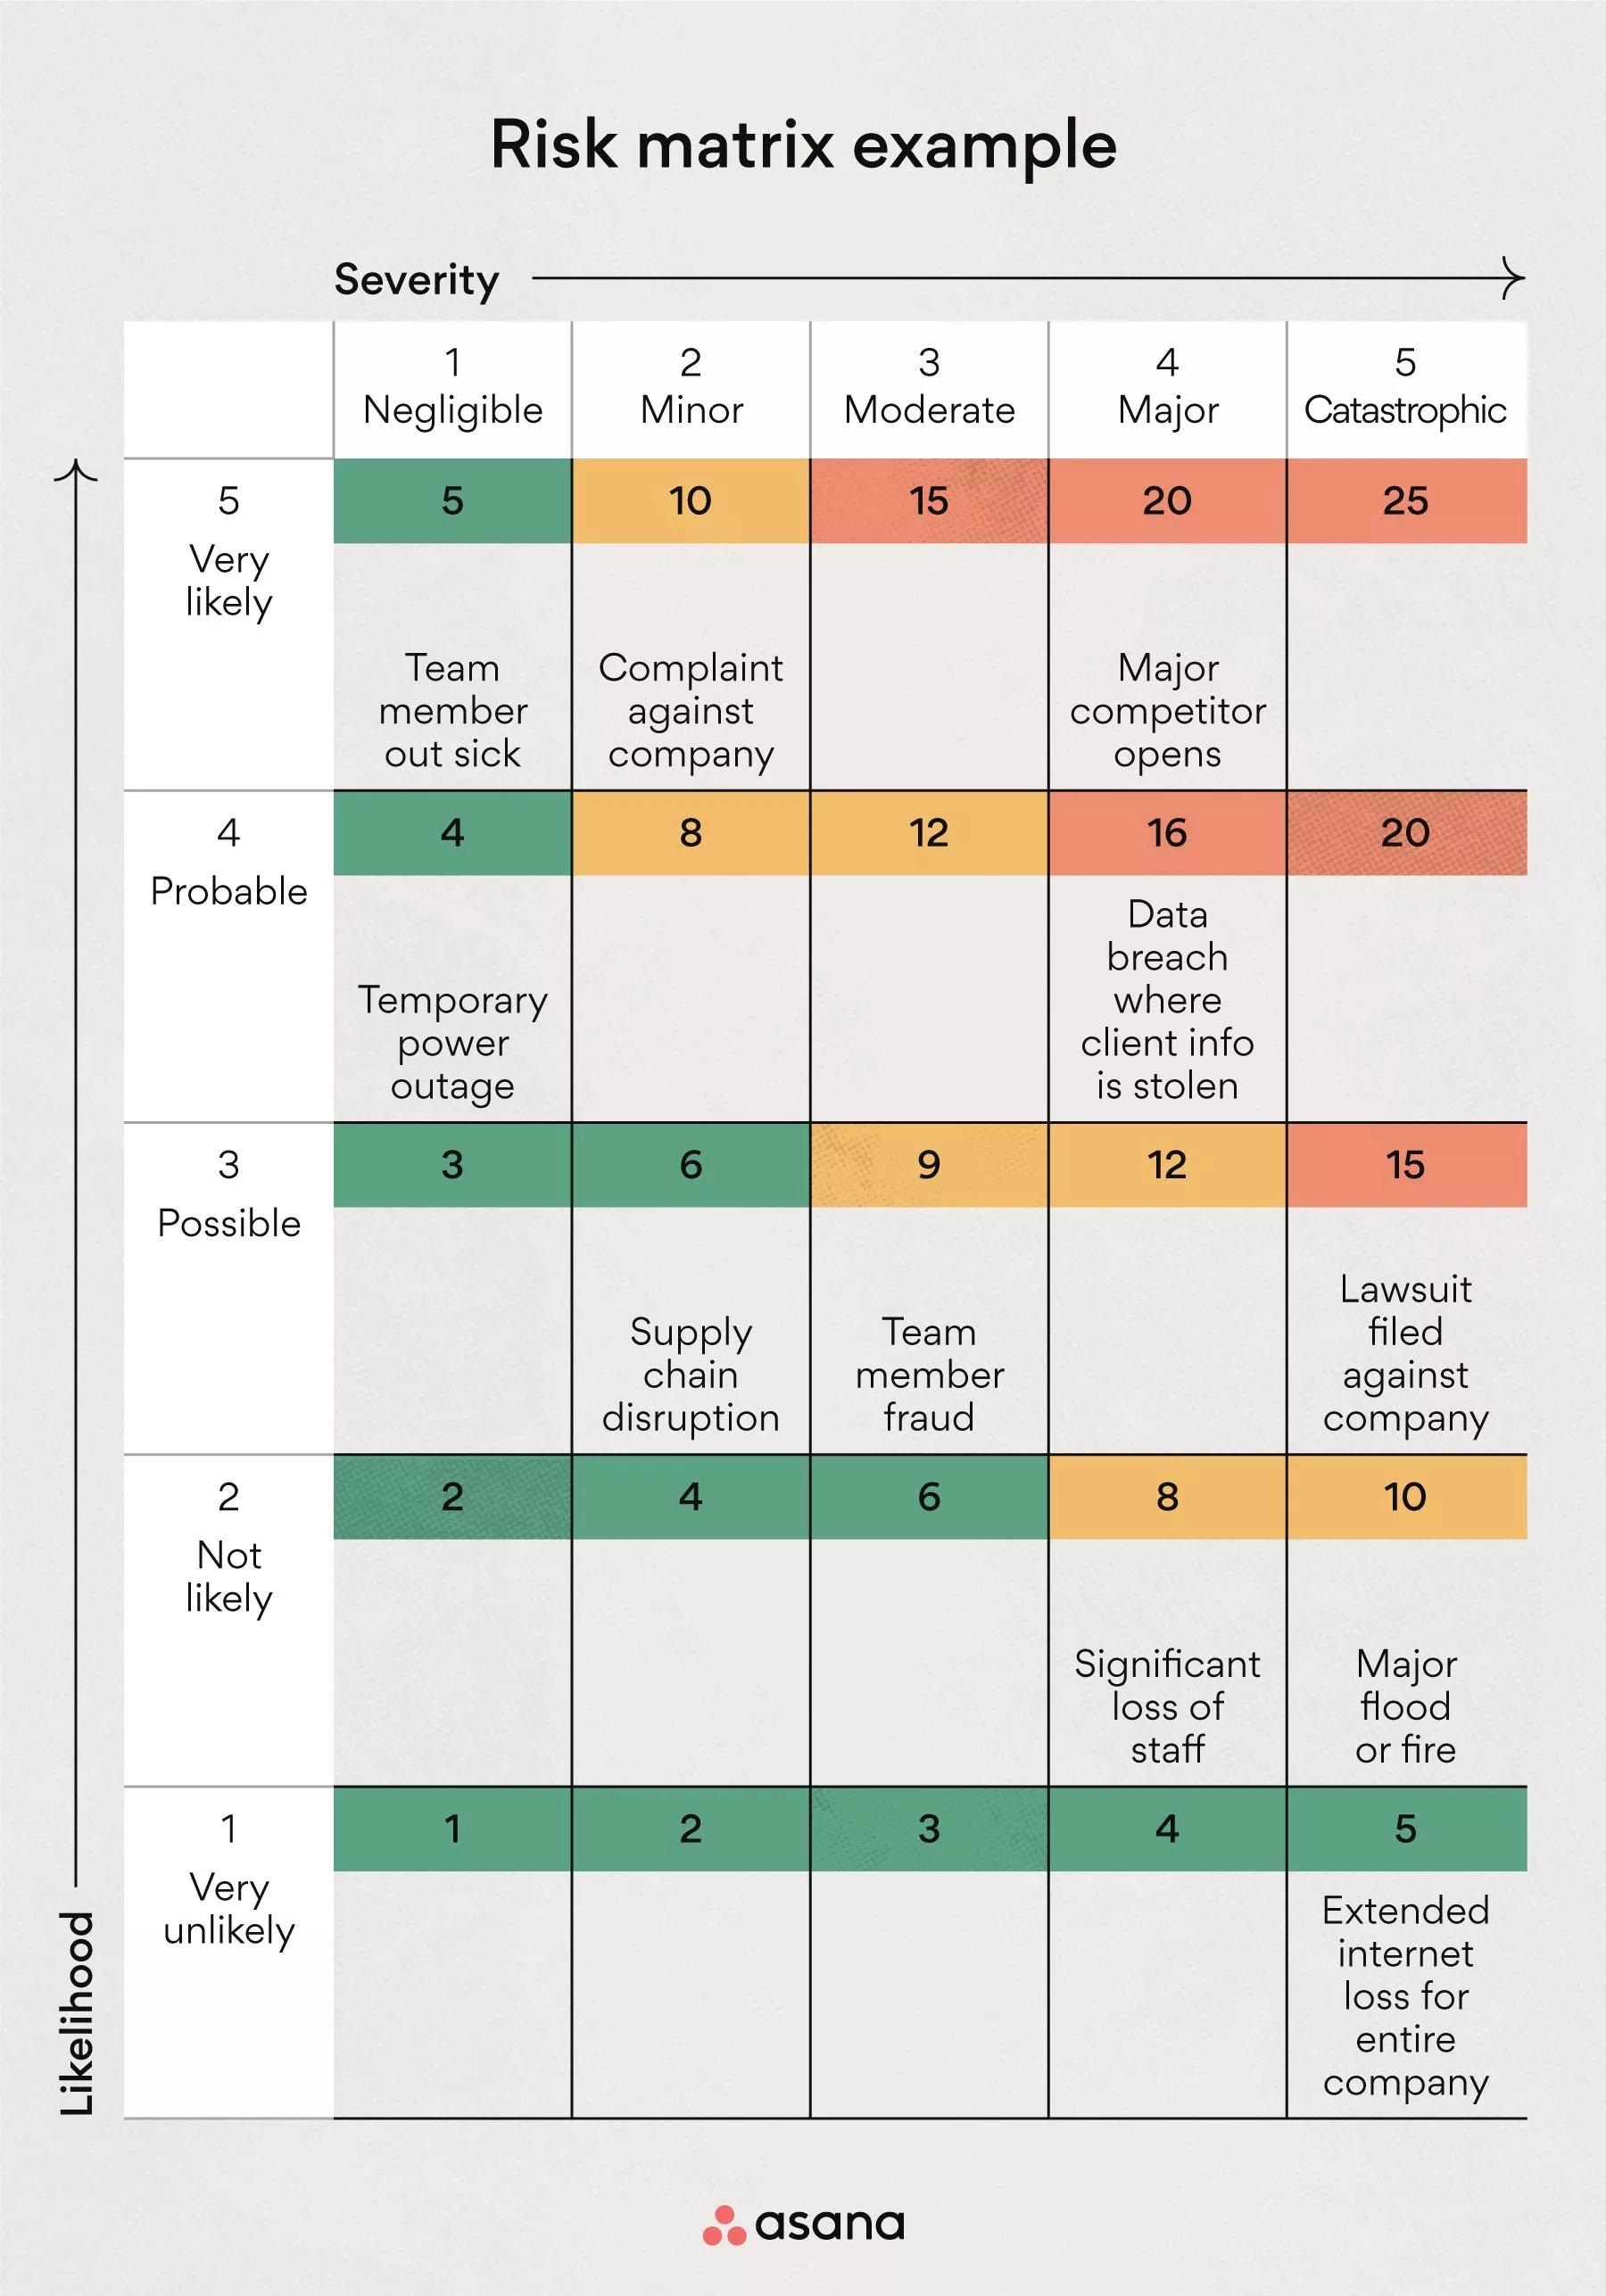
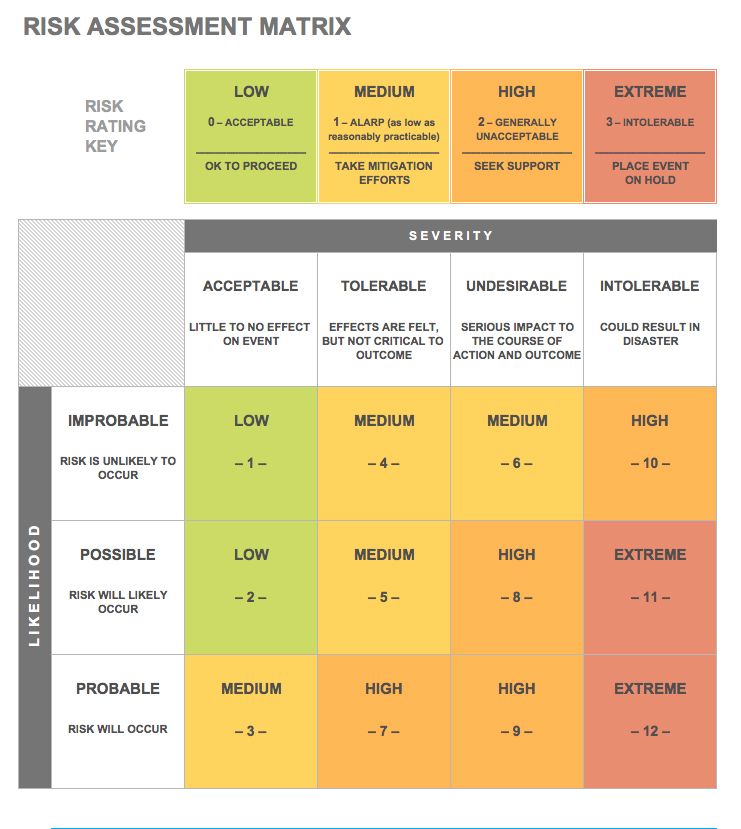
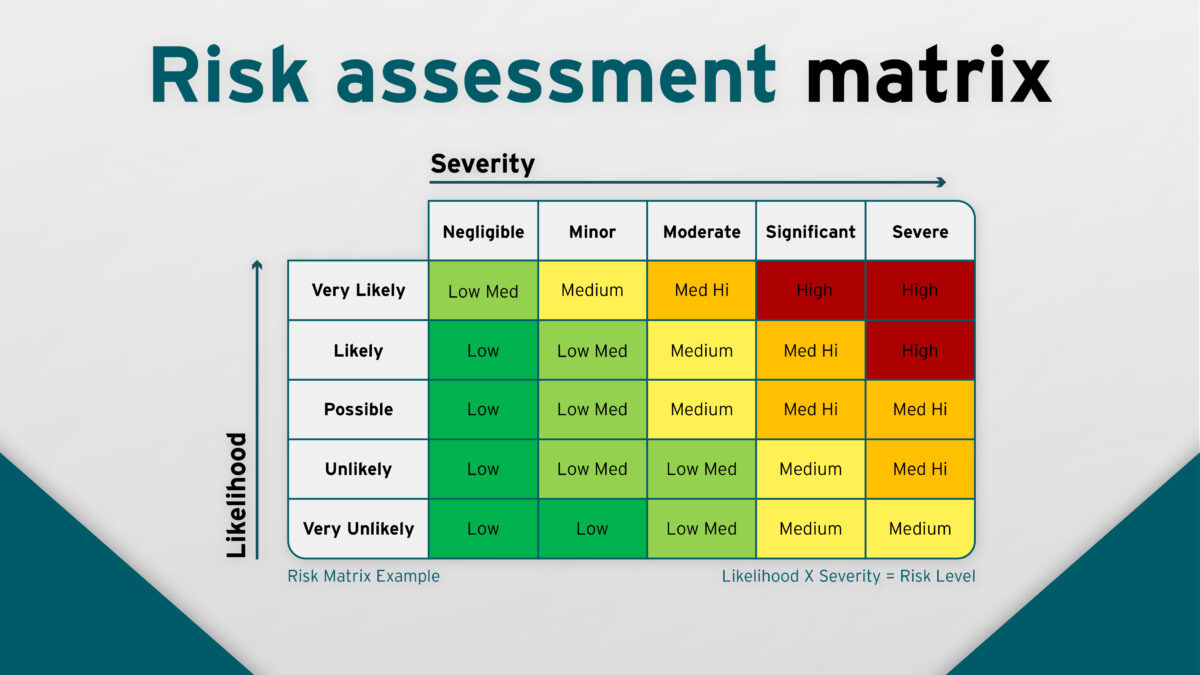
Most teams build risk matrices as if they are solving a homework problem. You list the risks, assign them numbers, and move on. That works until someone actually reads the output and realizes the matrix told them nothing they didn't already know. I spent several years dealing with this on infrastructure projects where the risk register became this thing that lived in a shared spreadsheet nobody opened after the first sprint. The actual method is straightforward. You take each identified risk and score it against two axes: likelihood of occurrence and severity of impact. The intersection gives you a risk priority number. In practice, people use 5x5 matrices because they look nice on dashboards, not because five levels of granularity actually adds signal. A 3x3 matrix with honest calibration often beats a 5x5 where every risk lands in the yellow zone.
Matrix Risk Assessment in Practice
Here is how I actually run a Matrix Risk Assessment without wasting three days of stakeholder time. First, you define the scales before you identify any risks. This is the part everyone skips. You write out what "Likelihood 4" actually means in operational terms. Is it monthly? Quarterly? Something that happened once in the last two years at a peer org? Without concrete anchors, different reviewers will score the same risk as a 2 and a 5 depending on their mood that week. I keep a calibration document alongside the matrix. It lists each score level with a brief real-world example from the project's own history or industry data. When two people disagree on a rating, you reference the calibration doc instead of arguing about gut feelings. This alone reduces scoring variance from something like 40 percent down to under 15 percent across a typical review cycle. The second step is identifying risks through a structured brainstorm rather than having the project manager fill it in alone. I pull together people from operations, security, finance, and the team actually delivering the work. The person closest to the system catches things the risk officer misses every time. A vendor lock-in scenario that the PM rated low became a critical risk once the deployment engineer explained how the API versioning was handled.
After scoring, you don't just dump everything into a color-coded grid and call it done. You rank the top ten risks and build mitigation plans for those. The rest go into a watch list. I learned this the hard way when a compliance audit flagged our risk register for having "unrealistic mitigation coverage." We had 87 risks with mitigation plans attached. Half were generic text like "monitor and review." The auditor was right.
Get the Full Details

Common Pitfalls That Wreck the Process
The biggest mistake is treating the matrix as a one-time exercise. Risks shift. A likelihood 3 risk from six months ago might be a likelihood 1 now because you implemented a control, or it might have become a likelihood 4 because a key dependency changed. I recommend a formal reassessment at each major milestone plus a quick quarterly review where someone updates the scores without rebuilding the whole document. Another issue is correlation blindness. Most matrices assume risks are independent. They rarely are. When you have a supply chain disruption and a regulatory change happening in the same quarter, the impact isn't additive, it is multiplicative. The matrix will show you two medium risks side by side and miss the compound effect entirely. I handle this by adding a separate section for correlated risk scenarios where I manually combine dependent risks and score them as a group. It takes extra time but it catches the stuff that actually keeps people up at night. There is also the averaging trap. When you aggregate risk scores across a portfolio, medium risks can cancel each other out and produce a deceptively low overall number. A portfolio showing an average risk score of 6 out of 25 might look healthy until you realize it contains three risks that are individually catastrophic. I always present both the aggregate view and the worst-case individual risks. The aggregate number is for steering committees. The worst-case list is for the people who actually have to respond when things go wrong.
Tools and Templates
You do not need expensive software for this. A well-structured spreadsheet with conditional formatting works fine for teams under fifty active risks. The moment you cross that threshold, you start needing features like version history, role-based editing, and integration with your issue tracking system. In that case, tools like RiskCloud, Diligent HighBond, or even a configured instance of Jira with custom fields can handle it. If you want a starting template, the Project Management Institute publishes a risk register template that pairs well with a 5x5 matrix layout. It is free and you can adapt it. For the calibration document I mentioned, I build a simple table in the same sheet with columns for score level, definition, and example. Keeping it in the same file as the matrix reduces the chance someone updates one and forgets the other. One more thing. If your organization still does Matrix Risk Assessment using paper forms or emailed PDFs, you are not doing risk management, you are doing risk theater. The framework only works when the data is current and accessible. Everything else is just paperwork that looks like governance.