How the Medical Device Risk Analysis Template Actually Works
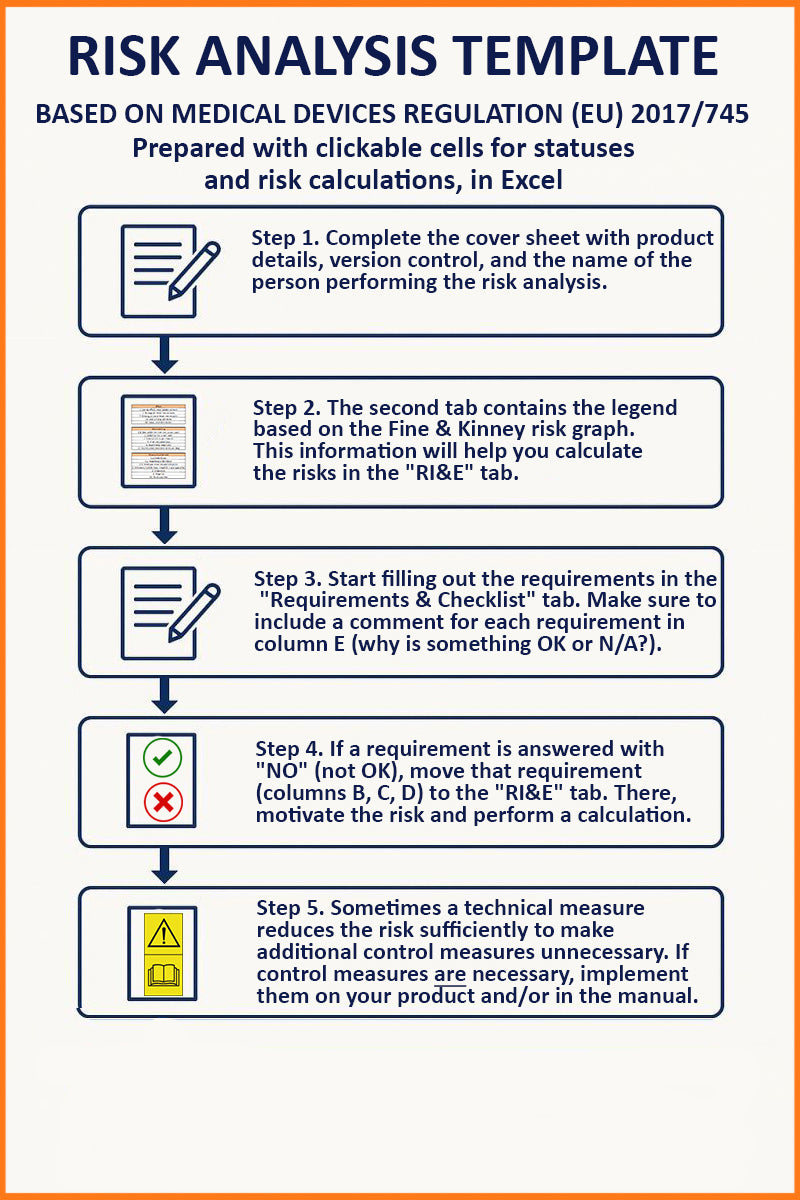
I used to build risk analyses from scratch for every project. Took two weeks minimum. Now I have a structured template that cuts that down to a day, sometimes less. The trick isn't finding a perfect template online — it's knowing how to adapt one so it doesn't just check boxes but actually survives a regulatory review. A Medical Device Risk Analysis Template is essentially a structured worksheet or document framework built around ISO 14971 requirements. It gives you fields for hazard identification, fault trees, severity and probability ratings, risk control measures, and residual risk acceptance decisions. Some templates are basic Excel sheets. Others are more sophisticated systems with built-in formulas for risk priority numbers. The type you choose depends on your device complexity and whether you're dealing with software, hardware, or a combination.
Building Your Medical Device Risk Analysis Template
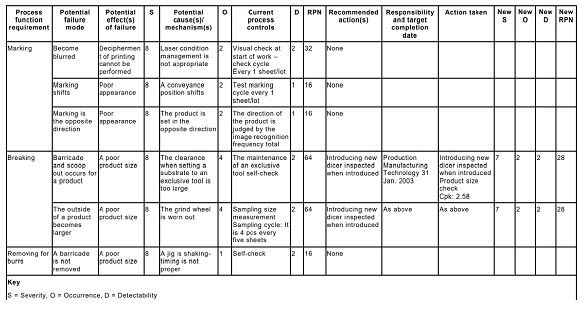
Start with the hazard analysis section. This is where most people go wrong. They jump straight into FMEA tables without first documenting what the device is supposed to do and how it can fail to do it. Write out a functional block diagram. Map each function to its potential failure modes before you open any risk matrix. Here's a problem I ran into recently that most templates don't address well. I was working on a pump controller that had a default safety state — if power was lost, the pump would automatically stop and close a valve. The initial template structure made me rate this as a single failure point with binary outcomes. But in practice, the valve could fail open or fail closed depending on spring orientation and actuator type. That distinction changed the severity rating from moderate to high for certain patient populations. My workaround was to add a subcategory field in the template for multiple failure states per hazard, with separate severity assessments for each. It took about ten extra minutes per row but prevented me from underestimating risk in the documentation. The next section covers risk estimation. You need columns for severity, occurrence probability, and detectability. Most organizations use a 5x5 matrix. I've seen simpler 3x3 ones that work fine for low-risk devices. The matrix determines whether a risk is acceptable, ALARP, or unacceptable. What most beginners miss is that detectability isn't about the device detecting its own failure — it's about whether the operator or another system can identify the hazardous situation before harm occurs. A ventricular assist device might have a sensor that detects clot formation, but if that sensor fails silently, the detectability rating drops significantly even though the device has monitoring built in.
After estimation comes risk control. This is where the template structure matters most. Every risk control measure needs a column for the measure itself, the standard or reference it satisfies, and verification evidence. I always add a residual risk re-evaluation column because reducing one risk often introduces another. Insulation on a power cable might prevent electric shock but create a thermal hazard if it melts under load. Here's something people rarely get right initially: the link between your risk analysis and your verification validation plan. Every risk control measure in your template should trace directly to a test or analysis that proves it works. If you can't write a test case for a control measure, it probably isn't a real control measure — it's just hope. I've seen templates with fifty risk controls and only twelve corresponding verification records. That gap is a major audit finding. For software-based devices, the template should include a separate section for software hazard analysis using standards like IEC 62304. Hardware and software risks interact in ways that don't show up in a flat table. A sensor reading error might be caught by hardware watchdogs, or it might propagate through firmware and produce incorrect pump commands before anyone notices.
Get the Full Details

Another thing worth noting about templates — they are never complete on the first pass. My typical process runs like this: draft the full template in three days, spend five days reviewing it with engineering, find gaps in hazard coverage, revise, then spend a week doing the actual analysis work. The template evolves as the analysis reveals new failure modes you hadn't considered. Don't treat it as a static form. If your template stops changing after the first version, you're probably not looking hard enough at the failure modes.
When Templates Fall Short
There are scenarios where even a well-built template doesn't work well. Complex system-level interactions between multiple devices or between a device and its environment are hard to capture in a row-based format. I once had a case where a patient monitoring device and an infusion pump were both in use, and a network failure caused both to enter degraded states simultaneously. The combined effect wasn't captured in either device's individual risk analysis. For that situation, I added a system integration risk section that documented cross-device interaction hazards separately from the product-level template. Another limitation: templates tend to encourage over-reliance on historical data for probability ratings. I've seen teams copy occurrence probability values from similar devices without justification. If your device operates in a different clinical environment or has different user demographics, the failure rates from the literature won't apply directly. It's better to justify probability estimates with your own data, even if that data comes from accelerated life testing or component failure rate calculations like MIL-HDBK-217 or FIDES. A properly sourced estimate rated at 1 in 100,000 is worth more than a copied estimate with the same number. If you need a starting point, search for templates aligned to ISO 14971:2019 specifically, not the older 2007 version. The 2019 revision added requirements for post-production data feedback loops and more explicit treatment of software hazards. Many free templates online are still based on the old standard and will miss sections that auditors now expect to see. Pay attention to whether your template includes a field for collecting and reviewing post-market surveillance data — that's a common gap in older templates and a recurring audit observation in recent years.
The template is a tool, not a solution. It organizes your thinking and creates an audit trail, but the quality of your risk analysis depends entirely on how thoroughly you identify hazards and how honestly you assess their likelihood and impact. No template will make up for superficial analysis.