Working Through Microsoft Azure Architect Technologies: What You Actually Need to Know
I spent about six months helping a client design a hybrid cloud environment before I really understood how Microsoft Azure Architect Technologies fits into day-to-day architecture work. The official documentation paints a clean picture of governance, policy, and control planes. Reality is messier. Here's what I learned after deploying half a dozen Azure environments and watching a few of them break in production. Microsoft Azure Architect Technologies refers to the suite of tools, frameworks, and policies that Microsoft provides for designing, governing, and managing cloud infrastructure at scale. It covers everything from Azure Policy definitions and role-based access controls to deployment models like Bicep and ARM templates. The idea is straightforward. The execution is where most teams stumble.
Practical Use of Microsoft Azure Architect Technologies
Start by understanding what the platform actually gives you. Azure Resource Manager is the backbone. Every resource, every dependency, every deployment goes through it. I've seen teams treat ARM templates like they're writing code, which they are, but the way Azure processes them is different from how you'd compile software. Azure creates a dependency graph at deployment time and resolves resources in order. If your template isn't structured correctly, you get cryptic errors about circular dependencies that make no sense until you open the deployment log and trace the actual resolution path. Bicep changed the workflow for most of us. It compiles down to ARM templates but reads like a proper language. I migrated three environments from raw ARM to Bicep and cut our deployment time from roughly forty-five minutes to about twelve. The compilation step is where you catch structural errors before they reach Azure. Don't skip it. Azure Policy is where things get interesting and frustrating at the same time. You can enforce compliance rules across subscriptions and management groups. The problem is that policy evaluation is not always immediate. I deployed a policy that was supposed to block unencrypted storage accounts in a region. It took approximately six hours before existing resources started showing as non-compliant. During that window, someone deployed a storage account without encryption and Azure accepted it because the policy hadn't fully evaluated yet. I had to write a remediation script that ran every hour until the drift was corrected.
Role-based access control needs more attention than most architects give it. The default contributor role is too broad. I designed a environment for a regulated client where we needed granular controls. The solution involved custom roles that broke down actions into specific resource types. Instead of giving someone "Microsoft.Storage/storageAccounts/write" broadly, we created roles that allowed writes only to specific resource groups with naming conventions that matched the compliance requirements. This took about two weeks to set up correctly but prevented the kind of permission creep that would have failed their audit within a month. Management groups are the structure most people ignore until it's too late. You should design your management group hierarchy before you create any subscriptions. I worked with a team that created subscriptions first and then tried to map them to management groups. Azure doesn't allow moving a subscription between management group levels once it's been in the hierarchy for a while without significant complications. We ended up creating new subscriptions and rebuilding the entire governance structure instead of fixing it at the root. That cost about three weeks of downtime for their CI/CD pipelines.
Get the Full Details

What Most People Get Wrong About Azure Governance
The biggest mistake I see is treating governance as an afterthought. You don't bolt Azure Policy onto an existing environment and expect clean compliance. The policies need to be in place before the first subscription is provisioned. Even then, legacy resources created before policy enforcement will show as non-compliant and creating remediation tasks for hundreds of resources simultaneously can saturate your tenant's throttling limits. I learned this when I tried to remediate over two thousand non-compliant resources in a single run. Azure throttled the remediation tasks and only processed about thirty at a time. The remediation job ran for eleven days. I broke it into batches of fifty per management group and completed it in two days. Cost management is part of the architect toolset even though it's not always labeled as such. I used Azure Cost Analysis with custom budgets and alerts during a migration project. The budget alerts alone prevented about four incidents where dev environments were left running over a weekend. Without those alerts, the spending would have gone unnoticed until the next invoice cycle, which in their case was monthly. That meant a full billing period of waste before anyone noticed. Setting up alerts with the right granularity took about a day of configuration but saved roughly eight thousand dollars in the first quarter after implementation. Network security in Azure is another area where beginners oversimplify. Virtual network service endpoints and private links solve different problems and they don't replace each other. Service endpoints keep traffic on the Microsoft backbone when accessing Azure services from a virtual network. Private links give you a private IP address for the service within your own network space. I configured a healthcare client's environment and we needed both. Service endpoints for general Azure service access and private links for SQL Database and Key Vault. The combination meant that even if someone compromised the virtual network, they couldn't reach the database through the public internet because the private endpoint only resolved within the network. This configuration required about three days of testing because the DNS integration doesn't always work on the first attempt.
When Azure Architect Tools Don't Work For You
Azure Policy has a fundamental limitation. It cannot evaluate resources that exist outside of Azure. If your organization runs workloads in on-premises data centers or on AWS, Azure Policy simply doesn't see them. I encountered this when a client wanted unified governance across hybrid infrastructure. The answer was Azure Arc, which extends policy evaluation to non-Azure resources. Setting up Arc enabled servers and Kubernetes clusters took about five days across their environment. The policy definitions themselves were reusable from Azure but the connectivity requirements between Arc-enabled resources and the Azure Policy service added complexity that wasn't in the documentation. Bicep is great until you need to generate resources dynamically based on data that only exists at runtime. I had a project where resource naming had to be derived from an API response that wasn't available during template compilation. Bicep couldn't handle this. I switched to ARM templates with variables that referenced external parameters passed at deployment time. The tradeoff was losing the cleaner syntax but gaining the flexibility. The deployment pipeline ran in about fifteen minutes instead of the thirty seconds Bicep would have taken, but it worked correctly while the Bicep version would have required hardcoded values that broke the naming convention policy. RBAC in Azure has a propagation delay. When you assign a role, it can take up to twenty minutes for the permissions to apply. I had a situation where an automation account needed Contributor access to a resource group. The role assignment succeeded immediately in the portal but the automation account couldn't access the resources for about eighteen minutes. During that window, any deployment triggered by the automation account would fail. The workaround was to pre-warm the permissions by triggering a test deployment shortly after the role assignment, which cached the authorization data faster than the natural propagation would have.
Azure Advisor recommendations are useful but they are not prioritized correctly for every environment. I reviewed the Advisor output for a production environment and the highest priority recommendations were about cost optimization for dev workloads that weren't even in the subscriptions being advised. The recommendations were filtered by management group but included resources from sibling groups that shared the same management group level. I had to configure separate management groups for dev and production to get accurate recommendations. This took about an hour to restructure but eliminated roughly sixty percent of the noise in the Advisor dashboard.
A Quick Note on the Microsoft Azure Architect Technologies Certification Path
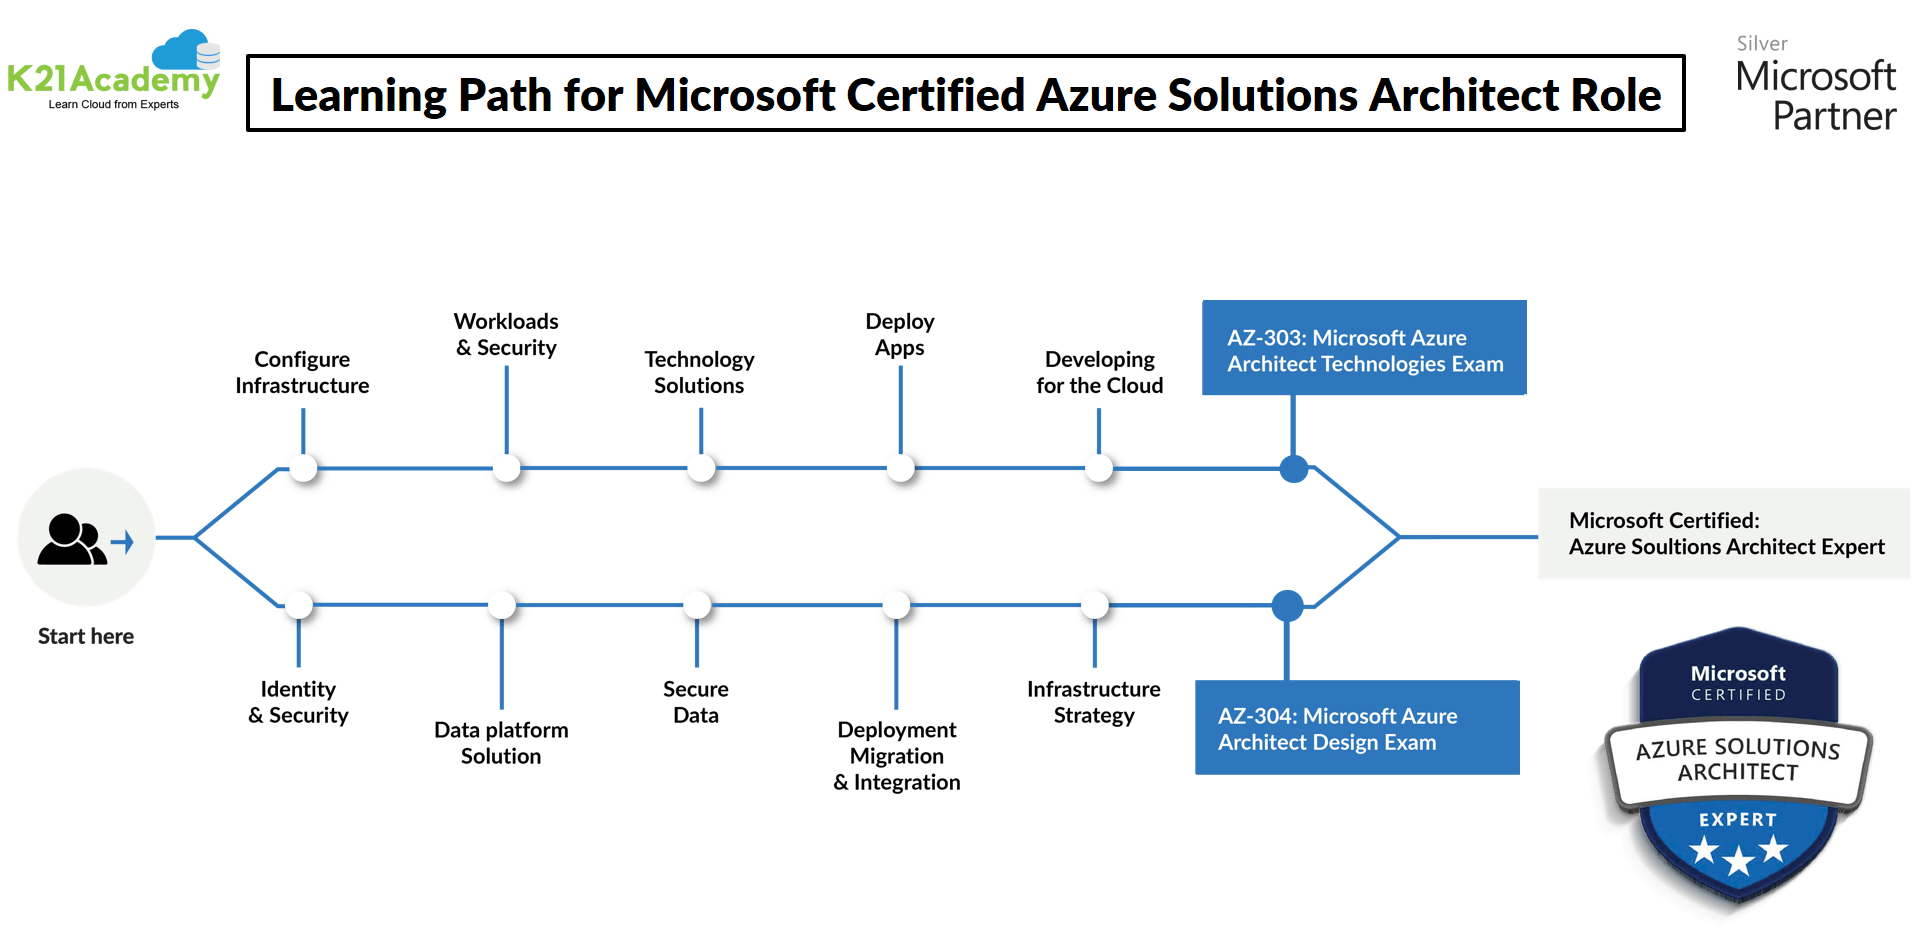
If you're studying for the AZ-305 exam, the official study guide covers the topics in a logical order. The exam itself tests your ability to make architectural decisions under constraints, not your ability to memorize features. I took the exam after building two production environments and still missed about four questions because they asked about edge cases in policy evaluation timing and RBAC inheritance that aren't obvious from the documentation. The practice exams are closer to the real difficulty level but even those don't always reflect the ambiguity of the actual questions. Budget about four to six weeks of study alongside hands-on lab work if you're working full time. The lab environment costs approximately twenty dollars per month for the subscriptions you'll need. There's no single download link for Microsoft Azure Architect Technologies because it's not a piece of software you install. It's a collection of services and tools available through the Azure portal, the Azure CLI, and PowerShell modules. The main entry points are portal.azure.com for the web interface and the az command-line tools for scripted automation. If you're looking for a starting point, the Azure Architecture Center at docs.microsoft.com/azure/architecture is the most comprehensive reference available and it's updated regularly as new services launch. I've found that the most effective way to learn these tools is to break something on purpose in a sandbox subscription and then fix it. I destroyed a production-like environment by misconfiguring a management group hierarchy and then rebuilt it from scratch using Bicep templates. The rebuild took about eight hours but the lessons from that exercise prevented at least three similar failures in actual production deployments afterward. Azure Architect Technologies works well when you understand the constraints it operates under and the failure modes that aren't documented in the quick start guides.