Why Contractors Map 800-171 to 800-53 Anyway
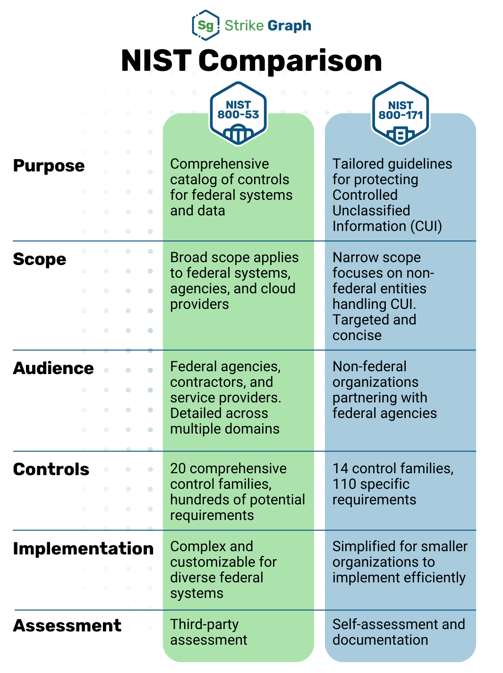
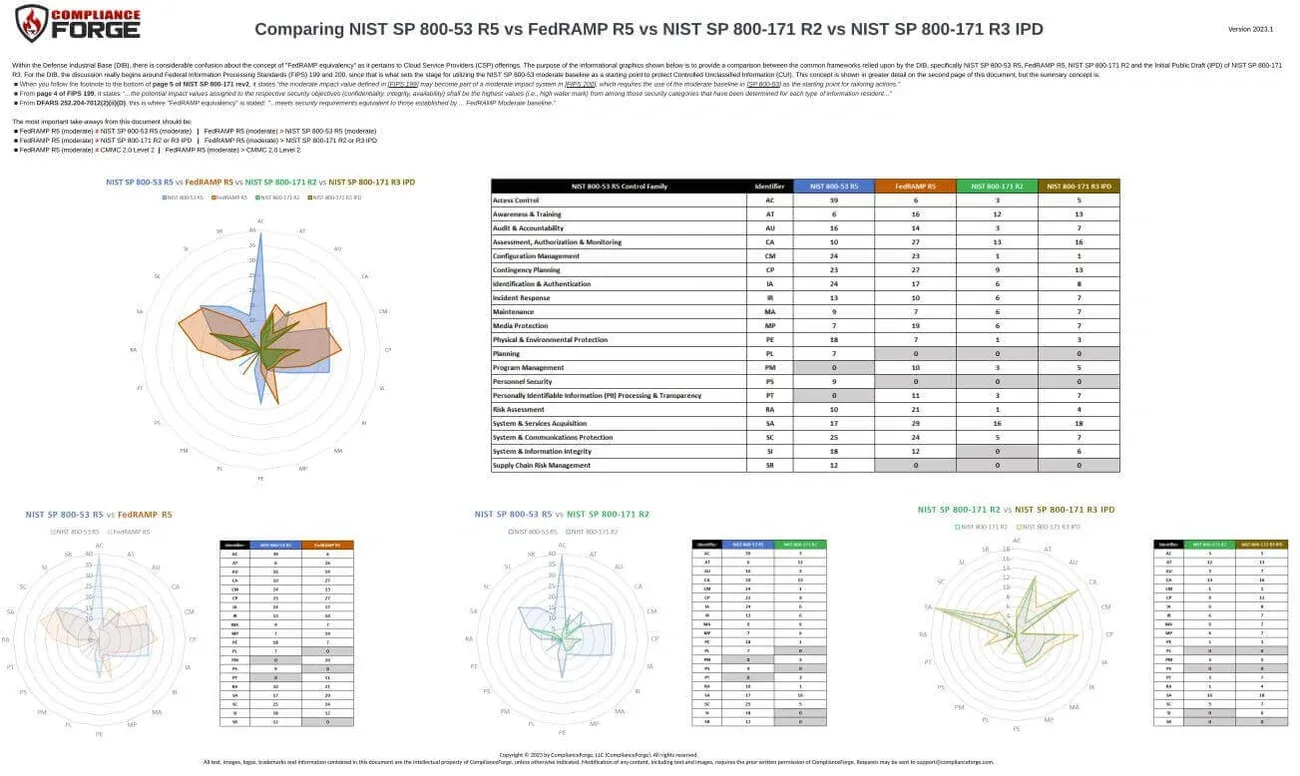
The most common reason I see organizations attempt a Nist 800 171 Mapping To 800 53 exercise is that a Defense Industrial Base contractor needs to satisfy a more mature compliance framework than 800-171 alone provides, or they are preparing for CMMC Level 3 where 800-53 families are the control baseline. Another practical driver: enterprise customers who aren't DoD ask for 800-53 compliance because they already run FedRAMP environments and find it easier to evaluate against that catalog. You start by loading both documents side by side. NIST 800-171 Revision 2 has 110 security requirements across 17 families. NIST 800-53 Revision 5 has hundreds of controls spread across twenty families. The mapping is not one-to-one. It is one-to-many, many-to-one, and occasionally nothing-to-nothing, which sounds dramatic until you hit it and waste half a day figuring out why a requirement has no match. The standard approach is to use the 800-171 requirement number as your anchor and find the closest 800-53 control family and individual control. I typically go family first. AC.1 from 800-171 maps cleanly into the 800-53 Access Control family, specifically AC-2 through AC-7. CT.1 maps to the Contingency Planning family but pulls more from the 800-53 CP-2 and CP-4 controls than anyone expects at first glance. SC.39, the one about safeguarding satellite communications, is basically orphaned in 800-53 unless you stretch it into SC-7 or SI-4 territory, and even then it is a weak fit.
Here is a practical workflow I have used for years now. Take each of the 110 800-171 requirements. Assign it to one or two primary 800-53 controls. Add a secondary note for any related controls that provide supplementary coverage. Build a mapping table with columns for the 800-171 ID, the 800-53 control ID, the control name, a gap explanation, and the implementation status in your environment. This takes roughly three to five business days for a small team that knows both documents. If someone tells you they did it in two days, they probably copied a pre-existing matrix and did not validate the mappings.
A Real Edge Case I Hit
On a recent engagement, the client needed to map 800-171 RA.3, Risk Assessment, into 800-53. The obvious choice is RA-5, Risk Monitoring. But RA.3 is actually a process obligation, not a monitoring task. It requires formal risk assessments at defined intervals and upon significant changes. RA-5 does not give you that structure. RA-1 gives you the risk assessment policy, RA-2 gives you the assessment procedure, and RA-3 itself exists in 800-53 Revision 5 but was demoted to a supplementary concern in some FedRAMP baselines. The real workaround I used was mapping RA.3 to RA-1, RA-2, and RA-3 collectively, then documenting in the gap analysis that the 800-171 requirement exceeds the baseline control's intent because 800-171 requires the organization to actually perform the assessment on schedule, while the corresponding 800-53 control focuses more on continuous monitoring after the assessment is done. That distinction matters during an audit. If you just say "RA-3 covers it," the assessor will push back, and you will look like you did not read the control language carefully. The first thing most people get wrong is assuming every 800-171 requirement has a clean 800-53 counterpart. It does not. NIST 800-171 was designed as a standalone baseline for controlled unclassified information. NIST 800-53 is a broader catalog with controls that assume federal systems, FISMA authority boundaries, and FedRAMP moderation. When you map backward, you are essentially translating from a simpler language into a denser one, and some concepts simply do not exist in the target vocabulary. The second thing people miss is that 800-171 Appendix D lists assessment objectives for each requirement. Those assessment objectives are sometimes more granular than the equivalent 800-53 control families. If you rely only on the control mapping and ignore the assessment objectives, you will under-map. I have seen teams skip this step and end up with three requirements that appeared covered but were actually missing sub-control testing. Fixing it after the fact costs about two weeks of rework.
Get the Full Details
Limitations You Should Accept Upfront
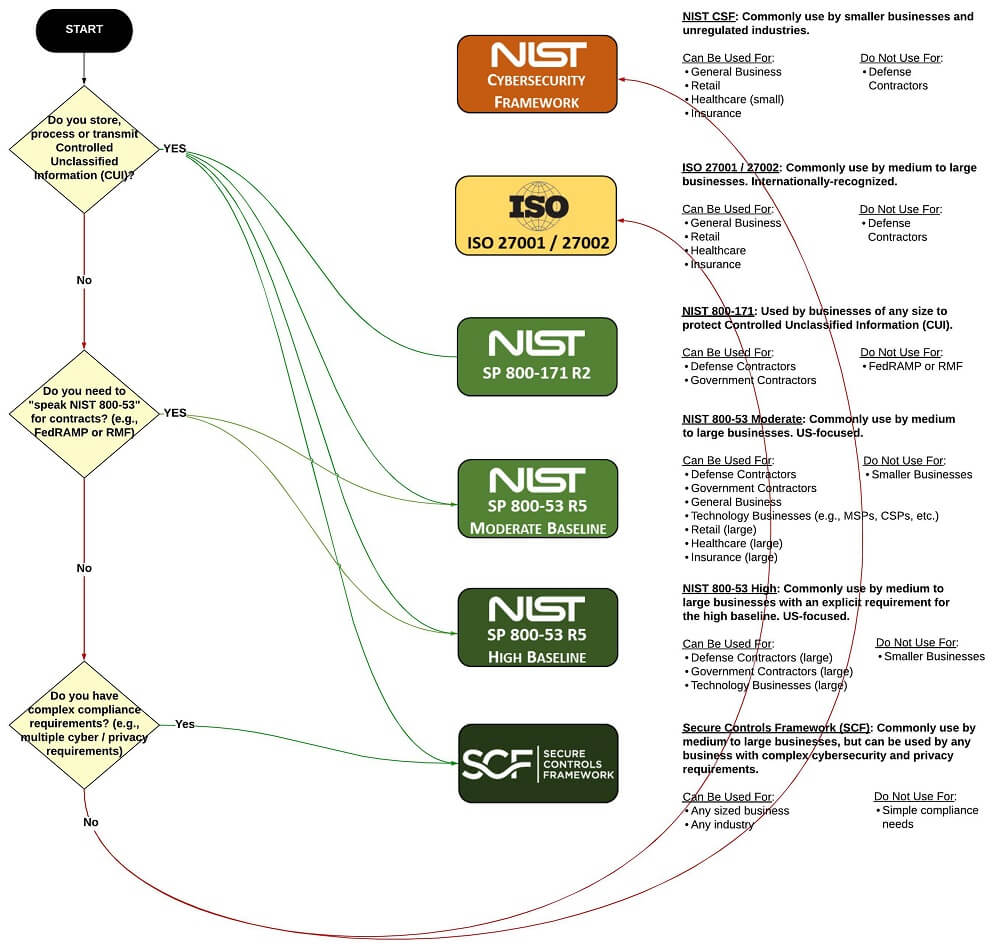
Mapping is useful for gap analysis and for satisfying customer requirements that ask for it. It is not a substitute for implementing 800-53 in a full-fed system. The resulting control set will be thinner than what 800-53 intends. Several 800-171 requirements have no meaningful 800-53 alignment, and forcing a connection creates false confidence. The SC family is the worst offender here. SC.1 through SC.8 mostly map fine. SC.39, as I mentioned, is an awkward fit. SC.36 and SC.37 about supply chain and monitoring also pull in different directions depending on which 800-53 baseline you use. If the goal is genuine 800-53 compliance rather than just a mapping exercise, the better path is to implement 800-53 directly and use 800-171 as a sanity check for DIB-relevant controls. If the goal is purely a mapping deliverable for a contract, I recommend sticking with the 800-171 requirements as the source of truth and treating the 800-53 mapping as supplementary evidence, not the primary compliance basis. A lot of people reverse that and it comes back to bite them during audits.
Where to Get a Mapping Reference
NIST does not publish an official crosswalk, so you will find community-maintained tables online. The most reliable ones I have seen are maintained by compliance vendors and DoD-adjacent contractors. Download one, validate it against the current revision of both documents, and correct the mismatches yourself. Blindly trusting a third-party matrix is how you inherit someone else's error. I spent a morning correcting a publicly available mapping that had AC.19 linked to AC-19 in 800-53 when it should have been AC-12 and AC-16 combined, because 800-171's AC.19 is about remote access, which 800-53 splits across those two controls. A small detail, but enough to fail a control test if you do not catch it. Once the mapping table is built and validated, use it alongside your system security plan. Reference the 800-171 requirement numbers in your SSP, note the mapped 800-53 controls in parentheses, and document any gaps with compensating controls. That is the structure that survives an assessment without requiring you to reconstruct everything from scratch when the assessor asks why a particular mapping is thin.
.png?width=1026&height=1622&name=SG - NIST 800-53 vs 800-171 Decision Tree (4).png "NIST 800-171 vs. 800-53: Differences, Similarities & Mappings")