How I Actually Use a Nist 800 53 Cheat Sheet Without Losing My Mind
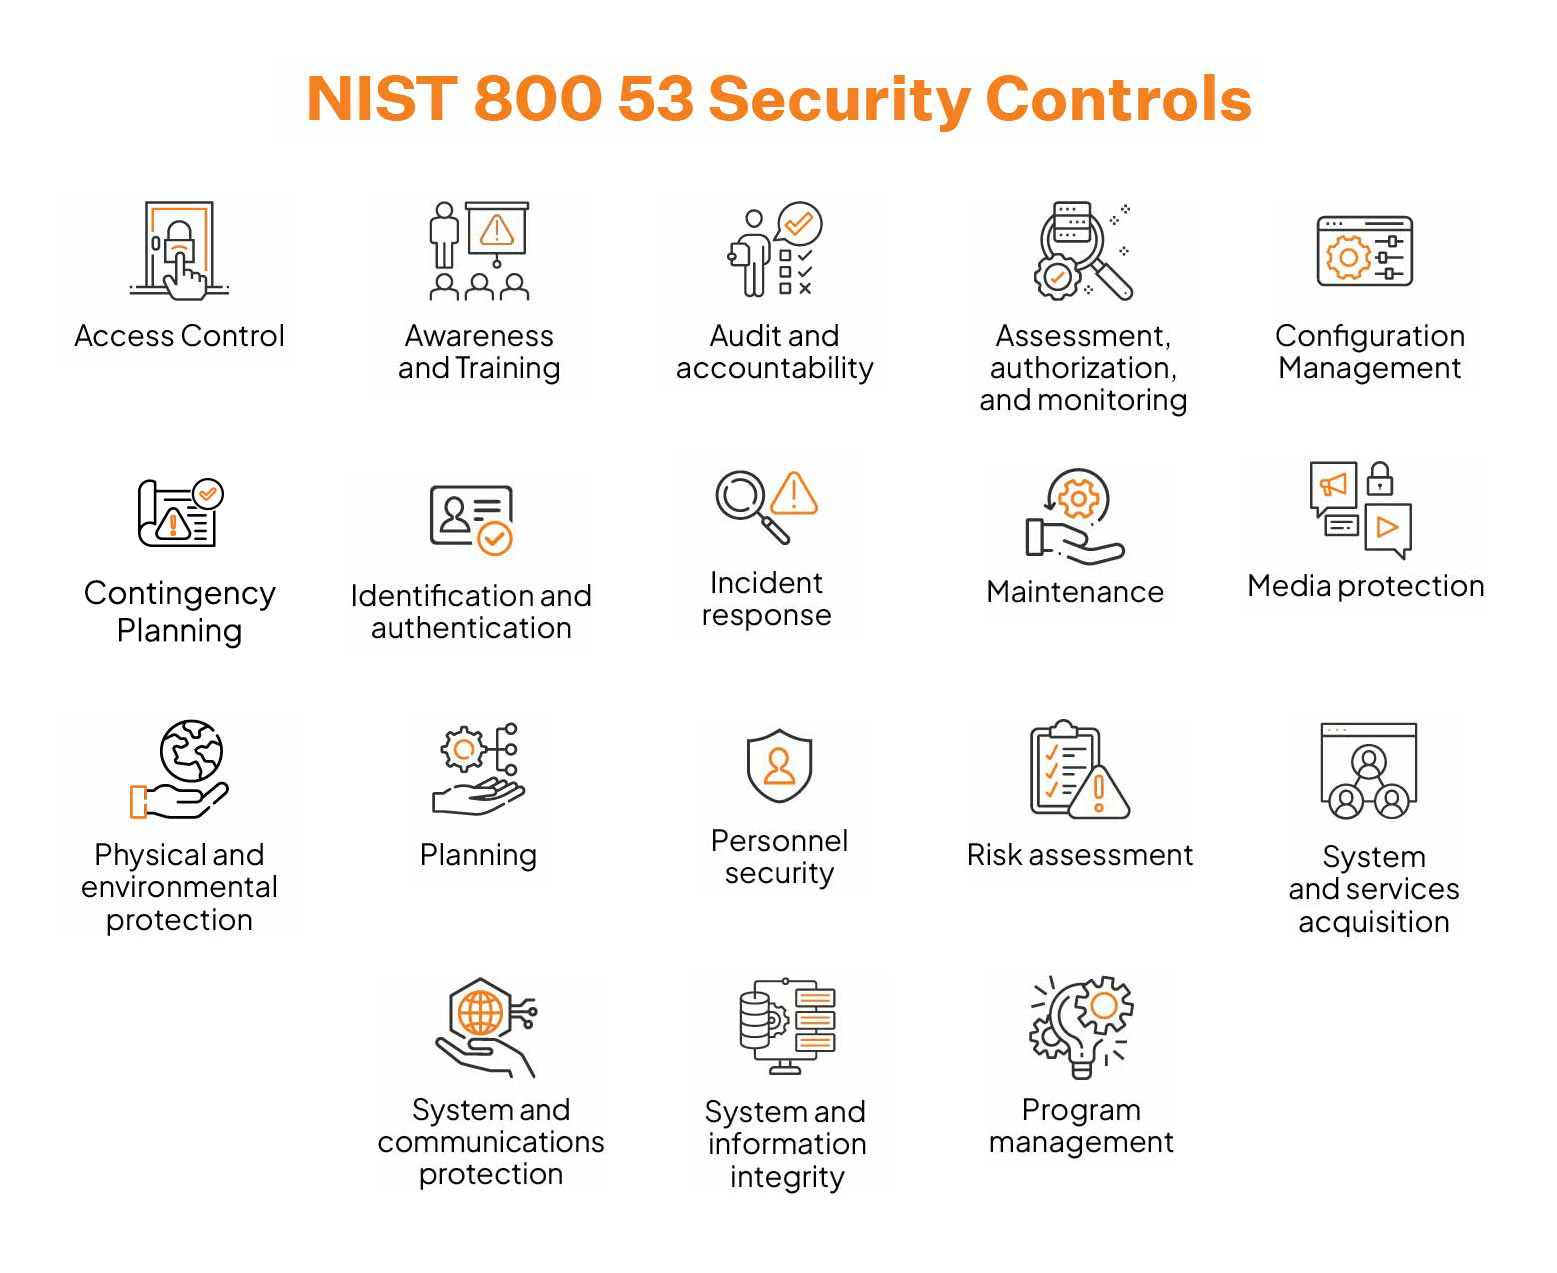
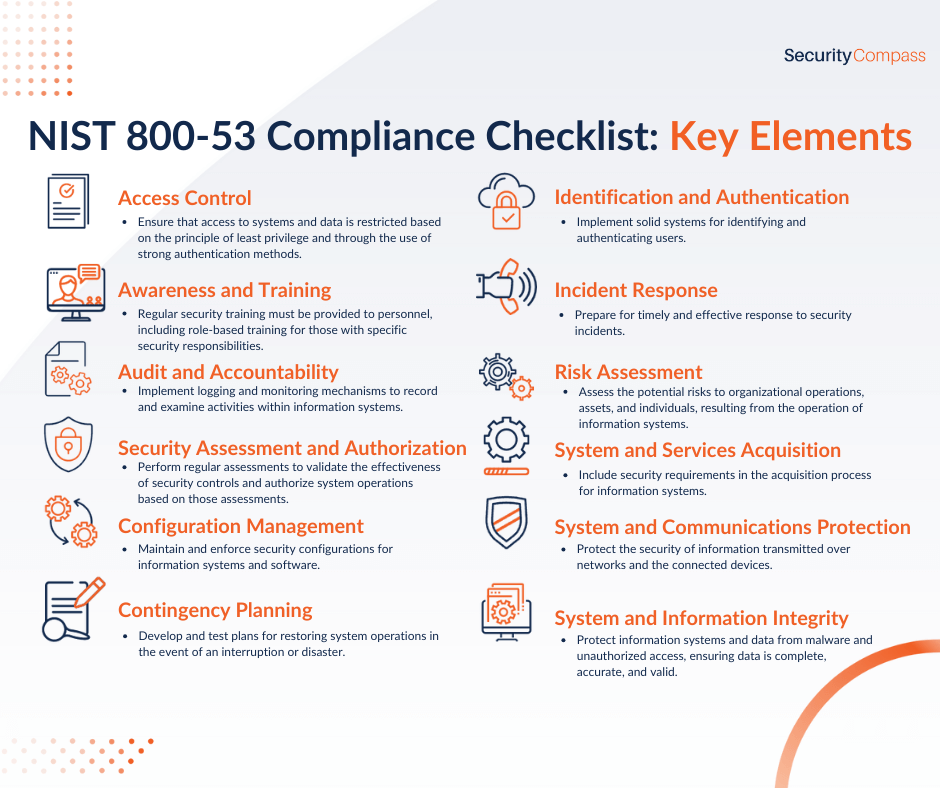
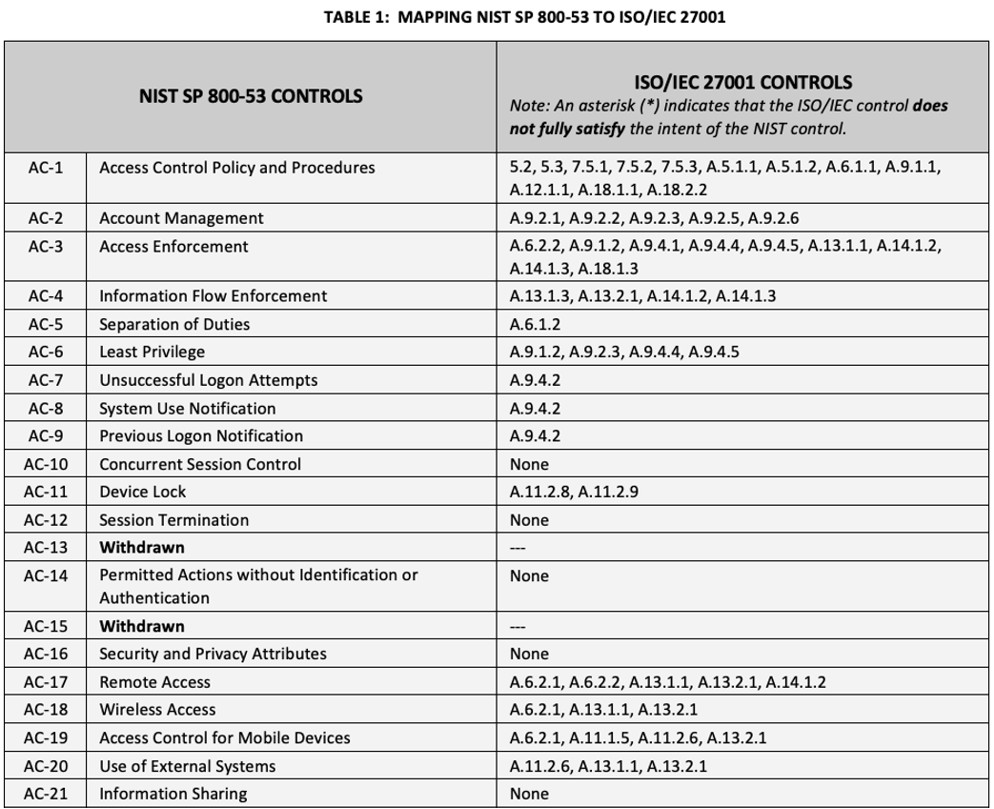
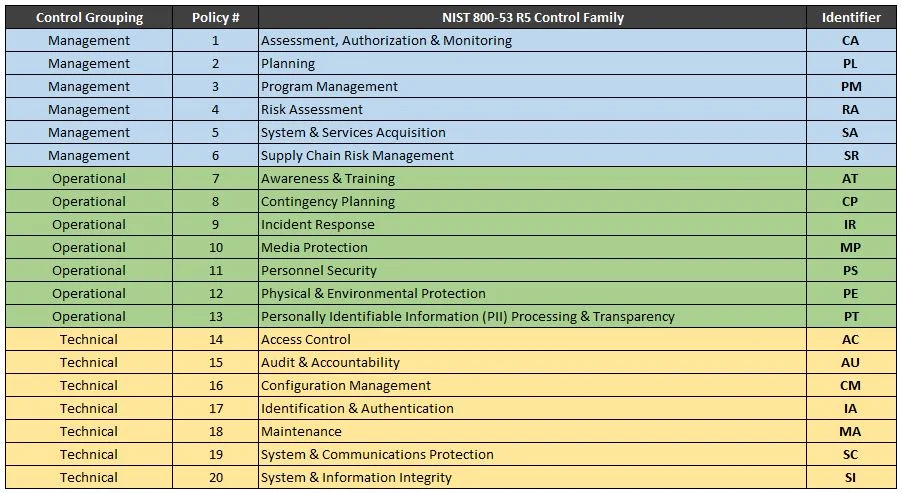
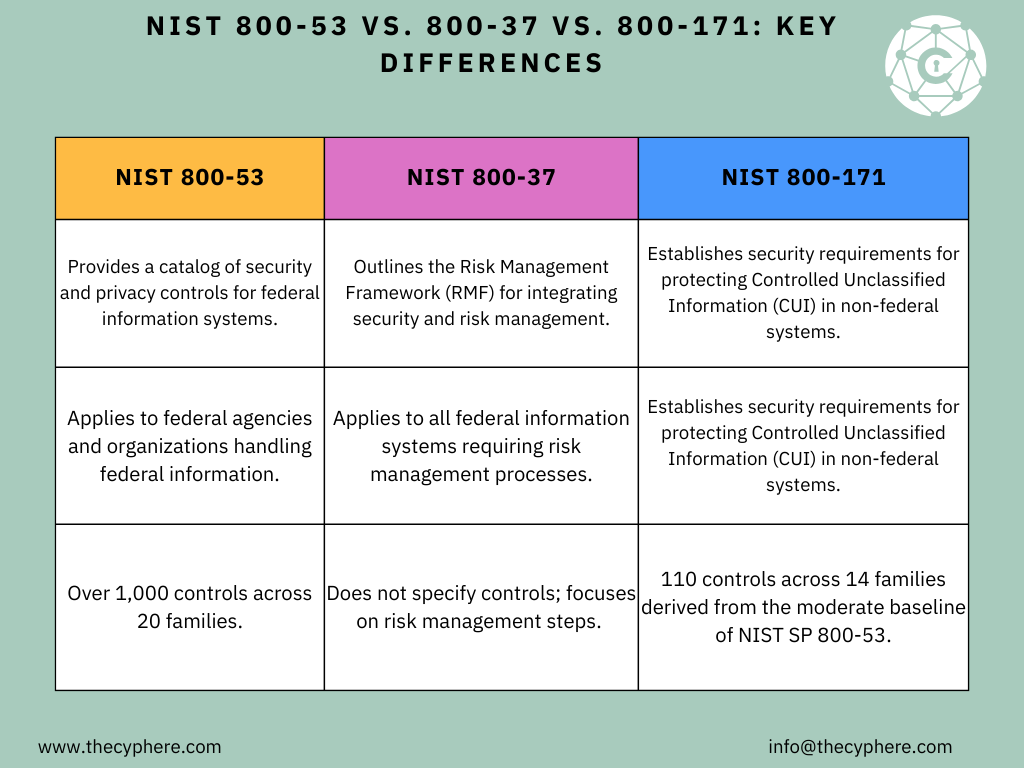
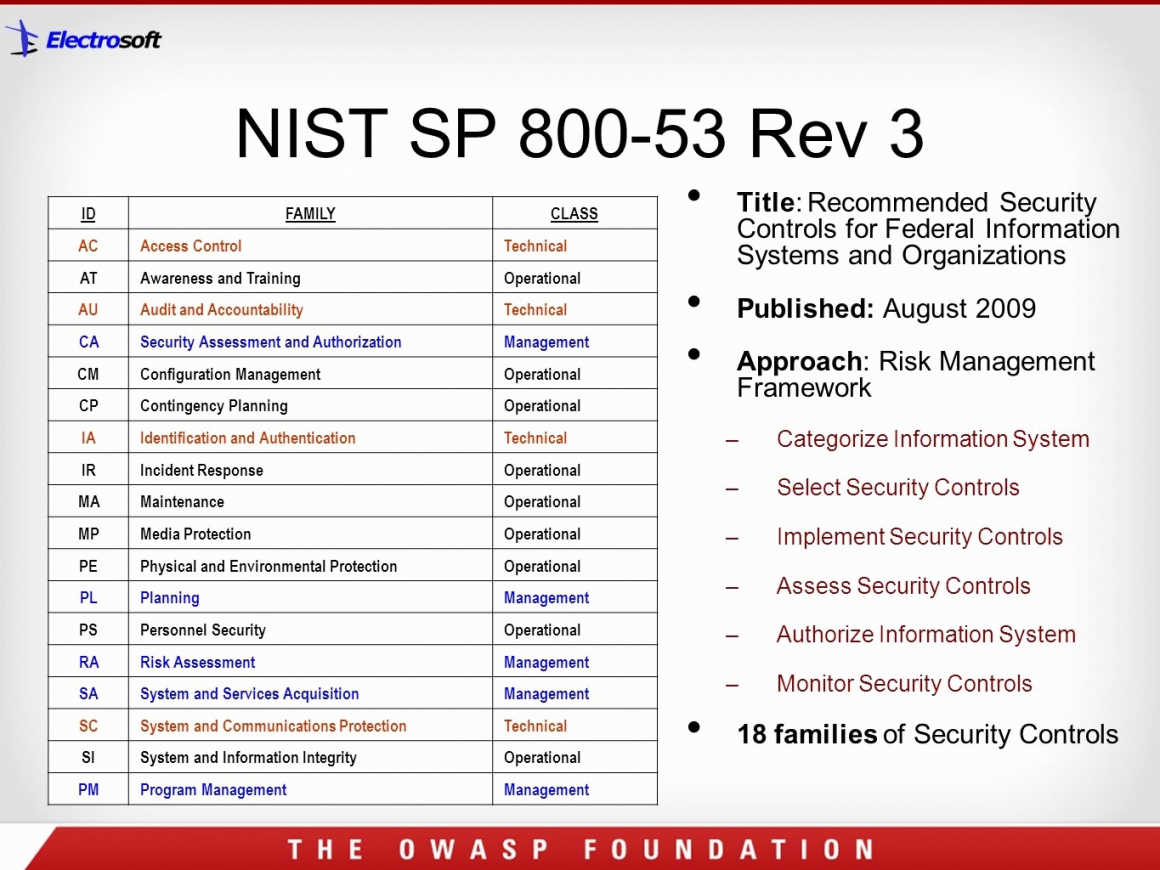
A Nist 800 53 Cheat Sheet is basically a compressed reference that maps control families, common control identifications, and baseline selections to the full catalog so you can stop flipping through a 600-page PDF every five minutes. I keep one pinned open during audit prep and remediation work. The full catalog is massive. Revision 5 alone covers over 1,100 controls across 20 families. Nobody memorizes that. The useful ones have three things at minimum: control family quick-reference tables, baseline mappings for low, moderate, and high impact, and cross-references to common control providers like CACM or CAW. Some also include ACSS (Assured Compliance Assessment Solution) short codes, which matter if your organization uses FISMA reporting tools. Without those codes, you end up manually translating control labels during assessment cycles, which wastes more time than anything else I deal with. I use a cheat sheet that lays out controls in a table format with columns for control identifier, family, baseline applicability, and a one-line summary of what the control actually requires. The summary column is where most free versions fail. They paste the exact control text, which is already in the official document. A real cheat sheet paraphrases it in plain language so you can scan it in seconds instead of re-reading the same bureaucratic sentence three times.
How to Build One That Doesn't Suck
Start with SP 800-53 Rev 5, pull the control tables from Appendix F, and export them. I use a Python script that reads the NIST HTML catalog and outputs a CSV with the control ID, family, impact level, and a simplified description I wrote myself. The simplified descriptions are what make the sheet usable under pressure. Machine-generated summaries are usually worse than useless because they miss the operational context. Here's the workflow I actually follow: First, I identify which controls apply to my target environment. That means filtering by impact level and any organizational tailoring statements. If my system is moderate, I start with the moderate baseline. Then I cross-reference with my existing security architecture to see which controls are already satisfied by infrastructure or platform controls, which ones need custom implementation, and which ones are partial matches that need compensating measures.
The second step is mapping controls to their common control providers. This is where people get tripped up. AC-2 account management might be handled entirely by the identity and access management platform, not by the application itself. If you treat every control as something the system owner must build from scratch, your security plan balloons to an impossible size. I flag each control with its provider type: shared, hybrid, or fully implemented by the system. Third, I add the assessment procedures. Not the full detailed steps, just the assessment type and the key evidence needed. For example, AC-2 requires reviewing account types and monitoring for unauthorized accounts. The evidence is account configuration snapshots and access review logs. I note that on the sheet so auditors and my team know exactly what to pull when the assessment window opens.
Get the Full Details
The Edge Case That Taught Me to Stop Trusting Default Maps
I ran into a situation where the standard baseline mapping listed IR-4 as a moderate-baseline control, but our incident response process was entirely outsourced to a managed detection and response provider. The control text says the organization must detect, collect, analyze, and respond to incidents. Our MDR vendor handles detection and initial response. We handle escalation and post-incident activities. The cheat sheet had no column for this kind of shared responsibility nuance, so I added one. The workaround was simple. I created a custom column called "primary responsibility" with values like vendor, org, or split. Then I added a notation field where I wrote exactly where the split occurred. This mattered during an actual assessment because the auditor asked whether IR-4 was fully implemented or partially covered. Without that column, I'd have spent twenty minutes explaining it verbally while they checked boxes. With it, I pointed to the sheet and moved on.
Common Mistakes People Make With These Sheets
Most free cheat sheets online are just screenshots of the NIST tables with minor formatting changes. They don't add value. A few are exported directly from FedRAMP dashboards without being updated for Rev 5. Using an outdated one will cause you to reference controls that no longer exist in the current catalog structure, or miss new controls like SC-39 or AU-12(t) that didn't exist in Rev 4. Another mistake is treating the cheat sheet as a completeness check. It isn't. The baseline tells you which controls apply. It doesn't tell you whether your implementation meets the control's intent. You still need actual assessment procedures, evidence collection, and gap analysis. I've seen teams treat having the control checked off on a spreadsheet as equivalent to being compliant. It isn't. The assessment is what matters. The biggest practical limitation I hit repeatedly is that a static cheat sheet doesn't scale well when you're managing controls across dozens of systems with different tailoring statements. Each system authorization package has its own control selections and supervisory conditions. My solution was to build a lightweight mapping tool that takes the base cheat sheet and layers system-specific tailoring on top using a simple tagging system. Controls get tagged with the systems they apply to, and the view filters automatically.
Nist 800 53 Cheat Sheet Where to Get a Working Version
The most reliable sources are the NIST website directly for the official control catalog, the FedRAMP marketplace for already-assessed control baselines mapped to specific cloud offerings, and your organization's own security control family documentation if you've already done tailoring work. I maintain a personal version in Notion that I update quarterly as new controls and overlays get published. It includes the control tables, family summaries, impact-level filters, and the provider mapping columns I described. If you want something ready to use without building your own, look for versions that include ACSS short codes, impact-level baselines, and a clear provider attribution section. Those three features separate the sheets that actually help from the ones that just look organized. Everything else is decorative.
When a Cheat Sheet Fails You Completely
During a joint Authorization to Operate review last year, I discovered that the cheat sheet couldn't handle overlapping control requirements between CA-7 and SI-2 because both dealt with updates but from completely different angles. CA-7 is about security configurational changes to the system. SI-2 is about timely software patches. They share some evidence but serve different purposes. The sheet listed them separately, which was fine until the auditor asked how we coordinated change control with patch management and whether dual tracking created gaps. That question required a process explanation, not a control lookup. The cheat sheet was irrelevant to answering it correctly. The fix was adding a linkage section to the sheet where I documented which controls share evidence or depend on the same operational process. Now when an auditor asks a cross-control question, I can pull up the linkage view and show the relationship instead of digging through separate control entries. It takes maybe thirty seconds to navigate to the right view. Before, it took fifteen minutes of cross-referencing. A cheat sheet saves time on lookup-heavy work. It does not replace understanding the control intent, the assessment methodology, or the operational processes that actually produce compliance. Use it for quick reference and mapping. Don't use it as a substitute for reading the full control text when the requirement is ambiguous or your implementation diverges from the standard assumption. That's where the real work lives, and no condensed reference can cover that for you.