Getting a Nist 800 53 Implementation Guide Actually Useful Instead of Another Shelf Filler
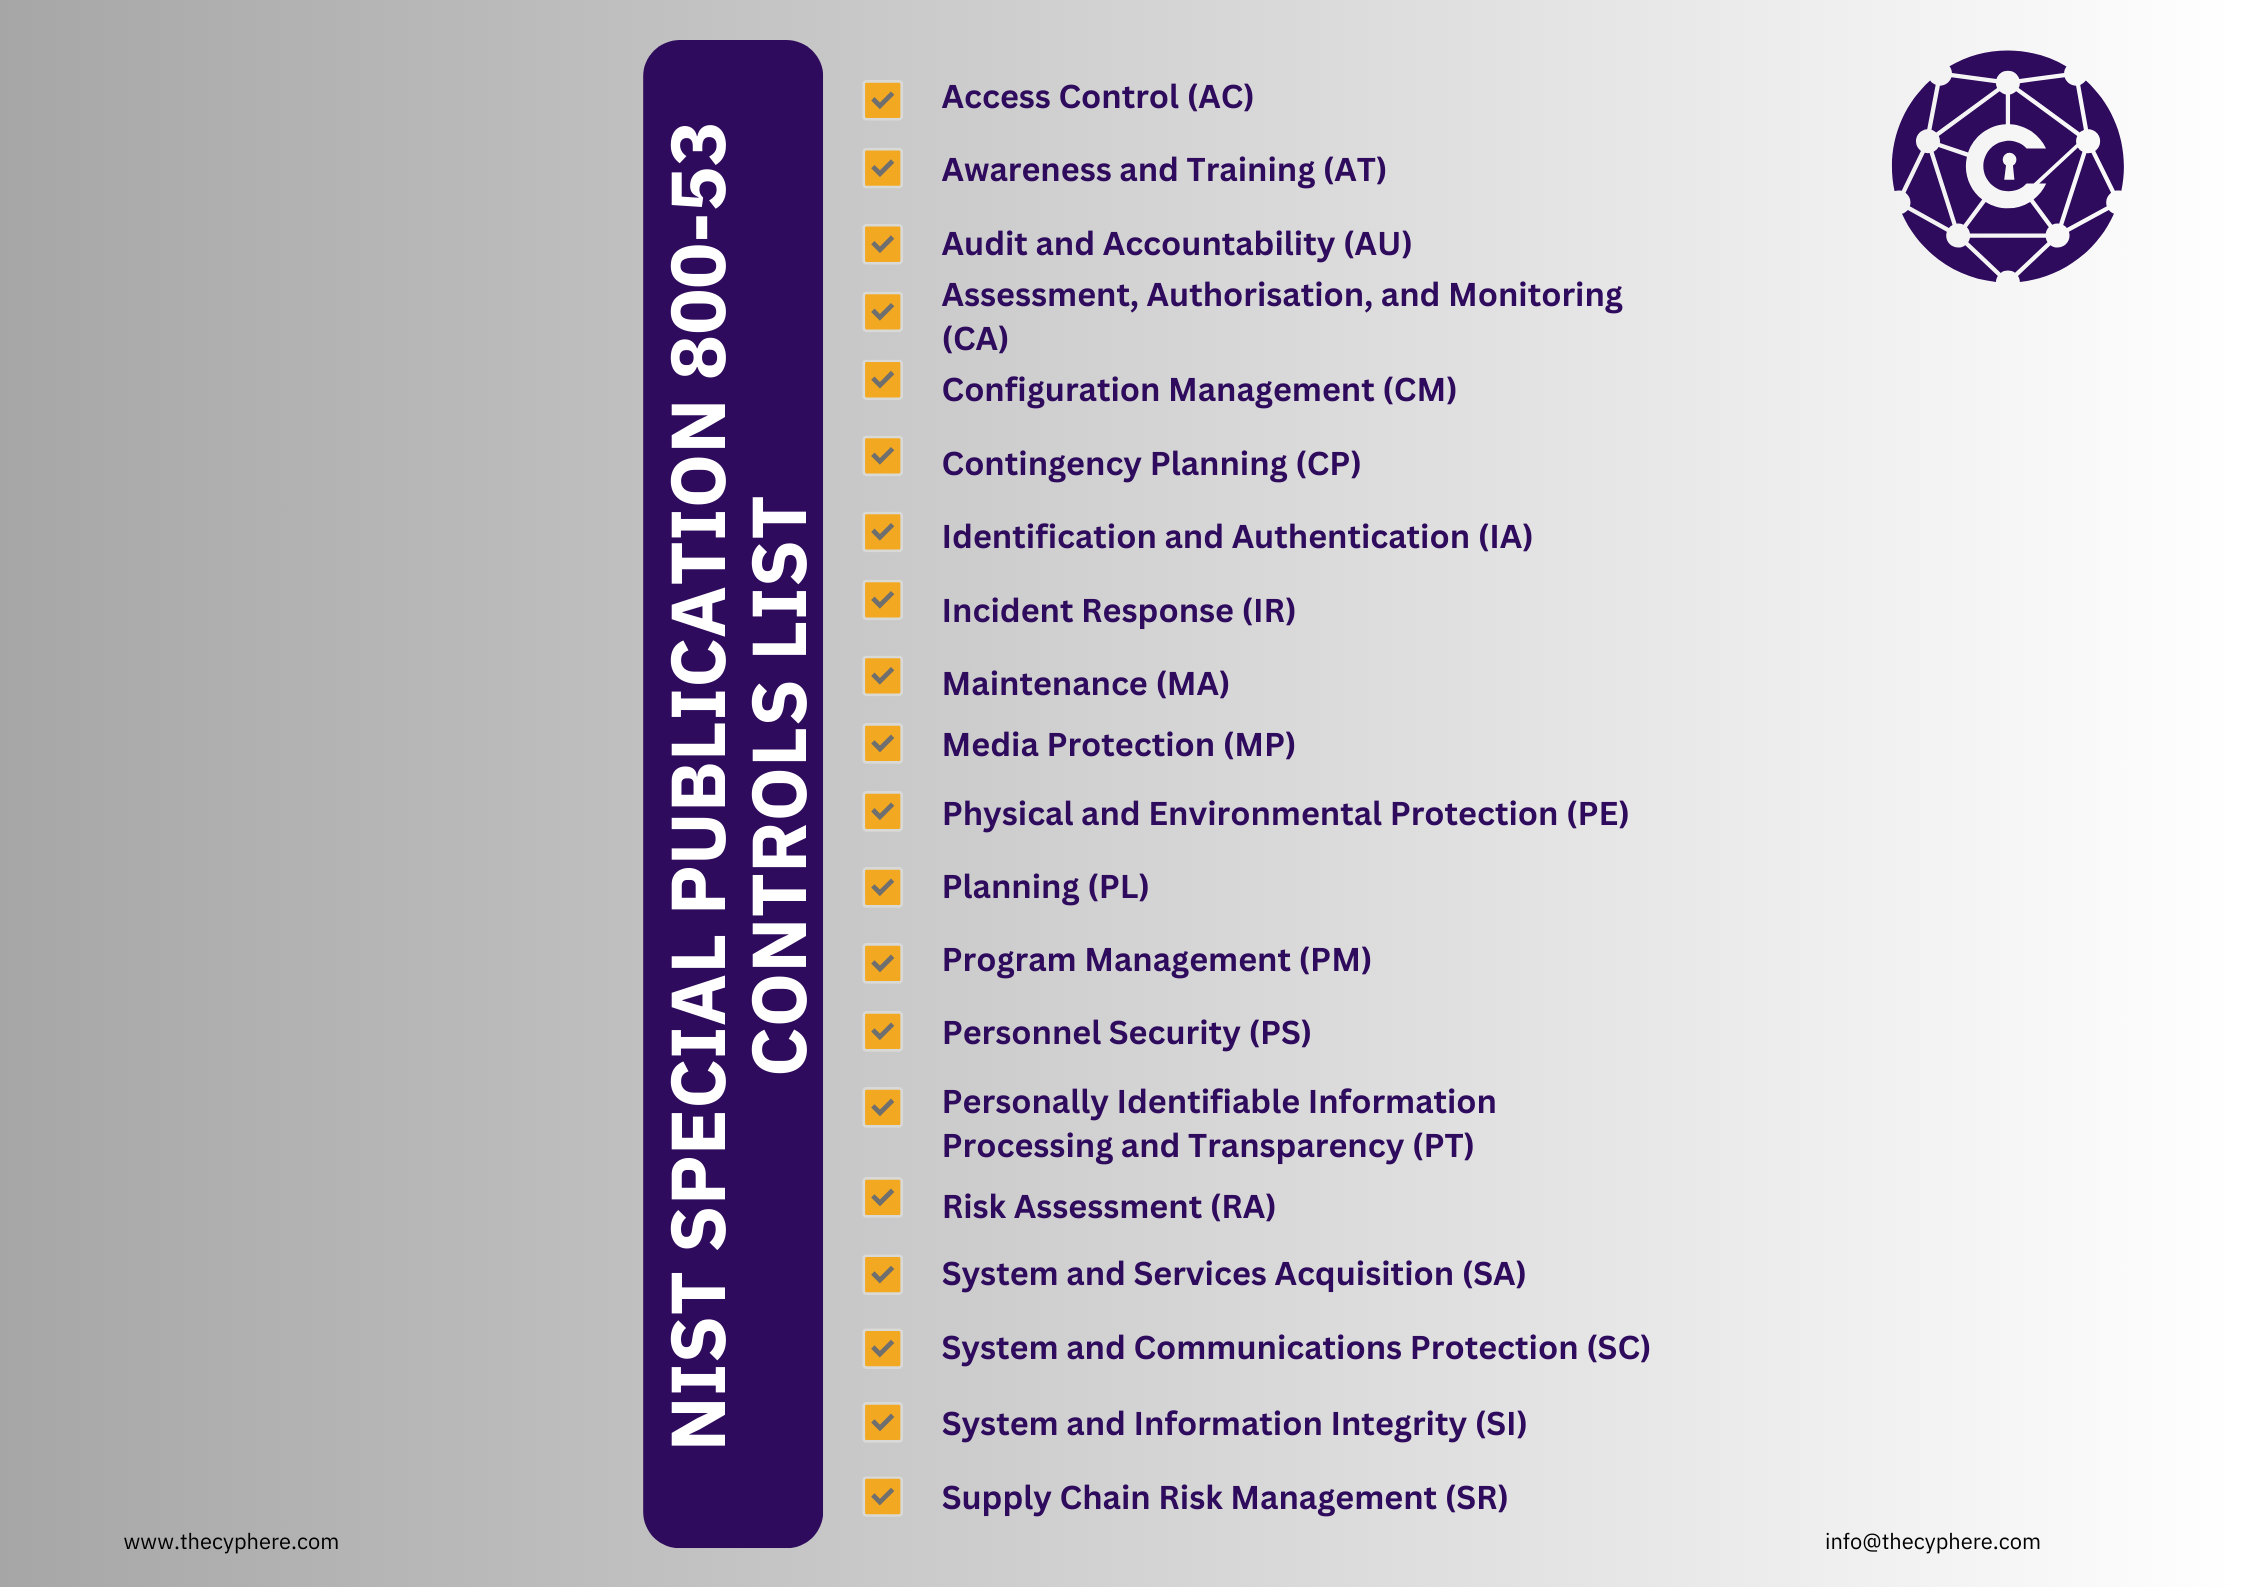
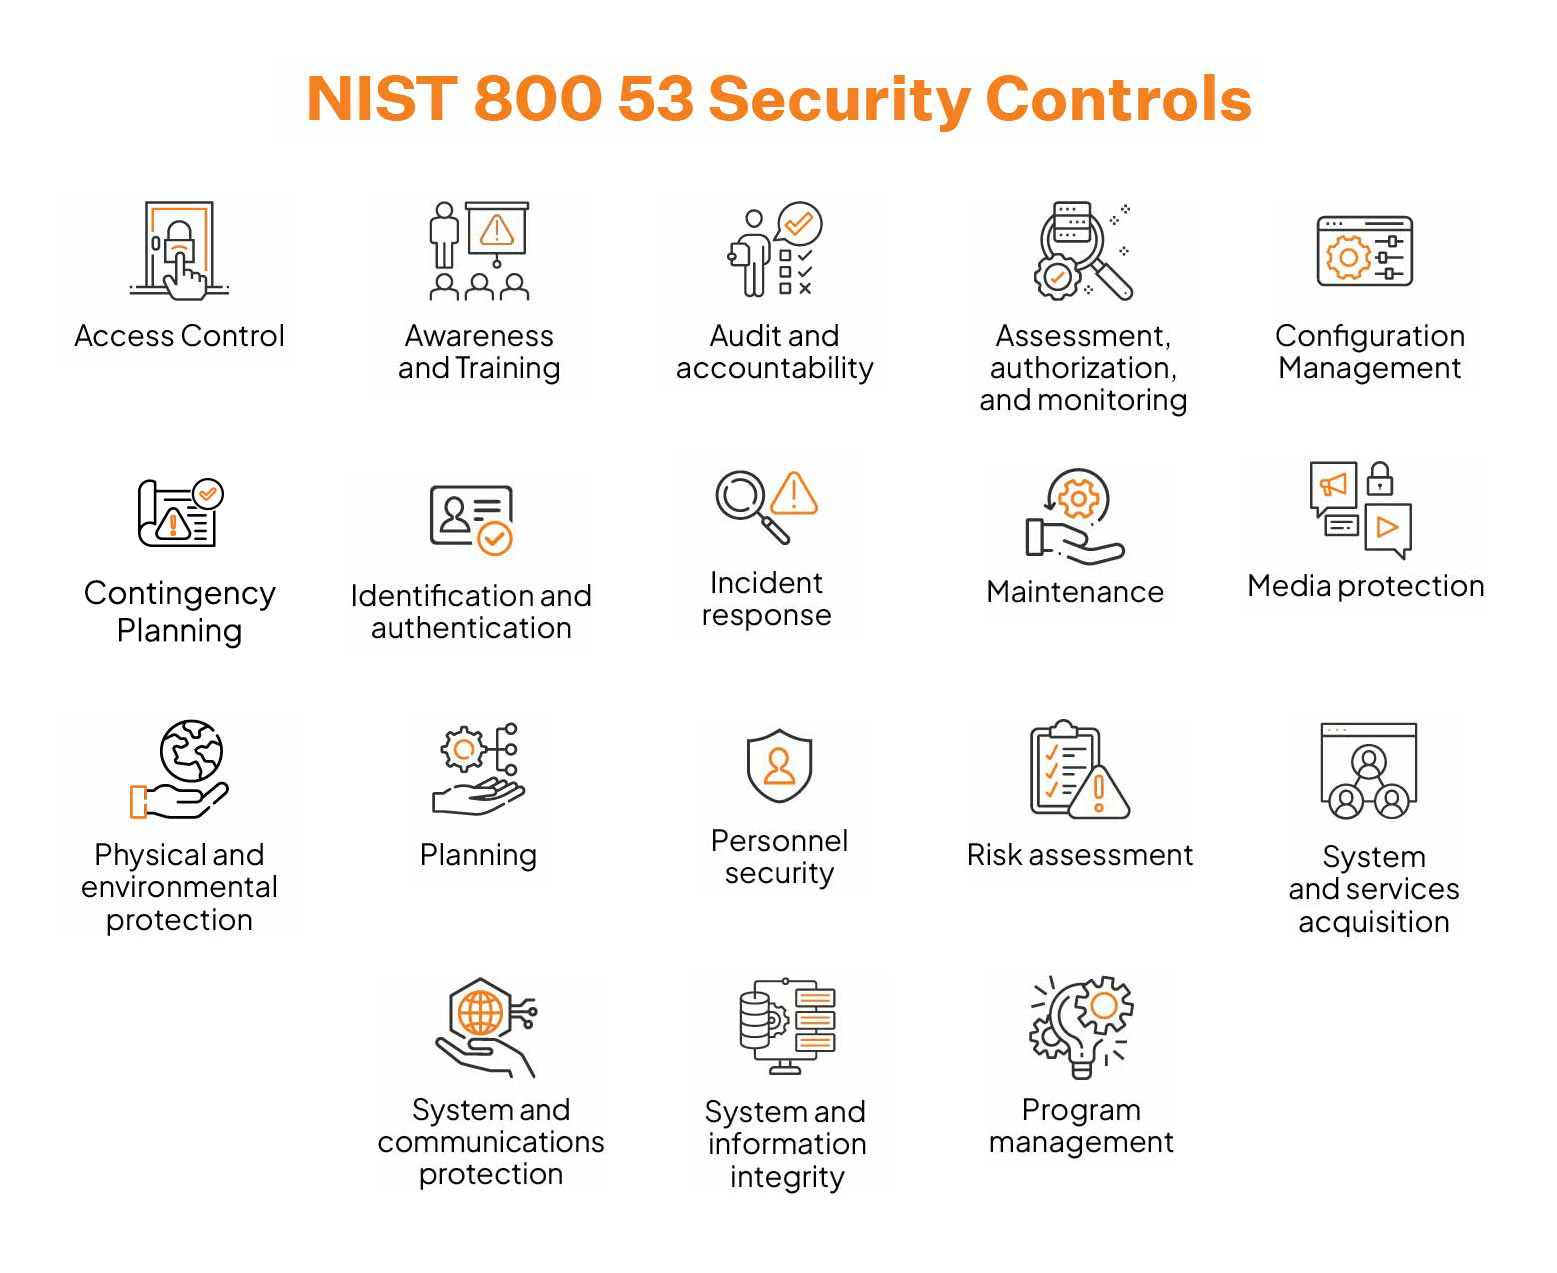
Nist 800 53 Implementation Guide isn't something you read cover to cover and suddenly your compliance status improves. It's a living document you reference while you're building out security controls, mapping them to your environment, and figuring out which ones your auditors will actually care about versus which ones are technically in the catalog but practically irrelevant to your deployment. The best guides cut through the catalog noise and tell you what implementation looks like on the ground. The base Nist 800 53 catalog lists controls. A proper implementation guide takes those controls and answers the questions that come after. How do you operationalize AC-2 (Account Management) when you're managing five thousand accounts across Active Directory, AWS IAM, and a legacy SaaS platform? What evidence does an assessor actually want to see for AU-6 (Audit Review)? Which SIEM tool configuration satisfies the detection requirements under SI-4? I found myself working on a FedRAMP moderate authorization about three years ago where the team had spent two weeks trying to map every single control in the catalog to our infrastructure. We were drowning in spreadsheets. The breakthrough came when we stopped treating the implementation guide as a checklist and started using it as a decision tree. Each control has families, each family has intent, and the intent is what matters for the assessment. You can satisfy the intent without implementing every sub-control the way the guide presents it theoretically.
How to Use an Implementation Guide in Practice
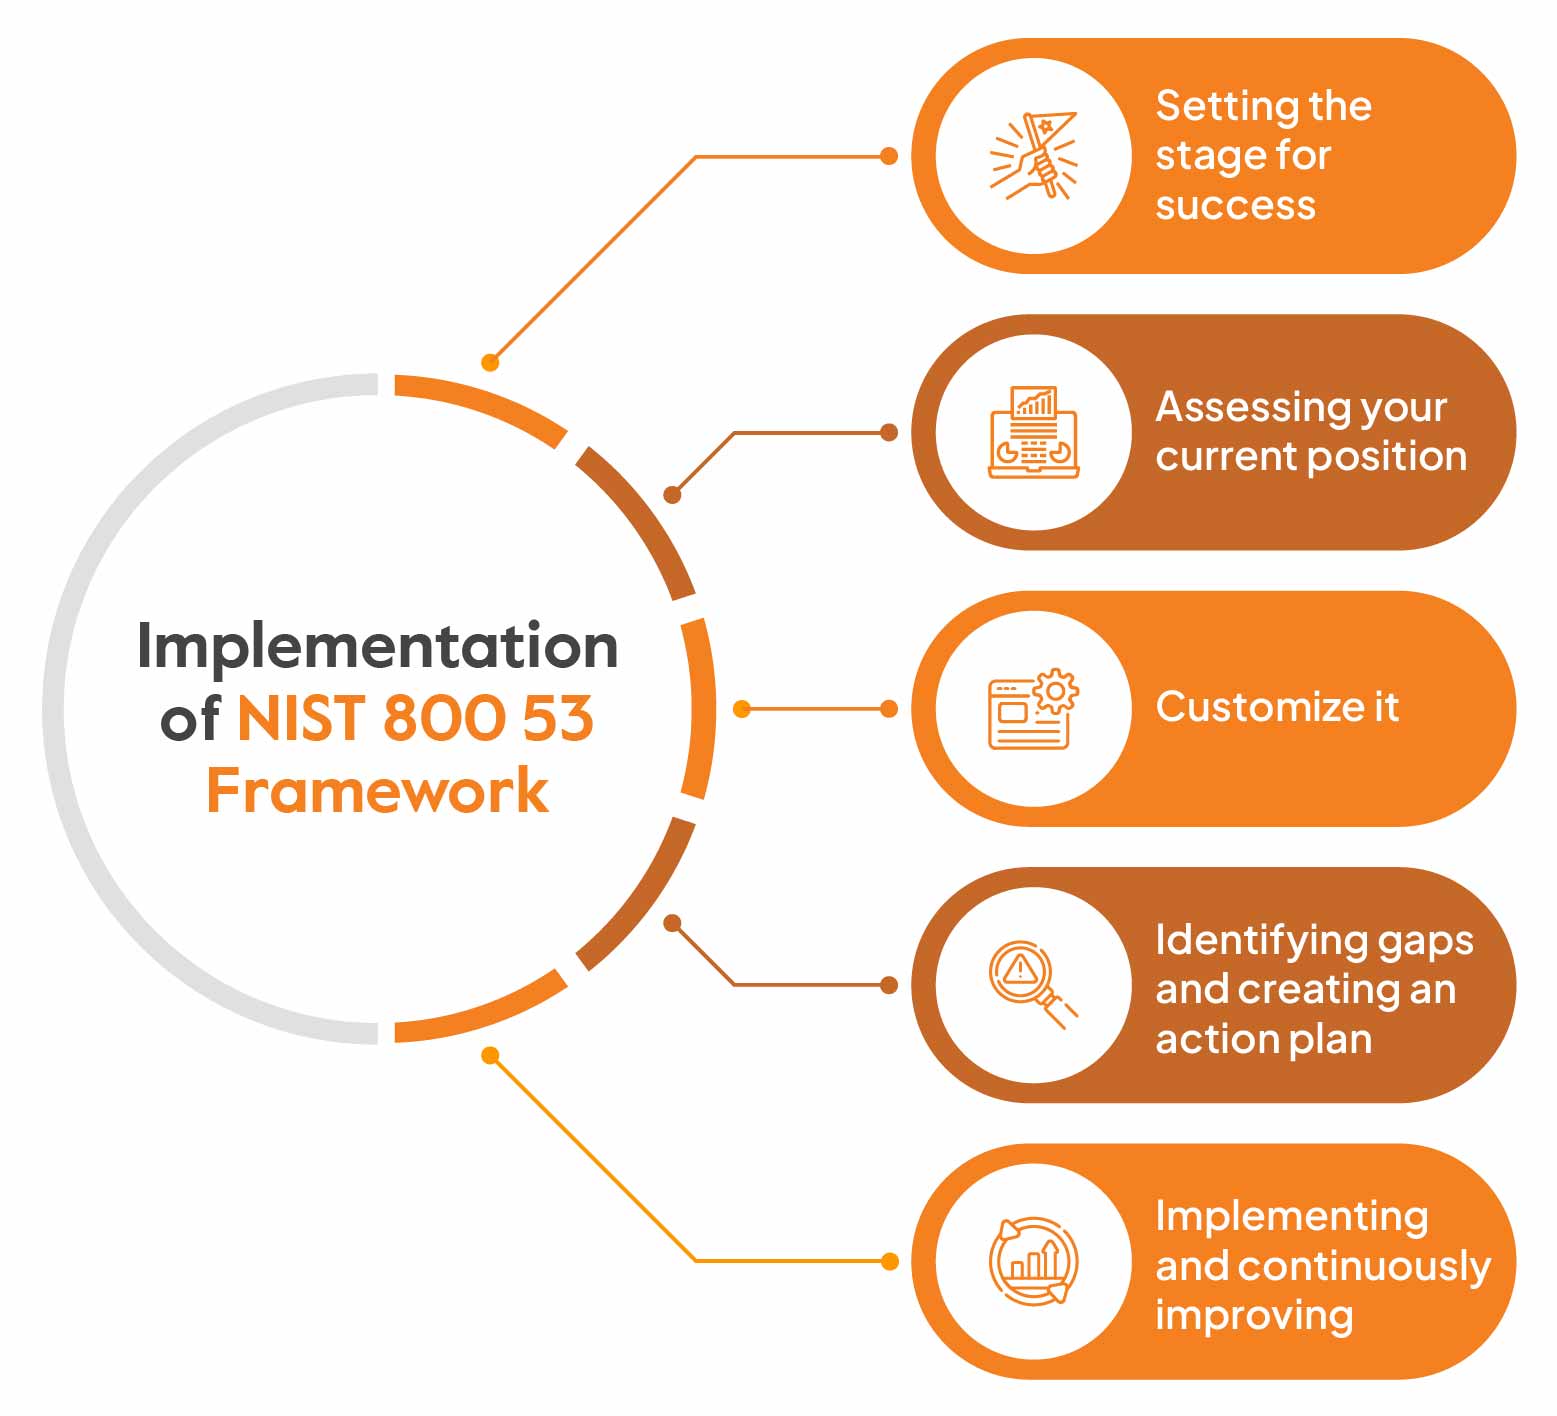
Start by identifying your system's security categorization. This determines which baseline of controls you're working from—low, moderate, or high impact. The gap between what the catalog says and what your system actually does is where the real work happens. Document each control, note the existing implementation, identify gaps, and assign an owner. This process typically takes a security team 3 to 6 weeks for a moderate-impact system depending on complexity. One thing most guides don't emphasize enough is the overlap between control families. CA-2 (Security Assessments) and SA-10 (Developer Configuration, Testing, and Validation) both touch on verification activities. If you structure your evidence collection around the assessment lifecycle rather than individual controls, you end up with fewer artifacts that satisfy multiple requirements simultaneously. It cuts your evidence gathering time significantly and reduces the chance of contradictory statements appearing in different control responses. Another practical issue: control tailoring. The baseline gives you a starting set, but not every control needs the same level of implementation across your environment. A standalone development server doesn't need the same network segmentation controls as your production payment processing system. The guide should help you understand which controls are mandatory as-is and which allow for compensating controls. This is where organizations most commonly get tripped up during assessments.
A Real Problem and How I Solved It
During that same FedRAMP engagement, we ran into a specific issue with CM-8 (Information System Component Inventory). The guide recommends an automated, continuously updated inventory. Our environment used a mix of CloudFormation templates, manual EC2 provisioning, and container orchestration through ECS. We had three different inventory sources that never synchronized, and the auditors flagged it immediately. The workaround was straightforward but not obvious from the guide itself. I built a lightweight Python script that pulled from CloudWatch logs, CloudFormation stack outputs, and ECS service listings every hour, merged them into a single SQLite database, and generated a diff report against the previous run. Anything that changed triggered an alert to our config management system. The whole setup took about two days to deploy and reduced the inventory discrepancy rate from roughly 40 percent to under 3 percent within the first month. It wasn't the most elegant solution, but it satisfied the control requirement without requiring us to migrate to an expensive CMDB tool that the project timeline couldn't accommodate.
Get the Full Details

Counter-Intuitive Things Beginners Miss
Most people assume more documentation equals better compliance. It doesn't. Assessors prefer concise, verifiable evidence over exhaustive documentation that contradicts itself. I've seen teams produce hundreds of pages of control narratives that fell apart under cross-referencing. A single page with a clear control statement, current implementation, responsible owner, and a screenshot or configuration snippet often passes review faster than a volume of text. Another misconception is that implementation guides are static. They aren't. Nist updates 800 53 regularly, and the implementation guidance shifts with each revision. The December 2020 revision introduced significant changes to the control structure, particularly around supply chain risk management (SR family) and continuous monitoring (CM family). If your guide hasn't been updated since at least 2021, parts of it are already outdated. Check the revision date before investing time in its recommendations.
Limitations and When This Approach Falls Apart
Implementation guides work well for standardized cloud environments and traditional on-premises data centers. They become much harder to apply when you're dealing with hybrid architectures that span multiple cloud providers, use edge computing, or incorporate IoT components. The control models assume a relatively bounded system boundary, and modern deployments often don't fit that assumption cleanly. There's also the question of cost. A thorough implementation following a quality guide for a moderate-impact system with significant custom development can easily require 200 to 400 engineering hours beyond the security team's normal workload. For smaller organizations, this is a substantial commitment. In those cases, leveraging a managed security service provider or a compliance automation platform can reduce the burden, though it introduces third-party dependency risks that themselves need to be controlled under SA-9. If your organization is small enough that the full Nist framework feels like overkill, consider starting with Nist 800 82 for operational security or the CISO Companion Guide, which maps common requirements to a more manageable subset. Not every system needs every control, and pretending otherwise just creates noise that obscures the controls that actually matter for your risk posture.