Why You Even Need This
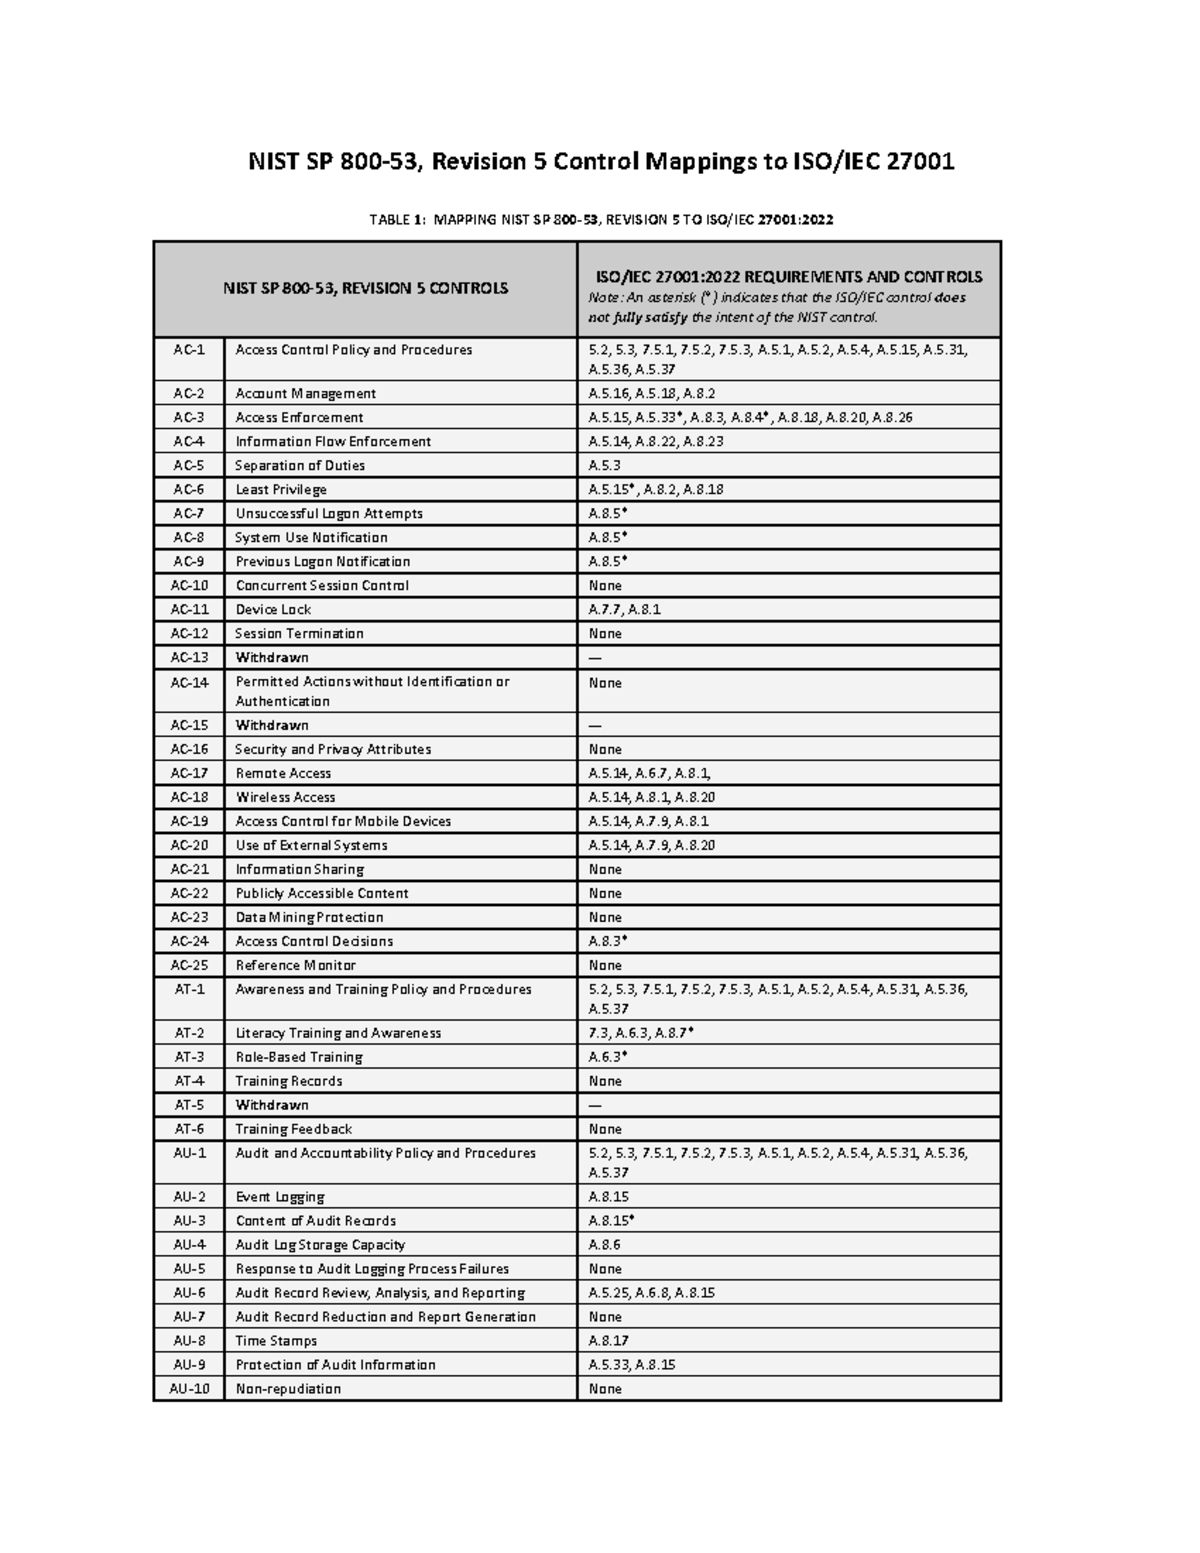
NIST 800-53 comes from the U.S. government side, and it's extremely granular. ISO 27001 is an international standard with fewer controls but more flexibility around how you implement them. Most organizations that do both end up wondering which NIST control maps to which ISO 27001 clause so they can stop building two separate evidence folders for the same thing. The actual process is straightforward, but the details matter. I'll walk through how I built a working crosswalk for a client last year and what went wrong with the initial version.
Nist 800 53 To Iso 27001 Mapping
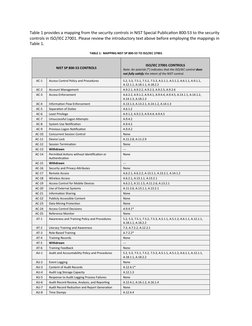
The core idea is matching NIST 800-53 controls to ISO 27001 Annex A controls. Here is how it actually works in practice. First, you take the NIST control catalog and pull each control identifier along with its title and any family grouping. Then you go to the ISO 27001:2022 Annex A list, which has 93 controls organized into four themes: organizational, people, physical, and technological. You compare the intent of each NIST control against each ISO control and create a bidirectional mapping table. I used a spreadsheet with three columns for the primary mapping: NIST control ID, ISO 27001 control ID, and notes on coverage. Then I added a fourth column for gaps where the NIST control had requirements that ISO 27001 simply didn't address. That gap column turned out to be the most useful part of the entire exercise.
One Specific Problem I Ran Into
I was working on a FedRAMP authorization where the system owner also wanted ISO 27001 certification simultaneously. We mapped about 1,400 NIST 800-53 controls down to the 93 ISO 27001 Annex A controls. The problem was AC-2(3) -- Account Disable. NIST 800-53 requires disabling accounts within 15 minutes of certain events. ISO 27001 A.5.15 only says something generic about account management. Our original mapping said AC-2(3) maps to A.5.15, but when the ISO auditor reviewed it, they said A.5.15 doesn't actually cover the 15-minute requirement. The workaround was to map AC-2(3) to A.5.15 for the baseline account management language, but then explicitly document the 15-minute disable requirement as an organization-specific policy that exceeds ISO 27001 scope. That way the NIST requirement still gets tested, and the ISO auditor doesn't flag a missing control. It adds a bit of overhead to the evidence package, but it prevents the awkward conversation where both auditors are asking about the same control and getting different answers. People tend to treat this as a one-to-one translation, but it's not. NIST 800-53 has subcontrols and enhancements that create a much deeper hierarchy. ISO 27001 Annex A controls are single statements without that kind of granularity. When you see a NIST control like AU-6 with seven different enhancement options, you can't just say it maps to one ISO control and move on. Some NIST enhancements have no ISO equivalent at all. These are mostly things like audit review frequency requirements, correlation rules, or escalation procedures that ISO 27001 leaves to organizational choice. Another issue is that ISO 27001:2022 restructured its Annex A significantly compared to the 2013 version. If you find a mapping reference online that says ISO 27001:2013, don't trust it without verifying. Control numbers changed. A.9.1.1 in 2013 is not the same as A.5.15 in 2022. This trips up a lot of people who download old crosswalks from vendor websites and use them without checking.
Get the Full Details
How to Actually Build the Crosswalk
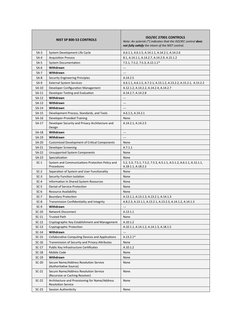
Start by getting the latest NIST 800-53 Rev 5 catalog and ISO 27001:2022. Don't skip Rev 5 -- it added a bunch of cloud-specific controls that matter if your environment isn't purely on-prem. Create a master spreadsheet with these tabs: the main mapping, a gap analysis tab, a NIST-only tab, and an ISO-only tab. For the main mapping, work family by family. NIST controls are grouped into families like AC for Access Control, AU for Audit, SI for System and Information Integrity. Go through each NIST family and match controls to the corresponding ISO theme. Organizational controls map mostly to the ISO organizational theme. Technological controls map to the technological theme. But there's overlap. Some NIST security controls like SC-28 also have policy implications that belong in the organizational theme. Don't force a one-to-one family match -- follow the control intent instead. Once the main mapping is done, fill the gap tab with anything that appears in NIST but has no ISO counterpart. For a typical FISMA Moderate system, that's probably 200 to 300 controls with no direct ISO equivalent. For a High impact system, the number goes up further because of the enhanced subcontrols. The ISO-only tab will be much smaller -- maybe 30 to 40 controls that exist in Annex A but don't have a clear NIST 800-53 equivalent. A.5.7 on threat intelligence is one example. NIST doesn't have a single control that says exactly this.
Counter-Intuitive Things Beginners Miss
Here is one: doing the mapping in one direction is enough for compliance purposes, but if you only map from NIST to ISO, you will miss ISO requirements that have no NIST parent. That gap is usually small, but it matters if you are getting certified to ISO 27001 and want actual coverage. I've seen auditors find that an organization had mapped everything from NIST down and completely ignored A.6.1.4 about remote working security, which isn't explicitly covered anywhere in NIST 800-53 as a standalone control. Another thing: people assume that because NIST 800-53 is more detailed, it covers more ground. It does in raw count, but ISO 27001 requires an Information Security Management System with documented policies, risk assessment methodology, statement of applicability, and management review. NIST 800-53 doesn't require any of that structural governance layer. You can fully implement every NIST 800-53 control and still fail an ISO 27001 audit because you don't have a proper SoA or you haven't documented your risk treatment process. The mapping exercise alone won't get you certified to ISO 27001.
Practical Time Estimate
A basic mapping for a medium-complexity environment with maybe 200 active NIST controls takes about 8 to 12 hours for someone who knows both frameworks well. A junior consultant who is still learning the controls will take 2 to 3 days. The gap analysis portion usually adds another 4 to 6 hours. If you're doing this for an actual compliance engagement, budget roughly two weeks of part-time work including review cycles. The biggest failure mode is treating the mapping as a substitute for actual control implementation. A beautifully formatted crosswalk means nothing if your access control process isn't documented, your incident response plan hasn't been tested, and your vendor assessments are missing. I've seen organizations spend months on mapping and then get flagged within two weeks of their ISO surveillance audit because they had no evidence of actual control operation. Another limitation: this mapping doesn't work well if your NIST source is Rev 4 and you're targeting ISO 27001:2022. The control structures are too different. Rev 4 uses a completely different numbering scheme and categorization. Stick to Rev 5 for anything current. If you're stuck on Rev 4 for legacy reasons, you need a separate mapping effort and you should expect a lot more gap identification work.
Resources
The official NIST 800-53 Rev 5 catalog is available at nist.gov. The ISO 27001:2022 standard is published by ISO and can be purchased through iso.org or your national standards body. There are also free crosswalk references from CISA and from several consulting firms, but verify any third-party mapping against the current versions before using it in an audit. The versions change, and outdated mappings are the fastest way to create compliance blind spots.