Working With the Nist Csf Assessment Tool: What Actually Happens
NIST doesn't actually publish a single downloadable piece of software called the "NIST CSF Assessment Tool." What exists is a set of guidance documents, the CSF 2.0 itself, and the Profile Conduit methodology that organizations are supposed to build their own assessment instruments around. Most teams end up creating spreadsheet-based or questionnaire-driven assessments, while others license third-party tools that claim CSF alignment. Understanding how this actually works in practice matters more than looking for a magic application. The Nist Csf Assessment Tool approach starts with the framework's five functions — Identify, Protect, Detect, Respond, Recover — and the tier ratings from 0 to 4 that measure implementation maturity. You map your current state against the CSF Categories and Subcategories, score each one, then define where you want to be. That's the basic workflow. It sounds simple because the framework is intentionally designed to be simple.
How the Nist Csf Assessment Tool Actually Works in Practice
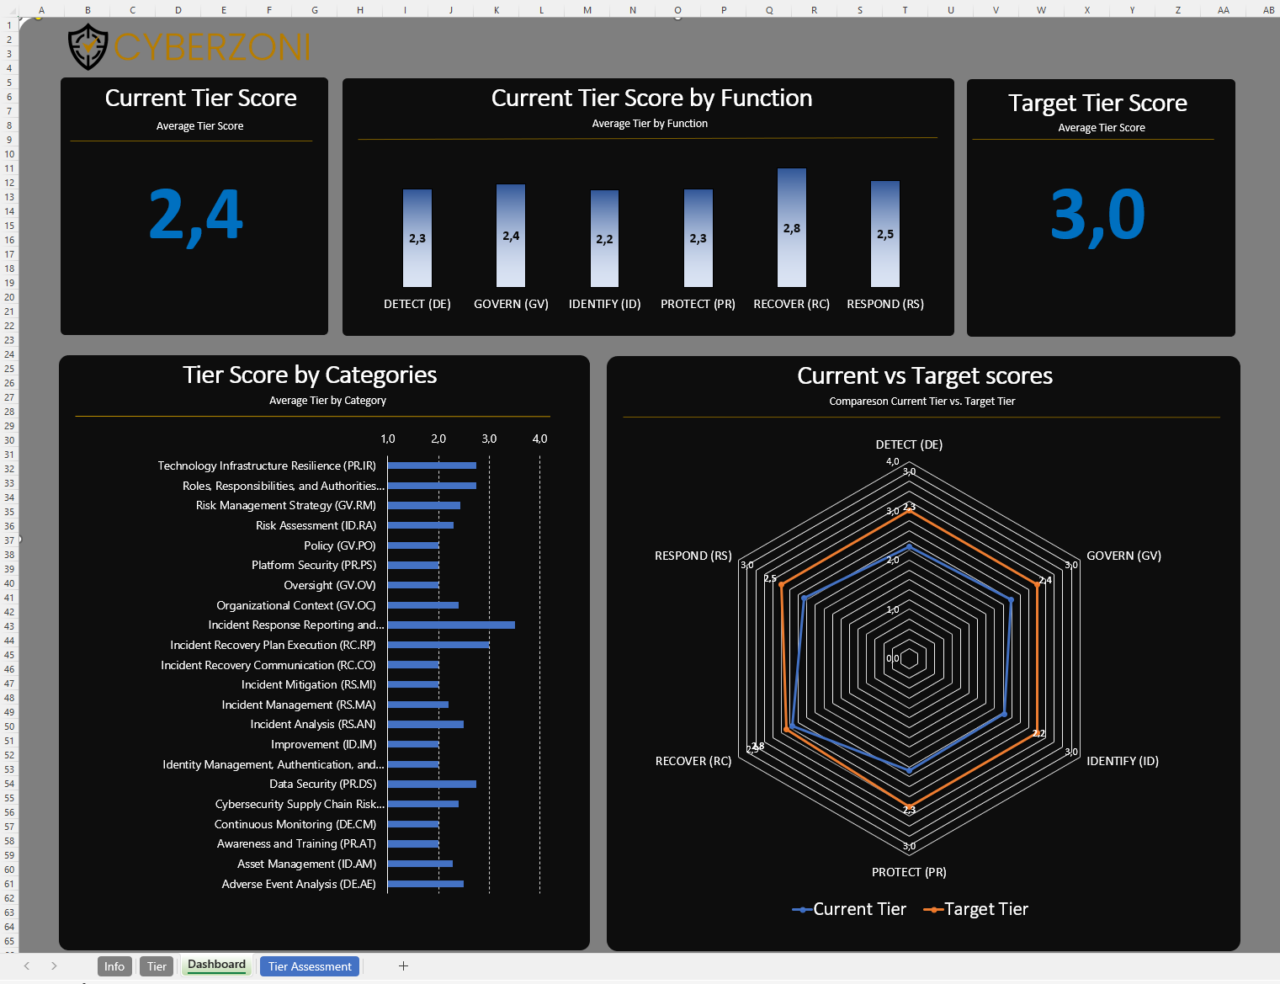
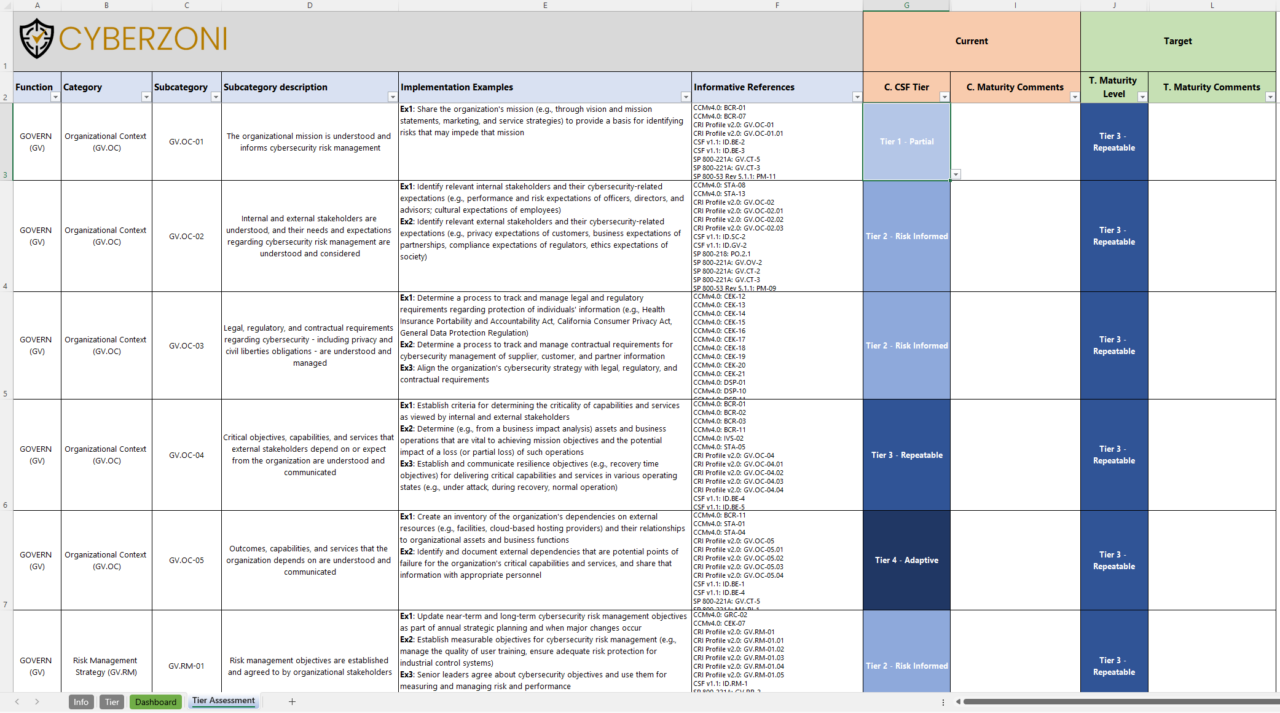
The most common practical approach uses the Profile Conduit as a worksheet. You create a Current Profile by going through every CSF Category and rating how well your organization implements each one on the tier scale. Then you build a Target Profile reflecting where leadership wants you to be. The gap between those two profiles is your improvement roadmap. NIST provides the CSF Correlation Matrix and the accompanying spreadsheets as starting templates, but they are not finished products. You have to adapt them. I spent a few years working with organizations running these assessments and found that the real bottleneck is never the scoring system itself. It's getting honest data. People will rate their detection capabilities as Tier 3 if their SOC runs SIEM queries manually twice a week and considers it sufficient. You need to ask specifically about alert volume, mean time to detect, and whether automated escalation exists before accepting any tier rating at face value.
Building Your Own Assessment Instrument
The most reliable method I encountered involved taking the CSF 2.0 Categories spreadsheet and adding columns for: evidence source, interview participants, actual findings, current tier score, target tier score, risk owner, and a notes field for justification. You don't need a fancy platform. A well-structured Google Sheet or Excel workbook with version control does the job, and it gets reviewed faster because stakeholders can actually open and read it. Here's something NIST documentation glosses over: the subcategory level detail creates an assessment that takes months to complete properly if you try to evaluate everything. One common shortcut that actually works is focusing on the high-risk categories first — the ones tied to your actual threat landscape and regulatory exposure. An organization handling payment card data should weight Decrypt and Access Control subcategories differently than a mid-market manufacturer that primarily faces ransomware risk. Your assessment tool should reflect that weighting from the start, not pretend every subcategory carries equal importance. I ran into a specific edge case with a healthcare client where the standard assessment template flagged their Incident Response subcategories as compliant because they had an IR plan document. The problem was the plan hadn't been tested in eight months, their backup systems failed a restoration drill, and their incident reporting to the board happened quarterly instead of within 24 hours as the framework expects. I stopped using the standard scoring table for that engagement and built a supplemental evidence requirement matrix that forced interview verification and artifact review before any subcategory could receive a Tier 2 or above. It added about three days to the assessment timeline but eliminated the false compliance ratings that the original template was producing.
Get the Full Details
Scoring and Maturity Assessment
The tier system measures process quality, not just presence of controls. A Tier 1 organization has ad hoc, reactive practices. Tier 2 uses some formal policies but relies heavily on individual knowledge. Tier 3 has organization-wide policies approved by leadership. Tier 4 continuously improves and adapts based on lessons learned. This distinction matters because organizations regularly score themselves at Tier 2 when they are actually Tier 1, or claim Tier 3 when their policies exist only in a shared drive nobody reads. When using a Nist Csf Assessment Tool workflow, scoring should always reference concrete artifacts. A password policy document alone gets you a Tier 2 at best. The same policy with documented approval signatures, regular review cycles, and enforcement through technical controls pushes it toward Tier 3. You need to train your assessment team on this distinction before they start rating, or you will get inconsistent scores across different evaluators.
Third-Party Tools and Commercial Alternatives
Several vendors offer tools marketed as NIST CSF assessment platforms. CyberEssentials Plus-aligned tools, SANS assessment frameworks, and commercial GRC platforms like RSA Archer or ServiceNow GRC all claim CSF mapping. None of them are official NIST products. They are commercial interpretations that vary in quality. If you go this route, verify that their framework library actually includes the CSF 2.0 Categories and not just the older CSF 1.1 structure, since NIST significantly reorganized the framework in the 2.0 update released in early 2024. The Profile Conduit spreadsheets from NIST are free and available through the official NIST website at csrc.nist.gov. They remain the most authoritative baseline for any assessment effort. Commercial tools can add value through reporting dashboards and continuous monitoring features, but they cannot replace the actual assessment work of gathering evidence and making judgment calls about maturity levels.
Common Pitfalls to Avoid
The biggest mistake I see is treating the assessment as a one-time event. The CSF is designed for continuous risk management, not annual compliance checkmarks. Organizations that complete a full assessment and then archive the results without maintaining a living profile miss the entire point. A proper assessment cycle should refresh the Current Profile at least quarterly for high-risk categories, and annually for the complete framework. Another pitfall is scoring without stakeholder input. If you assess your organization's governance practices solely by reading policy documents, you will miss the gap between written policy and actual practice. Interview the CISO, the operations manager, and at least one frontline engineer. Their answers will often reveal that the documented process looks nothing like what actually happens. Budget one extra day per functional area for interviews if you want accurate results. The framework also assumes you can clearly identify and prioritize your assets, which many organizations cannot do. A CSF assessment built on an incomplete asset inventory will produce misleading results because the Identify function will appear stronger than it actually is. Fix your asset management first, then reassess.
When the Framework Doesn't Fit
There are scenarios where the NIST CSF approach simply does not work well. Very small organizations with fewer than 50 employees often find the framework too heavy for their size and budget. The assessment itself can consume more resources than the risk it is meant to manage. In those cases, a simplified security controls checklist based on CIS Critical Security Controls tends to be more practical. Sector-specific regulated industries should cross-reference the CSF with their actual regulatory requirements. HIPAA for healthcare, PCI DSS for payment processing, and FISMA for federal contractors each have their own control structures that may overlap with or contradict CSF categories. Running a CSF assessment in isolation without mapping to your regulatory obligations creates gaps in your compliance posture. The assessment process itself requires someone with actual security engineering experience to interpret results. A project manager or compliance officer without technical depth can easily misjudge tier ratings, especially on the Detect and Respond functions where the difference between organizational and adaptive practices involves specific technical capabilities that are not obvious from policy documents alone. Budget for an experienced evaluator, or the scores will be wrong.