How NIST CSF Maturity Assessment Actually Works in Practice
Most people approach the Nist Csf Maturity Assessment like it's a compliance checkbox exercise. It isn't. That's the first thing you need to unlearn. The framework was designed as a living tool for organizations that want to understand where their cybersecurity posture actually stands relative to their risk tolerance. When treated properly, it gives you a map of weaknesses that would otherwise take years to discover through incidents.
What the Maturity Model Actually Measures
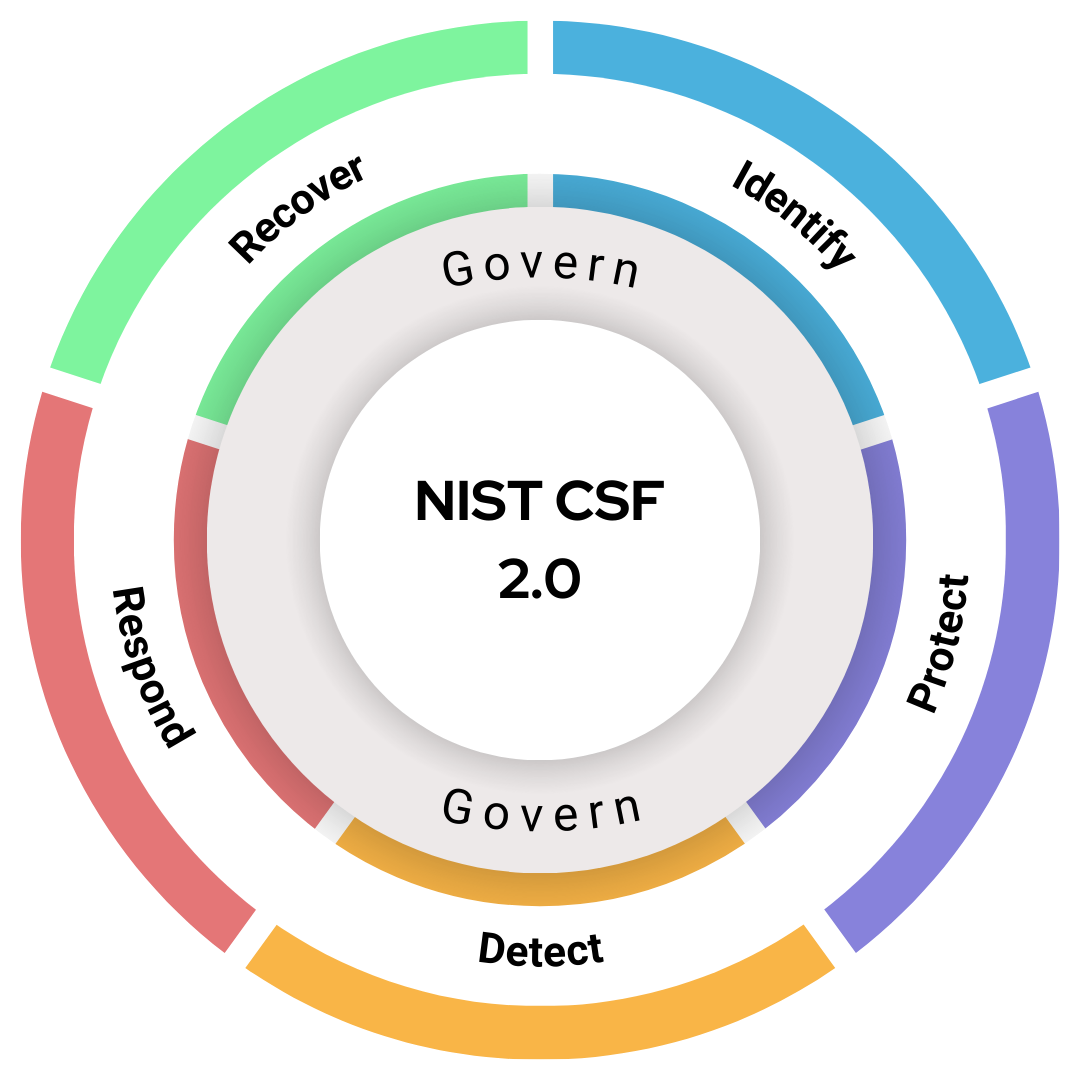
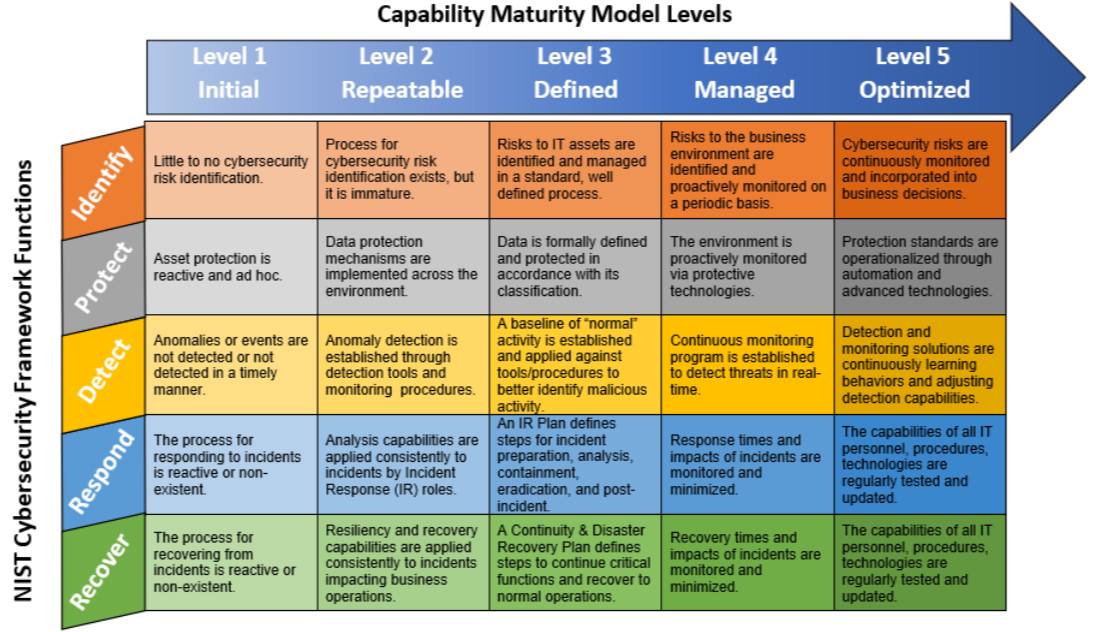
The NIST Cybersecurity Framework organizes cybersecurity activity into six functions: Identify, Protect, Detect, Respond, Recover, and Govern. Within those functions sit 108 subcategories. Each subcategory can be scored at one of three maturity levels: Partial, Informal, or Adaptive.
A Partial maturity score means you have some processes in place, but they're inconsistent or ad hoc. An Informal score indicates you have defined processes that are followed but not yet integrated across the organization. An Adaptive score means your processes are continually improved based on lessons learned and changing threats.
The scoring itself isn't complex. What makes it useful is the evidence you must provide for each score. You can't just claim a subcategory is at Level 3 because someone said so. You need documented procedures, training records, audit trails, and a track record showing the process has been refined over time. This is where most organizations struggle.
I once led an assessment for a mid-size healthcare provider that had spent six months and $80,000 on consulting to "achieve" a Level 2 or higher across the board. The final scores told a very different story. Their Incident Response subcategories were consistently at Partial maturity. They had a plan document, yes, but the last time anyone actually tested it was two years prior, and the contact lists were outdated. The consultant had accepted the existence of a document as sufficient evidence. I rejected it. The gap analysis revealed we needed to run tabletop exercises quarterly, not annually, and update the IR plan after every drill. That changed the trajectory of the entire assessment.
The Assessment Process Step by Step
You start by selecting the scope. This could be the entire organization or a specific division. A narrow scope produces a more accurate picture. A broad scope spreads your efforts thin and makes meaningful improvement harder to track.
Next, you assign an owner to each of the 108 subcategories. These should be people who actually do the work, not managers who delegate it. I've seen assessments derailed when someone from HR owned the Access Control subcategory even though they had no visibility into how provisioning and deprovisioning actually happened.
Then comes the evidence collection phase. For each subcategory, you gather artifacts: policies, procedures, system configurations, logs, training completion records, change management documentation, and post-incident reviews. NIST provides guidance on what constitutes adequate evidence in the CSF Implementation Tiers documentation, but the real standard is whether an external auditor could verify your claims.
You score each subcategory against the maturity criteria. The NIST CSF Profile tool is the official instrument, though many organizations build their own spreadsheets. The scoring should be evidence-driven, not opinion-driven. If you're scoring based on what you hope is true rather than what you can prove, the assessment is useless.
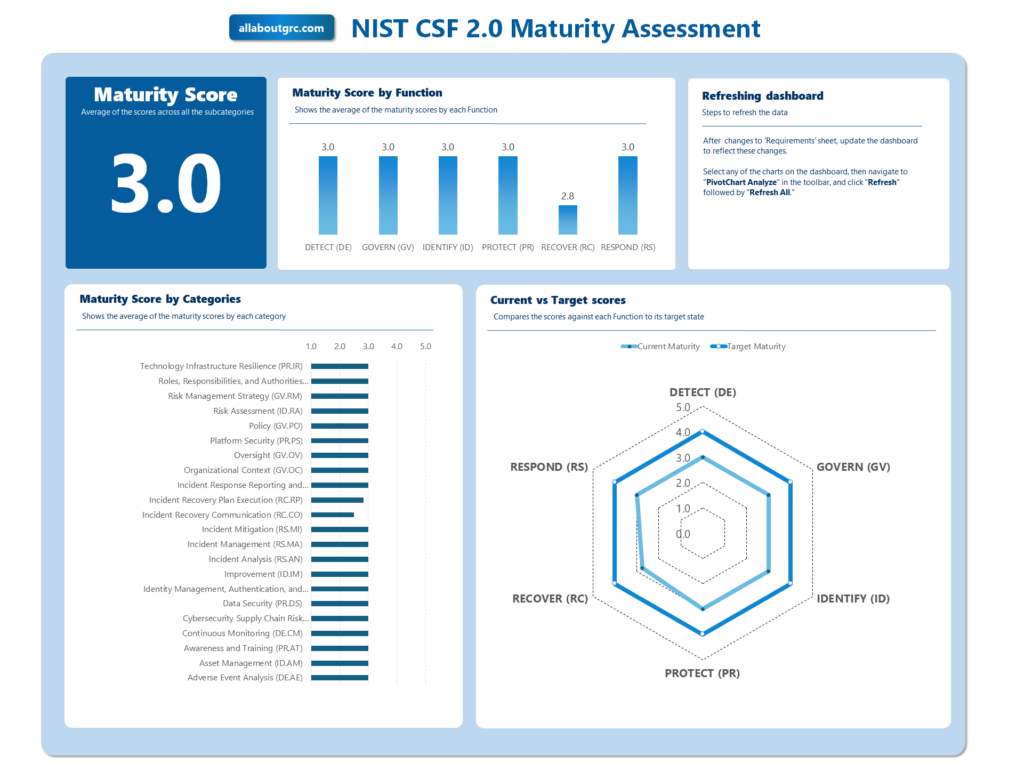
After scoring, you compile a gap analysis. This compares your current maturity levels against your target profile. The target profile should be risk-informed, meaning it reflects your organization's actual threat landscape and business priorities, not an aspirational score that looks good on paper.
Finally, you create an action plan. Each gap gets a remediation task with an owner, a timeline, and a success metric. Without this step, you've just produced a report nobody will read.
Common Pitfalls That Derail Assessments
The biggest mistake I see is treating the assessment as a one-time event. Maturity decays. Processes that were Adaptive six months ago can slip to Informal if staffing changes or leadership shifts priorities. The NIST CSF is designed to be reassessed regularly, ideally annually, with continuous monitoring feeding into the Identify and Govern functions.
Another pitfall is scoring subcategories in isolation. Cybersecurity functions are interdependent. Weaknesses in the Detect function undermine the effectiveness of the Respond function regardless of how mature Respond appears on its own. I've seen organizations score Respond at Level 3 while Detect sat at Level 1, which meant their incident response was sophisticated but rarely triggered because detection was inadequate. The overall security posture was poor despite the impressive-looking scores.
A third mistake is ignoring the Govern function. Before CSF 2.0 was released in 2024, Govern didn't exist as a separate function. Many legacy assessments skip it entirely. Govern covers oversight, risk management strategy, and policy. If you don't have executive-level commitment and documented risk management strategy, every other function loses its foundation. A Level 3 in Protect means nothing if Governance is at Level 1.
When the NIST CSF Maturity Assessment Falls Short
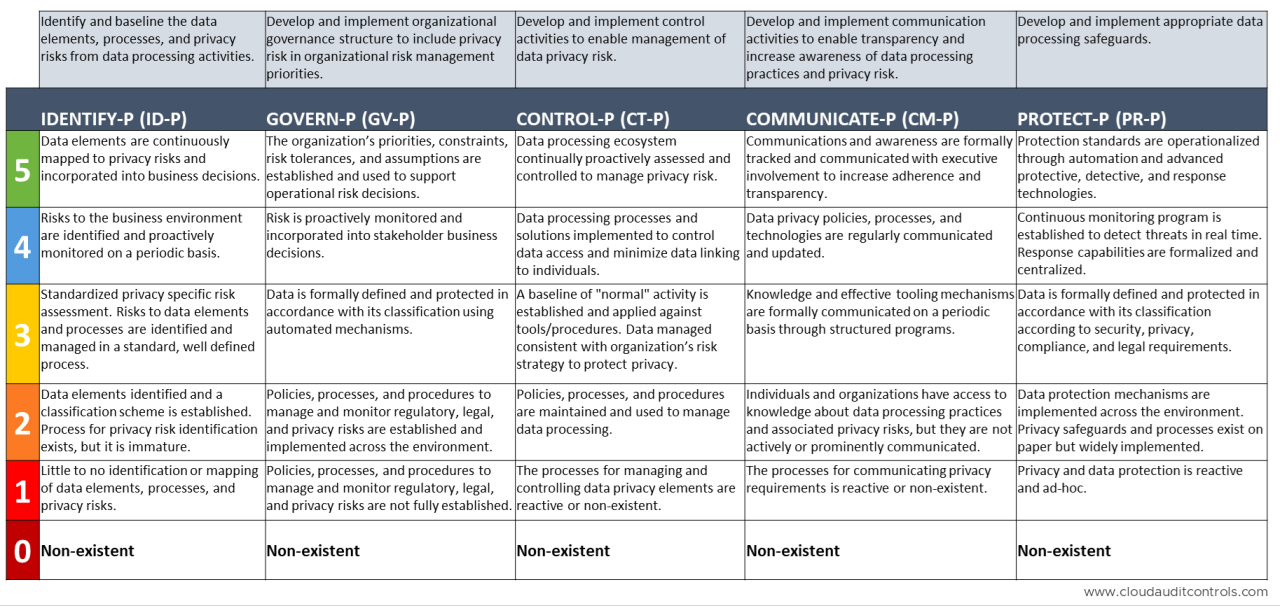
The framework isn't comprehensive. It was never meant to be. It doesn't address supply chain security with the depth that frameworks like SOC 2 or ISO 27001 do. It doesn't cover privacy explicitly—that's the domain of frameworks like NIST Privacy Framework. If your organization needs a certification or is responding to a contractual requirement that demands ISO 27001 alignment, the CSF maturity assessment alone won't satisfy you.
The framework also assumes a level of organizational maturity that smaller organizations may not have. A company with five IT staff members and no dedicated security team will struggle to demonstrate Adaptive maturity in any subcategory, regardless of how competent they are. The framework rewards process sophistication, which takes time and resources to build. In those cases, aiming for Informal maturity with clear documentation and a roadmap toward Adaptive is a more honest and useful outcome.
I've also encountered situations where the assessment was weaponized internally. A security team used a poorly conducted Nist Csf Maturity Assessment to justify a budget increase by inflating gaps that didn't truly exist. The board approved funding based on manipulated scores, and when the next assessment came around, the "improvements" had disappeared. This happens more often than it should. The solution is transparency in methodology and independent verification of key findings.
Practical Tips from Experience
Start small. Pick one or two functions to assess thoroughly rather than attempting all six at once. Identify and Protect typically yield the highest return on effort for most organizations. Once you've established a credible baseline in those areas, expand.
Involve the people who do the work early. Don't assemble evidence after the fact. Have operators, engineers, and analysts participate in the scoring process. Their input catches discrepancies between documented procedures and actual practice that a top-down assessment would miss entirely.
Keep a running evidence library. Instead of scrambling for documentation during an assessment window, maintain a centralized repository where artifacts are stored as they're created. This cuts the evidence collection phase from weeks to days and reduces the temptation to fabricate or stretch the truth about what exists.
Track maturity trends over time. A single assessment is a snapshot. Multiple assessments reveal whether you're actually improving or just moving numbers around. I recommend a minimum of two assessment cycles before drawing conclusions about organizational progress.
Gallery Nist Csf Maturity Assessment
NIST CSF Maturity Assessment | Clearwater
NIST CSF Maturity Assessments - risk3sixty
Why NIST CSF Maturity is Important for All Organizations
Understanding the NIST CSF maturity levels
Nist Maturity Scale _ What is NIST CSF Maturity? – OCEO