What You're Actually Getting When You Download a Nist Csf Risk Assessment Template
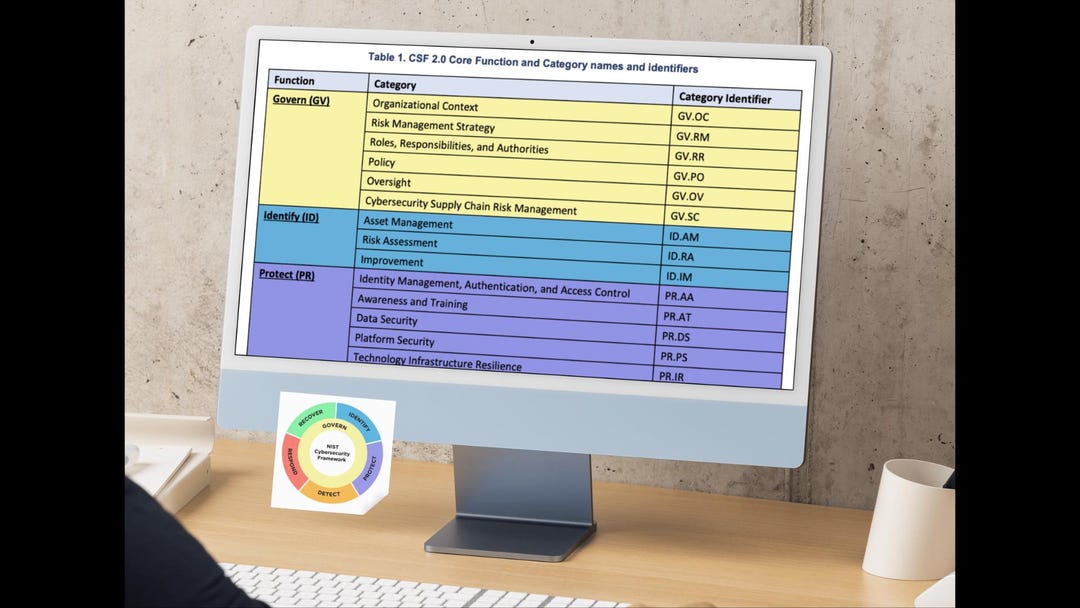
The NIST Cybersecurity Framework provides a structured approach to identifying and managing cybersecurity risk, and the risk assessment template built around it gives you a repeatable way to document that process. It typically includes fields for asset identification, threat sources, vulnerability descriptions, likelihood scoring, impact analysis, and risk treatment recommendations. The framework itself breaks into five functions: Identify, Protect, Detect, Respond, and Recover. Your risk assessment maps directly into the Identify function and feeds into the rest. Most downloadable templates you find online are Excel or spreadsheet-based. They work fine for small organizations but fall apart fast when you have more than fifty assets to track. I ran into this last year when a mid-size healthcare client tried to use a generic template across their entire network. They had over 200 endpoints plus medical devices, cloud services, and legacy systems. The spreadsheet became unmanageable within three weeks. We ended up switching to a dedicated risk management tool that could link assets to controls automatically and generate reports from the underlying data.
Where to Find a Working Nist Csf Risk Assessment Template
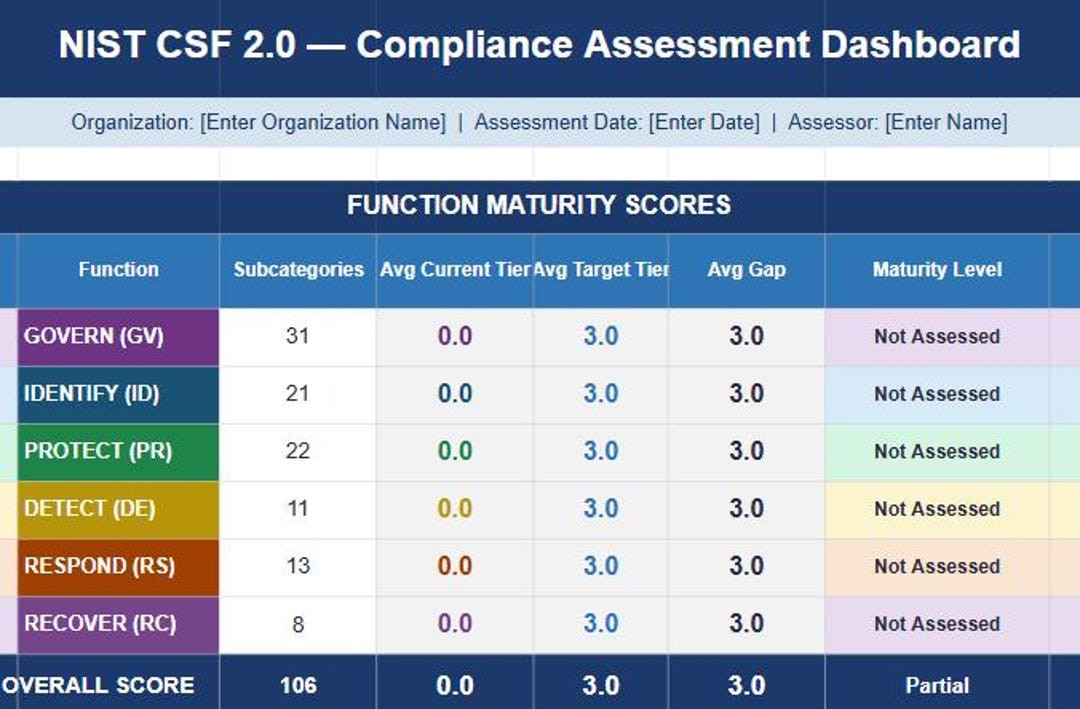
The NIST website itself doesn't host a single official fill-in-the-blank template you can download. What they do provide is the framework core documentation, supplemental guidance documents like SP 800-30, and reference materials. Most templates floating around are built by consultants, integrators, or community contributors who map NIST's categories into usable spreadsheets. The best ones mirror the NIST CSF's 103 categories across the five functions and include columns for current state assessment, target state goals, gap analysis, and priority ranking. I usually recommend starting with the NIST CSF Profile tool available through their website, then supplementing it with a template that fits your operational scale. If you're small enough, a well-structured Excel workbook with separate sheets for asset inventory, threat modeling, vulnerability tracking, and risk scoring will handle most scenarios. Don't overcomplicate it with conditional formatting or complex formulas. You'll spend more time maintaining the template than doing the actual risk assessment.
How to Actually Use It Without Wasting Two Weeks
The biggest mistake I see is treating the template as a form to fill out rather than a living document. You don't complete a risk assessment once and file it away. Here's how the process normally goes and where things typically break down. Step one is scoping. Define what systems, processes, and data assets you're assessing. This sounds obvious but most people skip straight to filling in risk registers without establishing boundaries first. A vague scope leads to incomplete assessments and gives stakeholders a false sense of security. Step two is asset identification and valuation. List every asset within scope, categorize them, and assign business value. Critical assets get prioritized. In my experience, business value assignment is where most teams stumble because they don't have clear criteria for what "critical" actually means. I use a simple scoring model based on confidentiality, integrity, and availability impact. Each gets a score of one to five, and the product gives you a composite value. It's not fancy but it cuts argument time in meetings significantly.
Get the Full Details
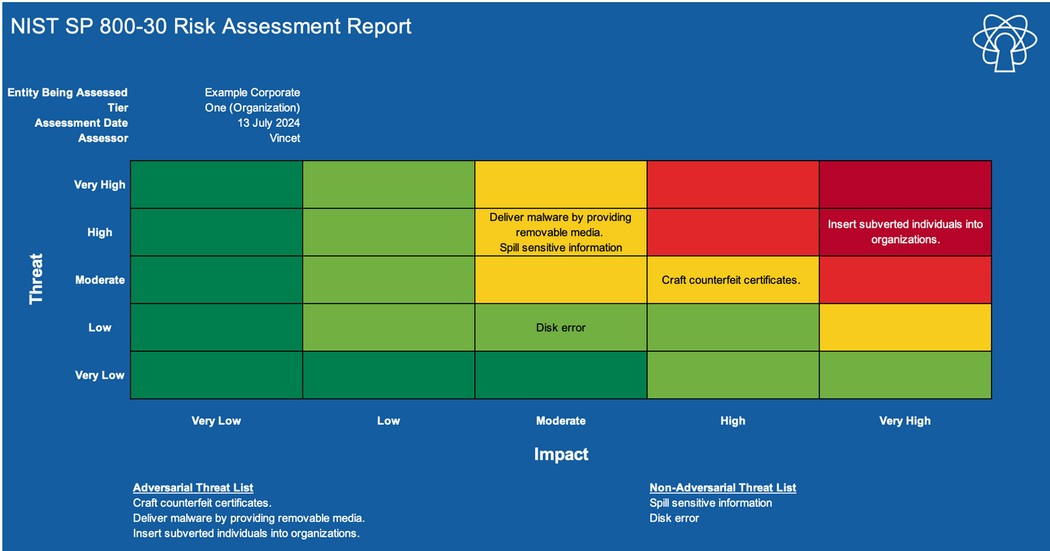
Step three is threat and vulnerability analysis. For each asset, identify relevant threat sources and existing vulnerabilities. Threat sources under NIST CSF include environmental threats, insider threats, and external malicious actors. Vulnerabilities are gaps in your controls. Cross-reference these against the NIST Control Correlation Set if you want mapping to specific controls. This step usually takes longer than anything else because you need access to vulnerability scan data, penetration test results, and sometimes manual review of configuration baselines. Step four is likelihood and impact determination. Rate each identified risk on a scale, typically one to five for both likelihood and impact. The resulting risk score is the product of those two numbers. Simple multiplication works for most situations. I've seen organizations use more complex probabilistic models, but the difference in decision quality is negligible compared to the effort required. Most stakeholders don't need Bayesian networks. They need to know which risks to address first. Step five is risk treatment and documentation. Each risk gets a treatment recommendation: accept, mitigate, transfer, or avoid. Mitigation maps to specific NIST CSF categories and subcategories. This is where the template really shows its value because it forces you to connect risk findings to actionable controls rather than leaving everything as abstract concerns.
Things No Template Will Tell You
Here's a counter-intuitive point that catches people off guard: your risk assessment is only as good as your asset inventory. I've reviewed assessments from companies that had thorough risk registers but were missing entire categories of assets. One engagement I worked on had a complete assessment of their Windows infrastructure and cloud services, but they'd entirely overlooked their industrial control systems in the manufacturing plant. The risks there were far more significant than anything in IT, yet they had zero entries in their register. A template can remind you to assess assets, but it can't discover assets you haven't accounted for. Another thing that's easy to miss: likelihood ratings tend to be inconsistently applied across different teams and departments. One group rates a vulnerability as "high likelihood" because they read a recent news article about a similar exploit. Another group rates the same vulnerability class as "low likelihood" because their patch management cycle is shorter. Without a standardized definition for each likelihood level, your risk scores become meaningless comparisons. I usually define each level with specific criteria tied to real-world indicators like CVE age, exploit availability, patch status, and threat intelligence feed data. The framework also doesn't handle dynamic risk very well. A risk assessment based on a snapshot in time becomes outdated the moment a new vulnerability is disclosed or a system changes configuration. Some organizations try to work around this with continuous monitoring tools that feed data back into the risk register automatically. Others accept that quarterly reassessment is the practical minimum. There's no universal answer here.
Common Pitfalls to Avoid
Using qualitative scales without documented definitions is probably the most destructive mistake. Saying a risk is "medium" means nothing if two people interpret that word differently. Write down exactly what each rating level represents and reference those definitions every time you score a risk. Another pitfall is assessing risk at the wrong granularity. If you assess at the organizational level only, you miss system-specific risks. If you assess at the individual server level only, you lose sight of systemic risks that span multiple systems. I typically recommend a hybrid approach where you assess at the business process level first to understand critical functions, then drill down into the systems that support those functions. Finally, don't let the template dictate your conclusions. Some templates push you toward scoring every possible risk with the same methodology. That doesn't work when you're dealing with fundamentally different risk types. A data exfiltration risk and a power supply failure risk require different assessment approaches even though both fall under the same NIST CSF category. The template should guide your thinking, not replace it.
When This Approach Doesn't Work
The NIST CSF framework assumes you have a reasonable understanding of your environment. If you're a startup with rapidly changing infrastructure, the framework's structure can feel rigid and slow. In those cases, some organizations find more value in lightweight approaches like the Center for Internet Security's Critical Security Controls, which are more prescriptive and easier to implement incrementally. There's also the FAIR model for organizations that want quantitative risk analysis rather than qualitative scoring. If your organization lacks basic asset discovery and vulnerability management capabilities, jumping straight into a full NIST CSF risk assessment will produce poor results. You need foundational cybersecurity hygiene before the framework adds value. Spend time getting your asset inventory accurate and your patching cadence established first. Then the risk assessment template becomes a useful analysis tool rather than just another compliance checkbox. The template itself costs nothing to download from most sources. The real investment is the time required to populate it accurately and keep it current. Budget accordingly.