How the Nist Csf Self Assessment Tool Actually Works
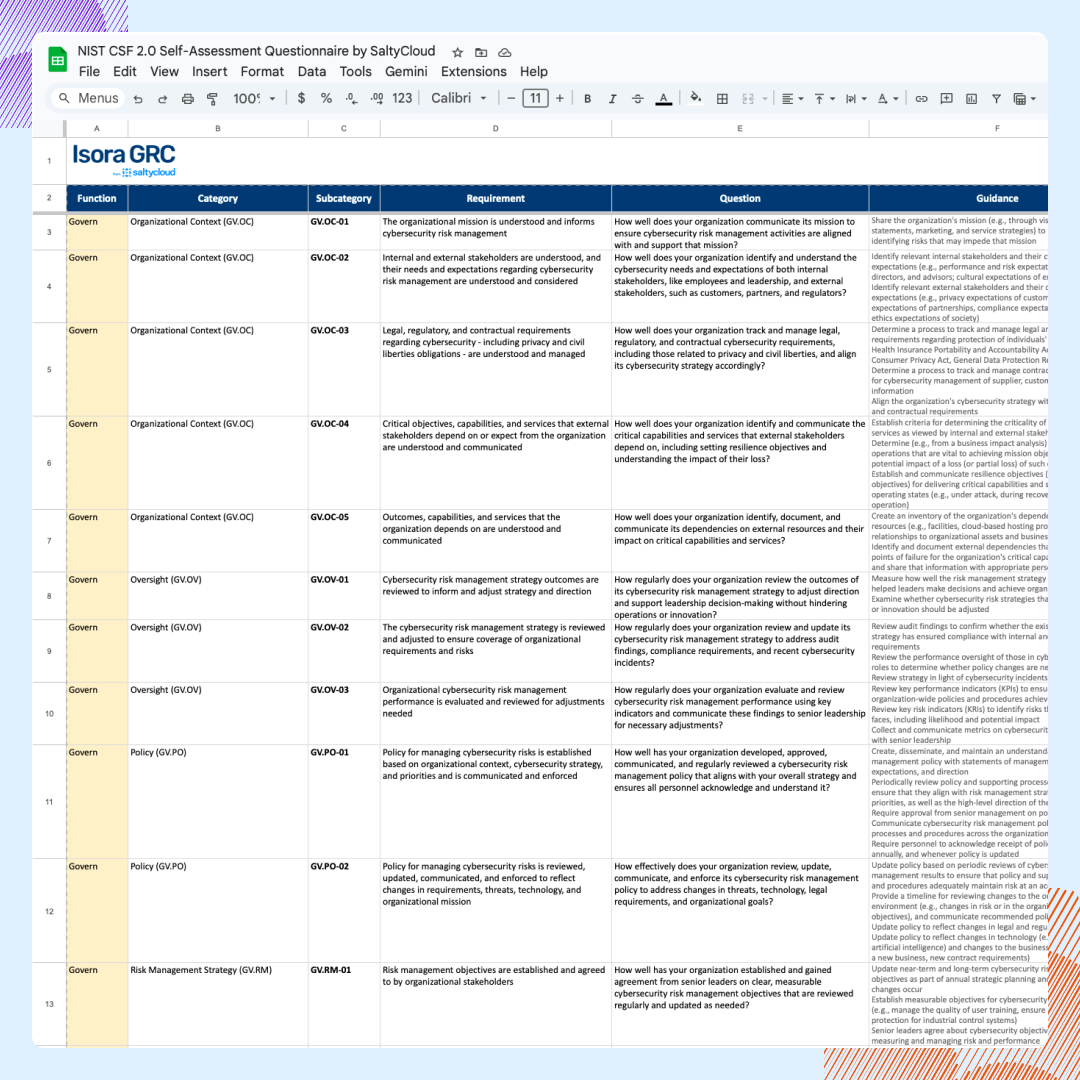
The NIST Cybersecurity Framework (CSF) provides a structured way for organizations to evaluate their cybersecurity posture. The self-assessment tool is one of several resources released by NIST to help teams perform these evaluations without needing an expensive consultant. It functions as a questionnaire-based instrument that maps your current controls against the framework's categories and subcategories. Most people grab the tool expecting it to walk them through everything step by step. That is not quite how it works. The tool gives you a structured survey format. You answer questions based on what your organization currently does. Then it cross-references your responses against the NIST CSF taxonomy and generates a profile showing where you stand relative to the framework's tiers. The output is a gap analysis, not a remediation plan.
Getting Started with the Nist Csf Self Assessment Tool
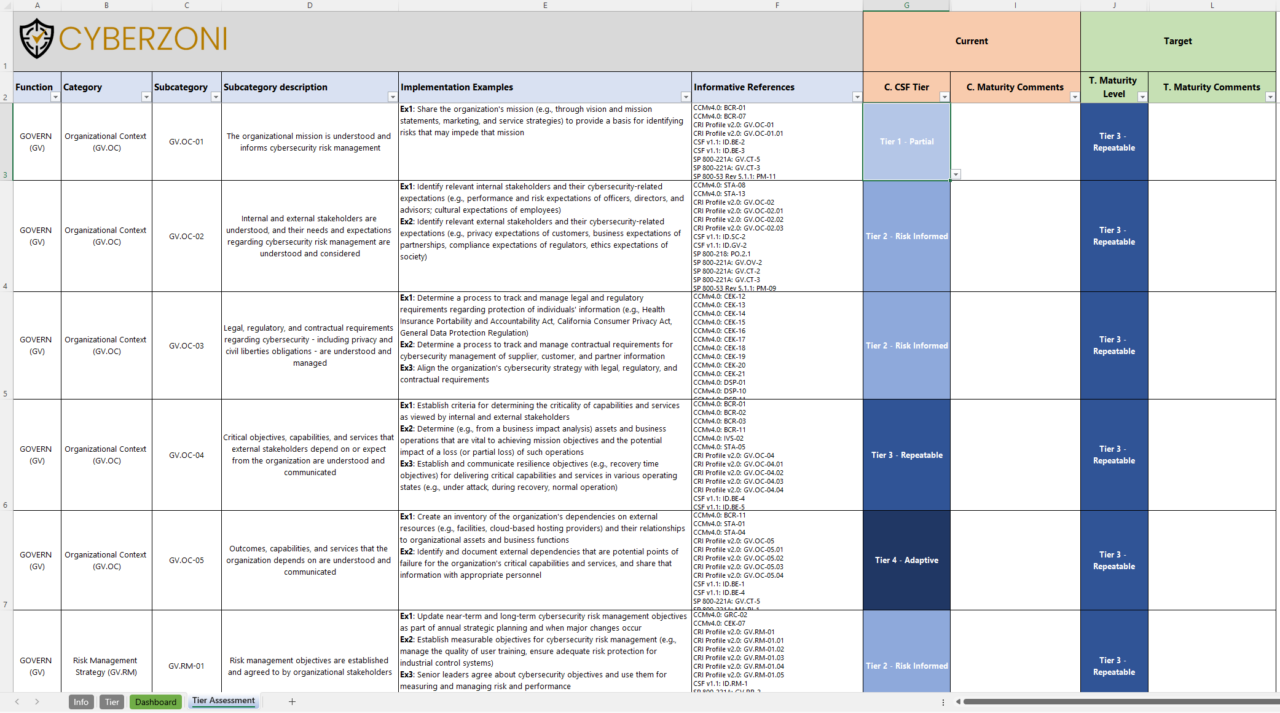
You can download the current version from the NIST website. The tool typically comes in spreadsheet format, sometimes as a standalone application depending on which iteration you find. Once you have it, open it and familiarize yourself with the layout. There is usually a response sheet where you input your answers, followed by a profile sheet that auto-populates based on your inputs. Here is what most people miss when they start: the tool does not tell you what a "Tier 1" or "Tier 2" risk management process means in practical terms. You need to understand the four tiers independently before the tool's scoring means anything to you. Tier 1 is Partial, where policies may not exist formally. Tier 2 is Risk Informed, where leadership is aware of cybersecurity risks but approaches are ad hoc. Tier 3 is Repeatable, where formalized processes exist and are consistently applied. Tier 4 is Adaptive, where you continuously improve based on lessons learned and changing threats. Getting the right tier requires honest answers, not aspirational ones. I ran into a specific issue last year when a client tried to use the tool for a SOC 2 readiness assessment. They were answering questions based on what their policies said on paper, not what actually happened day to day. The resulting profile looked impressive, but when I dug into their incident response logs, the reality was significantly different. The workaround was straightforward: I required them to interview at least three people per department before filling out any responses. The tool measures organizational practice, not document existence. Paper policies and actual practices are two different things, and the assessment reflects whichever one you honestly report.
Common Pitfalls That Skew Your Results
The biggest problem I see is conflating the NIST CSF with the 800-53 control catalog. They share DNA but serve different purposes. NIST 800-53 is prescriptive. It tells you exactly what controls to implement. The CSF is outcome-focused. It describes what effective cybersecurity looks like without dictating how to achieve it. Using the self-assessment tool as if it were a compliance checklist will give you misleading results because the framework is intentionally flexible. Another frequent error involves the Scope section. The tool asks you to define what is in scope for your assessment. If you leave it blank or define it too narrowly, your profile becomes meaningless for decision-making purposes. I once saw a mid-sized company define their scope as only the corporate HQ network, excluding cloud infrastructure and remote workforce endpoints. Their assessment showed a respectable maturity level, which turned out to be completely inaccurate given how much of their operations had migrated to cloud services over the previous two years. Define your scope broadly enough to cover all material systems, or the results will mislead you. The tool also does not account for regulatory requirements outside the CSF itself. If your organization is subject to HIPAA, PCI DSS, or state-specific breach notification laws, the self-assessment will not flag gaps in those frameworks. It only evaluates against the NIST CSF. You need to layer your regulatory obligations on top of the assessment results, not assume the tool covers everything.
Get the Full Details

What to Do With the Results
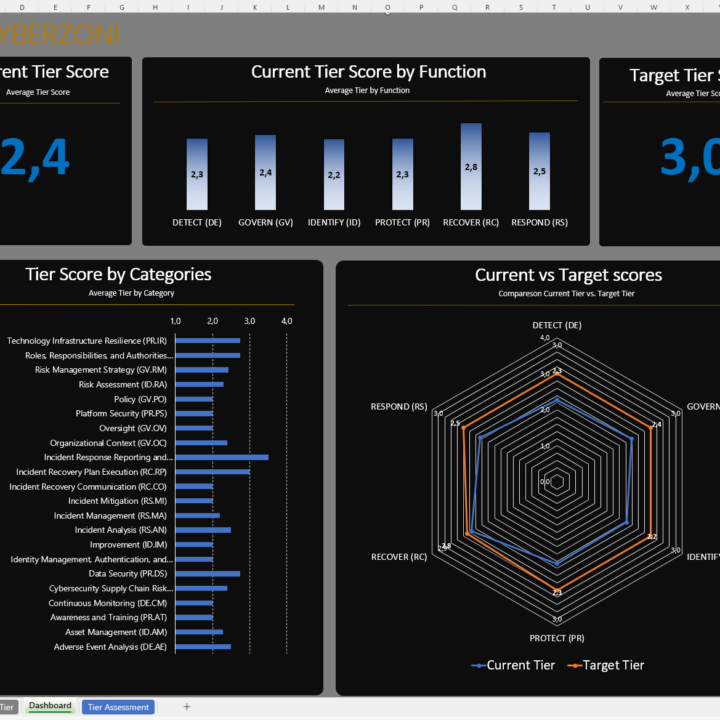
After you complete the assessment, you will have a current state profile and optionally a target state profile. The difference between those two profiles is your remediation roadmap. But here is the thing: the tool does not prioritize gaps for you. It does not tell you which controls matter most based on your specific risk landscape. That decision requires judgment from someone who understands your business context. I recommend taking the output and mapping it against your actual threat intelligence and business impact analysis. A control that scores low on the assessment might be critical for your organization if you handle sensitive health data. Another control that scores well might be irrelevant if you do not operate in an industry where that specific threat vector exists. The numbers from the tool are a starting point, not a conclusion. The assessment should also be repeated periodically. I have seen organizations treat a single completion as a permanent achievement. The framework and your environment both change. Reassessing every six to twelve months keeps the profile current and gives you a trackable record of improvement over time. Some teams spread this out to annual cycles, which is acceptable for smaller organizations with stable environments. For faster-moving teams, quarterly check-ins on the high-risk categories are worth the extra effort.
One more thing worth noting: the tool is free and openly available, which is one of its real advantages. But do not treat it as a substitute for a thorough internal audit or an external assessment. It is a self-reported instrument by design, and self-reporting always carries the risk of optimism bias. Use it as one input among several when making investment decisions about your security program.