Mapping the Nist Cybersecurity Framework Financial Services Landscape
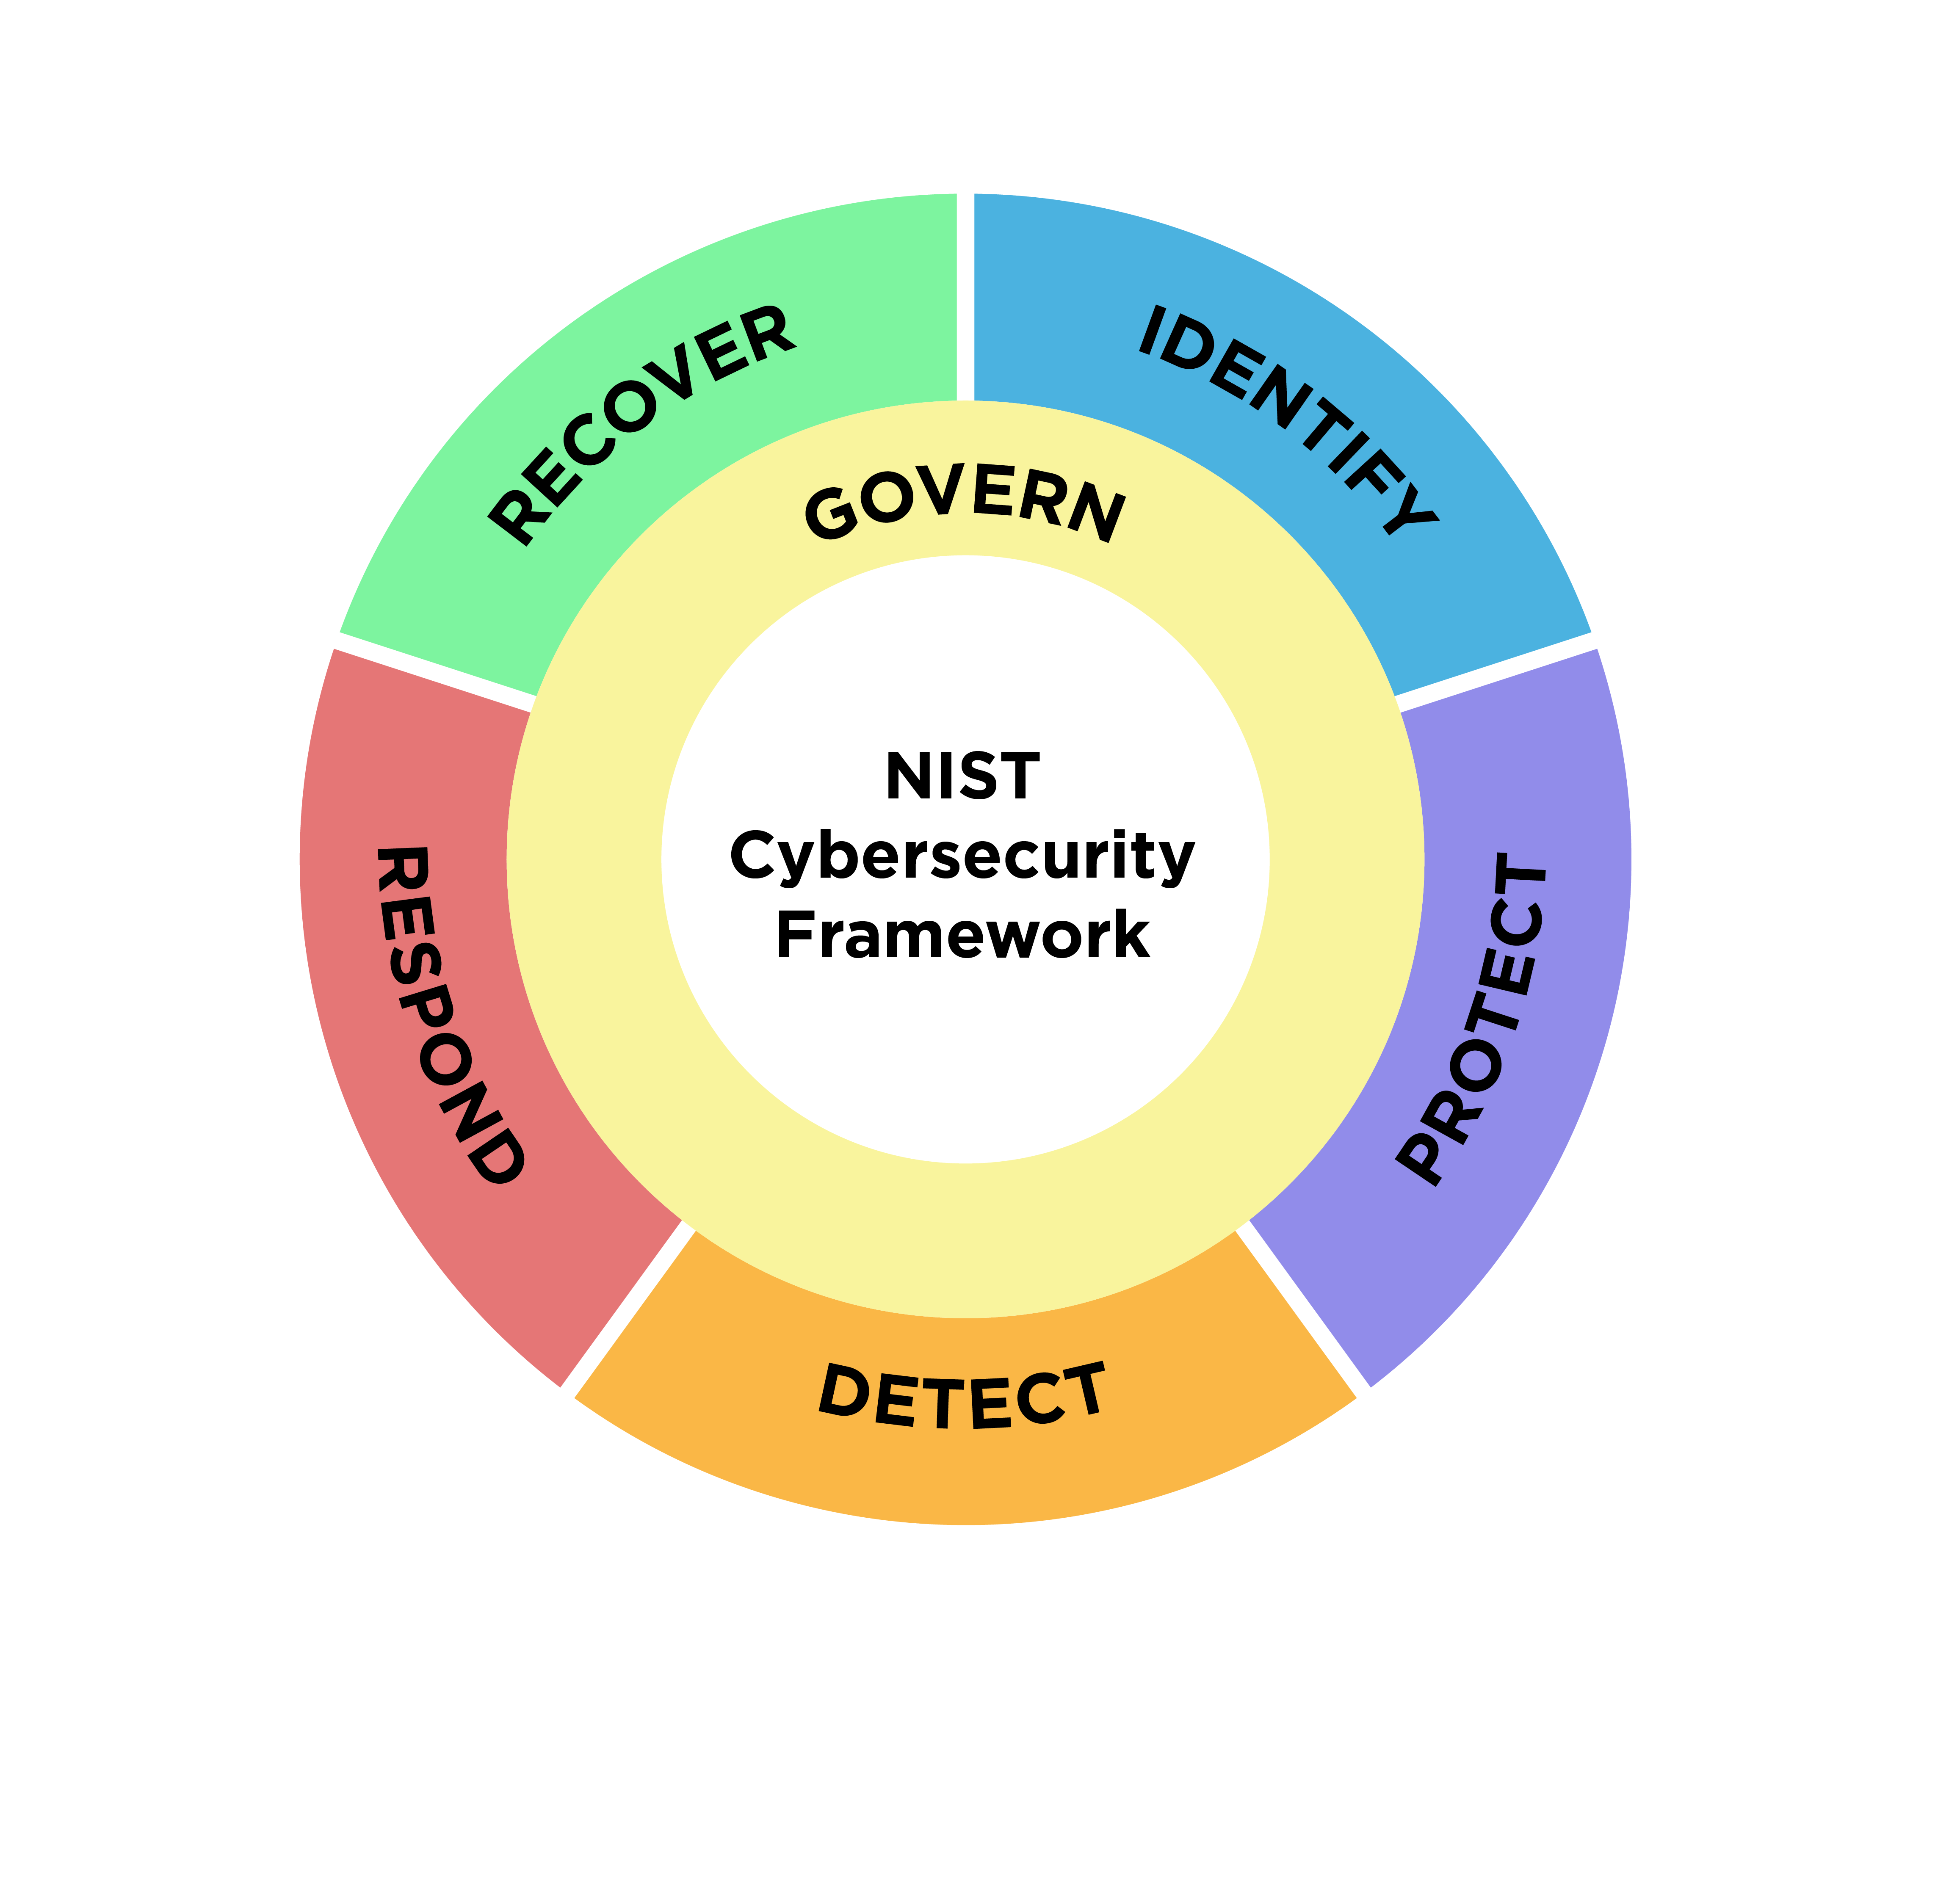
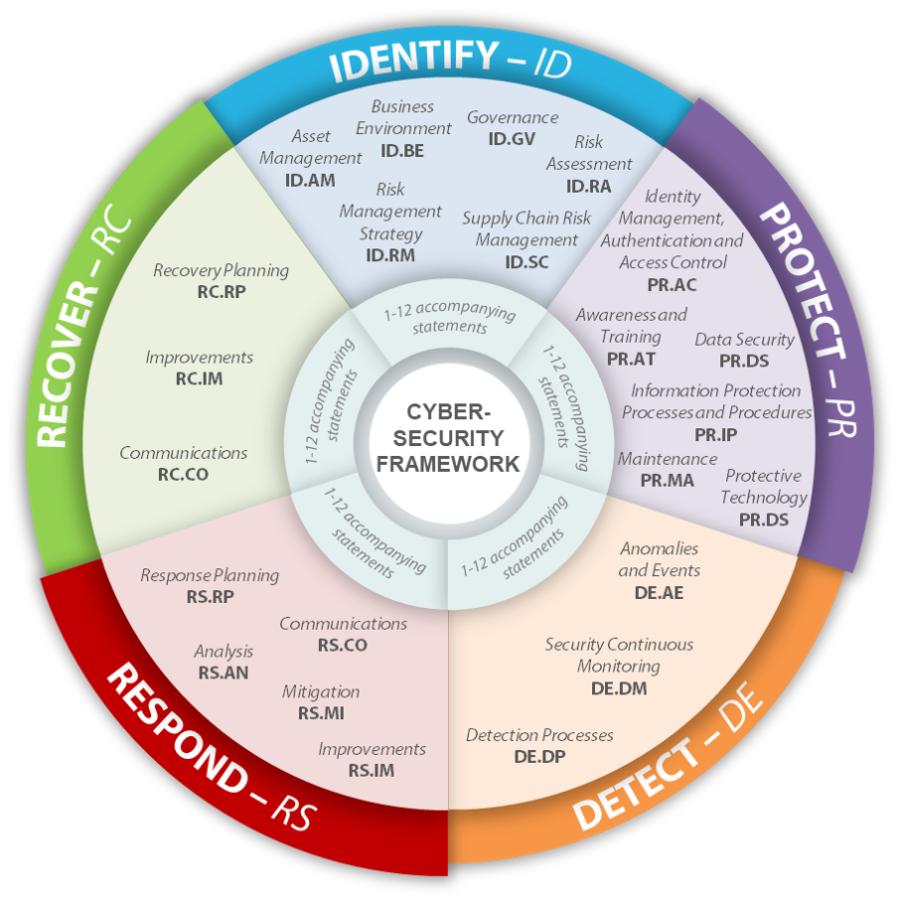
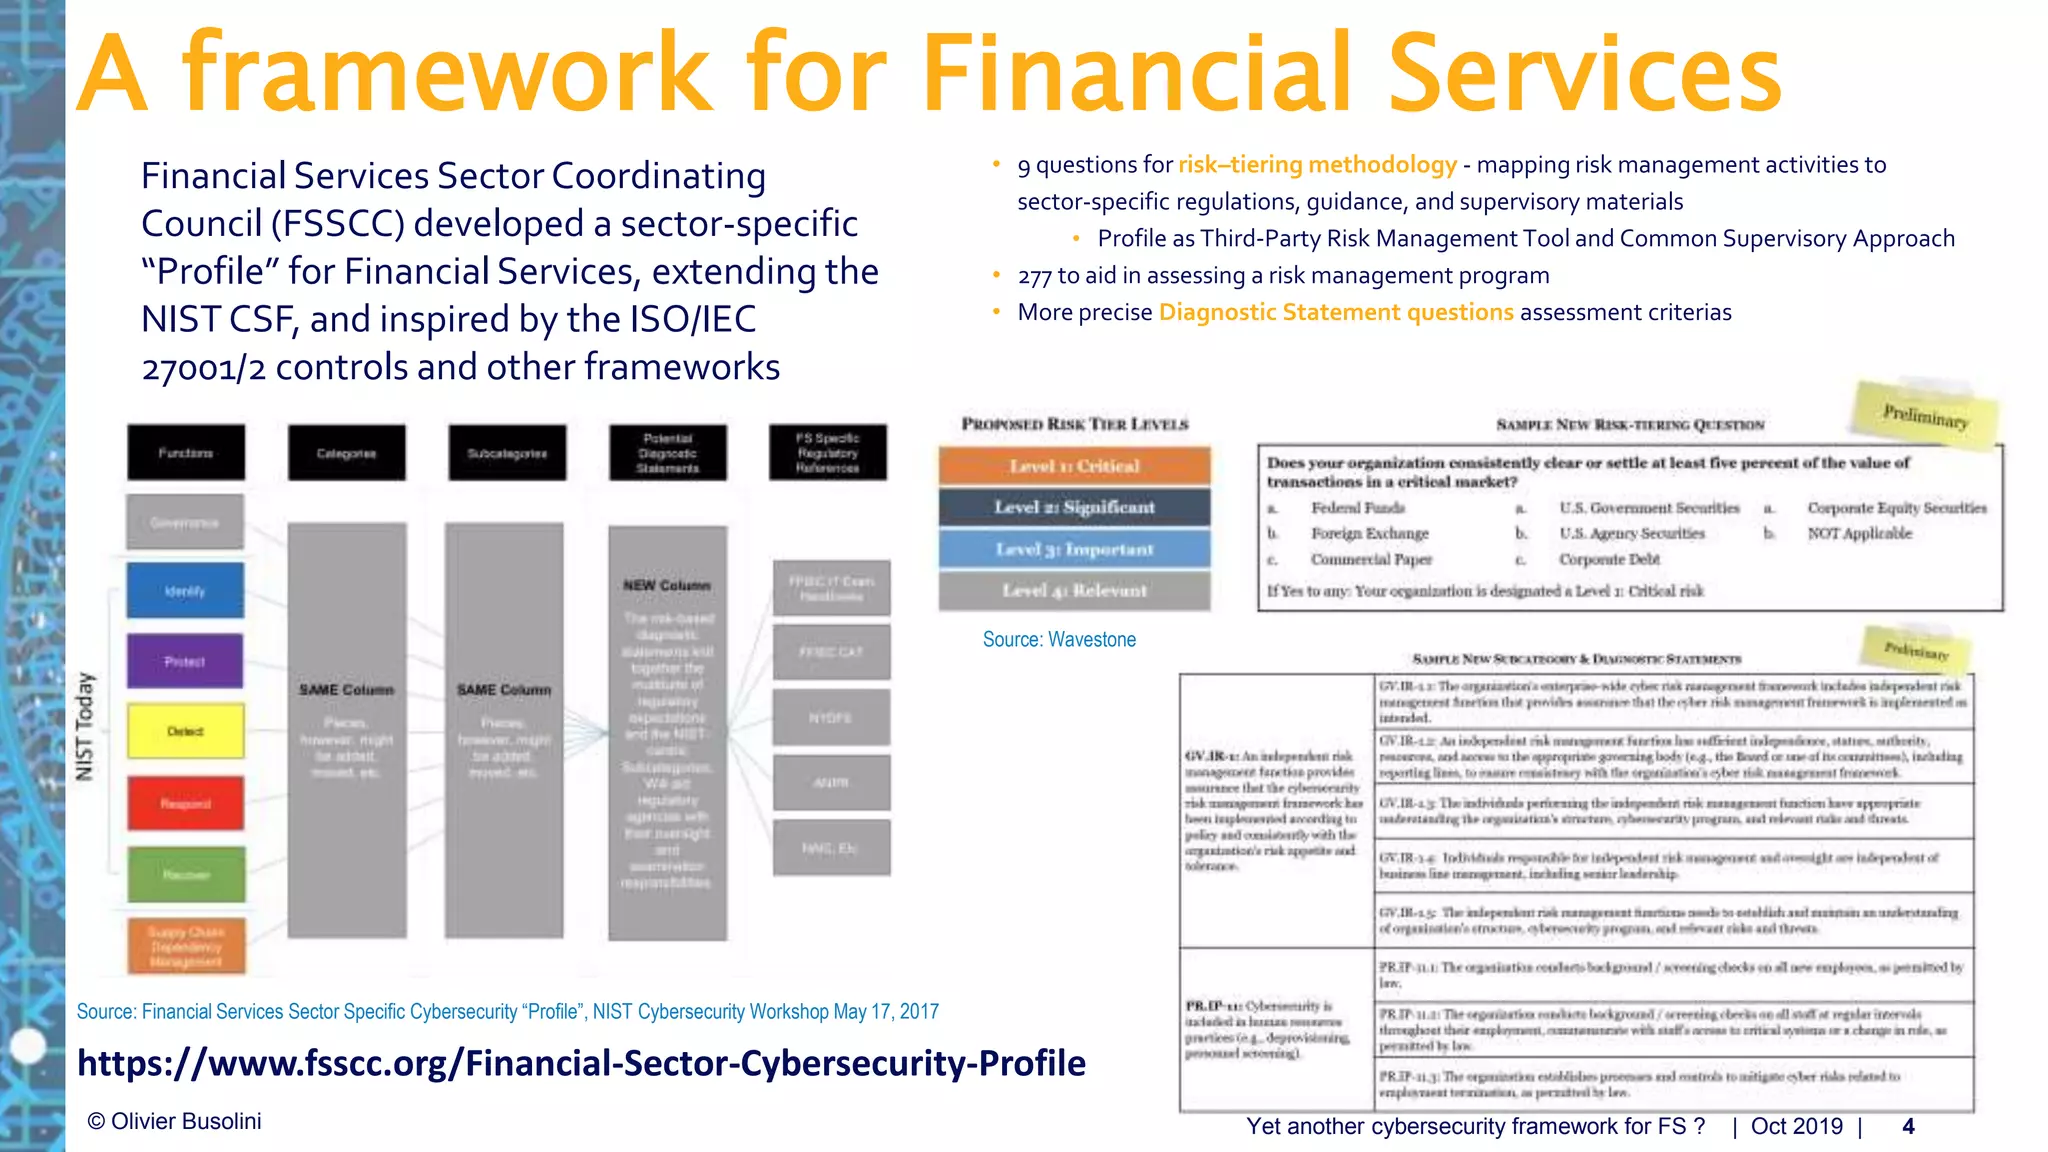
The NIST Cybersecurity Framework (CSF) isn't a compliance checkbox for financial institutions. It's an operational taxonomy that most banks and credit unions use to translate regulatory pressure into something their security teams can actually work with. The framework itself is voluntary at the federal level, but state-level regulators, FFIEC examiners, and the SEC's new cybersecurity disclosure rules make it functionally mandatory for anyone handling consumer financial data. Most people encounter the CSF through the 2014 or 2023 versions. The core structure hasn't changed much between those releases. Five functions: Identify, Protect, Detect, Respond, Recover. Under each function sit categories and subcategories. For a community bank, you might focus on ID.BE (enterprise beliefs and environment), PR.AC (access control), and DE.CM (continuous monitoring). A payment card processor would weight PR.DS (data security) and RS.RP (response planning) much heavier. The framework doesn't tell you which controls to implement. That's the common misunderstanding. It tells you what outcomes you should be achieving, then maps existing standards like NIST 800-53, ISO 27001, PCI DSS, and FFIEC CAT to those outcomes. Your job is cross-referencing.
I spent about three weeks last year trying to get a mid-size regional bank's board to accept that mapping the CSF to their incident response plan wouldn't fix their actual detection gaps. They wanted to hand the framework to the compliance vendor and move on. We ended up spending more time on gap analysis than any formal documentation. The practical reality is that a CSF assessment takes most organizations about 40 to 60 hours for a basic Tier 1 or 2 alignment. If you're already running an SOC with SIEM rules tied to ATT&CK, expect 80 to 120 hours because someone has to validate that the coverage actually exists on the ground. The 2023 update introduced the Tiers, which clarify implementation maturity from Partial (Tier 1) to Adaptive (Tier 4). This matters more for financial services than most people realize. FFIEC exams and SEC Regulation S-K disclosures both effectively require you to demonstrate at least Tier 2 awareness and Tier 3 execution for material cybersecurity risks. A Tier 1 self-assessment on paper won't survive a regulatory interview where they ask about continuous monitoring programs. Here's something nobody warns you about during the initial mapping: the CSF's Function 3 (Detect) overlaps significantly with SOX IT general controls, especially around change management logging. If your bank does both Sarbanes-Oxley and FFIEC compliance, the same access review controls cover both frameworks. You can consolidate that evidence collection. Most teams don't realize this until they're deep into audit season and realize they've been doing parallel work for the same evidence.
Another thing that trips people up is the Recover function. Almost every financial institution skips over RC.RP (recovery planning) and RC.IM (improvements). They treat recovery as DR/BCP territory and forget that the CSF expects documented lessons-learned after every significant incident. I worked with a credit union that got cited by their state regulator for having no formal post-incident improvement cycle. They had the technical controls in place but couldn't show they were learning from failures. The fix was straightforward, but it required a process change, not a technology purchase. If you need the actual framework documents, they're free at nist.gov/cyberframework. The 2023 version includes the Profile implementation tool, the tier definitions, and the mappings to over two dozen other standards. The CSF 2.0 supplement for the financial sector came out in 2024 and adds sector-specific considerations around payment system resilience and real-time fraud detection integration. The main limitation of the framework is that it doesn't address third-party risk directly. FFAR and DORA-style vendor oversight falls outside its scope unless you fold it into the Identify function manually. Several financial institutions I've spoken with supplement the CSF with a third-party risk management program built on SIG questionnaires and continuous monitoring feeds. The NIST guide for supply chain security (SP 800-161) pairs reasonably well with it.
Get the Full Details

The other practical constraint is that the CSF produces a risk profile, not a risk score. The profile shows where you are relative to where you want to be. It doesn't quantify dollar exposure or help you prioritize which gaps cost the most to leave open. For that, you need either FAIR analysis or a custom risk scoring model. I've seen some firms try to force the CSF into a quantitative framework and it creates more confusion than it solves. Keep them separate. For implementation, start with the Identify function and build a current state profile before touching anything else. Most teams jump straight to Protect because it's where the budget lives, but without a clear Identify baseline, you're just documenting controls that may not align with actual business risks. Use the CSF Promising Practices Guide to avoid some of the common misalignments. It's free and covers the stuff that usually goes wrong during first implementations.