Building a Policy That Actually Maps to the NIST CSF
Most people open the NIST Cybersecurity Framework and immediately reach for a template. That is usually the wrong starting point because a policy written to satisfy a framework looks nothing like a policy written to solve your actual problems. I spent three years helping mid-size organizations try to get through audits without rewriting their security documentation every eighteen months, and the single biggest friction point was always the gap between what the framework asks for and what a policy template actually provides. A template guide is meant to give you a structural starting point so you are not staring at a blank document when the compliance team asks for updated policy language. The CSF Core has three layers: the tiers that describe how well an organization implements the framework, the functions which are Identify, Protect, Detect, Respond, and Recover, and the categories and subcategories underneath each function. A good template aligns your policy headings to those subcategories while leaving room for the organization-specific details that auditors will actually check during an interview. I have seen organizations import a generic template and then spend six weeks mapping controls afterward. If you align your policy sections to the subcategory level from the start, you cut that effort down to about two days for a typical small-to-medium environment. The catch is that the CSF does not mandate any specific policy format. NIST only expects you to demonstrate that you have implemented the relevant subcategories at an appropriate tier level. That means the template should be a crosswalk document as much as a set of policy statements.
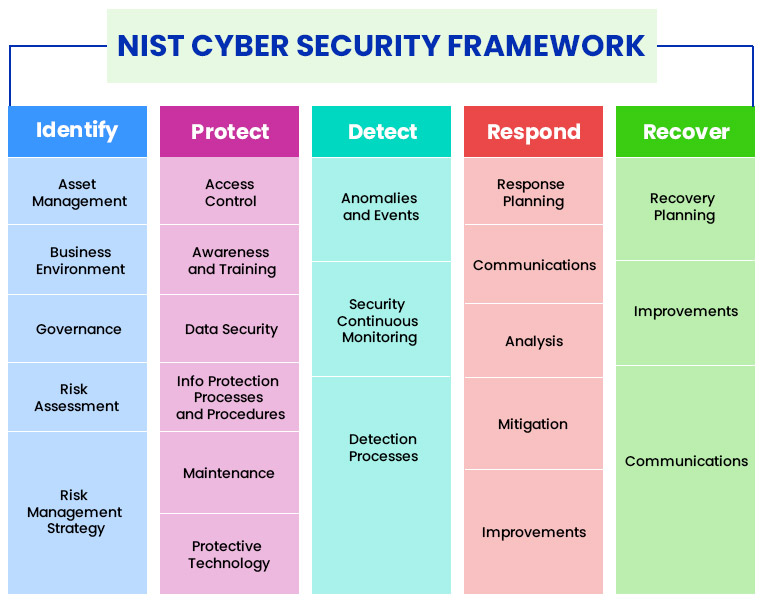
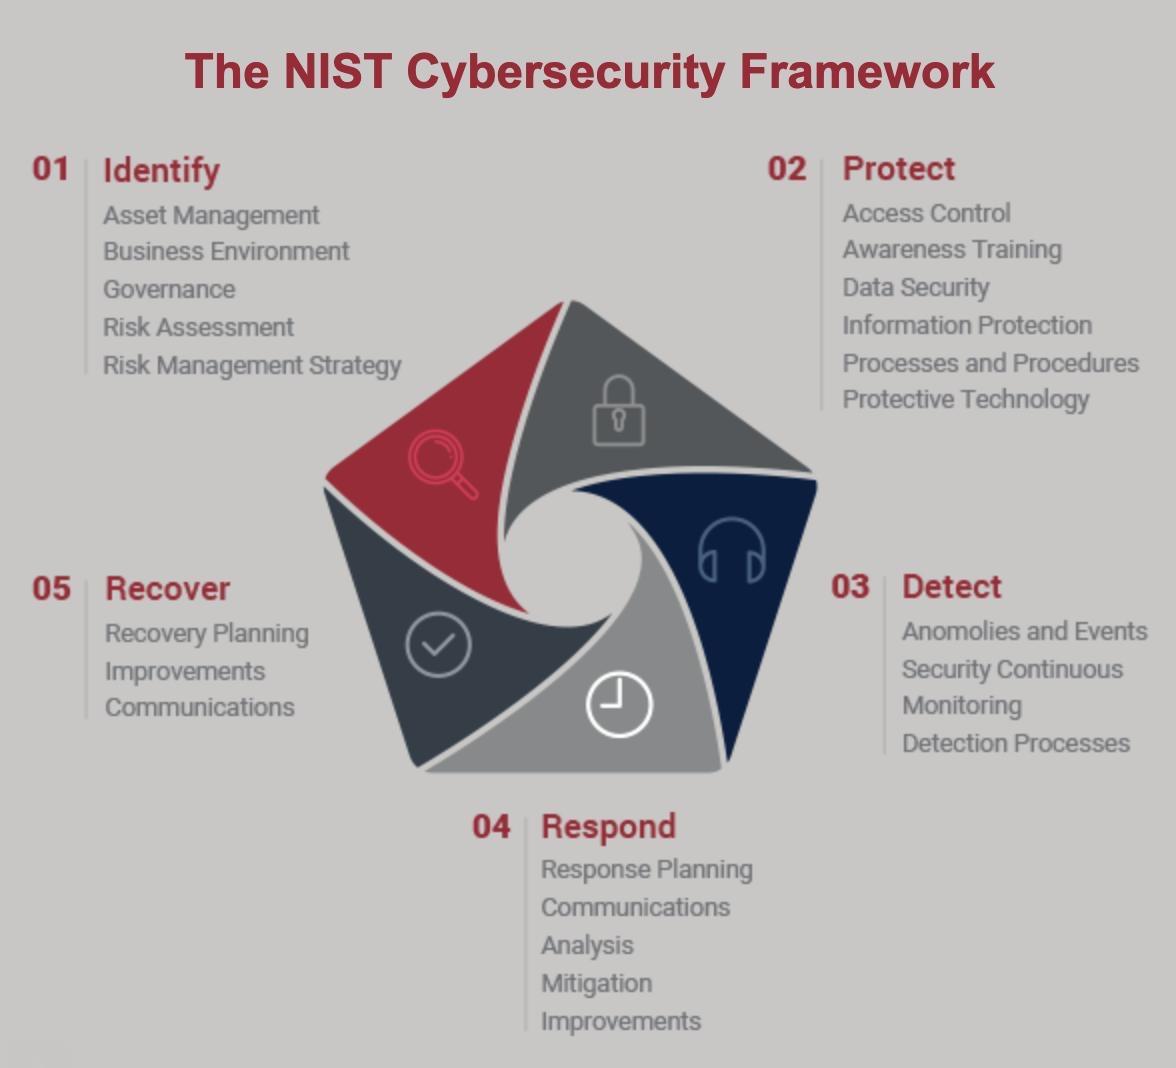
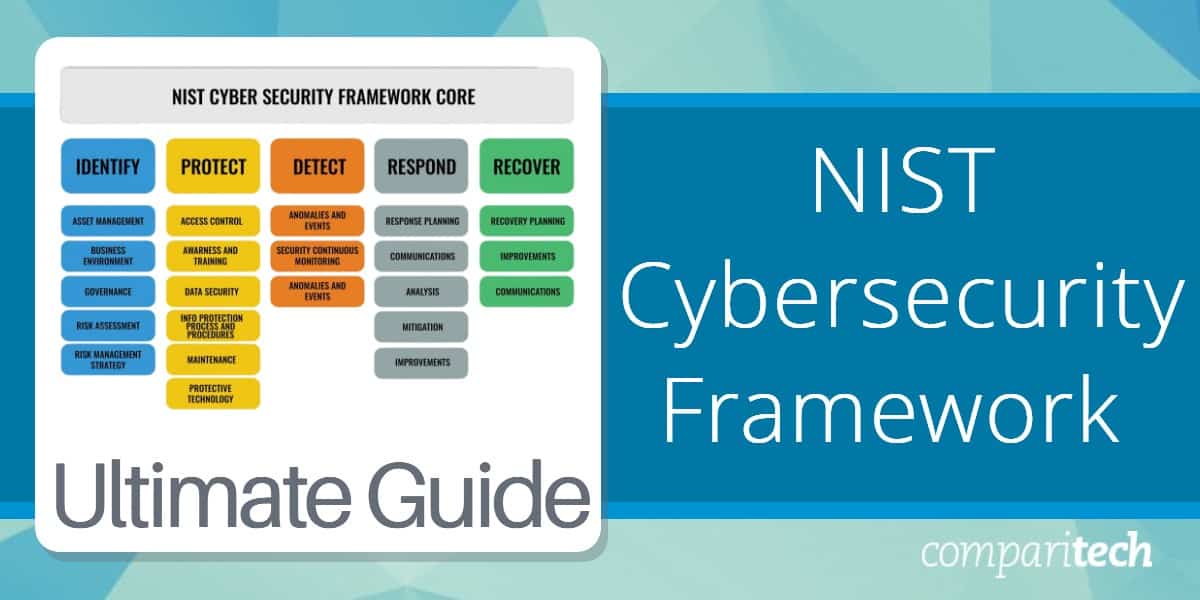
The framework itself breaks into five functions. Identify covers asset management, risk assessment, governance, and supply chain risk. Protect includes access control, awareness training, data security, protective technology, and maintenance. Detect addresses continuous monitoring, detection processes, and anomalous activity analysis. Respond is about response planning, communications, analysis, mitigation, and incident improvement. Recover focuses on recovery planning, improvements, and communications during a crisis. Your policy should reference these functions explicitly so an auditor can trace your document back to the CSF without guessing.
How I Built a Working Template Instead of Downloading One
Early in my career I downloaded a free CSF template from a vendor site and tried to adapt it for a healthcare client. The template had thirty-seven policies, most of them padded with generic language like "the organization shall implement appropriate measures". Auditors rejected two-thirds of the policies during the evidence review because the language did not map to specific subcategories or assign ownership. That experience taught me that the value of a template guide is in its crosswalk, not in the boilerplate text. What I ended up building was a spreadsheet that listed every CSF subcategory in column one, the corresponding policy section in column two, the assigned policy owner in column three, and the evidence type required for audit in column four. The policy document itself was lean. I wrote only the sections that had a direct subcategory mapping, and I left the rest out. For the healthcare client this produced a twenty-two policy document instead of thirty-seven, and it took the audit team less than forty minutes to verify coverage compared to the previous three-day marathon. The one edge case that still trips people up is the overlap between Identifying risks under the Governance subcategory and Protecting under the Access Control subcategory. A single policy about role-based access often satisfies both ID.GV and PR.AC. I learned this the hard way when a consultant billed our client for writing two separate policies that said the same thing. I merged them into one policy with two subsections, each referencing its own subcategory code. That reduced maintenance burden without sacrificing audit traceability.
Get the Full Details
What Most People Get Wrong About CSF Policy Templates
Beginners treat the framework as a checklist of policies to write. It is not a checklist. It is a risk-based structure. Writing a policy for every subcategory sounds thorough but creates a maintenance nightmare. I once worked with a company that had policies for every DE.CM subcategory under Detect and could not produce a single log sample when asked during an audit. They had the documents but not the operational evidence to back them. Another common mistake is ignoring the tier level. The CSF defines four tiers: Partial, Risk-Informed, Repeatable, and Adaptive. If you are at Tier 1, you do not need enterprise-grade policy language. You need something that proves you are aware of the risk and have started to address it. Over-polishing your policies for a Tier 1 environment is a waste of time and often raises auditor suspicion because the language does not match the organization's actual maturity. Here is a counter-intuitive point that most templates miss. The CSF is intentionally non-prescriptive about technology. A template that recommends specific tools, vendors, or configurations is already outdated. I advise keeping tool references out of the policy text and putting them in an associated standard or procedure document instead. This way when you switch from one SIEM to another, you only update the procedure, not the policy. Policies should state what you intend to achieve, not how you currently achieve it.
Practical Steps to Create Your Own Template
Start by listing the subcategories that apply to your environment. Not all fifty-four categories are relevant to every organization. A small e-commerce business will care much more about PR.DS and DE.CM than it will about ID.SC or RS.MI. I usually recommend mapping subcategories to your existing risk register first. Any subcategory with no corresponding risk item is either a low-priority gap or redundant with another control you already manage. Once you have your subset, draft each policy section with three components. The first is the purpose statement tied directly to the subcategory code. The second is the scope defining who and what the policy applies to. The third is the responsibilities section naming the roles accountable for implementation. Keep the operational details for standards and procedures. That division keeps the policy readable and forces the technical content into documents that update more frequently. Create a traceability matrix on a separate sheet. Map each policy section to one or more subcategories, each subcategory to a risk item, and each risk item to a tier level. During an audit this matrix becomes your fastest evidence path. Auditors can verify coverage in minutes instead of hours. I have used this approach with organizations ranging from eight employees to fifteen thousand, and the matrix scales without needing a complete rewrite.
Where Templates Fall Short and What to Do Instead
No template can solve the problem of integrating the CSF with other frameworks. If your organization also follows ISO 27001, SOC 2, or HITRUST, you will find that many CSF subcategories overlap with controls from those standards. A pure CSF template guide will not show you those mappings. You need a cross-reference table that links CSF categories to ISO 27001 control IDs and SOC 2 criteria. Building that table takes extra time upfront but eliminates duplicate work during certification audits. Another limitation is supply chain risk. The ID.SC and PR.SCM subcategories require vendor risk management practices that most policy templates handle superficially. I encountered this with a logistics company that had a perfectly mapped CSF policy but no vendor questionnaire process. The auditor flagged the gap immediately. The workaround was to create a separate supply chain risk annex to the main policy and link it through the traceability matrix rather than trying to force vendor management content into the core policy document. There is also the problem of outdated guidance. NIST released the CSF 2.0 in 2024 with a new Govern function replacing part of the Identify function. Many template guides online still use the 1.1 structure. If you are building a new policy, start with the 2.0 categories. The Govern function shifts some policy ownership toward board-level and executive accountability, which changes how you write your responsibilities sections. Ignoring the 2.0 update means your policy will look stale to anyone who has read the latest NIST publication.

Where to Find a Usable Starting Document
NIST publishes the Cybersecurity Framework itself for free at nist.gov/cyberframework. The core document includes the taxonomy and crosswalk tables but does not provide policy text. Several vendors and professional bodies have created template guides based on the framework. I recommend comparing any third-party template against the official NIST CSF 2.0 subcategory list before adopting it. Look for documents that include the subcategory codes in their headings and provide a traceability matrix as an appendix. If you are looking for a free starting point, the NIST SP 800-53 family of publications includes control families that map closely to the CSF. Using those as a supplemental reference gives you more structured language than most CSF-only templates. For smaller organizations that cannot afford a full compliance consultant, the CISA CSF resources page offers simplified implementation guides that can serve as a baseline before you build your own template. The most practical approach is to take any template guide, strip out the generic filler, keep the crosswalk intact, and rewrite each policy section in your organization's voice. A policy that sounds like your internal documentation gets followed. A policy that sounds like it came from a framework manual gets filed away and forgotten. The difference is subtle but it shows up immediately during audits when interviewers ask staff to describe their own security practices.