Working With the NIST Risk Assessment Matrix
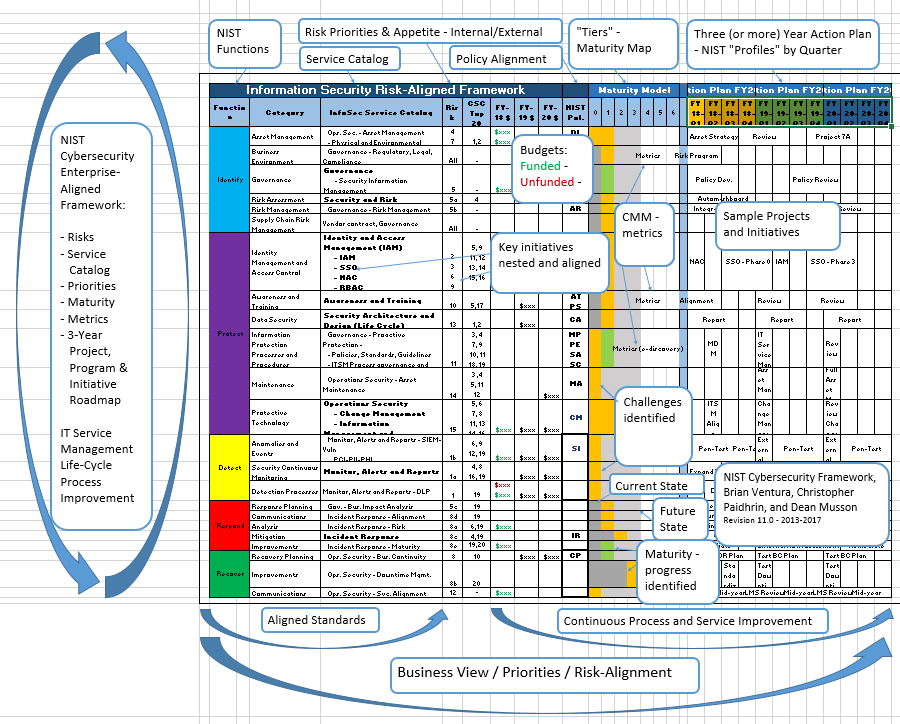
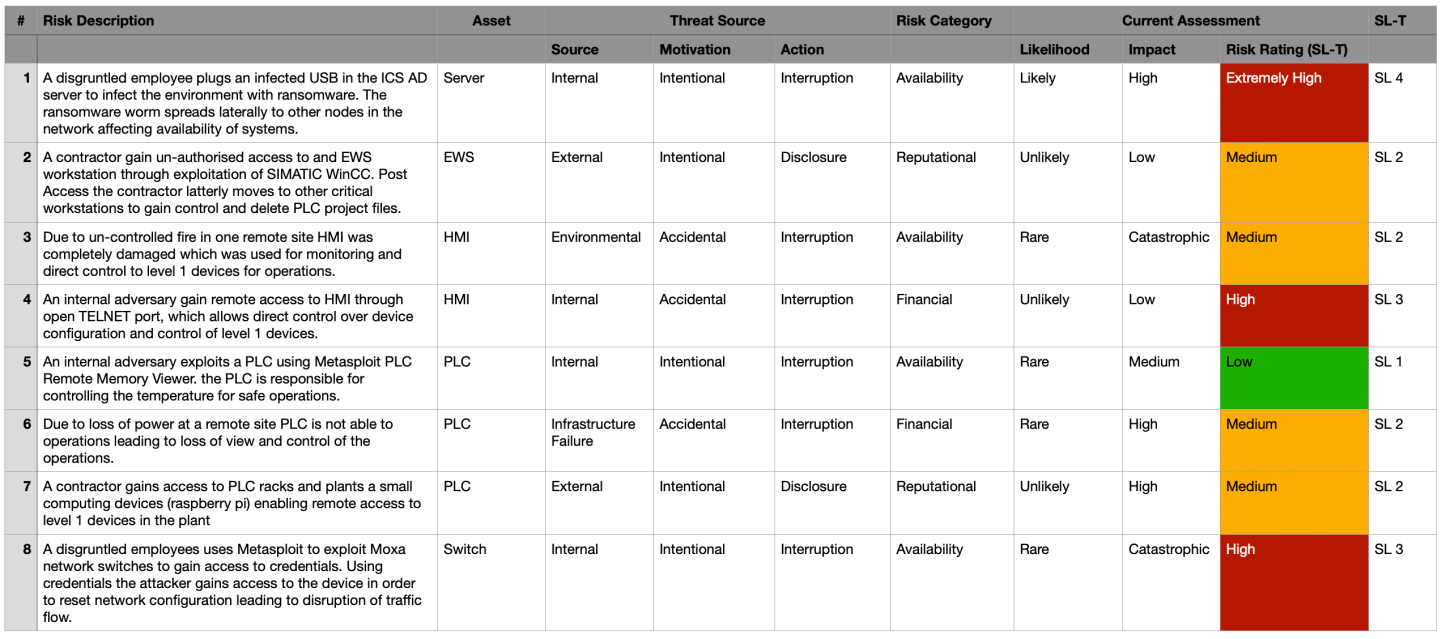
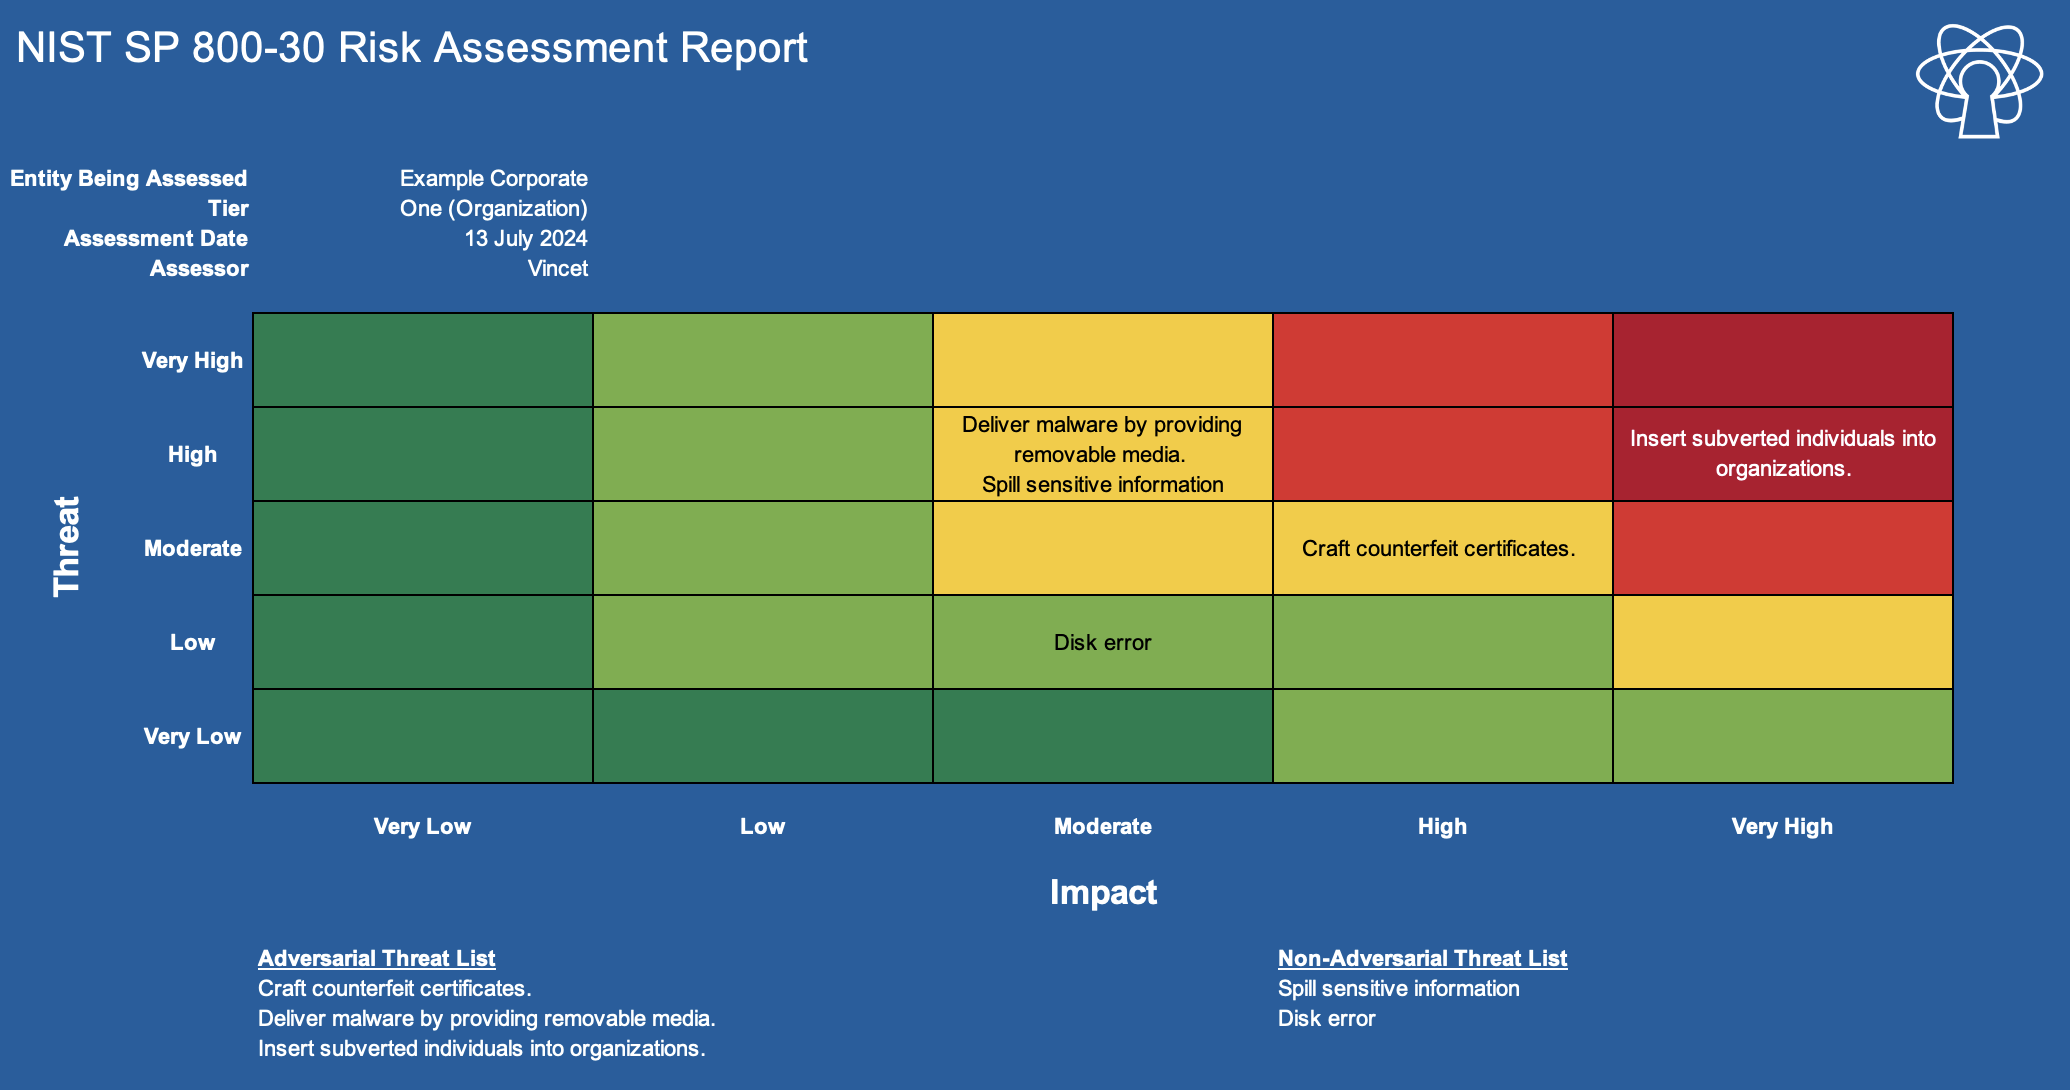
The NIST Risk Assessment Matrix is basically a grid that maps likelihood against impact to give you a risk score. You fill it in, you get numbers you can use to prioritize. That's the theory. The reality is messier than that. In practice, most people build or download a template and start plugging in their findings from the asset inventory and threat analysis phases. The matrix itself is simple: likelihood on one axis, impact on the other, and a color-coded cell in between. Green means low, yellow means medium, red means high. You end up with a spreadsheet that someone else will ask you to defend during a compliance review. The real work happens before you even open the matrix. You need a credible likelihood scale and an impact scale that actually reflects your organization. If you're using a five-point scale for both, here's what that typically looks like in the field:
Likelihood scale goes from near-certain to rare. Impact scale goes from negligible to catastrophic. The specific wording matters more than the number of levels. When I've seen teams use vague labels like "medium" without clear definitions, the scores become meaningless within a few months because different assessors are interpreting the same category differently.
Building Your Matrix Step by Step
Start by defining what each level means in concrete terms. Not "likely" but "occurs at least quarterly based on historical data or credible intelligence." Not "high impact" but "system down for more than 24 hours with data loss exceeding $50,000." These definitions don't stay static. They get revised when your environment changes or when a close call happens and you realize you underestimated something. Once your scales are locked down, you iterate through each asset or risk scenario and assign a likelihood and impact value. Multiply or look up the combination in your matrix to get the risk score. Then rank them. The top five are your immediate attention. The bottom twenty might not need action beyond monitoring, depending on your risk appetite. Here's where people commonly go wrong. They treat the matrix as a one-time exercise instead of a living document. The matrix should be reviewed at least annually, or whenever something significant changes in your infrastructure. A new cloud service, a merger, a change in compliance requirements. All of these shift what counts as high impact or how likely certain threats are.
Get the Full Details
A Problem I Actually Encountered
One time I was working on a Nist Risk Assessment Matrix for an organization that had recently migrated a significant portion of their workload to a third-party SaaS provider. The legacy risk assessment had been built around on-premises threats like hardware failure and physical intrusion. The new SaaS environment introduced entirely different attack surfaces and failure modes that didn't map cleanly onto the existing likelihood categories. The workaround was to create a supplementary mapping layer. Instead of trying to force the SaaS risks into the old likelihood definitions, we added specific scenario-based likelihoods for cloud-specific threats like credential compromise, misconfigured storage buckets, and supply chain vulnerabilities. We kept the original matrix intact for legacy assets and layered the new assessment alongside it. It added maybe two weeks to the overall timeline but prevented the absurd situation of scoring a real cloud breach scenario as "unlikely" just because our definitions were outdated.
Things That Aren't Obvious
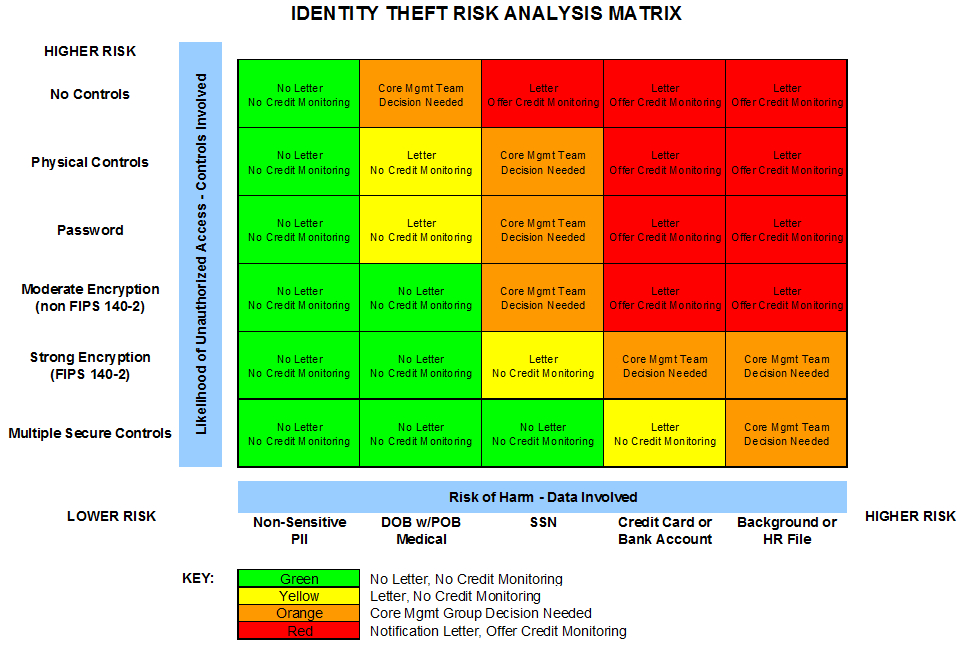
First, the matrix naturally pushes you toward quantification even when the underlying data is highly uncertain. Assigning a numeric likelihood to something like a nation-state APT doesn't make it more real. It just makes it look like you understand it better than you do. In those cases, the honest answer is often "unknown with high severity" or whatever your framework allows for insufficient data scenarios. Second, most organizations conflate risk treatment with risk acceptance. Just because a risk scores red on your matrix doesn't automatically mean you need to spend money to mitigate it. Sometimes the cost of mitigation exceeds the expected annual loss. That's an explicit decision you should document, not a gap in your process. There are also edge cases where the matrix breaks down entirely. When you have dependencies between risks, the independent scoring model falls apart. A compromised VPN and a vulnerable patch management system might each score medium individually but together they enable a full network compromise. The matrix won't capture that interaction unless you build it into your process somehow, which most people don't.
Where to Get a Template
NIST publishes guidance in SP 800-30 Rev. 1 that describes the methodology in detail. The government doesn't host a downloadable matrix template on their site, but you can build one from scratch using the structured approach outlined in that publication. Commercial and community templates exist on GitHub and various security resource sites if you want something you can import directly into Excel or Google Sheets. If you need something fast and functional, the simplest approach is a ten-cell grid with likelihood levels one through five on the vertical axis and impact levels one through five on the horizontal axis. Each cell contains the product of the two scores. Color code them and you're done. Then customize the definitions to match your actual operational context.

The Honest Take
The NIST Risk Assessment Matrix is useful but overrated. It gives structure to something that would otherwise be a free-form conversation, and that structure is valuable for consistency and audit readiness. But it cannot substitute for actual domain knowledge about your environment. A perfectly constructed matrix applied to poor-quality input data produces a polished-looking report that doesn't reflect reality. The people who get the most out of it treat the matrix as a discussion tool rather than a calculation engine. The score itself matters less than the conversation it forces you to have about why you assigned that likelihood, why that impact level, and whether the treatment decision aligns with your actual risk appetite. If you can facilitate that conversation, the matrix is doing its job. If you're using it to generate scores and file them away, you're wasting everyone's time.