Getting a NIST Risk Assessment Report Template to actually work
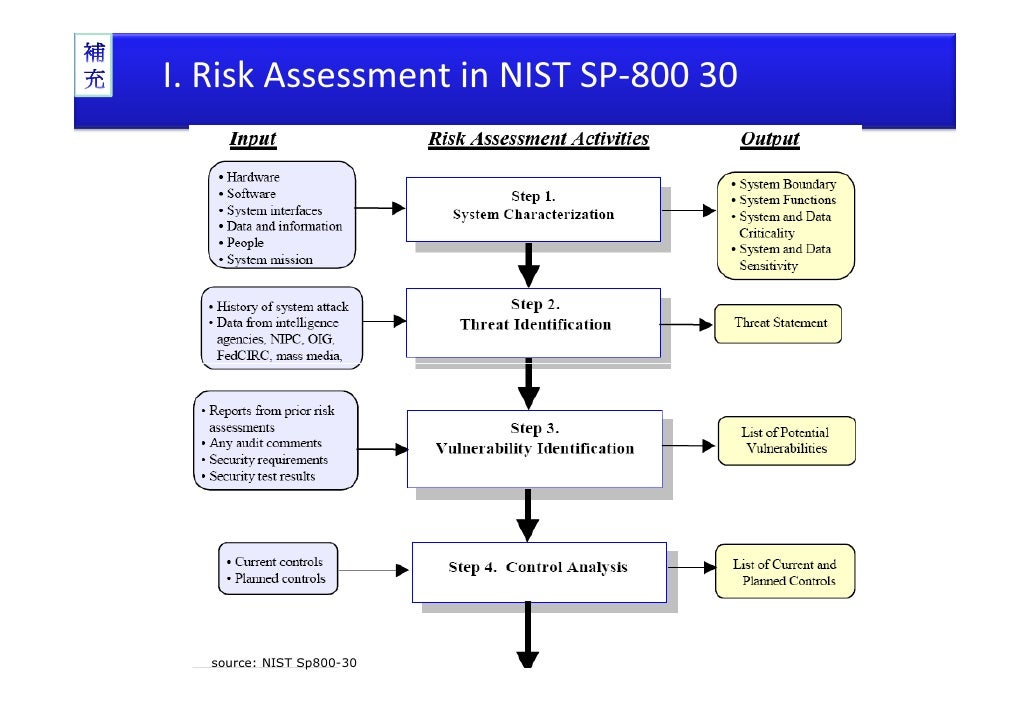
Most people download a generic template and immediately run into the problem that it does not match their organization's actual asset inventory or risk tolerance. I spent about three weeks last year cleaning up a template that had been pulled from a government contractor's shared drive. It was full of fields for system security plans, authorization boundary definitions, and impact level matrices that simply did not apply to a mid-size private company doing FedRamp moderate compliance. We ended up deleting about sixty percent of the original columns and rebuilding the rest around our own findings from the initial reconnaissance phase. The core challenge with any Nist Risk Assessment Report Template is that NIST SP 800-37 Revision 2 frames the process around the entire risk management lifecycle. Your report needs to reflect that structure: categorize, select, implement, assess, authorize, and monitor. But the template itself is not a substitute for actually doing those steps. People conflate the two constantly.
How to build a usable Nist Risk Assessment Report Template
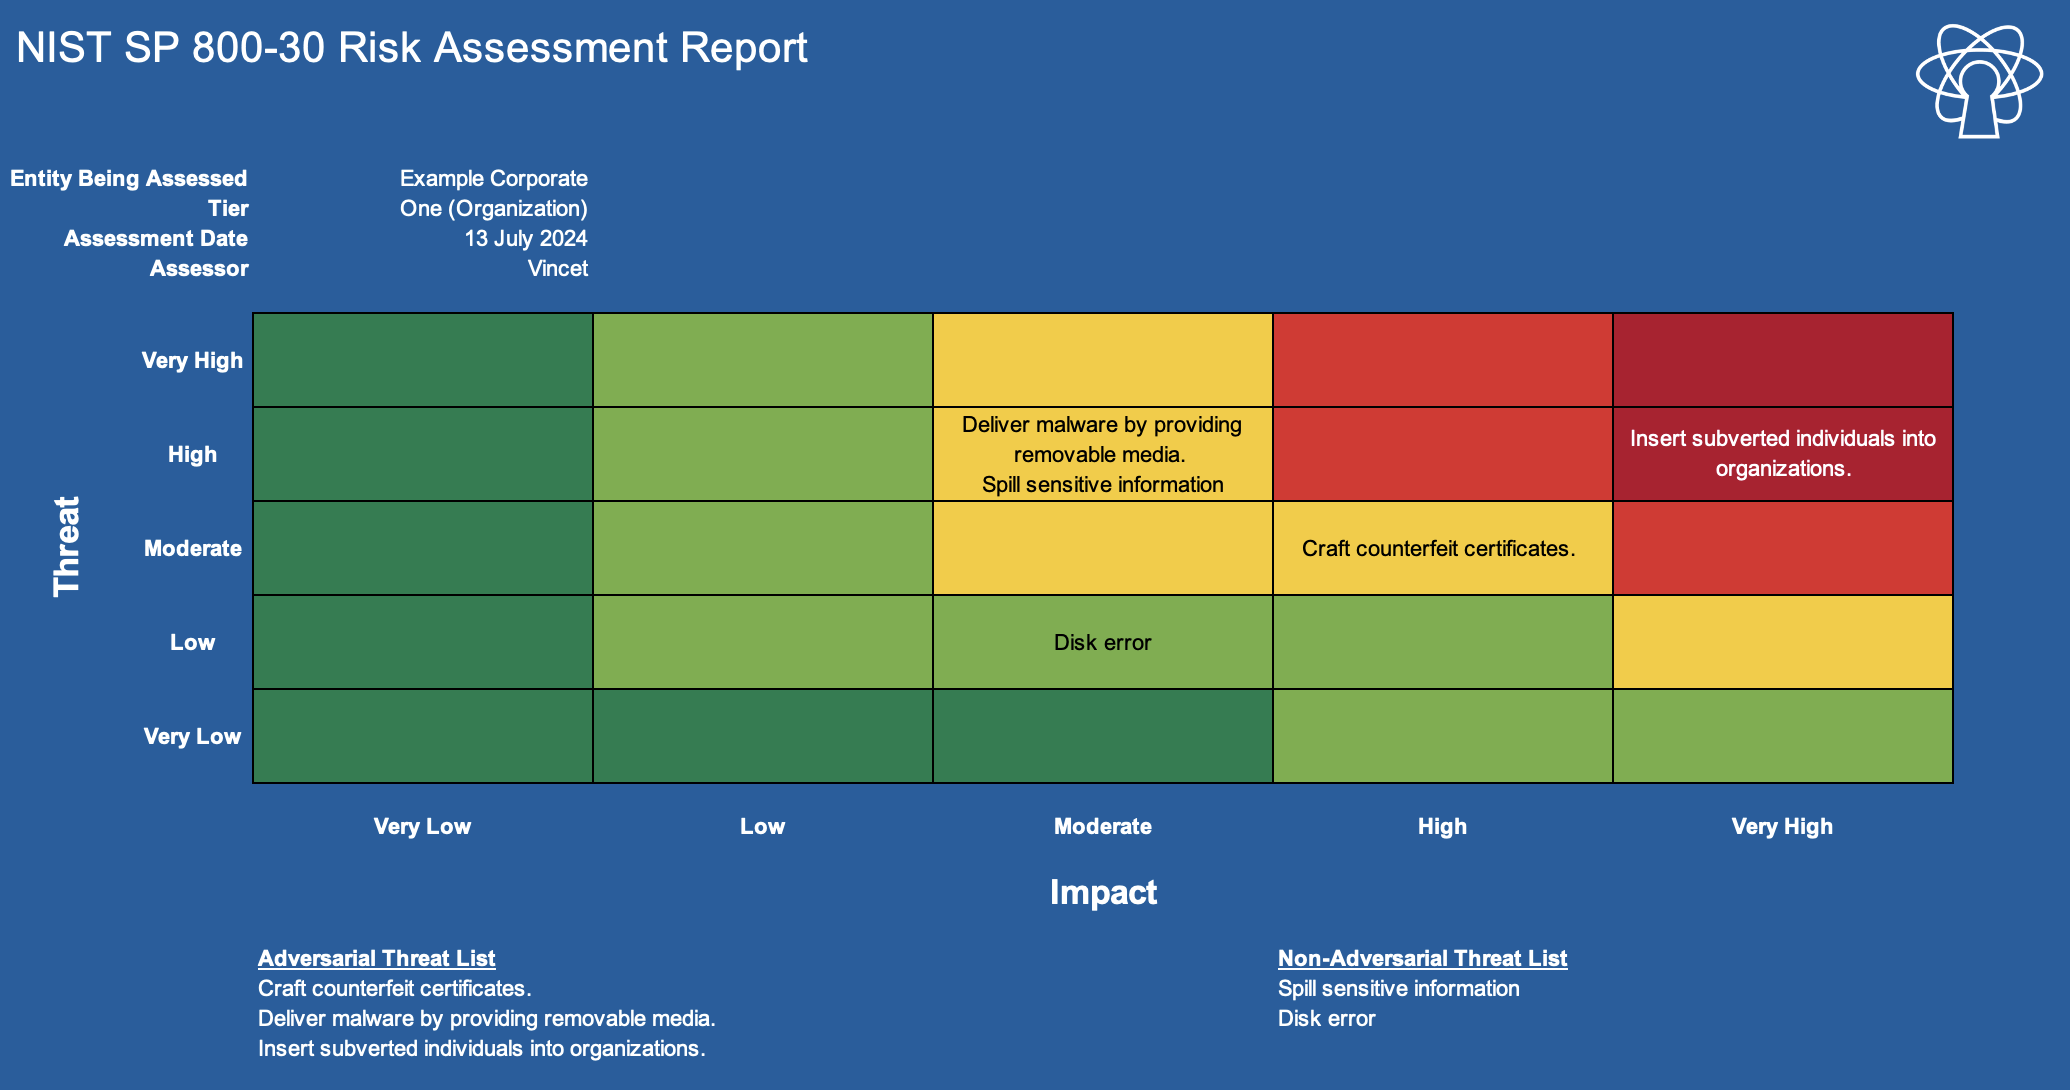
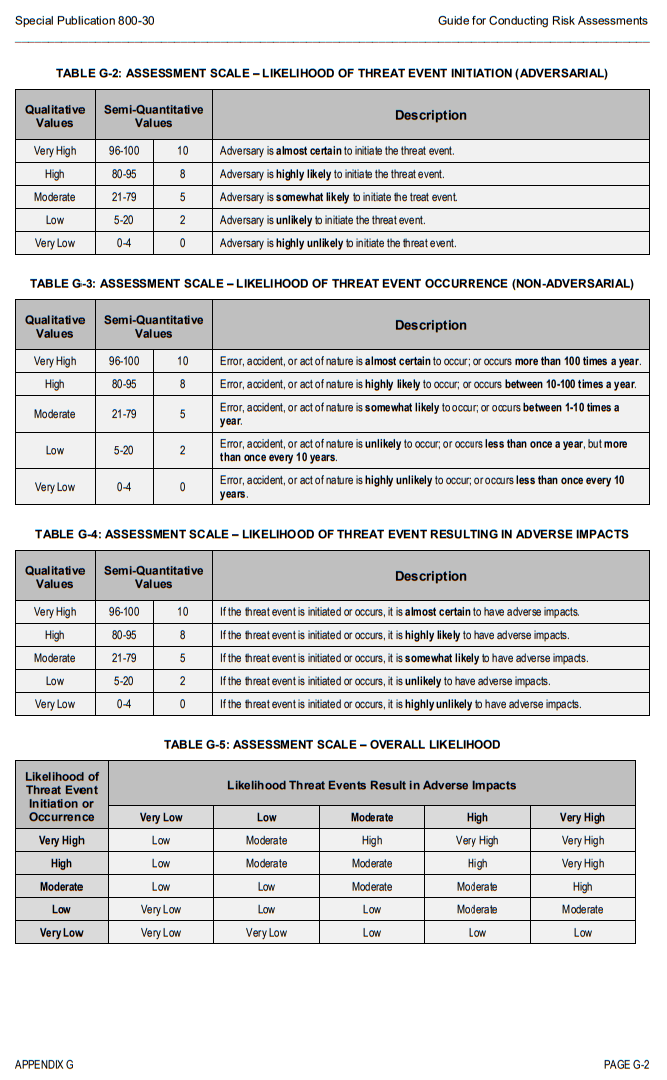
Start by identifying your authorization boundary. This is the section most templates get wrong because they assume you are assessing a single FISMA system when your environment might include multiple cloud workloads, third-party SaaS connections, and on-prem legacy infrastructure. I keep a separate diagram that maps every data flow crossing that boundary and attach it as an appendix. Auditors will ask for it within the first five minutes of a review. The template should contain these sections at minimum: executive summary, scope and methodology, asset inventory with classification, threat and vulnerability identification, likelihood determination, impact analysis, risk calculation, mitigation recommendations, residual risk acceptance, and monitoring schedule. Anything beyond that is usually filler that nobody reads and slows down the document. For the likelihood and impact scoring, use a consistent scale. I recommend a five-point scale across the board. Some organizations mix a three-point likelihood scale with a five-point impact scale and then wonder why the resulting risk matrix looks arbitrary. It does. Pick one scale and stick with it for every assessment you produce.
The risk calculation section is where most people stumble. You need to multiply likelihood by impact, but the multiplication alone tells you nothing about treatment options. Below each calculated risk score, I add a mandatory field for recommended control families drawn directly from NIST SP 800-53 Rev 5. If the risk falls below your threshold, you still document the acceptance rationale. Do not skip it. Auditors will flag an unexplained low-risk finding as a process gap. I ran into a specific issue with a client assessment where the template included a field for Continuous Monitoring Strategy but left no place to record the actual tools or data sources being used. The client was relying on a SIEM integration that pulled from AWS CloudTrail, Azure Sentinel, and a custom Python parser for on-prem AD logs. The template had no row that could hold that much detail. I added a sub-table under the monitoring section with columns for tool name, data source, update frequency, and alert escalation path. That fixed the problem permanently for all subsequent assessments. One thing that is not obvious from reading the standard: NIST expects risk assessments to be iterative, not static. A single report will not satisfy the requirement. The template should include a revision history table and a field for the next reassessment date based on trigger conditions such as significant architecture changes, new threat intelligence, or a completed incident. Without that, you are producing a document that expires the moment it is printed.
Get the Full Details

Here are a few practical realities about using these templates that the documentation does not emphasize: Templates created for high-impact systems often create unnecessary overhead when applied to low-impact systems. A FISMA high system requires a completely different depth of control assessment than a low business impact system. I scale my template sections based on the impact level before I begin. This usually cuts the draft time from four hours down to about forty-five minutes for low-impact assessments. Third-party risk is frequently treated as an afterthought in these reports. If your organization uses any managed service providers or cloud providers, you need a dedicated section that captures the provider's ATO status, the most recent SSAE 18 or SOC 2 report reference, and your residual risk acceptance for that dependency. I have seen assessments fail because the reviewer could not trace a critical application back to its hosting provider's authorization package.
The biggest limitation of any Nist Risk Assessment Report Template is that it cannot capture organizational context that exists outside the standardized fields. Your risk appetite statement, your internal policy references, and your specific threat landscape may not fit neatly into any prebuilt format. When that happens, adding a customization appendix is better than trying to force content into ill-fitting cells. If your environment is small enough that a full SP 800-37 framework feels excessive, some teams transition to a simplified risk register based on NIST SP 800-39 concepts. It covers the same ground but with far fewer required sections. You lose some formal consistency, but you gain speed and something that actually gets reviewed instead of filed away. I keep my current template as a Google Sheets file with locked header rows and a separate Google Doc for narrative sections. It is not the most elegant solution, but it has worked without major issues across twelve separate assessments over the past two years. The spreadsheet handles the scoring and matrix work. The document handles everything that requires explanation. Dividing them this way prevents the file from becoming impossible to navigate when it grows beyond about twenty assessed assets.
The main takeaway is that the template is a container, not a methodology. The value comes from how thoroughly you fill it, which depends entirely on how well you understand your own systems and the controls you have already implemented.