Why the Nist Risk Assessment Template Xls is harder to use than the documentation suggests
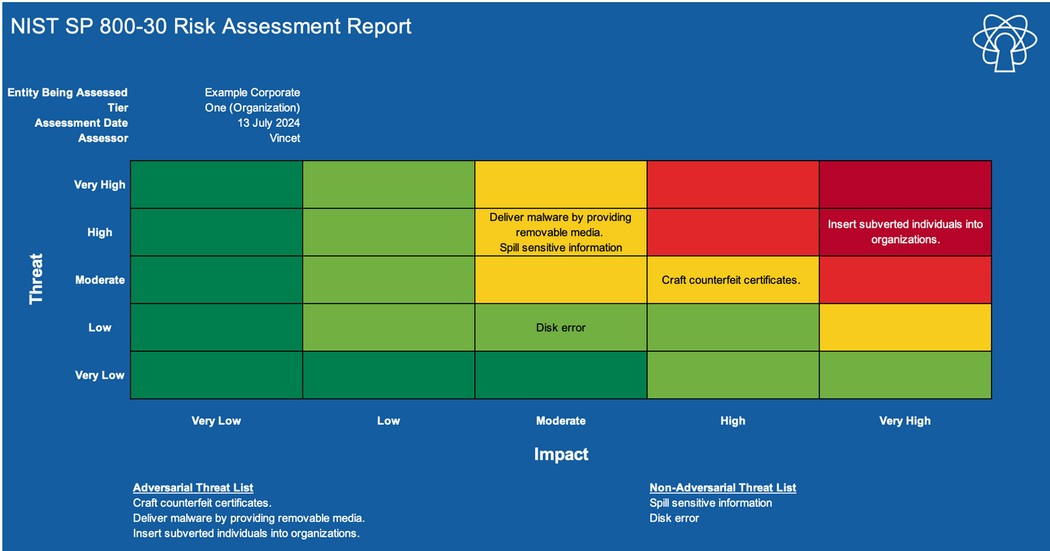
Most people download the spreadsheet and immediately hit a wall. The template assumes you understand NIST SP 800-30's probability × impact framework, but it doesn't explain how to actually populate the fields when your asset inventory is messy, your threat data is sparse, or your stakeholders refuse to agree on what "high" means. I spent three weeks wrestling with a fresh install from NIST's site before I figured out the actual workflow that doesn't leave you with a sheet full of blank cells and guessed scores. The core problem is structural. NIST templates are intentionally generic by design. They cover federal systems broadly, which means they weren't built for a mid-size healthcare vendor or a SaaS company trying to satisfy SOC 2. You'll find yourself constantly adapting columns that expect government-specific controls. The template's built-in formulas for likelihood and impact rely on predefined scoring tables that don't always map cleanly to non-federal environments. I ran into this exact issue when a client needed to assess risks for a HIPAA-compliant cloud deployment, and the default risk score matrix produced numbers that made no sense in our context. I ended up replacing the impact column with a weighted scoring system that factored in breach cost, downtime, and reputational damage separately instead of using the single 1-to-5 scale the template provides.
Nist Risk Assessment Template Xls: How to Actually Use It
Download the file from csrc.nist.gov and open it in Excel, not Google Sheets. The macros and pivot table functionality break in the web version. Start by filling in the asset register on the first tab. This is where most people skip ahead and regret it later. The rest of the template references that sheet, so if your assets aren't listed with unique identifiers, every risk scenario you create will throw a #REF error. Step one: Populate the threat and vulnerability tables before touching the risk scenarios. The template calculates probability based on historical frequency data in those tables, and leaving them empty forces you to guess. I've seen people manually override the formulas instead, which defeats the entire point of using a standardized template. Step two: Map each risk scenario to at least one control from the NIST 800-53 family. The template includes a reference sheet with control IDs organized by family. If you're in a non-federal environment, cross-reference with NIST 800-171 or ISO 27001 controls where the 800-53 mappings are too broad to be useful. A common gap I've encountered is that the template doesn't account for third-party supply chain risks unless you manually add a new category in the threat identifier column.
Step three: Run the risk acceptance report before you present anything to management. The output tab generates a summary that most auditors actually read. If the report shows every risk as "medium," either your scoring is wrong or your organization has no real risk appetite documented anywhere. I had a situation once where the entire inventory came back as medium because everyone used the same default values instead of evaluating each asset individually. The fix was setting up a mandatory field in the likelihood column that required a source citation for every score above 2.
Get the Full Details
Pitfalls that will ruin your assessment
The biggest mistake I see is treating the template as a one-time compliance exercise rather than a living document. Risk assessments are supposed to be iterative. If you don't update the threat frequency tables after a significant incident or a new CVE affects your infrastructure, your subsequent assessments will be stale. I've reviewed assessments from companies that reused the same spreadsheet for four years without changing a single threat entry. The numbers looked clean, but they were completely disconnected from reality. Another issue is the assumption that all assets are equal. The template doesn't weight criticality by business function. A financial system and a printer both get the same treatment in the default scoring. I created a workaround by adding a multiplier column tied to asset criticality and feeding that into the impact calculation manually. It took about ten minutes to set up and dramatically improved the accuracy of the risk rankings. There's also a subtle problem with the probability distribution logic. The template uses a simple average for combining threat and vulnerability likelihood, which understates risk when both are high. In practice, when threat frequency is frequent and vulnerability severity is critical, the combined probability should reflect compounding risk, not just averaging. I adjusted the formula to use a geometric mean instead of arithmetic, which produces more realistic scores in high-severity scenarios.
What the template can't handle
The NIST Risk Assessment Template Xls doesn't support continuous monitoring integration. It's a static document that requires manual updates. If you're looking for automated risk scoring based on live vulnerability scans or SIEM feeds, this template won't give you that. You'll need to pair it with something like a GRC platform or write your own scripts to pull data from tools like Nessus or Qualys and push it into the spreadsheet. It also lacks support for quantitative risk analysis. Everything is qualitative or semi-quantitative. If your organization needs Annualized Loss Expectancy calculations or FAIR-style models, you'll have to build those separately and reference them from the template's notes column. I spent a day building an ALE calculator that pulled data from our insurance premiums and historical incident logs, then linked it to the main risk register so the financial impact column auto-updated whenever the annualized rate changed. The template is also rigid about taxonomy. It uses NIST's official terminology, which means if your industry uses different risk classifications—like the OWASP top ten for software development or the HHS breach notification rules for healthcare—you'll spend time translating between systems. I found that creating a lookup table that mapped NIST categories to industry-specific ones reduced this friction significantly. The lookup took about fifteen minutes to build and saved hours of manual reconciliation during audit prep.
A workaround I ended up relying on
One edge case that the template doesn't address at all is concurrent risk mitigation across multiple systems. Say you have a vulnerability in your Active Directory that affects twenty-five servers. The template makes you create twenty-five separate risk scenarios, even though the root cause and mitigation are identical. I wrote a simple VBA macro that groups related risks by common vulnerability and lets you assign a single mitigation action that propagates across all linked scenarios. It cut my assessment time roughly in half for environments with correlated risks. For smaller teams who don't want to write macros, a simpler approach is to add a grouping column and use Excel's filter function to aggregate related risks manually. It's not elegant, but it works and doesn't require any scripting knowledge. Either way, the time savings are real. An assessment that would normally take two people a week can get down to three or four days if you stop treating every finding as an isolated event.

When to look elsewhere
If you need real-time risk dashboards, multi-jurisdictional compliance mapping, or integration with your existing IAM and SIEM tools, the NIST template alone won't cut it. It's a foundational document, not a complete risk management system. Organizations that outgrow it typically migrate to platforms like SecureFrame, Drata, or OneTrust, which automate much of the evidence collection and continuous monitoring that the spreadsheet leaves entirely manual. That said, the template remains useful for small teams that need a structured starting point without a five-figure software commitment. The key is understanding its limits upfront rather than discovering them three weeks into your assessment and having to rebuild everything from scratch. Most people waste time on the second part. The first part is straightforward if you take the asset inventory seriously and don't rush through the threat and vulnerability tables.
Where to get it
The official template is available at csrc.nist.gov under the risk management framework resources section. Look for the spreadsheet package labeled for SP 800-30 implementation. Make sure you're downloading the latest revision, as older versions have known issues with the pivot table formulas that cause incorrect aggregations when you filter by control family. The current version resolves those calculation errors, though some of the structural limitations I mentioned above remain unchanged. Once you have it open, spend at least an hour on the asset register before doing anything else. That single decision determines whether the rest of the template functions correctly or degenerates into a mess of broken references and guesswork. Everything downstream depends on that foundation being solid.