Working with a Nist Security Assessment Plan Template
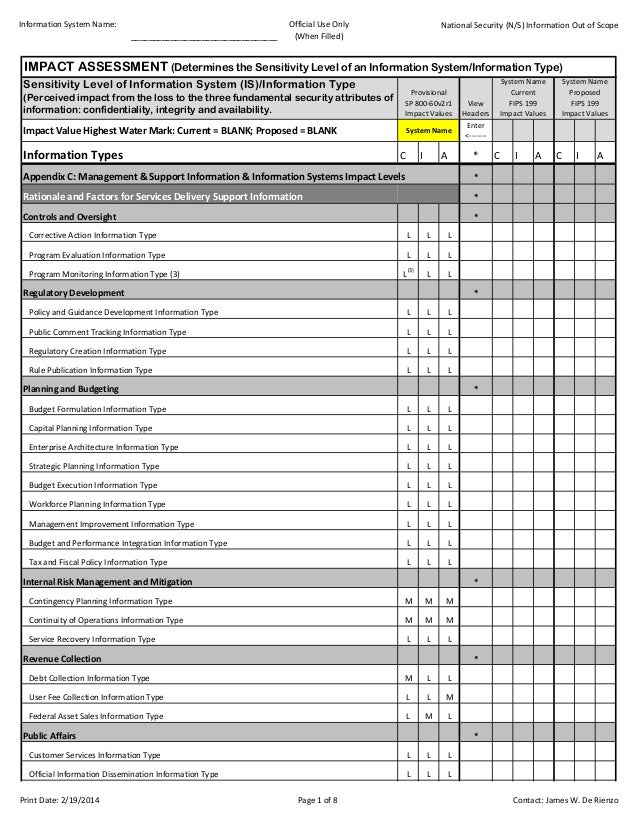
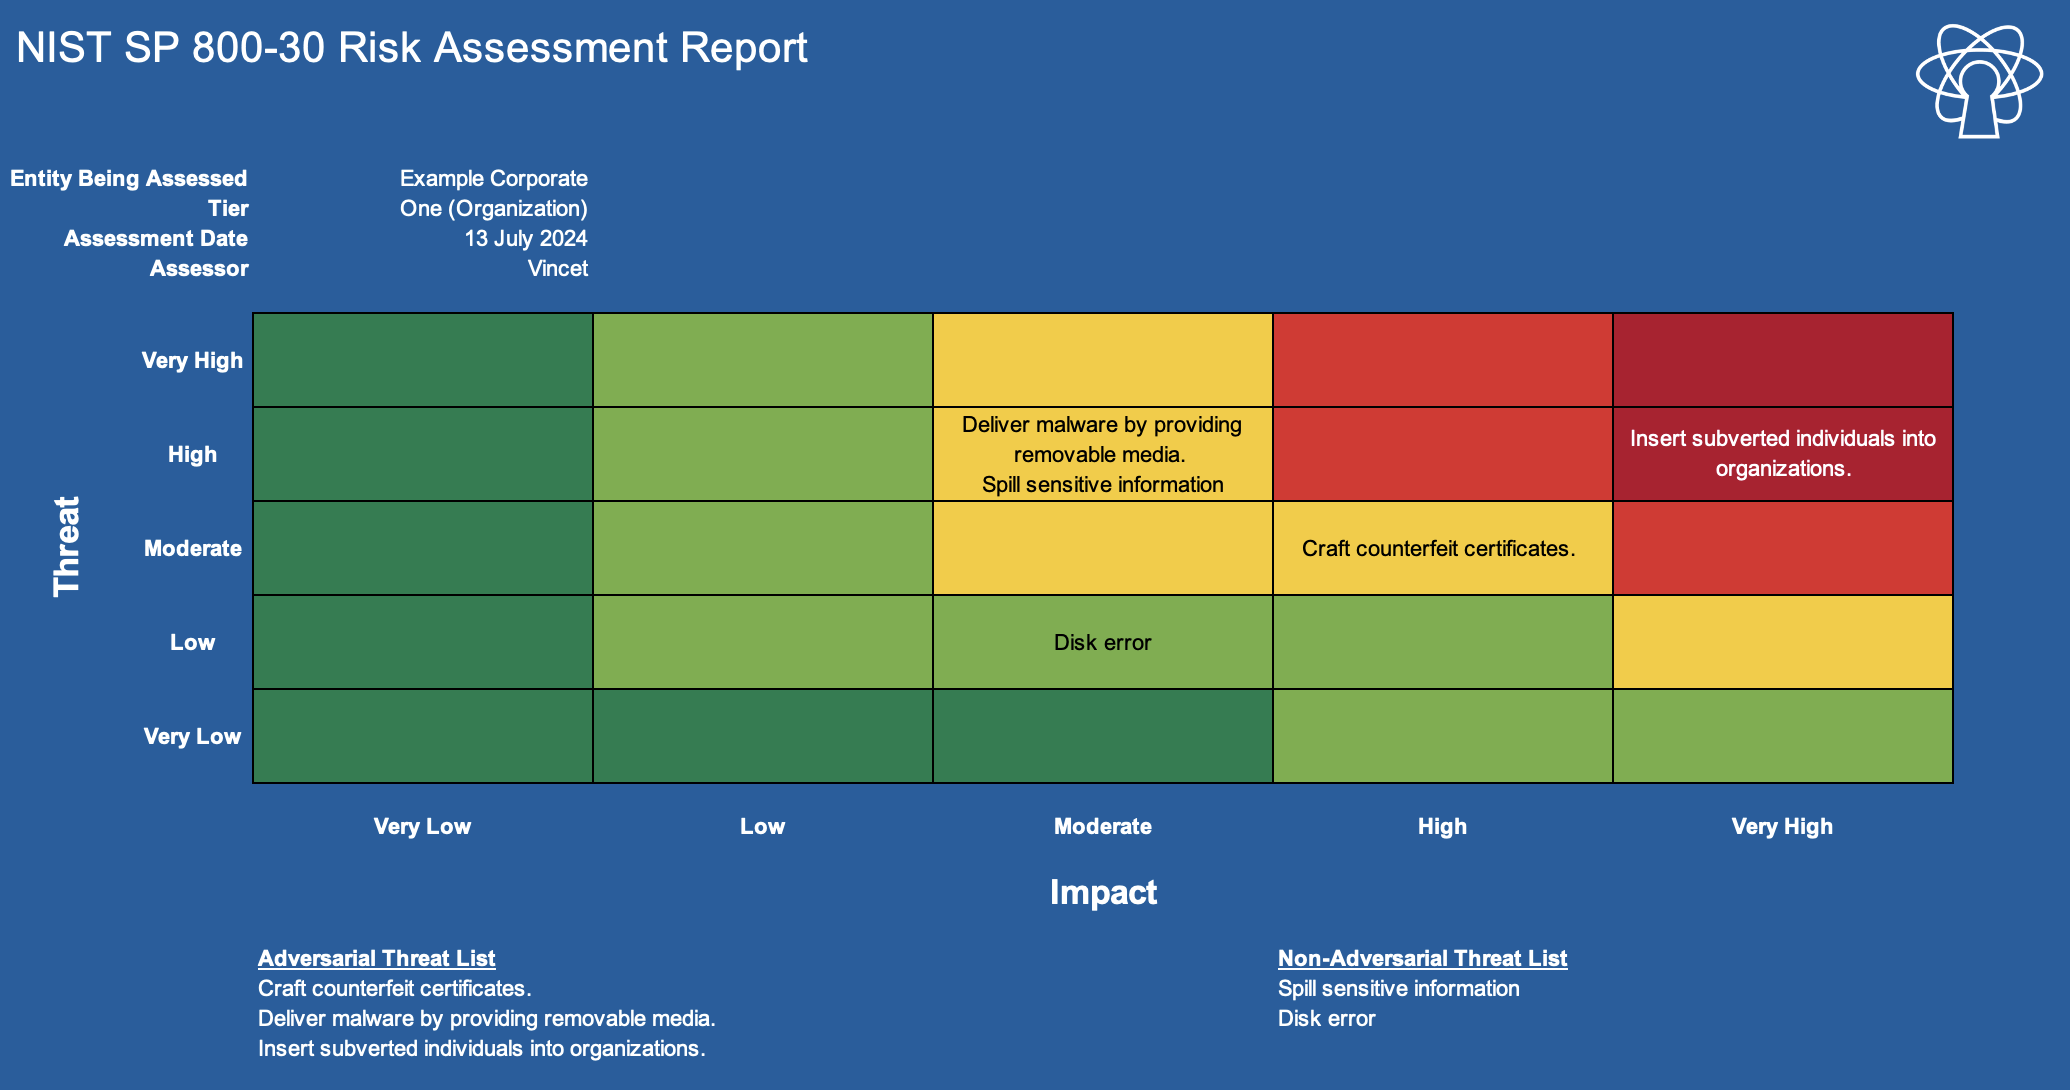
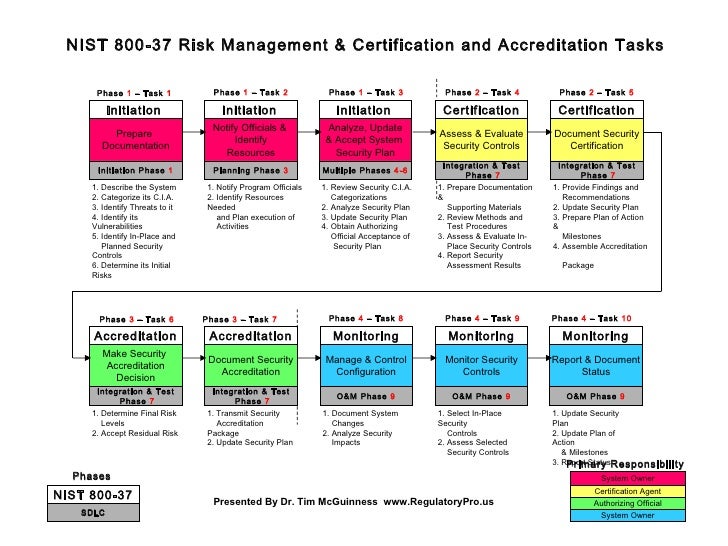
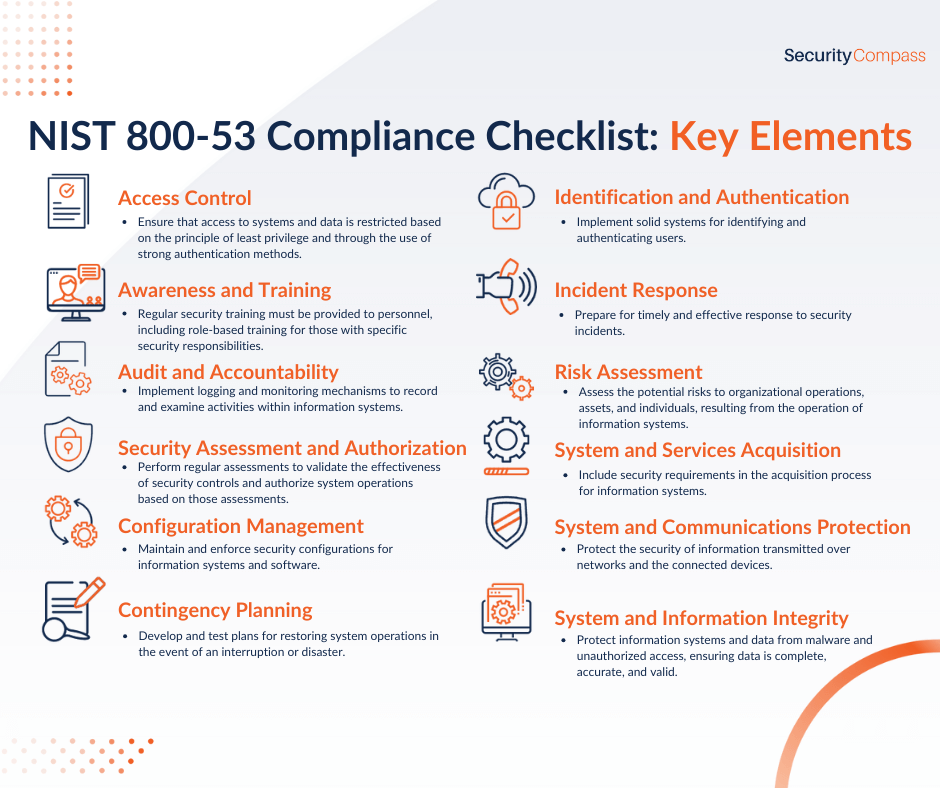
A Nist Security Assessment Plan Template is really just a structured way to document what you're going to check, how you're going to check it, and who's responsible for each piece before you actually start testing. People treat it like paperwork, but the version that actually works is the one that gets used during the assessment instead of filing it away after sign-off. Most templates pull their sections from NIST SP 800-53A guidance. You'll see the same core components repeated across agencies: scope, assessment objectives, control families being tested, methods and tools, schedule, roles, acceptance criteria, and reporting format. The template itself doesn't force you to think critically about any of it, which is why so many plans look good on paper and fall apart on day one. The useful ones add a mapping table that links each assessed control to its source system, the specific test method, and the evidence required. That table is what separates a plan from a placeholder.
How I actually use these templates
I start by pulling the control baseline from the system's security authorization package, then I build the assessment plan around the controls that are scoped in for that particular system. Not every control in 800-53 applies to every system, and the template won't tell you that. You have to figure it out from the system boundary documentation and the data flow diagrams. Once the controls are identified, I assign a test procedure to each one. The procedure needs to be specific enough that another assessor could replicate it without calling you. "Verify encryption is enabled" is not a procedure. "Run nmap --script ssl-enum-ciphers against port 443 and confirm TLS 1.2 minimum with cipher suite AES_256_GCM" is a procedure. The difference matters when someone comes back six months later for a follow-up assessment. I include tool selection in the plan rather than figuring it out mid-assessment. If your plan says vulnerability scanning will use Qualys, and your environment blocks Qualys agents due to a misconfigured VLAN, you've just lost a day before you even start. I learned that the hard way on a cloud migration project where the template assumed on-prem Nessus deployment. The workaround was documenting an alternative scan methodology using an agentless API-based approach through the cloud provider's native assessment tooling. The auditors accepted it because the control coverage was identical and the evidence trail was cleaner than what a traditional scanner would have produced anyway.
Common mistakes that waste time
Skipping the evidence specification. Many templates have a field for evidence type but leave it blank or write "screenshot" as the only option. Screenshots don't prove anything by themselves. You need to specify the output file format, the tool parameters, the timestamp requirement, and where the artifact gets stored. This takes maybe ten minutes per control but saves hours during report writing. Assuming one test method per control. NIST 800-53A lists multiple examination, inspection, and interview procedures for most controls. A good plan documents which procedure is selected and why, especially when you're choosing an interview-based approach over an automated test. Automated tests miss social engineering components, configuration drift that happened after patching, and access review gaps. If your plan only uses automation, your assessment is already incomplete for IRM and AC family controls. Putting dates that don't account for scope changes. Assessment plans often show a fixed schedule, but scope changes during testing are normal. A new subnet gets discovered, a service owner isn't available for interviews, or a vulnerability scan reveals a host that wasn't in the asset inventory. I build in a buffer of roughly 15 to 20 percent of total estimated hours for scope adjustments, and I note in the plan that the schedule is subject to change based on scoping findings.
Get the Full Details
When the template approach breaks down
The biggest limitation is that a template assumes a stable system boundary. Continuous deployment environments, containerized microservices, and multi-cloud architectures change boundary definitions faster than a plan can be updated. If you're assessing a Kubernetes cluster with auto-scaling pods that restructure every few hours, a traditional Nist Security Assessment Plan Template becomes outdated within the first assessment window. In those cases, I shift to a risk-based sampling approach instead. Rather than trying to cover every control instance, I document the sampling methodology, the population definition, and the confidence level. The plan becomes more of a framework than a checklist, and the focus moves to whether the testing methodology itself is defensible rather than whether every box is checked.
Where to find a usable Nist Security Assessment Plan Template
Government agencies typically use the templates provided through their Authorizing Official or RMF process, which are usually available on the organization's security compliance portal. Public sector templates from NIST themselves are hosted at csrc.nist.gov under the Risk Management Framework documentation section. Commercial organizations can adapt the same structure using FedRAMP's low-medium-high baseline templates as a reference point, since those are built directly from the same 800-53A control assessment guidance. The key is modifying the template for your environment rather than using it verbatim. A template that worked for a monolithic on-prem database server will give you false confidence if you paste it directly into a plan for a serverless API gateway. The control mapping changes, the test methods change, and the evidence requirements change. The structure stays the same, but the content needs to reflect what you're actually assessing.