What actually goes into a Nist Security Assessment Report Template
Most people grab a generic template and start filling in checkboxes. That produces something that looks right but won't survive a real assessment review. The Nist framework doesn't hand you a single official document you download from their site. It gives you a process — SP 800-37 is the main one — and leaves the report format to your organization's judgment. That gap between what the standard says and what you actually produce is where things fall apart. A proper report needs to connect findings back to specific control families in SP 800-36 Rev 4. It needs to show evidence trails. It needs to separate what you tested from what you found. The Nist Security Assessment Report Template you build should reflect that architecture from day one instead of retrofitting it after the fact.
Why the Nist Security Assessment Report Template matters for actual audits
I've seen assessment reports that took six weeks to complete because the team had no structure going in. They spent three of those weeks figuring out how to organize evidence. Once I switched to a standardized template with pre-built sections mapping directly to control families, the same scope came back in about nine business days. The difference wasn't faster testing. It was not wasting time reorganizing findings later. The template should include an executive summary section written last. Most people put it first and then have to rewrite it entirely once findings are finalized. Include a scope definition with system boundaries and network diagrams. Include a methodology section explaining assessment type — walkthrough, interview, test, or a combination. Include a control-by-control findings table with status columns: implemented, partially implemented, not implemented, or not applicable. Every finding needs an associated control ID, a severity rating, and the evidence reference that supports it.
The structure that actually works in practice
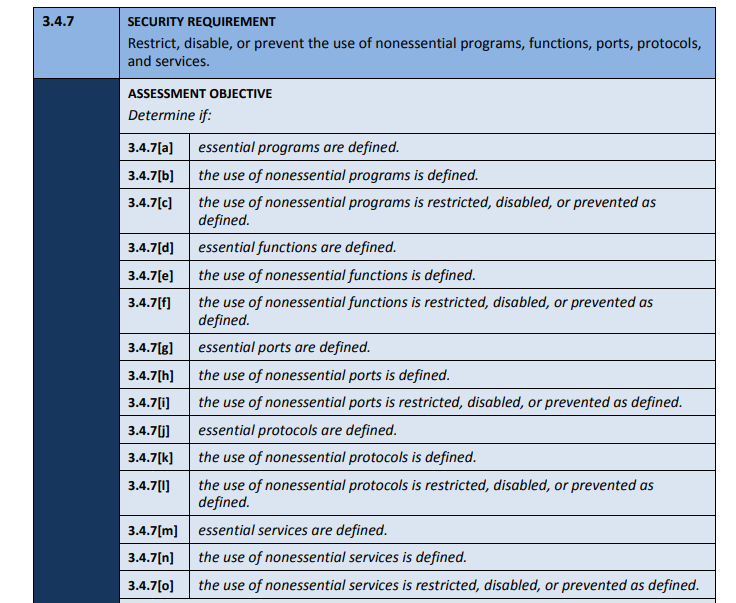
Start with system information. This sounds basic but it is where most reports get confused. Define the system name, classification level, responsible official, and the FISMA impact level. Then define the assessment boundary clearly. Include what is in scope and what is explicitly out of scope. I once had a assessor claim our external-facing web app was assessed when the report scope only covered the internal database tier. That disconnect caused a major dispute during the authorization review. We spent two weeks reconciling the boundary definitions. After the scope, document the assessment methodology. Specify which Nist publication guided the work — usually SP 800-53 Rev 4 or Rev 5 depending on when the assessment was planned. List the assessment types used for each control. Walkthrough means you reviewed documentation. Interview means you spoke with personnel. Test means you executed technical procedures. Most controls require a combination of at least two of these methods to be considered adequately assessed. The findings section is the core. Each finding should have a unique identifier, the control number from SP 800-53, the control title, the assessment method used, the observed condition, the risk determination, and a recommendation. Keep recommendations actionable. "Improve security" is useless. "Implement MFA on all remote access solutions per IA-2(1)" is something an engineer can actually work from.
Get the Full Details
Common mistakes that derail the whole process
Using Rev 4 controls with a Rev 5 assessment framework is the most common error I encounter. The control numbers changed between revisions. AP-4 became PE-4 in Rev 5. AC-2 stayed the same but added new subcontrols. If you mix versions you will reference controls that do not exist in the framework your authorizing official expects. Crosswalk the control numbers before you begin writing anything. There are published mapping tables on the Nist website that cover this. Use them. Another issue is the severity scoring approach. Some teams use subjective ratings like high, medium, low without tying them to a defined criteria. Others try to apply CVSS scores to governance controls where they do not belong. CVSS works for vulnerabilities in software. It does not work for access control policies. Use the FISMA impact level — low, moderate, high — to determine finding severity. A finding against a high-impact system control is automatically more severe than the same finding against a low-impact system. Duplicate findings across multiple control families is also a recurring problem. A single weakness in identity management often touches AC-2, IA-2, and AU-2 simultaneously. Writing three separate findings for the same root cause inflates the report without adding value. Link them to the common control and note the relationship instead of repeating the same observation three times.
Building a template you can reuse across assessments
Create a master template document with placeholder sections for every required element. Do not build a new template for each engagement. The slight variations between systems matter less than the consistency of structure across engagements. Authorizing officials and auditors benefit enormously from seeing the same format repeatedly. It makes cross-system comparisons possible. Include a version history log. Track template updates because the underlying Nist publications change. SP 800-53 Rev 5 added controls that did not exist before. CN-2 and PL-8 are examples. If your template does not account for newer control families it becomes obsolete the moment an assessor references them.
Limitations you should know about upfront
A template only helps if your team understands the controls it references. A beautifully formatted report with shallow findings is worse than a sparse report with deep analysis. I have seen organizations produce impressive-looking documents that an assessor dismissed in fifteen minutes because the evidence columns were empty or referenced non-existent logs. The template cannot compensate for missing technical evidence. Automated reporting tools promise to generate these documents from scanner output. They can handle the technical vulnerability portion reasonably well. They struggle with governance and process controls that require human judgment. Interview results, policy reviews, and walkthrough observations do not export from a Nessus scan. Plan for manual effort on the non-technical controls regardless of what tooling you use. The biggest bottleneck is usually the evidence collection phase, not the writing phase. Building the template takes a few hours. Collecting sufficient evidence for every control in scope across a mid-size system typically requires two to four weeks of dedicated effort. Schedule accordingly.
Downloadable Nist Security Assessment Report Template guidance
Nist does not publish a single ready-to-fill template document. Their closest offering is the sample assessment plan in SP 800-37 Appendix F, which you can use as a structural reference. Many organizations derive their own templates from that appendix combined with their CERP guidance. If you need a starting point, adapt the sample plan format into a full report structure rather than inventing something from scratch. The control mapping tables and assessment type columns in that appendix translate directly into report sections. Set up your spreadsheet or document with the control family columns, the assessment method fields, and the evidence reference column before you assign anyone to fill it in. Deciding that after work has started is the most reliable way to waste time and produce inconsistent results.