Working with the NIST Security Impact Analysis Template
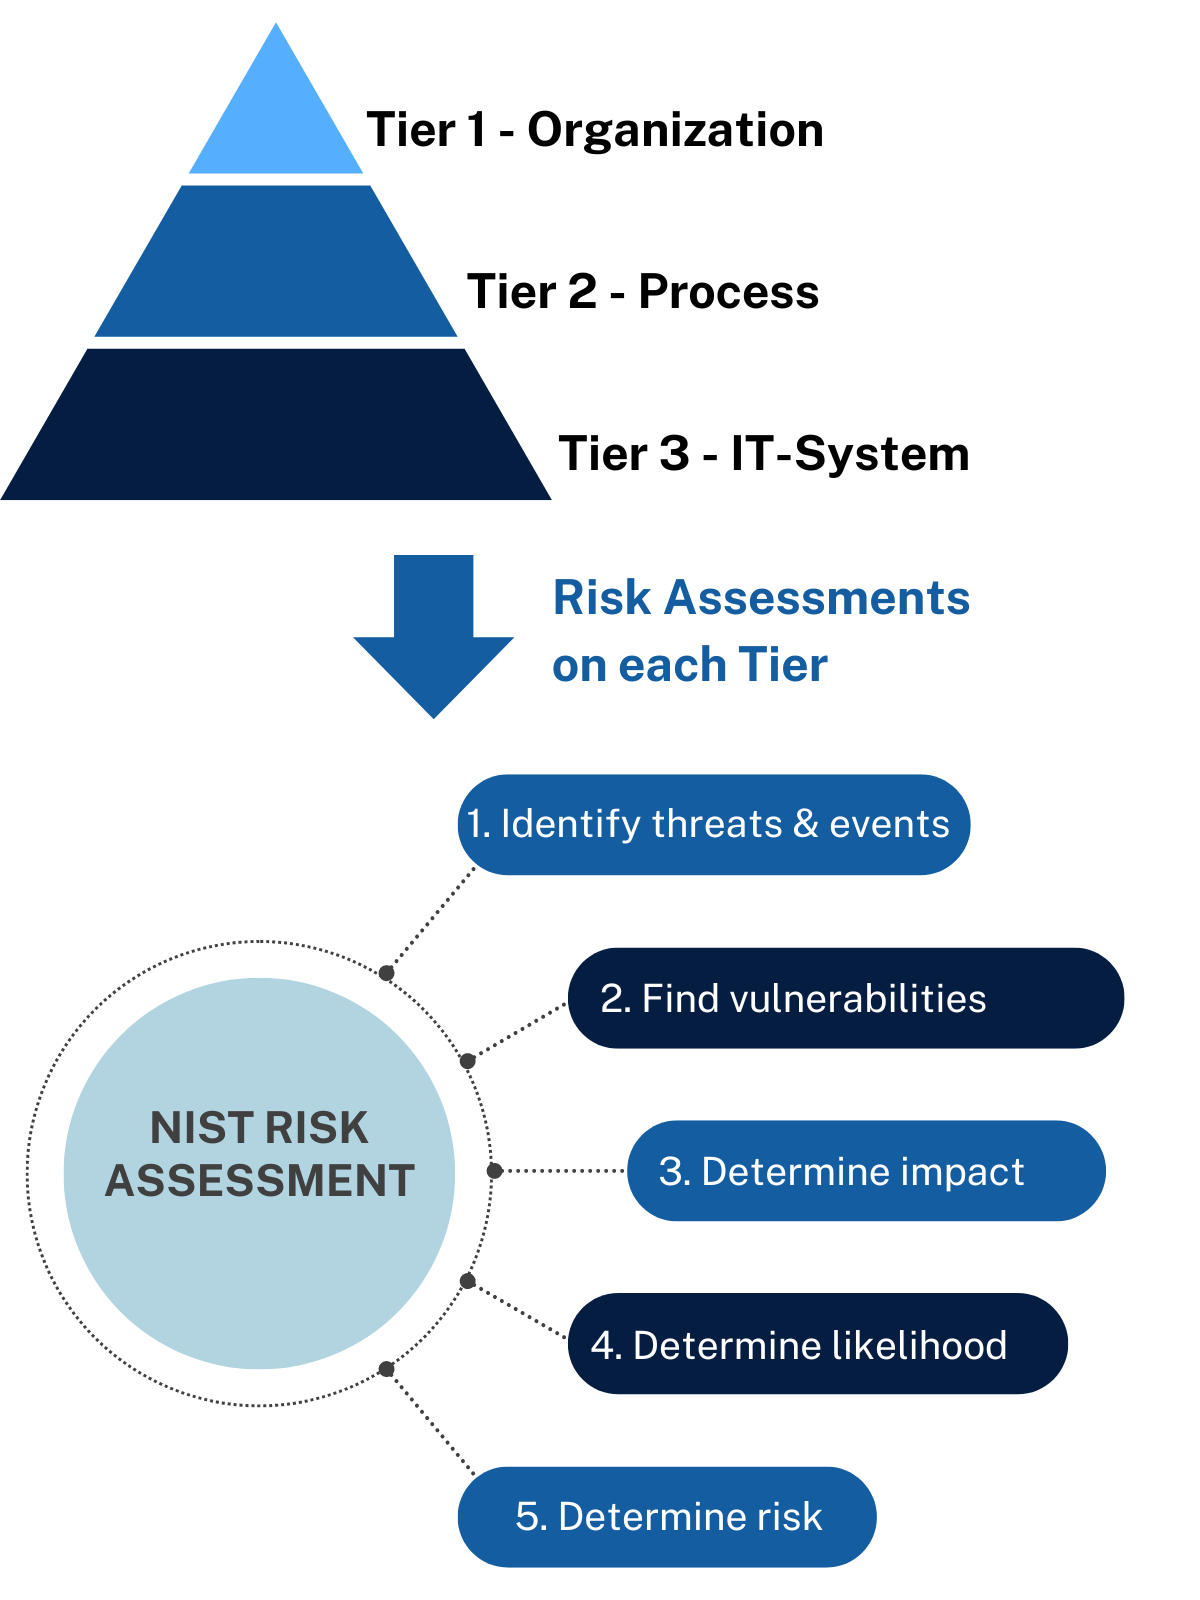
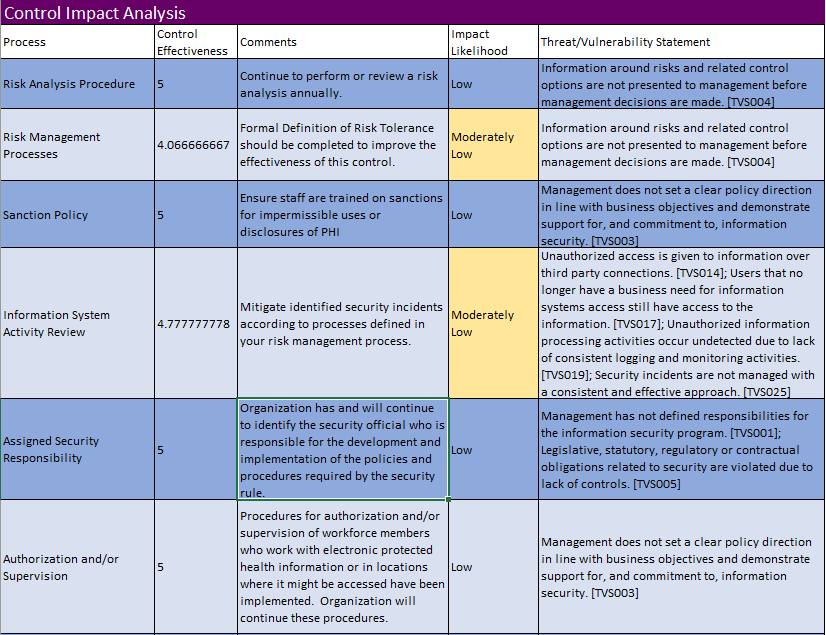
Most organizations rush through this part of their compliance work because they don't realize it's the section auditors actually scrutinize the most. The Nist Security Impact Analysis Template is not some optional formality. It is the document that ties your risk assessment to actual security controls, and getting it wrong means your entire compliance posture looks suspicious to anyone reading it. I ran into a real problem recently with a client who had literally copied a previous template from a different system into a new assessment. The control mappings looked correct on the surface, but the impact levels didn't match the sensitivity of the new system. We had a high-impact system where the template still showed moderate impact across the board. It took about four hours to catch before an auditor would have. The fix was going back to FIPS 199 and manually recalibrating each boundary condition against the actual data flows. Never skip that step. Templates are starting points, not finished products.
Using the Nist Security Impact Analysis Template Correctly
The template works in a straightforward sequence. You start by defining the system boundary, which means drawing a clear line around what is and is not included in your assessment. This is where most people make mistakes. I have seen teams include third-party SaaS tools in the boundary without noting them as separate systems, and then omit them from the control implementation entirely. The template has a section for this distinction, but you have to fill it out deliberately. Leave it blank and the auditor will assume you overlooked it. Next comes the categorization of information types. You map each data flow to a confidentiality, integrity, and availability impact level. Low, moderate, or high. These are defined in FIPS 199 and you cannot just pick levels that feel convenient. The highest impact rating across any three properties determines the overall impact level of the system. This single rule causes problems constantly because people average the values or pick the most common one instead of following the standard. Pick the highest. Always. Once the impact levels are set, you move into the control baseline selection. The NIST framework provides recommended baseline controls for each impact level, but the real work happens in the tailoring phase. You read through each control in the baseline and determine whether it applies to your environment. Controls that do not apply get documented with a reason, not just skipped. Skipping a control without justification is essentially admitting you have an unaddressed gap. Write a sentence explaining why. "Not applicable because this system does not process payment card data" is the kind of explanation that satisfies an auditor. "Does not apply" does not.
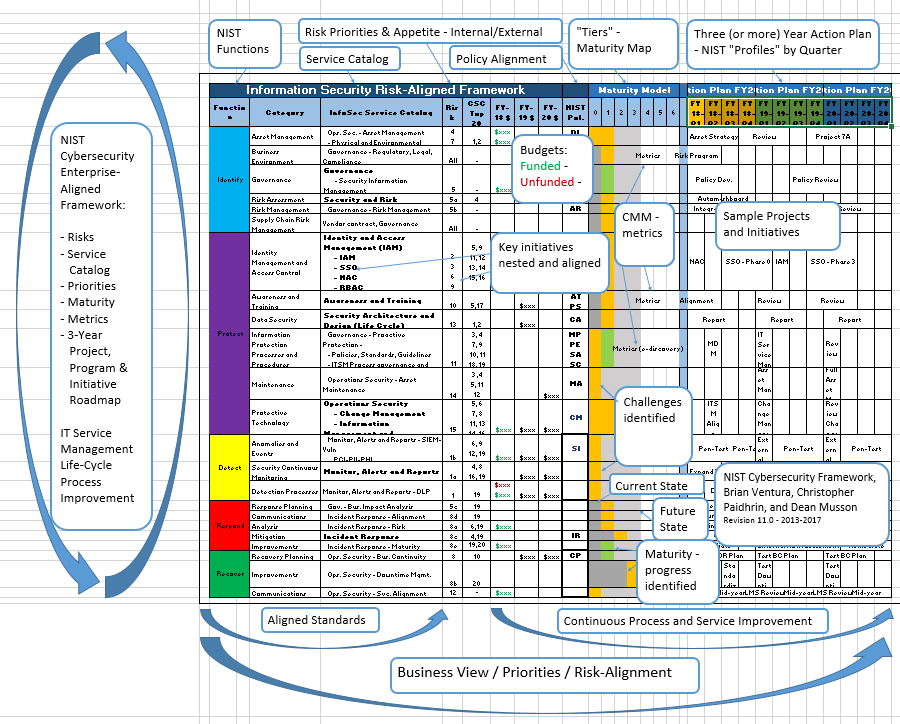
The final section involves documenting the authorization process and the continuous monitoring plan. This is where templates are least helpful because every system has different monitoring requirements. The authorization package needs to include the system security plan, the results of your control implementation assessment, and the plan of action and milestones. The monitoring plan needs frequency, responsible parties, and thresholds. Without all three elements for each, the documentation is incomplete and will be flagged. The full template can be found in NIST Special Publication 800-37, Revision 2, which covers the risk management framework. You will also find companion templates in SP 800-39 for program-level coordination. Many organizations consolidate these into an internal document format, which is fine as long as every required field from the source material is represented. Compression is acceptable. Omission is not. One thing nobody tells you about this template: it does not account well for supply chain risk. If you are integrating components from multiple vendors, the standard template will not ask you about any of it unless you explicitly add that section. I started creating a supplemental vendor impact annex about three years ago and it has saved me from at least two compliance failures. The annex tracks each third-party component, its access level to your system, and the security controls it is expected to meet. It takes about twenty minutes to set up once, then maybe ten minutes per vendor add or change. Worth every minute.
Get the Full Details
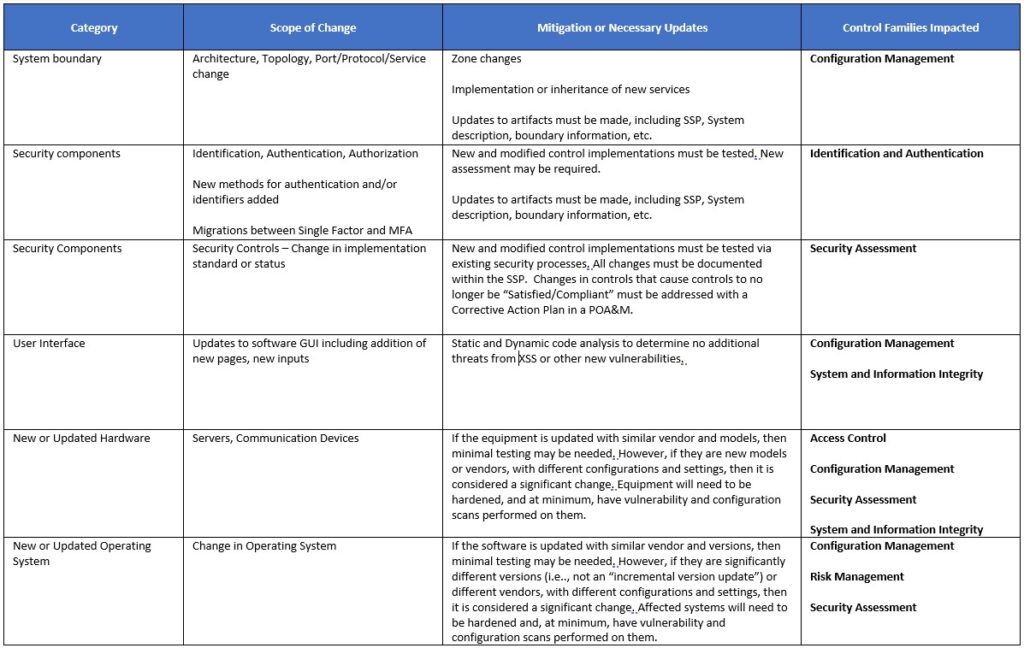
Another practical issue is version drift. When you update a system, the template often becomes stale because people update the system diagram but forget to revisit the impact analysis. I recommend a simple rule: any change to a system component triggers a review of the entire template, not just the affected section. It is easier to do the review while the change is fresh than to discover a mismatch six months later during an audit. The template is available freely from the NIST website under SP 800-37 documentation. There is no paid version. Anything asking you to pay for it is not the official template. The government also maintains a Risk Management Framework portal at nist.gov/itl/specs/rmf.cfm where you can download the current revision and any associated spreadsheets or worksheets that some teams find easier to work with than the prose-based template. If your organization handles federal information, this process is mandatory. If you are in the private sector, many contracts and insurance requirements now reference the same framework, so the effort applies there too. The documentation you produce serves double duty: it satisfies regulatory requirements and it actually improves your security posture because the exercise forces you to think about what data you have, where it lives, and what happens if it goes wrong. That last part is the one most people gloss over, and it is the one that matters most when something actually breaks.