NYDFS 23 NYCRR 500 Compliance Is More Exhausting Than the Rulebook Suggests
Most teams approach the New York DFS cybersecurity risk assessment expecting a checklist they can hand off to a junior analyst and move on with. That does not work. The regulation requires a documented assessment of cybersecurity risks across the entire organization, but it also requires you to explain how you determined which risks mattered most, what controls are in place for each one, and where the gaps actually are. The nuance is in the documentation, not the template. Under 23 NYCRR 500.13, covered entities must perform a risk assessment at least annually. This applies to financial institutions with over $50 million in assets or roughly $5 billion in total global assets if they operate as insurance companies. The assessment needs to evaluate both internal and external threats, identify systems and data that are material to operations, and determine which risks the existing controls can address and which ones remain unacceptably high. It is not enough to say your controls are good. You have to show the reasoning. I spent about six months helping a mid-size bank bring their assessment into compliance after their last one got rejected during a DFS exam. The examiner sent back three pages of findings and every single one came down to the same problem. The bank listed controls without tying them to specific threats or risk scenarios. They had an intrusion detection system, but no documentation showing how that system mapped to the phishing and ransomware vectors that the DFS guidelines explicitly flag as primary concerns. Fixing it meant rewriting about eighty percent of the original document to include threat scenarios, likelihood ratings, impact assessments, and control mappings for each one.
The most common mistake I see is treating the risk assessment as a static annual event. It should be treated as a living process. The regulation requires a refresh when there are material changes to infrastructure, operations, or threat landscape. A major cloud migration, a new payment processor, or a significant breach all trigger the need to update. Several organizations I work with have started doing quarterly reviews instead of relying on a once-a-year exercise because the threat environment shifts fast enough that annual updates create blind spots that regulators notice immediately.
Building an Assessment That Actually Passes Scrutiny
Start by identifying all systems and data assets. Not just the production ones, but the backup infrastructure, third-party integrations, and legacy systems that still process transactions. The DFS guidance specifically calls out third-party risk, and examiners routinely cite gaps in vendor management. If you have a relationship with a payment processor or a core banking provider, you need documentation showing how you evaluate their security posture and what your contractual safeguards require. I had a client who failed their assessment because they could not produce evidence of reviewing their cloud provider's SOC 2 reports. They assumed the contract was sufficient. It was not. After asset identification comes threat modeling. You need to go beyond generic threat lists and map threats to your specific environment. The regulatory framework gives you categories, but the examiner wants to see how you applied those categories. For example, the regulation mentions denial of service as a threat. A generic threat library says distributed denial of service attacks exist. A real assessment says your internet-facing API gateway that handles customer onboarding is exposed to DDoS, your mitigation involves AWS Shield Advanced with a failover to a secondary region, and the last test of that failover happened in March 2025 with a forty-second recovery window. Likelihood and impact ratings are where most teams stumble. They assign numbers without criteria. If you say a particular threat is high likelihood, the examiner will ask how you determined that. What data supports the rating. If you cannot point to internal incident history, industry benchmarks, or published threat intelligence, your rating is essentially an opinion, and opinions do not satisfy regulatory requirements. I recommend using a scale where each level has a clear definition. Low means the event has not occurred within the organization or industry in the past five years. Medium means there is historical precedent but limited frequency. High means the event has occurred multiple times or current threat intelligence indicates elevated activity. This takes time but it also prevents the kind of pushback that derails review cycles.
Get the Full Details

Impact assessment follows the same logic. Use financial impact, operational disruption, reputational damage, and regulatory consequences as the four dimensions. Rate each one on a scale from negligible to catastrophic. A data breach affecting customer personal information typically scores high across all four dimensions for a financial institution. A phishing attempt that gets blocked by email filtering might score low on impact but still warrant a medium likelihood rating given the industry context.
Mapping Controls to Identified Risks
Every identified risk needs a corresponding control or a documented plan to address it. The control can be preventive, detective, or corrective. It can be technical, administrative, or physical. What matters is that there is a clear link between the risk and the response. If you identify ransomware as a high-priority threat, you need controls that address prevention such as endpoint detection, awareness training, email filtering, and network segmentation, controls that address detection such as anomaly monitoring and log aggregation, and controls that address response such as backup integrity checks and incident response procedures. Compensating controls are acceptable under the regulation if the primary control is not feasible, but you need to document why the primary control is not viable and how the compensating control provides equivalent protection. I worked with a regional credit union that wanted to use manual password rotation policies as a compensating control for automated privileged access management. The examiner rejected it. Manual rotation is not equivalent to automated enforcement because it introduces human error and audit gaps. The workaround was to phase in a cloud-based identity solution that fit their budget over eighteen months while documenting the interim controls they used to manage risk in the meantime. The register of controls should be a separate document linked to the risk assessment, not buried inside it. This makes updates easier and gives examiners a clear reference point. Include the control name, the risk it addresses, the control type, the owner, the implementation status, and the results of the most recent test or review. A control that has never been tested is a control that has never been verified. Examiners do not trust untested controls.
Documentation Standards and Common Pitfalls
The assessment itself should be a single coherent document that an examiner can read without needing a glossary or a walkthrough. Use plain language. Define any acronyms the first time they appear. Include an executive summary that states the overall risk posture, the top five risks, the status of critical controls, and any open remediation items. Most professionals skip the summary because they think the details are sufficient. They are wrong. The summary is usually what an examiner reads first, and if it is vague or missing, it sets a negative tone for the entire review. One counter-intuitive thing about the NYDFS framework is that admitting your risk posture is not optimal can actually help you. Organizations that present their assessment as a perfect zero-risk state tend to look either uninformed or evasive. The regulation expects you to acknowledge residual risk. The question is whether you have identified it, documented it, and have a plan to reduce it. A well-written assessment will explicitly state which risks remain at an acceptable level and which ones require ongoing remediation investment. Another pitfall is over-reliance on third-party audit reports. A SOC 2 Type II report from your cloud provider or your core platform vendor is useful, but it is not a substitute for your own risk assessment. The DFS guidance requires you to assess risks to your own operations, and that means you need to understand how vendor controls affect your specific environment. I had a situation where a client submitted their entire risk assessment as a single appendix of vendor audit reports. The examiner returned it and asked for evidence of independent assessment. The client had to spend another three weeks building out their own threat models and control mappings from scratch.
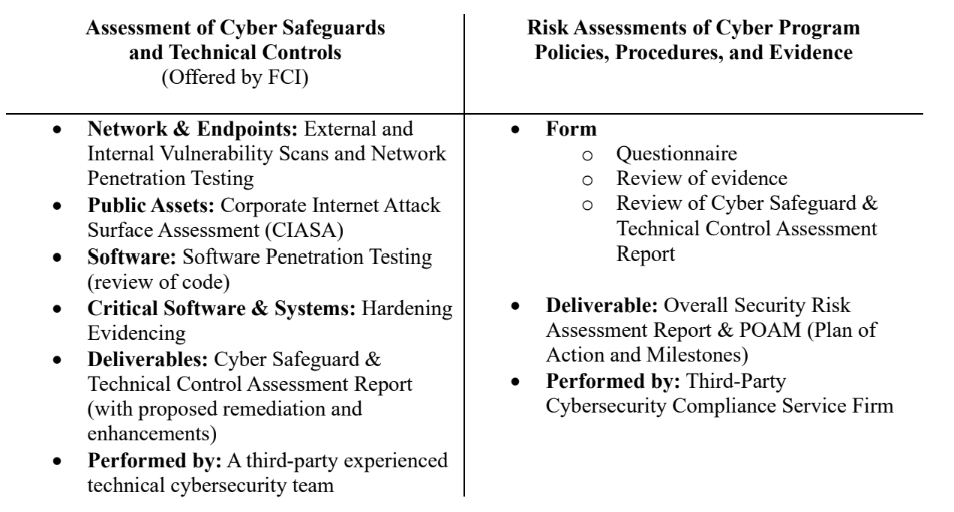
The review cycle should include a section on lessons learned from the previous assessment period. Document any incidents that occurred, any controls that were implemented or changed, any new threats that emerged, and any gaps that were identified during internal testing. This shows continuity and demonstrates that the organization is actively using the assessment as a management tool rather than a compliance checkbox.
Practical Workflow for Smaller Organizations
Smaller covered entities often try to complete the assessment in a single weekend. This rarely produces adequate results. A realistic timeline for a mid-size organization with moderate complexity is about four to six weeks of focused work. Break it down into phases. Week one is asset identification and scope definition. Week two is threat identification and historical data collection. Week three is risk rating and control mapping. Week four is draft review and gap analysis. Week five is finalization and management sign-off. Week six is distribution to relevant stakeholders and filing if required. If you lack internal expertise, hiring a consultant is common, but you still need to ensure the output meets your organization's actual operating conditions. A consultant who has never visited your network or spoken with your operations team will produce a generic document that looks reasonable but fails scrutiny when examined closely. I have seen this happen repeatedly. The best outcomes come from consultants who work alongside your team, validate assumptions with your staff, and incorporate your actual incident history and operational constraints into the assessment. The final document should be stored in a controlled location with version history. Changes to the assessment should be tracked and dated. When you update the assessment after a material change, reference the prior version and note what triggered the update. This creates an audit trail that examiners can follow easily.
What the Assessment Does Not Cover
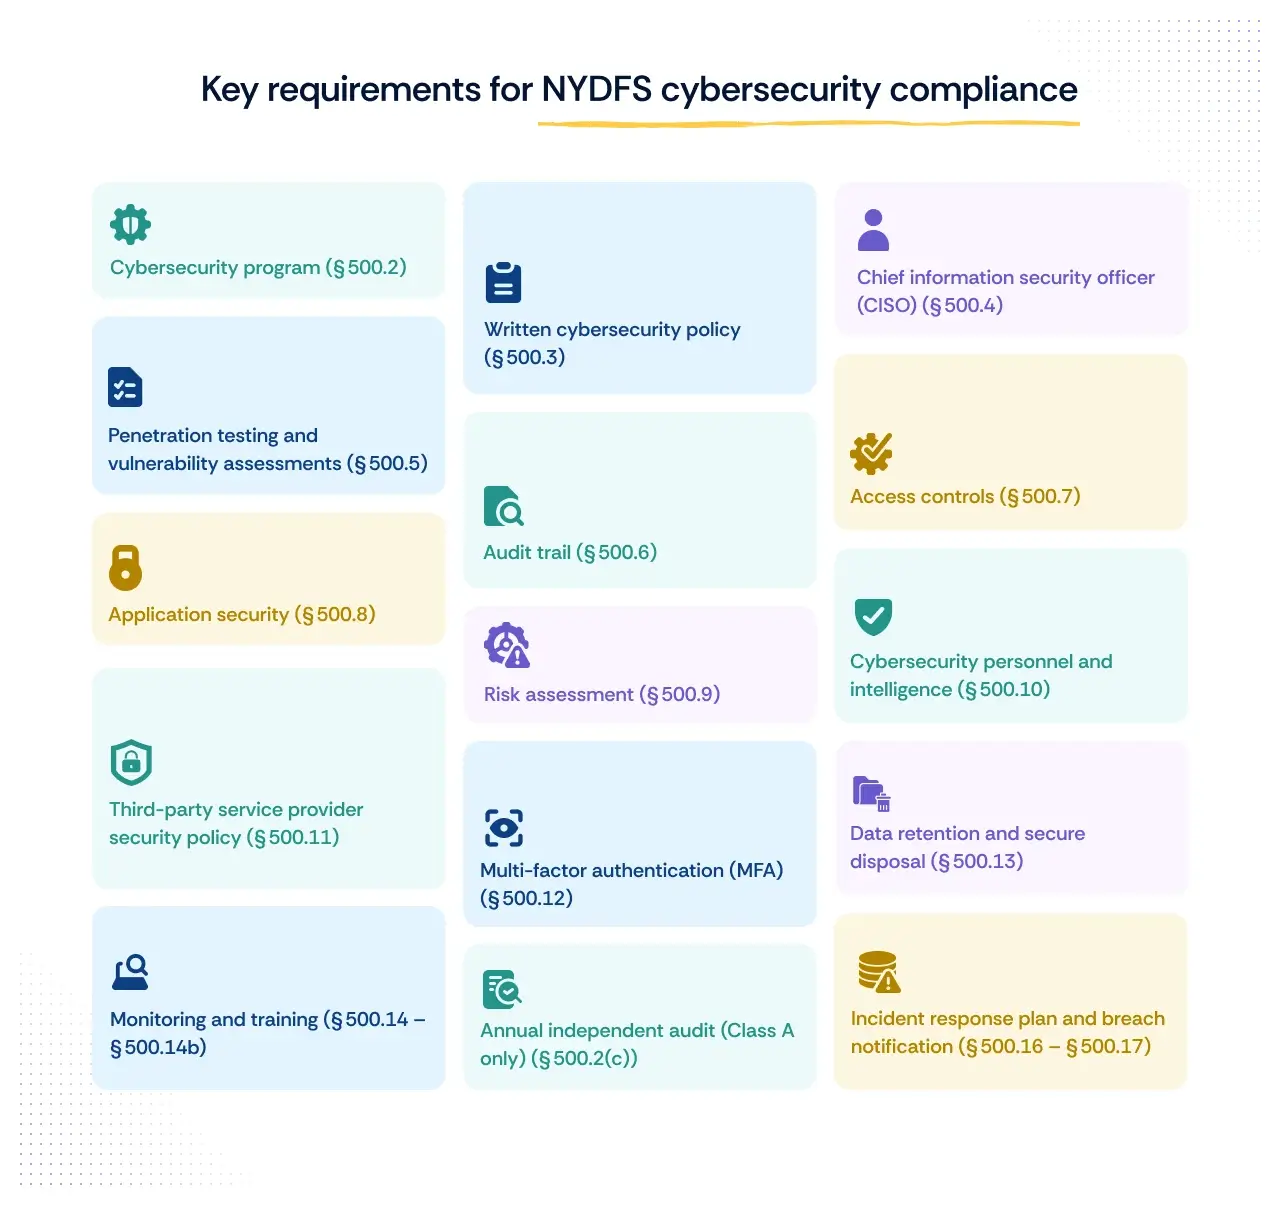
It is worth noting that the NYDFS cybersecurity risk assessment is one component of the broader compliance framework. It does not replace the cybersecurity policy required under 500.05, the incident response plan required under 500.11, or the penetration testing requirements under 500.15. Each of these elements has its own requirements and timeline, and they need to be internally consistent. If your risk assessment identifies a specific threat but your incident response plan does not include procedures for responding to that threat, the examiner will flag the inconsistency. Alignment across all three documents is something I have seen slip through multiple times simply because different teams drafted each document independently without cross-referencing. Training requirements under 500.06 also connect directly to the assessment. The risks you identify should inform the content of your cybersecurity awareness training. If your assessment highlights phishing as a primary vector, your training program should address phishing explicitly. If your assessment identifies weak password practices as a contributing factor to risk, your training should cover password hygiene. This linkage is often missed but it strengthens the overall program significantly. The annual assessment deadline is tied to your calendar year unless your board designates a different period. Start early. The assessment process tends to expand beyond initial estimates because new risks surface during the documentation phase that were not apparent during the planning phase. Rushing it produces a thin document that will not withstand examination. A thorough assessment with clear reasoning, documented control mappings, and honest risk ratings is what actually protects the organization and satisfies the requirement.