What You Actually Need to Know Before You Start Testing
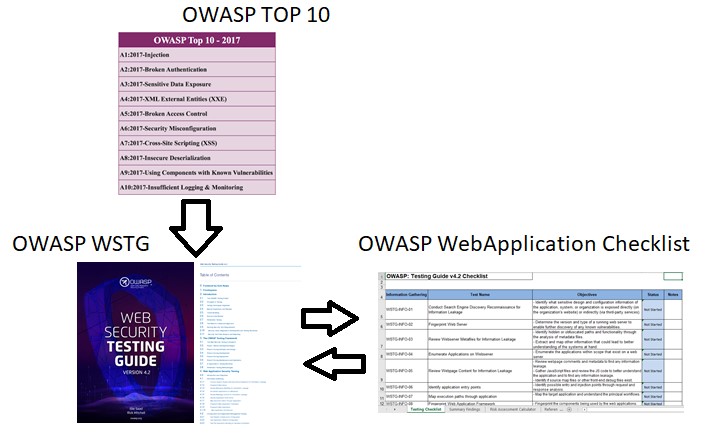
The OWASP API Security Top 10 is a living document, and the testing guide that accompanies it is one of those resources everyone bookmarks and then never actually uses. I've been running API security tests for over a decade across fintech, healthcare, and e-commerce platforms. The guide works, but it is not a checklist you can hand to a junior analyst and expect clean results. It is a framework that requires context, and the differences between passing a test and actually finding something worth fixing come down to how deeply you understand the underlying mechanics. At its core, the guide maps out testing procedures for each of the ten API-specific vulnerabilities. That sounds straightforward. The reality is that OWASP categories like broken object level authorization and lack of resources and rate limiting overlap in ways the guide does not always make clear. When I test an API, I do not approach it category by category. I look at the authentication flow first, then trace how tokens are used across endpoints, and then map which authorization checks are enforced client-side versus server-side. The guide gives you the what. You supply the how. One thing beginners consistently miss is that the guide assumes a certain level of API maturity. If you are testing a monolithic REST API with basic token auth, the testing procedures for cryptographic failures or server side request forgery might not apply in any meaningful way. On the other hand, if your API uses OAuth 2.0 flows across multiple microservices with JWTs passed in headers and query strings interchangeably, most of the categories become relevant simultaneously. I once spent three days testing a single endpoint because the API used a custom token format that blended elements from three different OWASP categories. Standard procedural checklists would have missed it entirely.
How to Actually Use This Guide Without Wasting Time
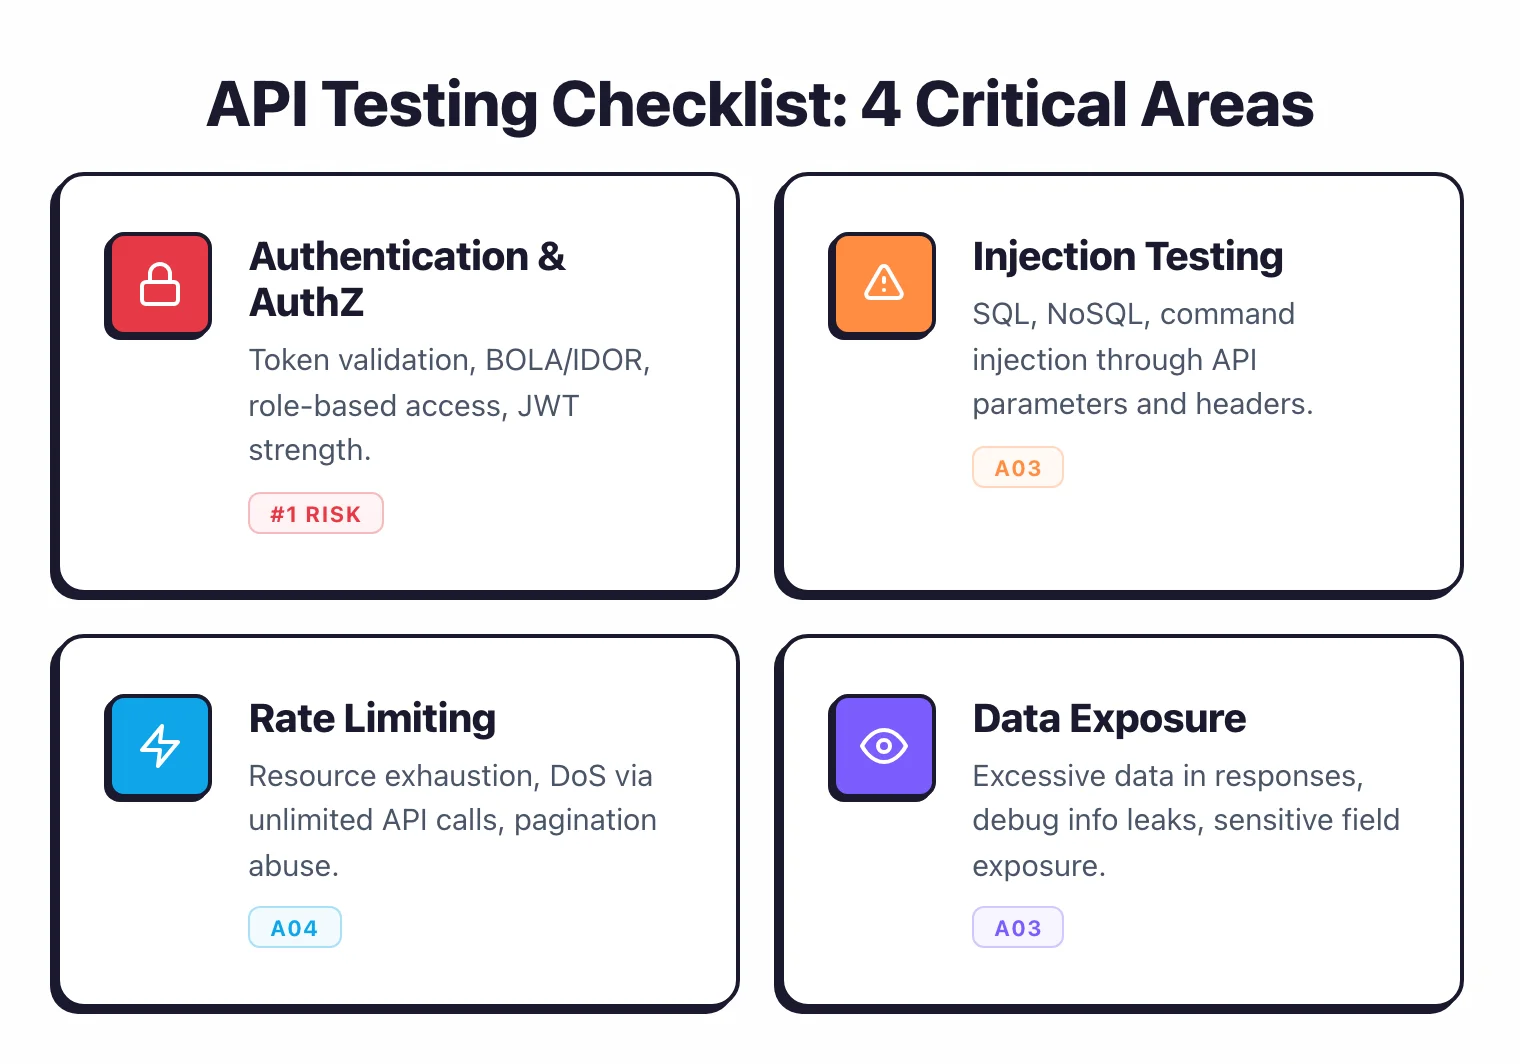
The most effective approach I have found is to start with the API's technical documentation, not the guide. Pull the OpenAPI spec, read the authentication section, and identify every token type in play. Then open the OWASP API Testing Guide and work backwards from what you already know about the system. This reverses the common mistake of reading the guide first and then trying to force it onto the target. For Insecure Direct Object References, which is A01 in the current version, the guide tells you to enumerate identifiers. That is technically correct but practically incomplete. The real test is understanding the data model. I worked on a healthcare API where patient IDs were sequential integers, which made enumeration trivial. But the API also had a secondary lookup table that mapped internal UUIDs to visible IDs in most responses. A tester following the guide mechanically would catch the integer endpoint but miss the UUID leakage through the lookup endpoint. The vulnerability was the same category but required two separate probing strategies. Broken Authentication, A02, is where most teams cut corners. The guide covers token expiry, refresh token rotation, and credential stuffing. What it does not emphasize enough is the interaction between authentication mechanisms when an API supports multiple. I tested a payment platform that accepted both API keys and JWTs interchangeably on the same endpoints. The test procedure for each mechanism was sound in isolation, but the combined behavior allowed token substitution attacks that neither standalone test would reveal. If your API has mixed auth methods, add a dedicated testing step for cross-mechanism interactions before you move on.
Where the Guide Falls Short and What to Do Instead
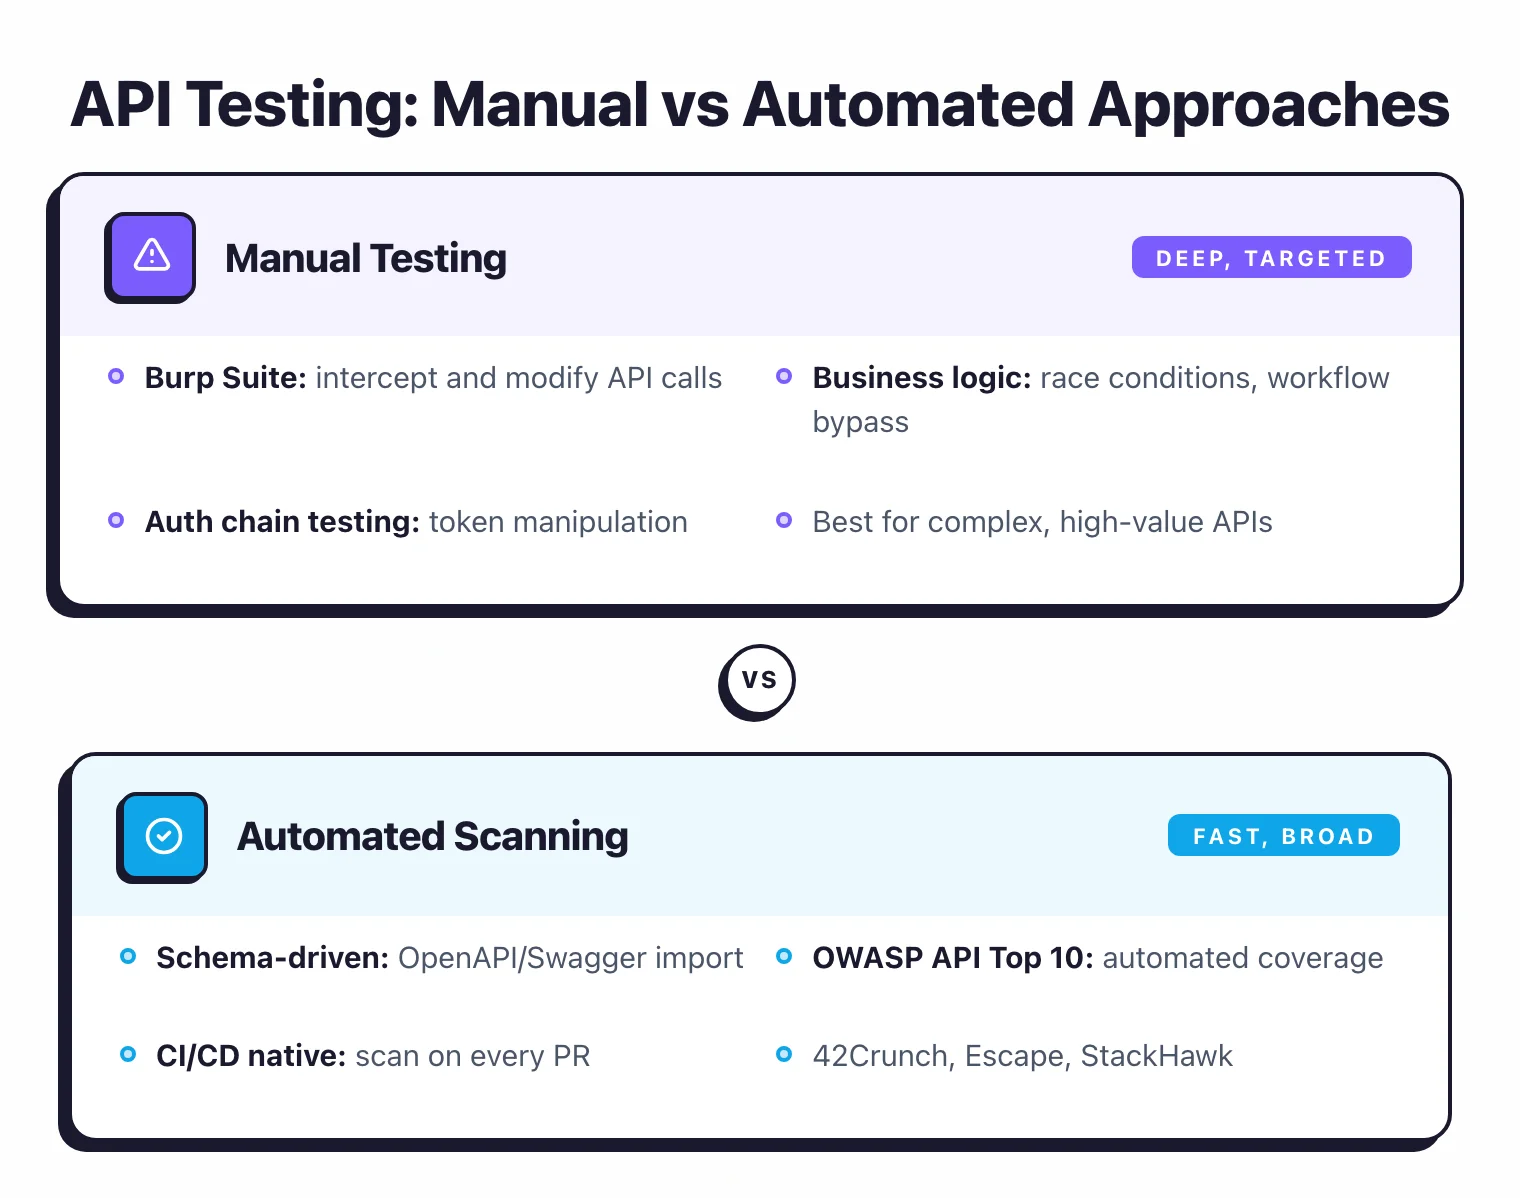
The guide is strong on traditional web application vulnerabilities ported to API contexts. It is weaker on modern architectural patterns. Serverless APIs with event-driven architectures, GraphQL endpoints, and gRPC services are either underrepresented or addressed only superficially. If you are testing a GraphQL API, the guide mentions some GraphQL-specific considerations in a few sections, but you will need to supplement it with the OWASP GraphQL Cheat Sheet and custom fuzzing strategies for nested queries and introspection abuse. Another gap is mass assignment testing. The guide references it under A04, but the procedures are generic. Real mass assignment vulnerabilities in APIs depend heavily on how your framework deserializes input. I use a combination of Burp Suite Professional with custom inline scripts and a Python-based fuzzer that generates edge-case payloads for every writable field. The automated tools catch the obvious cases. The manual testing catches the logic flaws where a field like is_admin appears in an unexpected nested object or where a rejected update on one field causes a partial state change that leaks information. For Rate Limiting testing under A07, the guide suggests sending repeated requests and checking for throttling. This is useful but insufficient. I test rate limits by checking multiple dimensions: per-user, per-IP, per-endpoint, and global. I also test whether rate limit counters reset predictably or have edge cases like timezone-based resets or session regeneration bugs. One e-commerce API I tested had rate limiting that reset at midnight UTC regardless of the user's actual session start time. This meant a user in Los Angeles could effectively bypass rate limits by waiting for the UTC rollover and making a new burst of requests. The guide would not have flagged this because the basic throttling was in place.
Get the Full Details
Practical Tools and Workflow
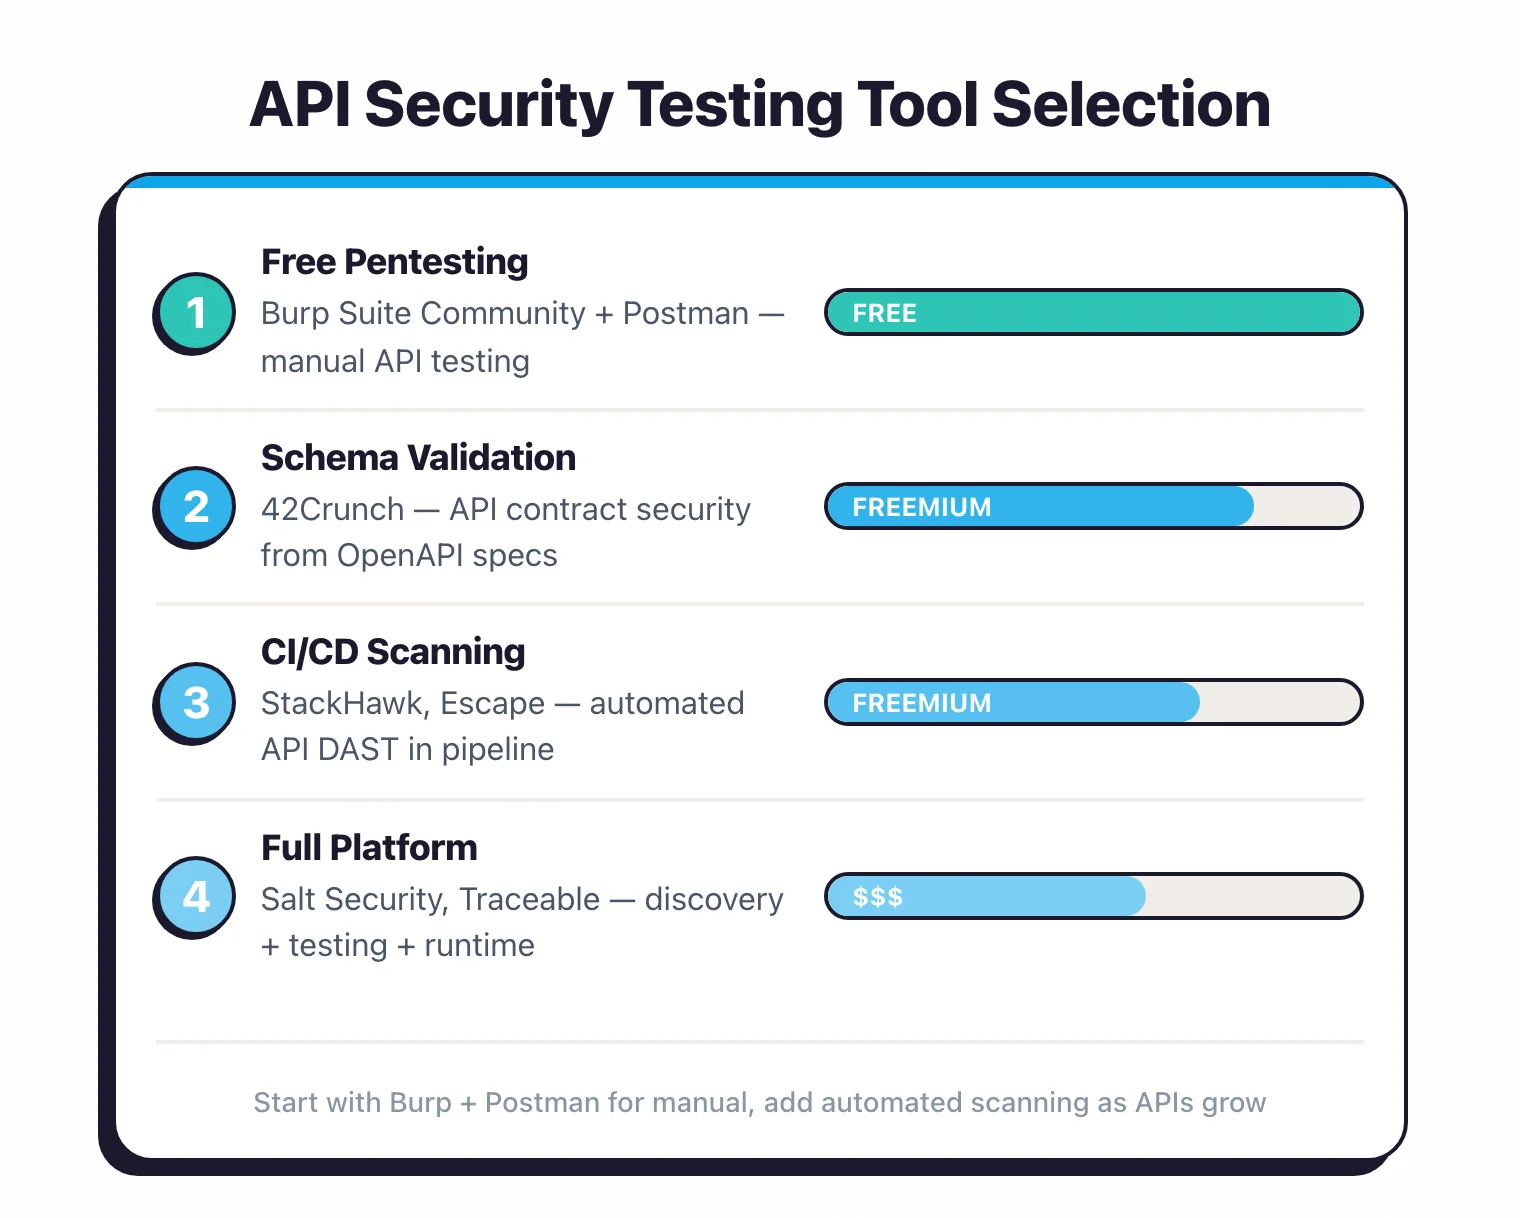
My standard workflow starts with OWASP ZAP for passive and active scanning, but I treat the scan results as a starting point, not a conclusion. ZAP's API scanning addons cover some OWASP categories well, but they miss context-specific issues that require understanding of business logic. I then move to Burp Suite for manual exploration and targeted exploitation. For programmatic testing, I write custom Python scripts using requests and pytest that encode the specific test cases from the guide tailored to my target's architecture. One practical tip that saves significant time: export your API spec and use it to generate a test matrix. Map each endpoint to each OWASP category and note which tests are applicable. This prevents you from running irrelevant procedures and helps you track coverage. I have a simple spreadsheet template that I adapt for each engagement. It takes about twenty minutes to set up and usually saves two to three hours of testing by preventing duplicate or irrelevant test runs. The guide is available freely on the OWASP website. Download it, read it, but do not treat it as a substitute for understanding how your specific API works. The vulnerabilities you find will depend more on your knowledge of the system than on how thoroughly you checked boxes against the guide. The ones you miss will always be the ones that exist in the gaps between categories.