Where to Start When You Are Given a Black-Box App and Two Weeks
I used to get handed URL lists with zero documentation and told to "test it." The first time I tried to work through OWASP resources, I spent three days just figuring out which document to actually open. There are too many of them. The OWASP Testing Guide V5 sits somewhere in the middle of that mess, and it is useful if you know how to use it. It is not a checklist you print and tick off. It is a reference manual organized by testing technique, not by vulnerability type. That distinction matters more than most people realize when they are three hours into a penetration test and their notes are already a disaster. The guide itself is available at https://owasp.org/www-project-web-security-testing-guide/. It is maintained by the OWASP Foundation. The current stable version is V5, which shifted the entire structure away from the old vulnerability-first layout. I picked it up when someone on my team asked why my findings kept missing the mark on risk scoring. The real problem was that I was skipping the methodology steps and jumping straight to exploitation. That is what the V5 version is designed to prevent.
Owasp Testing Guide V5
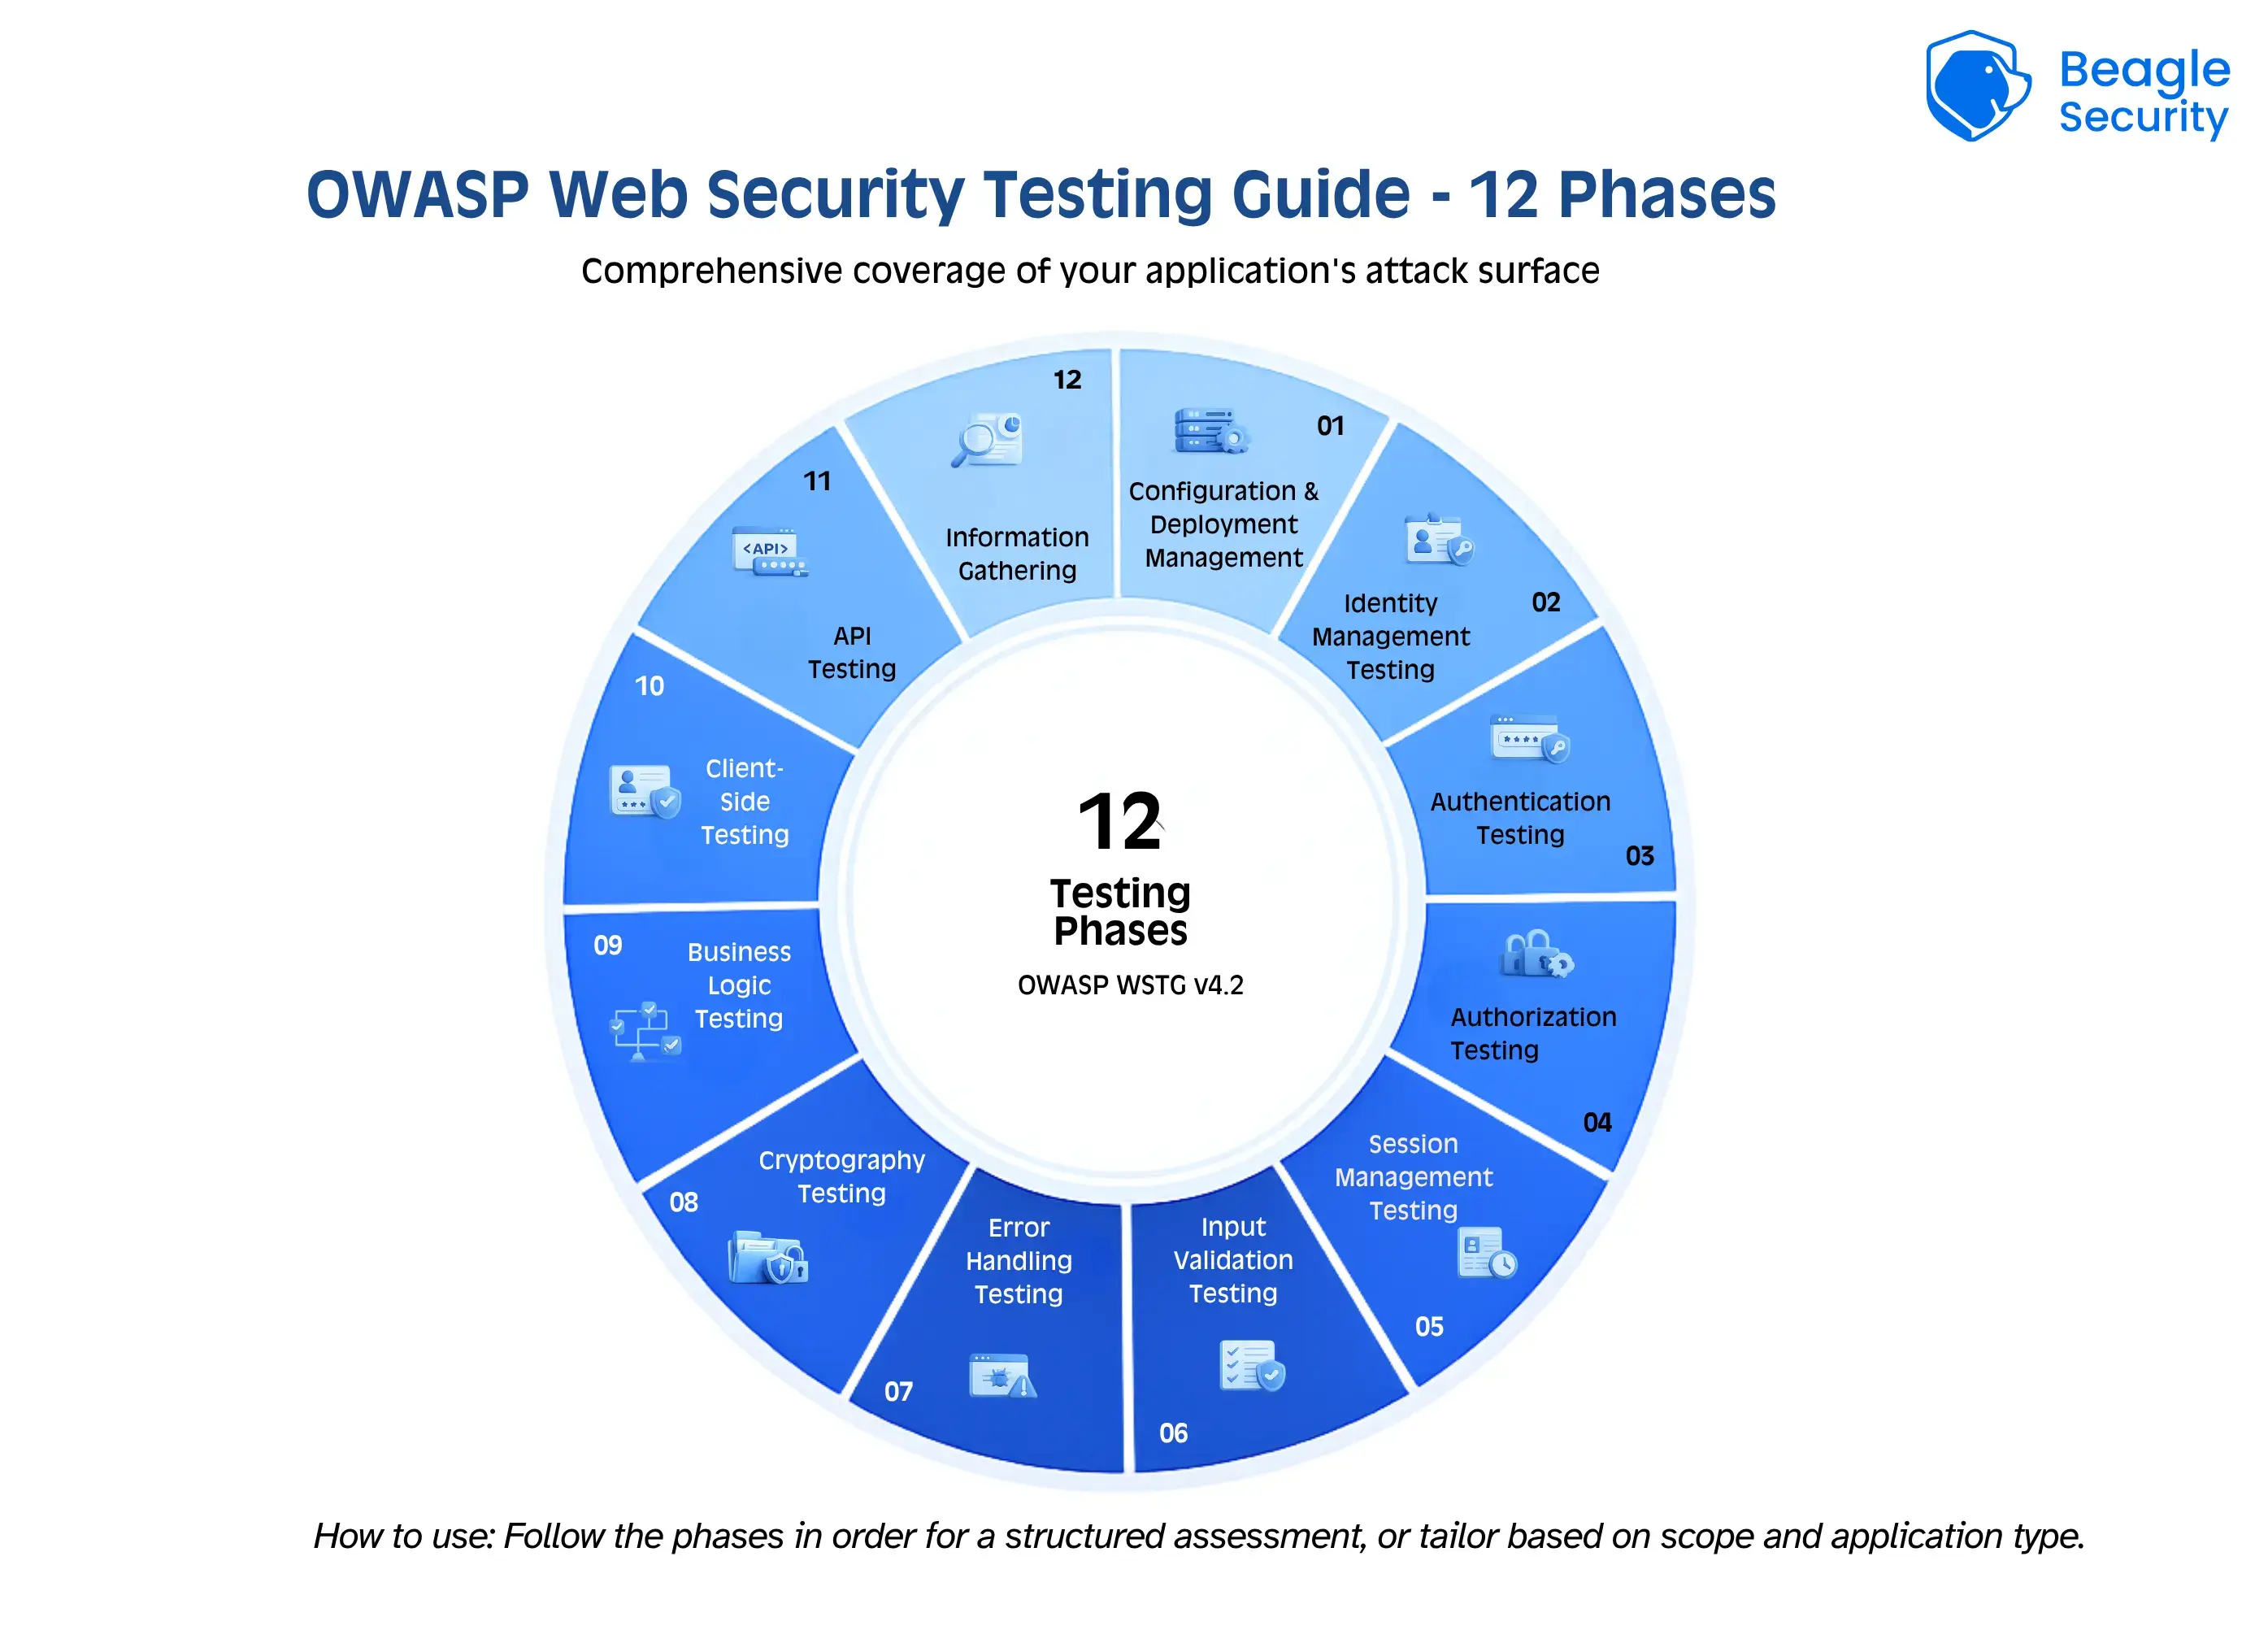
The guide is divided into four main parts. Part One covers preparation and planning. Part Two is the actual testing methodology broken into fourteen chapters. Part Three deals with reporting. Part Four contains appendices with things like regex patterns and payload lists. The testing methodology chapters are where most people spend their time. Each chapter follows the same skeleton: a goal statement, test objectives, test cases, and expected outcomes. The test cases are numbered in a hierarchical format like 4.1, 4.1.1, 4.1.2 so you can reference them in your report without guessing. Here is something most beginners miss. The guide assumes you already know how to useBurp Suite or OWASP ZAP. It does not teach you tool operation. It teaches you what to test for and in what order. I wasted about a week early in my career thinking the guide would walk me through proxy configuration. It will not. You need to handle the tool setup separately and then use the guide as your decision tree for what to do next. The fourteen methodology chapters map to specific attack surfaces. Information gathering comes first because it sounds obvious but most testers skip straight to scanning and miss the manual reconnaissance layer. The chapters cover authentication testing, session management testing, access control testing, injection flaws, CSRF, business logic testing, and a dozen other areas. Each chapter has a section called "Test Case" that breaks down into individual procedures. For example, Chapter 4 on Authentication has test cases like verifying password complexity enforcement, testing for credential stuffing resistance, and checking for account lockout mechanisms. The numbering lets you say "I tested AC-2 per testing guide section 7.2.1" and have it mean something concrete.
How I Actually Used It On a Real Engagement
Last year I was testing a healthcare API. The application claimed HIPAA compliance and had a superficial login page. I opened the Testing Guide V5 and started at Chapter 7, which covers access control. Test case 7.1 is about testing for bypassing access control checks on URL. I forced direct object references on patient records and found that the API accepted integer-based patient IDs without checking whether the authenticated user had permission to view that specific record. I pulled five thousand records before the rate limiter kicked in. The guide told me exactly which test case to follow. It did not tell me how to write the exploit, but it gave me the structure to document it properly. Another edge case that tripped me up involved test case 6.3 on session token placement in URLs. The app in question stored session tokens in both the query string and the cookie. Most tools flag the cookie version but ignore the URL version unless you are manually walking the application. I had to write a customBurp macro to capture the URL-based token on every request. The Testing Guide pointed me at 6.3, but the actual workaround for catching dual-token leakage required custom automation. I wrote a smallPython script that parsed theBurp history for requests containing session identifiers in the query string. It took me about forty minutes to put together and caught six additional endpoints the automated scanner had missed entirely.
Get the Full Details

What the Guide Gets Wrong or Leaves Out
The Testing Guide V5 is thorough but it is not fast. Going through every test case for a mid-complexity web application takes roughly two to three days of focused work if you are doing it manually. An automated scanner might find the same issues in twenty minutes but it will miss contextual problems like business logic flaws and race conditions. The guide does acknowledge this gap in the business logic testing chapter but it does not give you a framework for finding those issues. You need your own methodology for that part. I keep a separate checklist for business logic testing that covers things like price manipulation, parameter tampering on transactions, and workflow state confusion. The OWASP guide treats business logic testing as one chapter among fourteen, which makes it feel less important than it actually is. Another limitation is the guide is web-focused. If you are testing mobile apps or APIs that do not have a browser interface, a lot of the testing procedures need adaptation. Chapter 5 on session management testing assumes cookie-based sessions. Many modern REST APIs use JWT or opaque tokens passed in headers. The guide mentions this in passing but does not provide alternative test cases. I had to modify the session fixation and session hijacking procedures from Chapter 5 to work with header-based token transport. The concepts are the same but the test execution is different.
Practical Workflow That Actually Works
Here is what my process looks like now. I start with Chapter 2 for information gathering and run what I can through automated tools while I do manual recon simultaneously. I take notes in a structured template that maps each finding back to a specific test case number from the guide. This makes the handoff to the reporting phase much cleaner. When I hit a testing chapter, I do not read the whole thing first. I scan the test cases, pick the ones relevant to the application's technology stack, and work through those. A PHP application does not need extensive testing against Java-specific injection vectors. Skipping irrelevant chapters saves hours. The reporting chapter in Part Three is worth reading before you start testing. It tells you how to structure your findings, assign risk ratings using both CVSS and contextual severity, and write executive summaries. I used to write findings as narrative paragraphs. The guide recommends a structured format with vulnerability description, proof of concept, impact, and remediation. Switching to that format cut my report writing time from about eight hours down to two hours for a standard engagement. If you want the guide as a downloadable PDF, it is available on the same OWASP page I linked above. The online version updates more frequently than any printed copy, so I usually keep the browser tab open rather than downloading. The guide also has a companion document called the OWASP Top Ten which is separate but related. Do not confuse the two. The Testing Guide tells you how to test. The Top Ten tells you what the most critical vulnerabilities are. They complement each other but serve different purposes.
The Testing Guide V5 is not the final word on web application security testing. New attack vectors appear every year that the guide does not cover. API security testing has evolved significantly since V5 was published and newer OWASP projects like the API Security Top Ten fill some of that gap. But for standard web application assessments, it remains one of the few structured methodologies that is freely available and broadly accepted by the industry. If you are starting out, use it. If you are experienced, reference it when you need to justify your test coverage to a client. It provides the traceability that makes your findings defensible.