Understanding the Actual Costs of PCI DSS Certification
The Pci Dss Certification Exam Cost is not a single flat fee like most people expect. It varies heavily depending on your organization's size, scope, and which level you fall under. Let me walk through what it actually looks like in practice, because the official documentation makes it sound simpler than it is. PCI DSS doesn't actually have a certification exam in the traditional sense. That's the first thing most people get confused about. There's no test you sit for. What exists are two different tracks: the QSA (Qualified Security Assessor) path for external auditors, and the internal certification for organizations getting assessed. The QSA exam through PCI SSC runs around $2,500 to $3,500 per attempt for the three-day training plus the certification exam. That's individual level. For your actual organization's compliance assessment, you're paying a QSA company, and that's where the real cost sits. A Level 1 merchant or service provider assessment typically runs $15,000 to $75,000 depending on complexity. I worked with a mid-sized payment processor last year that got quoted $42,000 for their annual ROC. The quote was based on their transaction volume, number of systems in scope, and the fact that they had three data centers. Smaller merchants at Level 4 might pay as little as $3,000 to $8,000 for a Self Assessment Questionnaire review with a QSA firm.
Then there are the hidden costs that never make it into the initial budget. Remediation. Always remediation. Your first audit will almost certainly find gaps. A friend who runs IT compliance at a regional bank told me their first ROC came back with 23 high-severity findings out of roughly 140 requirements. Fixing those took about four months and another $18,000 in engineering time before they could even book a re-assessment. That's the pattern you're working with.
How the Cost Structure Actually Works
PCI DSS v4.0 changed some things compared to v3.2.1. The new version introduced customised approaches and more granular requirements. Some organizations saw their assessment costs go down slightly because they could justify custom controls instead of needing every single technical requirement met rigidly. Others saw costs go up because the document requirements are heavier and the QSA firms charge by the hour now rather than a flat project fee. This depends entirely on your assessor. Here's a practical breakdown of what drives the number: Transaction volume and Level classification: Level 1 is over 6 million Visa transactions annually, or any organization that processes card-not-present at scale. Level 4 is under 2 million. The difference isn't just volume though - it's also about whether you're a service provider. Service providers get assessed more frequently and more deeply because one failure exposes many merchants.
Get the Full Details
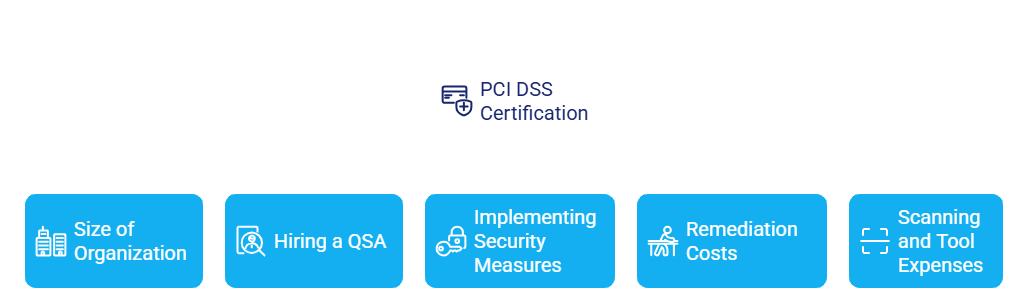
Scope complexity: If you can reduce your scope through proper network segmentation, you save money directly. I helped an e-commerce company segment their web server farm from their internal HR systems about three years ago. Their initial scoping exercise dropped from 47 systems down to 12. That alone cut their annual assessment cost from around $38,000 to roughly $16,000. Segmentation is the single most effective cost control in PCI DSS compliance. Assessor selection: Big four accounting firms charge premium rates. Boutique QSA firms are often 30 to 50 percent cheaper and sometimes more thorough because they actually care about retaining your business. I've seen the same organization get a $60,000 quote from one firm and $28,000 from another for an identical scope. The work product quality was comparable. Frequency: Level 1 requires annual ROC. Levels 2 through 4 may qualify for annual SAQ submission instead. SAQs are significantly cheaper but only if your environment qualifies for them. Some organizations that should be doing SAQs get pushed into full ROC assessments because their QSA firm sees more billable hours that way. That's a conflict of interest worth being aware of.
A Specific Problem I Encountered
During a gap analysis for a healthcare payments processor, we discovered their SSL certificate for the payment portal had expired 11 days before the on-site assessment was scheduled. The QSA had not flagged this in the remote scoping phase, and the client assumed it was covered because the certificate renewal had been automated. Automated certificate renewal broke silently due to a DNS propagation issue that went unnoticed for two weeks. The immediate workaround was to generate an emergency wildcard certificate, rotate it across all endpoints, and document the entire incident timeline for the QSA. The QSA accepted the evidence but added a finding for inadequate monitoring of certificate validity periods. That finding required compensating controls - specifically a daily monitoring script and a secondary alerting mechanism. Total cost of that situation: about $4,000 in emergency engineering time, two weeks of stress, and a formal finding on the ROC that needed to be closed before the report could be issued. A $200 annual certificate plus a basic monitoring tool would have prevented all of it.
Counter-Intuitive Things Nobody Tells You
First, having a prior clean audit does not guarantee a lower cost next year. In fact, some QSAs charge more on subsequent years because they assume you'll have accumulated additional systems and complexity. The only real leverage you have is switching assessors. Changing QSA firms between assessment cycles is common practice and can reset pricing negotiations. I've seen organizations save 20 to 30 percent simply by obtaining competitive quotes every two years. Second, the concept of "out of scope" is often misunderstood. Just because something isn't directly processing cardholder data doesn't mean it's out of scope. If it stores, processes, or transmits CDEs, or if it's in the same VLAN or shares the same root DNS zone, it may fall within scope. A common pitfall is assuming that because a system is in a DMZ or behind a firewall it's exempt. It's not. The PCI DSS scope rules are about data flow, not network topology assumptions. Third, annual compliance is not the same as continuous compliance. Many organizations do their assessment, file the paperwork, and consider themselves done until the next year. This is where most failures happen. Changes to infrastructure happen constantly. A developer spinning up a new server for a marketing campaign can inadvertently put a new system in scope. The assessor's annual report only captures the state at the time of the assessment, not the state during the other eleven months.
What This Approach Doesn't Work For
Trying to self-assess your way through a Level 1 ROC is not viable. The PCI SSC explicitly prohibits this. You must use a Qualified Security Assessor. The SAQ path is genuinely the only self-service option, and it's only available to specific merchant profiles. If you're a small e-commerce site that uses a fully outsourced payment gateway and never touches cardholder data directly, a SAQ A might fit your situation. But if you have any custom integration, any server handling payment data, or any direct connectivity to a payment gateway, you're likely looking at a full assessment regardless of how small your operation is. Also, keeping costs down by skipping remediation on minor findings is a bad idea. Every open finding becomes a negotiation point with your assessor and potentially with your acquiring bank. Banks are increasingly auditing their merchants' compliance status independently. An open finding on your ROC is visible to them, and they can impose fines or higher transaction fees regardless of what your QSA says about risk acceptance. The realistic budget range for a small-to-mid business doing annual compliance should account for the assessment itself, a remediation buffer of at least 25 percent of the assessment cost, and ongoing monitoring tools. For a typical Level 2 or 3 organization, that usually lands between $8,000 and $25,000 per year when done properly. Anything quoted significantly below that range should raise questions about what's actually being covered.