What a PCI DSS Compliance Assessment Actually Looks Like
Most people treat a PCI DSS Compliance Assessment as a checkbox exercise. It isn't. It is a forensic review of how cardholder data moves through your environment, who touches it, and what controls exist at every single hop. The standard itself has grown over the years, but the core problem hasn't changed: assessors need proof that your environment meets the requirements, not promises. I spent several years doing these assessments inside and outside organizations, and the pattern is always the same. Companies that prepare properly treat it like an infrastructure audit. Companies that wing it end up spending weeks scrambling for evidence that should have existed from day one.
Understanding a Pci Dss Compliance Assessment
A Pci Dss Compliance Assessment is the formal evaluation process where an organization demonstrates adherence to the Payment Card Industry Data Security Standard. This typically involves a QSA (Qualified Security Assessor) or an internal RO-QSA depending on your merchant level. The assessor reviews documentation, interviews staff, tests controls, and produces a Report on Compliance (ROC) for Level 1 merchants or a Self-Assessment Questionnaire (SAQ) for smaller merchants. The assessment covers twelve requirement areas grouped into six objectives: building and maintaining a secure network, protecting cardholder data, managing vulnerabilities, implementing strong access controls, regular monitoring and testing, and maintaining an information security policy. But reading those twelve requirements won't help you when the assessor asks you to produce logs from three years ago showing who accessed a database containing PANs.
The Step-by-Step Process
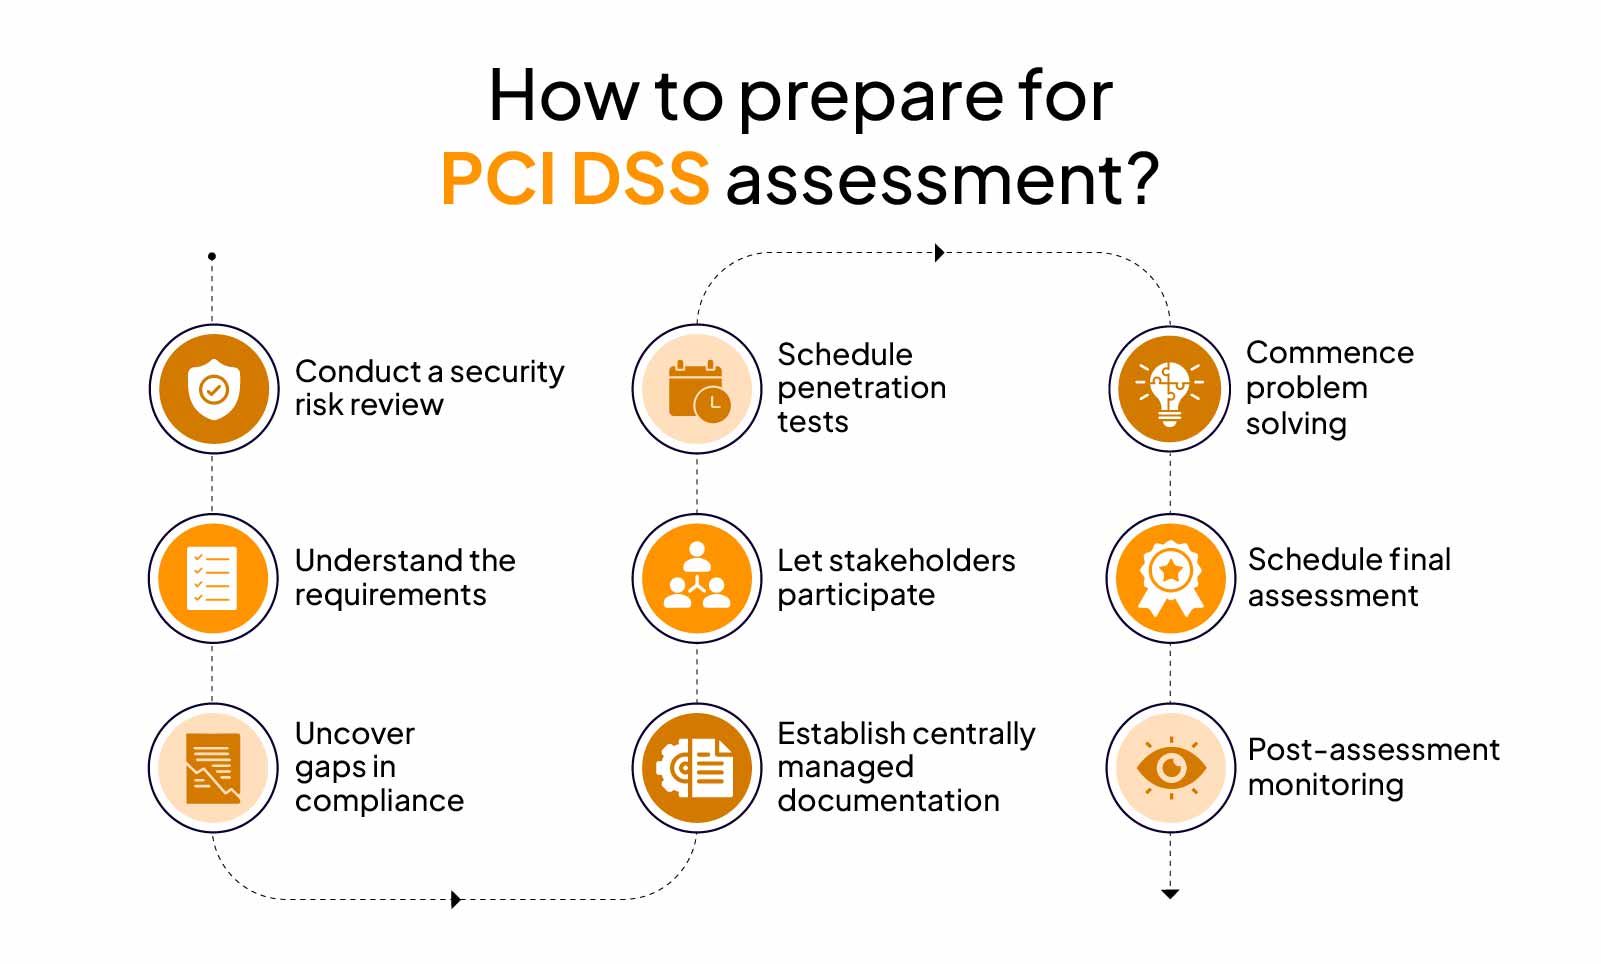
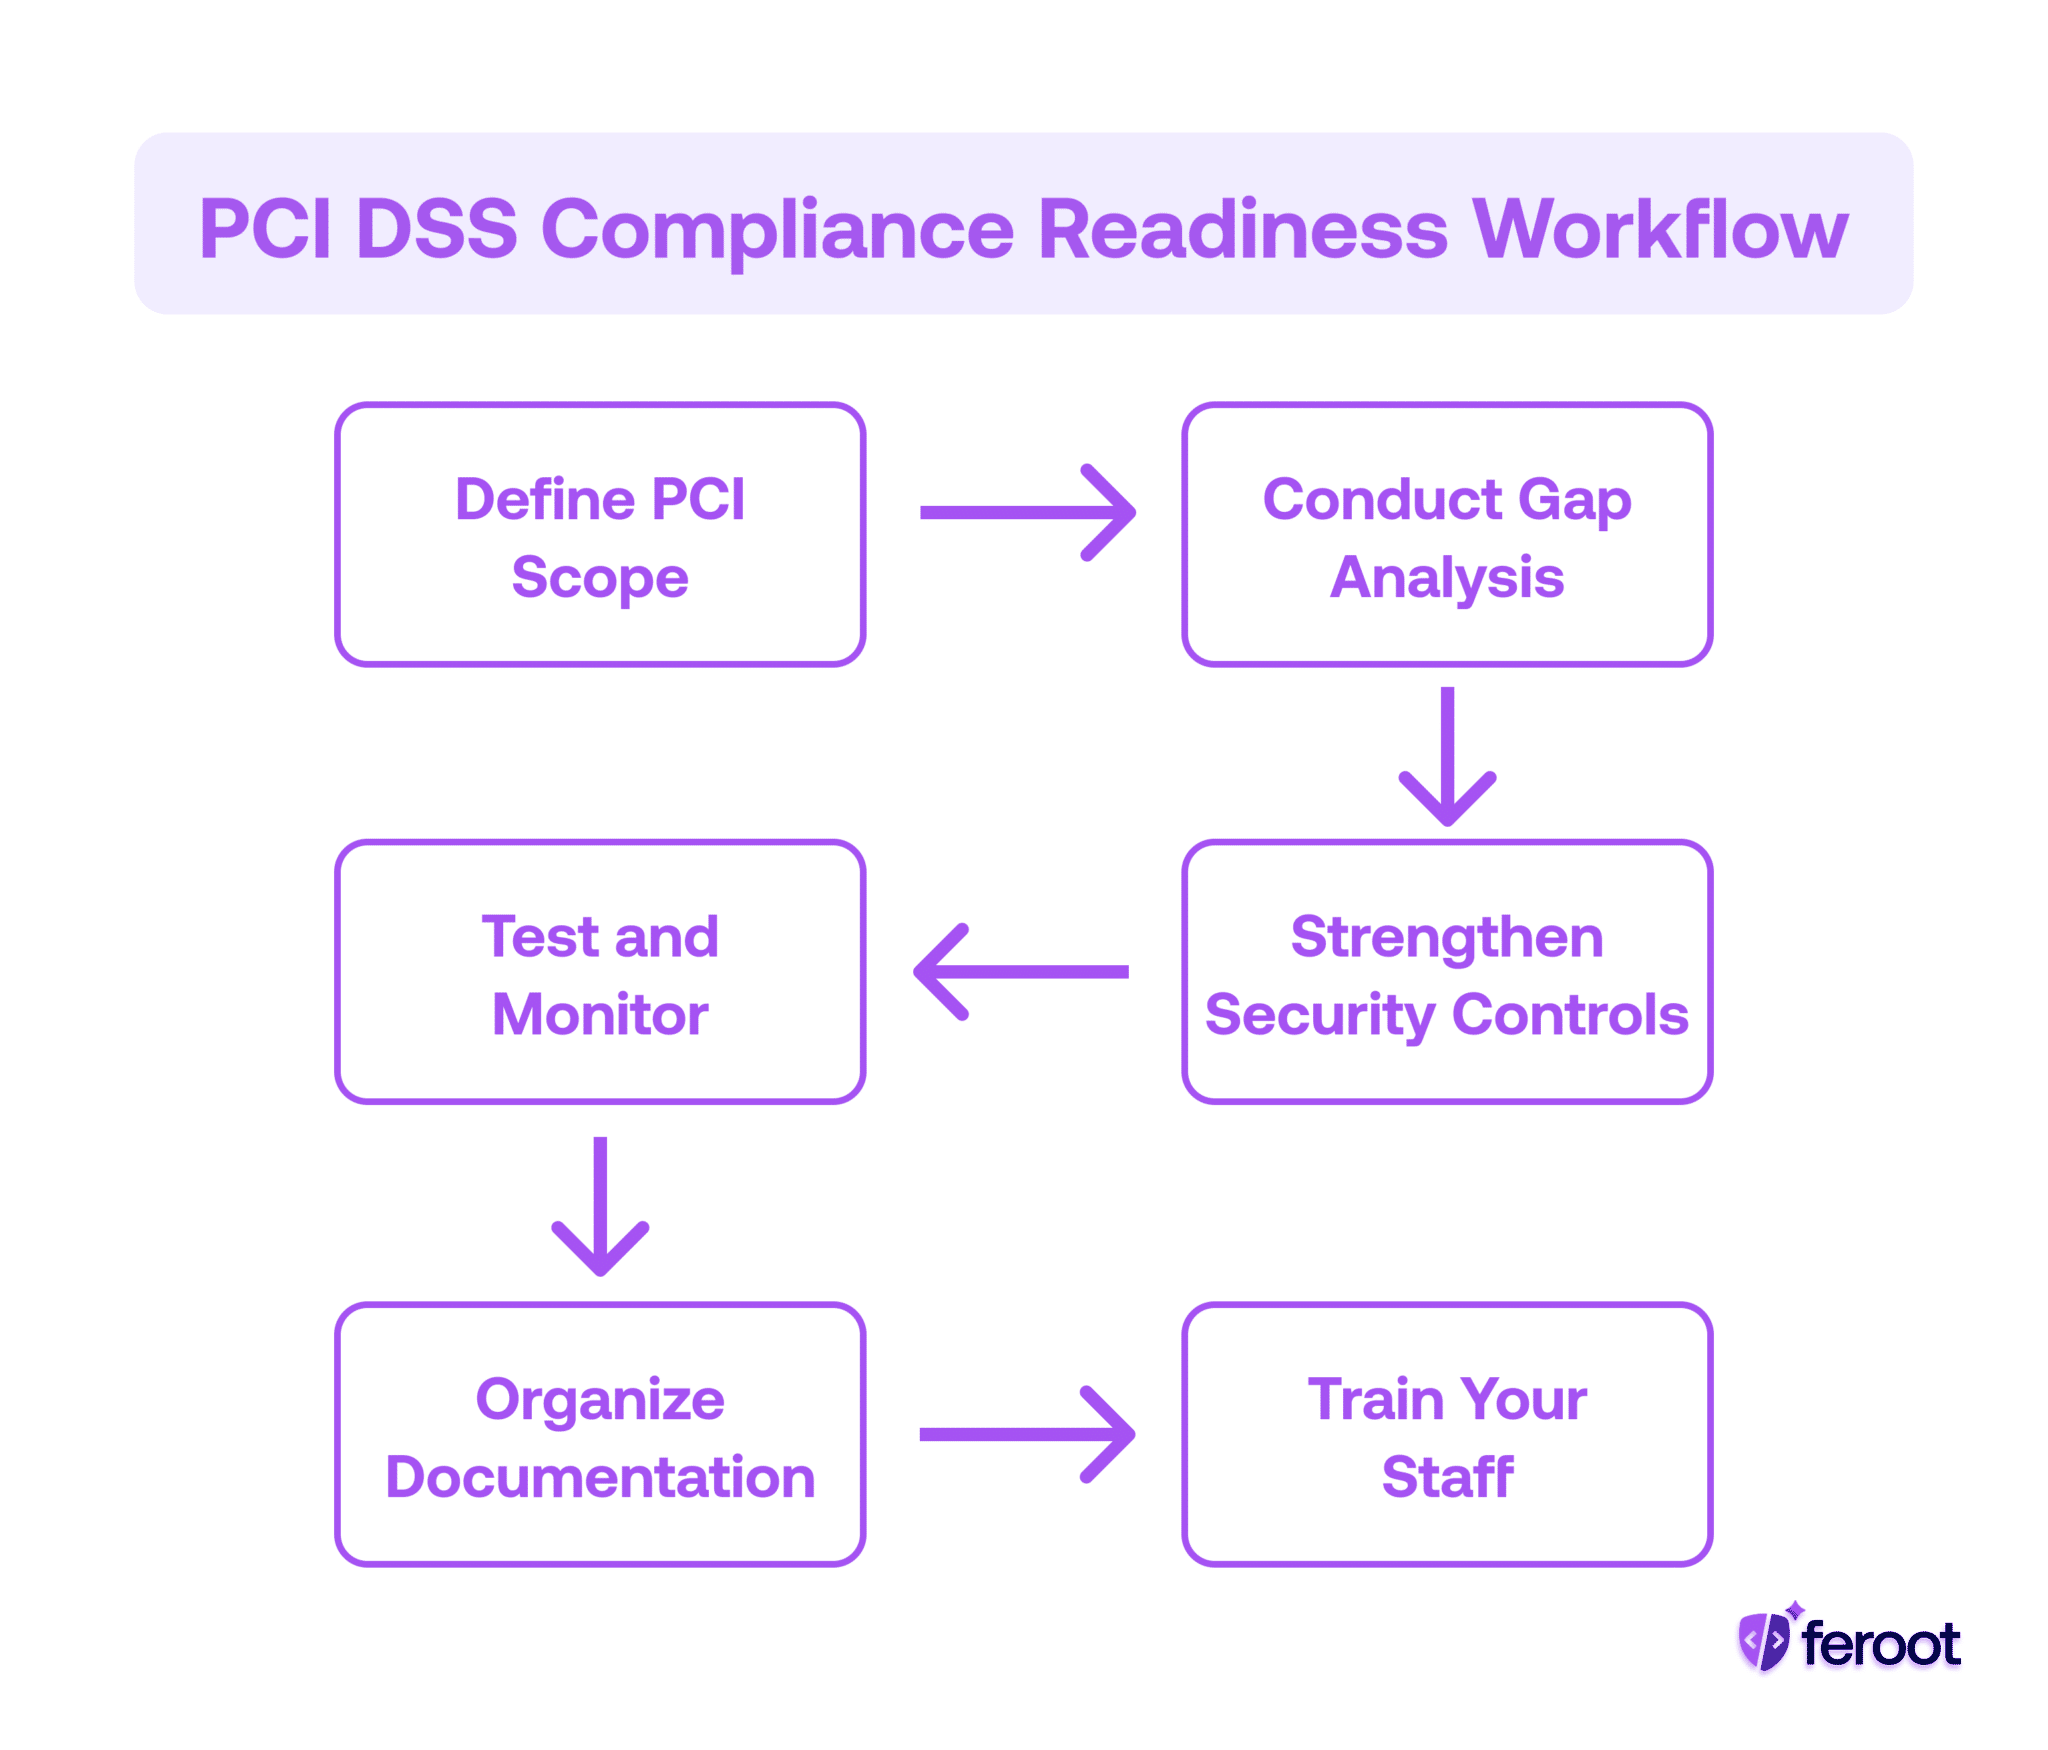
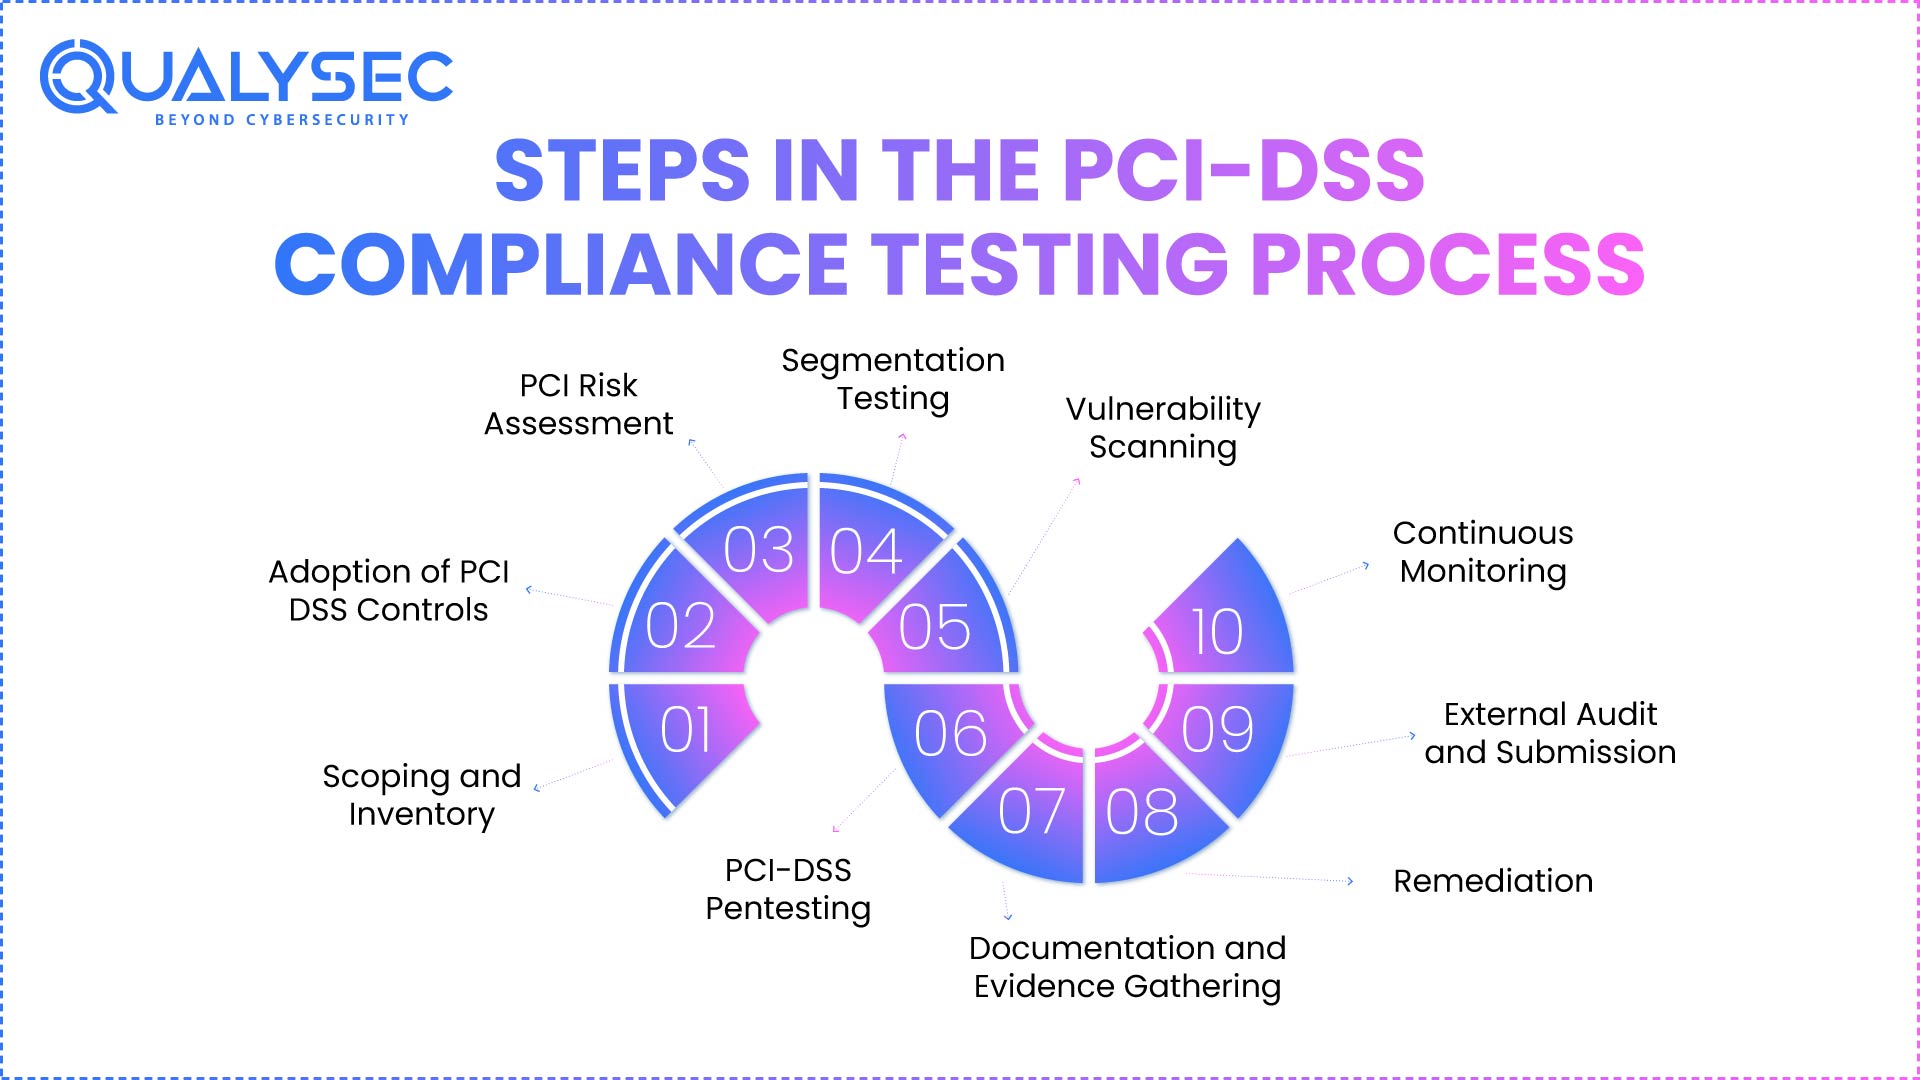
Here is how the actual work breaks down, not the textbook version. This is where most assessments succeed or fail before anything else happens. You need to clearly identify every system, person, and process that stores, processes, or transmits cardholder data or sensitive authentication data. The moment you find an undocumented system in scope, your timeline evaporates. I worked with a mid-size retailer once who had segmented their payment environment using a firewall rule they believed was sufficient. When the assessor traced the traffic paths, they found a legacy VPN connection that bypassed the segmentation entirely. That VPN connected a contractor's laptop directly into the cardholder data environment. Fixing it took three days of change management, but the real cost was the two-week delay in the assessment timeline while they validated the segmentation was actually effective. I learned to ask about every remote access point, VPN, and out-of-band management path on day one instead of day fourteen.
Get the Full Details
Proper scope definition includes mapping the CDE (Cardholder Data Environment) boundary with diagrams showing all data flows, not just the obvious ones. Document every system interface. If a third-party vendor touches cardholder data, that data flow needs to appear in your diagrams too.
2. Document gathering
Before the assessor arrives, you need policies, procedures, and technical evidence ready. The key documents include your Information Security Policy, Access Control Policy, Incident Response Plan, Change Management Policy, and the Risk Assessment. On the technical side, you need current network diagrams, system inventory, vulnerability scan reports, penetration test results, and log retention configurations. The documents that cause the most friction are the ones people create after the assessment starts. A dated policy that references outdated technology signals to an assessor that your security program is reactive rather than proactive. If your current policies don't match reality, fix them before the assessment begins. It is cheaper to spend a week updating documentation than to spend six weeks during the assessment trying to retroactively justify gaps.
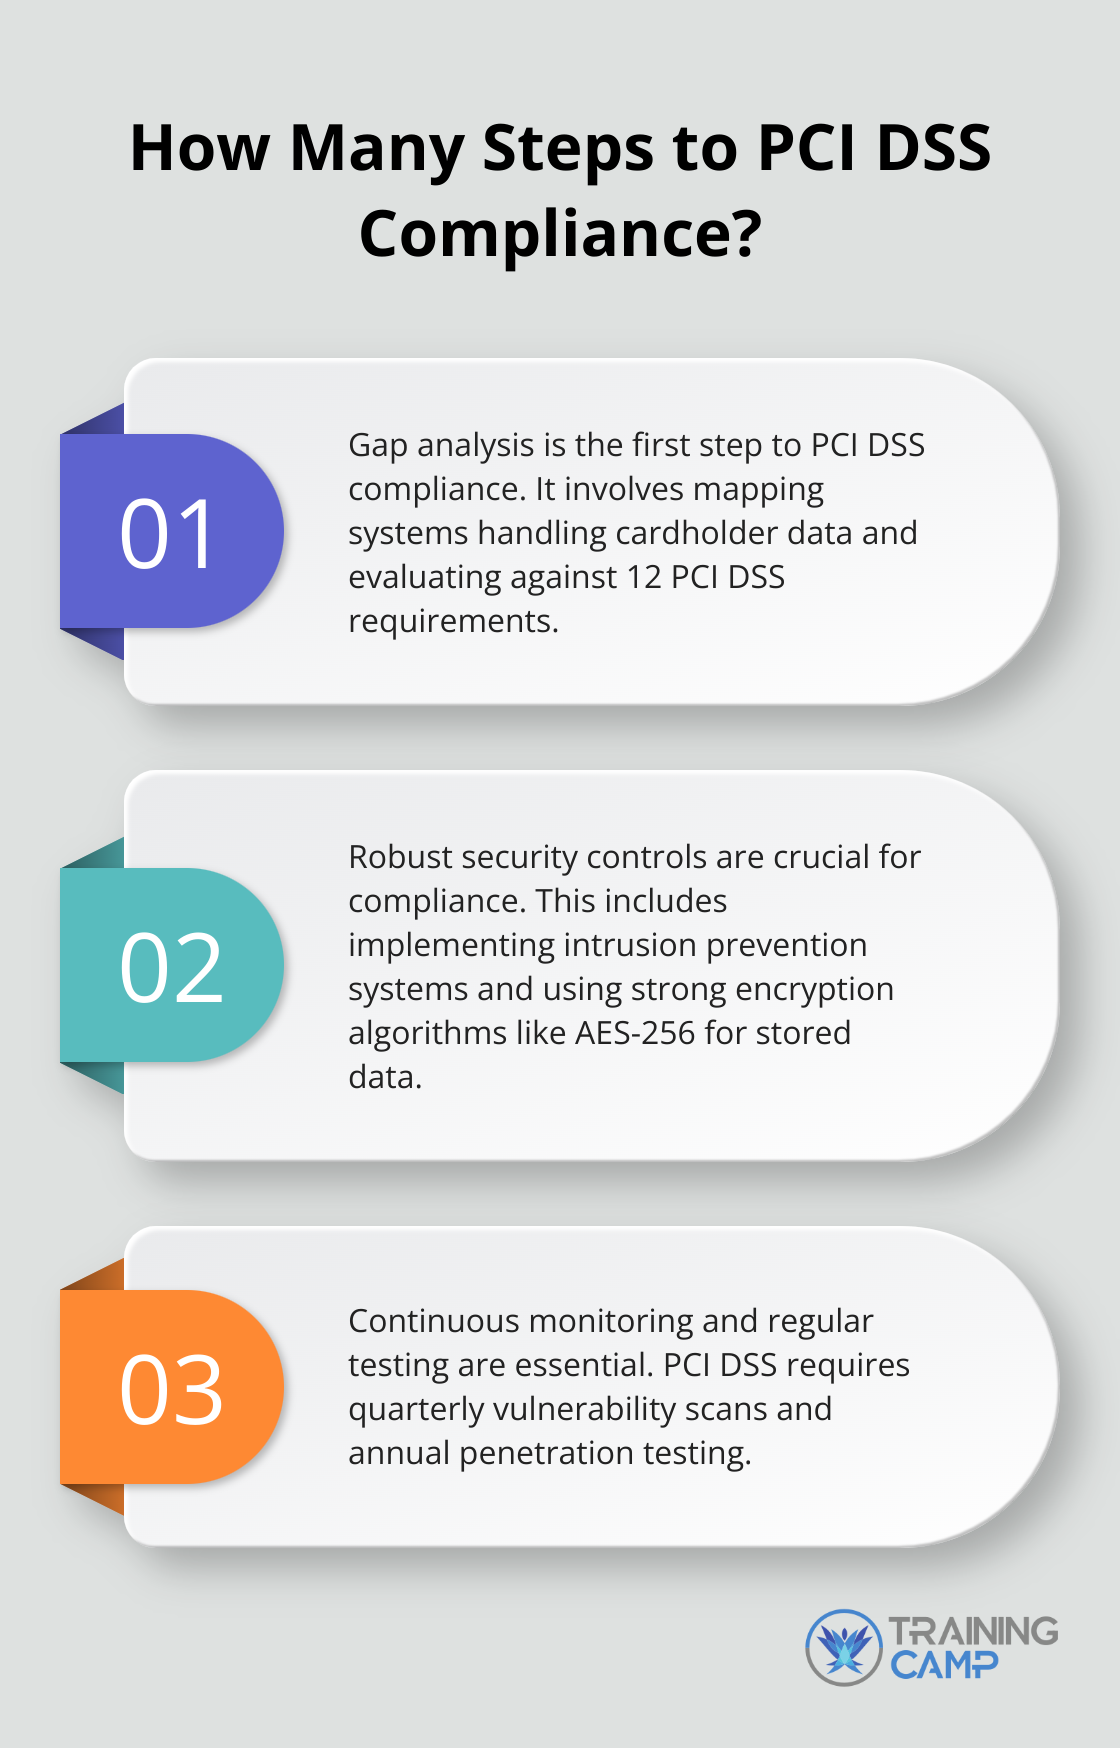
3. Gap analysis
Run through each of the twelve requirements and mark where you comply, partially comply, or don't comply at all. This is different from the official SAQ because you are being honest with yourself, not filling out a form for a bank. Partial compliance counts as non-compliance, so don't gloss over it. A useful trick here is mapping controls to the specific requirements they address. Some controls cover multiple requirements. For example, a robust SIEM that monitors access to cardholder data systems might satisfy elements of requirements 10 and 11. Identifying these overlaps helps you prioritize remediation work and communicate efficiency to the assessor.
4. Remediation
Every gap identified in your assessment needs a remediation plan with an owner and a deadline. The requirements themselves provide guidance on what controls to implement, but the timeline depends entirely on your infrastructure complexity. Encryption of stored cardholder data alone can take anywhere from two days to eight weeks depending on how many systems are involved and whether your applications were designed with encryption in mind. The hard part of remediation is often not the technical work but getting the right people to do it. Security teams don't control the servers. Infrastructure teams don't own the compliance calendar. I've seen assessment timelines slip because the database administrator responsible for encrypting stored PANs was on vacation for three weeks. Build buffer time into your remediation schedule. Not because you're sloppy, but because real organizations have real vacations.
5. Testing and validation
Once remediation is complete, you need to validate that controls work as intended. This involves internal testing before the assessor arrives. Vulnerability scans must be performed by an Approved Scanning Vendor (ASV) for external-facing systems. Internal network scans should be run quarterly. Penetration testing needs to happen at least annually and after any significant infrastructure changes. The ASV scan is a common stumbling block. These scans are relatively shallow but they are mandatory, and failing them blocks your entire assessment. The most frequent failures are outdated web server software, missing security patches, and open ports that shouldn't be open. Keep these patched and monitored continuously rather than treating the ASV scan as an annual event. This usually cuts the process down from a frantic two-week panic to a routine weekly check that takes about fifteen minutes.
6. The formal assessment
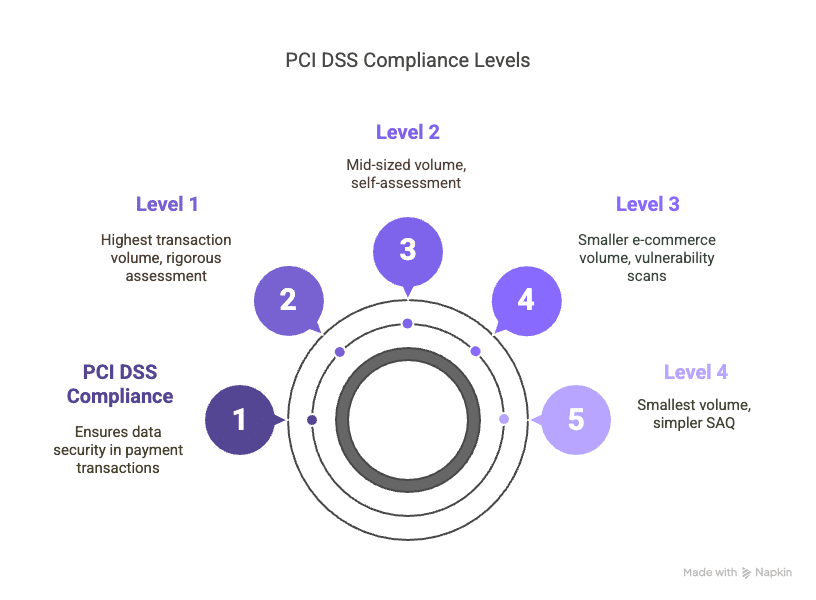
The formal assessment phase varies by merchant level. Level 1 merchants require an on-site assessment by a QSA who produces a full ROC. Levels 2 through 4 may complete an SAQ, though some issuing banks require a ROC anyway regardless of the official tier. During the assessment, the QSA will interview staff, review documentation, perform walk-throughs of processes, and test technical controls. They may also conduct their own vulnerability scans and penetration tests. Be prepared to produce evidence on demand. If the assessor asks for logs from a specific date range and it takes you two hours to locate them, that is a problem worth fixing for next time. Automate log retrieval where possible.
Common Pitfalls That Derail Assessments
Outdated network diagrams. This is the number one issue I see. Your infrastructure changed six months ago but your diagrams still show the old architecture. Assessors trust their own recon more than your documentation, and contradictions between the two raise red flags about your overall control environment. Inconsistent access controls. Granting administrative privileges to contractors or temporary staff without proper justification and documentation violates multiple requirements. I once found a contractor with root access to a payment processing server who had been with the company for eleven months and still didn't have a formal access request on file. That is an easy failing if you're not prepared. Weak password policies. Requirement 8 is straightforward, but implementation is where organizations trip up. Password complexity requirements, expiration policies, and lockout mechanisms all need to meet the standard's specifications. More importantly, you need to enforce them consistently across all systems, including legacy ones that may not support modern password requirements. Those legacy systems need compensating controls documented and approved, or they become liability points during the assessment.
Insufficient log retention. The standard requires log retention of at least one year with three months immediately available for analysis. If your log management solution retains logs for only ninety days, you're non-compliant. This is a configuration issue that takes minutes to fix but gets overlooked because nobody thinks about it until the assessment starts.
Advanced Nuances Most Guides Miss
Compensating controls are legitimate but heavily scrutinized. If you cannot meet a requirement due to technological limitations, you can implement a compensating control that meets the intent of the requirement. However, the documentation burden is significant. You need to describe the limitation, explain why the compensating control satisfies the requirement's intent, and demonstrate that the control is effective. QSAs are trained to be skeptical of compensating controls because they have seen too many poorly justified examples. If you plan to use them, document rigorously from the start and involve your QSA early in the process rather than surprising them during the formal assessment. Third-party service providers change the entire landscape. If you use a payment processor or managed security provider, they handle certain compliance obligations for you. But you remain responsible for ensuring they actually fulfill those obligations. Get your SOC 2 Type II report or PCI Attestment of Compliance from your vendors. Review it annually. If a vendor cannot produce current compliance documentation, that is your problem, not theirs, in the eyes of the assessor. Cloud environments add complexity that the standard doesn't fully address. The PCI DSS v4.0 guidelines for cloud environments are still evolving, and different cloud providers interpret their shared responsibility models differently. A service like Amazon RDS might handle encryption at rest for you, but you still need to manage encryption in transit and key management. Document exactly which responsibilities fall to you versus your cloud provider for every system in scope.
When the Standard Doesn't Apply
There are legitimate scenarios where full PCI DSS compliance may not be feasible or necessary. If you only capture PAN visually through manual entry and never store, process, or transmit it electronically, your scope may be limited to the most basic SAQ. Some organizations qualify for SAQ A or SAQ A-EP if all cardholder data processing is fully outsourced to a compliant third party. Understanding which SAQ fits your environment is critical because submitting the wrong one is a compliance failure in itself. Another edge case is tokenization. If you replace cardholder data with tokens before it enters your environment, the tokenized data is generally outside the scope of PCI DSS. However, the tokenization service itself must be compliant, and you need to understand the relationship between tokens and original PANs. I worked on an assessment where a company assumed their tokenization approach removed everything from scope, but the mapping database that linked tokens to PANs was left in their environment unencrypted and unmonitored. That database was squarely in scope, and the gap almost caused a reportable breach.
Practical Recommendations
Start early. A thorough PCI DSS Compliance Assessment takes most organizations three to six months from start to finish. Smaller environments with mature security programs might complete it in six to eight weeks. If you are starting from scratch, budget six months minimum. Invest in continuous compliance tools. Manual compliance checking is error-prone and doesn't scale. Tools that automate evidence collection, policy validation, and continuous monitoring reduce the assessment burden dramatically. The upfront cost is real, but the time savings during the actual assessment period are substantial. Build relationships with your QSA early. The QSA is not your adversary, but the dynamic can feel adversarial if you approach it that way. Share your gap analysis findings before the formal assessment begins. Ask questions about unclear requirements. A collaborative relationship makes the entire process smoother and often surfaces issues that would otherwise go unnoticed until it was too late.
Train your staff. Compliance is not just a security team problem. Developers need to understand secure coding practices related to payment systems. Help desk staff need to know how to handle calls about cardholder data. Executive leadership needs to understand their accountability. I've seen assessments derailed because a developer deployed code with hardcoded encryption keys because nobody in the organization had explained why that was a problem. The assessment itself is the easy part. The hard part is maintaining compliance year-round. Set up quarterly reviews of your control environment. Reassess scope whenever infrastructure changes. Keep your documentation current. The organizations that treat PCI DSS as an annual checkpoint rather than an ongoing program are the ones that end up stressed, behind schedule, and non-compliant when it matters most.