Setting Up a Pci Listed P2pe Solution Without Losing Your Mind
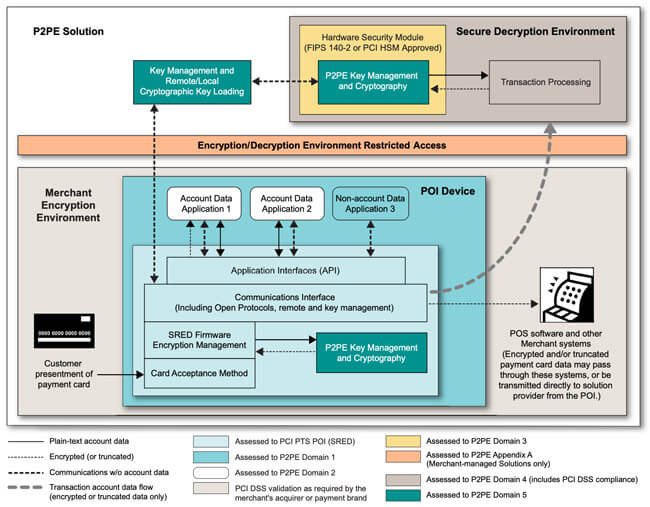
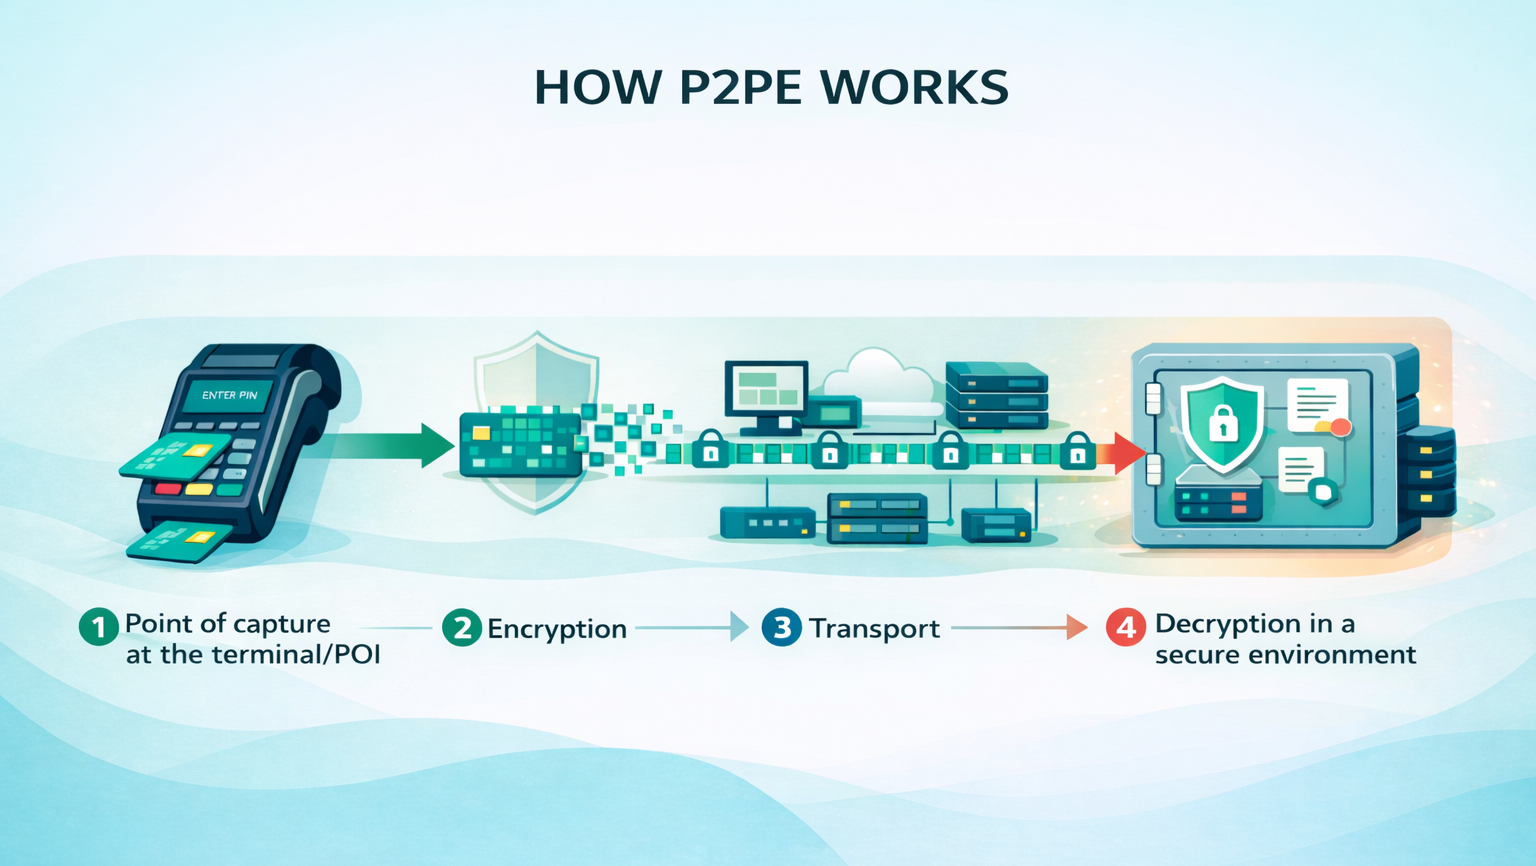
P2PE stands for Point-to-Point Encryption, and it is the process of encrypting cardholder data at the payment terminal so it stays encrypted all the way through your infrastructure until it reaches the decryption device. When a vendor calls their offering a "PCI Listed P2PE Solution," what they mean is the product has been validated by the PCI Security Standards Council and appears on their official list. That list matters because having one of these solutions can get you out of needing a full SAQ C or SAQ TRX questionnaire — you only have to complete a shorter P2PE-specific attestation instead. The first thing you need to do is go to the PCI SSC website and pull the current list of validated P2PE solutions. It gets updated periodically, and vendors will sometimes reference an older validation that has since lapsed. I learned this the hard way in 2023 when a provider I was evaluating had lost their listing during a recertification gap, and we had already begun configuration work. They reassured me it would be renewed within weeks. It wasn't. We ended up pulling the plug on that vendor and starting over with a different one. That cost us roughly three weeks of delays and a lot of unnecessary configuration work on hardware that turned out to be useless for our audit. When you are comparing options, pay attention to whether the solution supports both PIN and non-PIN transactions. Some listed solutions only handle cardholder data encryption and do not encrypt the PIN block. If your environment processes any debit or ATMs, and the P2PE box does not cover PIN encryption, you are still exposed on that front and you will need additional controls. This is one of those details that almost nobody mentions upfront.
Another detail that people gloss over is whether the solution supports your specific terminal models. The PCI SSC validation is tied to particular hardware combinations. A vendor might tell you their solution works with "most major terminals," but then you find out their validated list only covers two out of the five terminal SKUs you actually use in production. I ran into this with a mid-sized retail chain that had rolled out new terminals across thirty locations and then discovered the P2PE solution they purchased only supported the legacy model. They had to either retire the new terminals or switch P2PE vendors mid-deployment. Both options were expensive.
The Actual Deployment Process
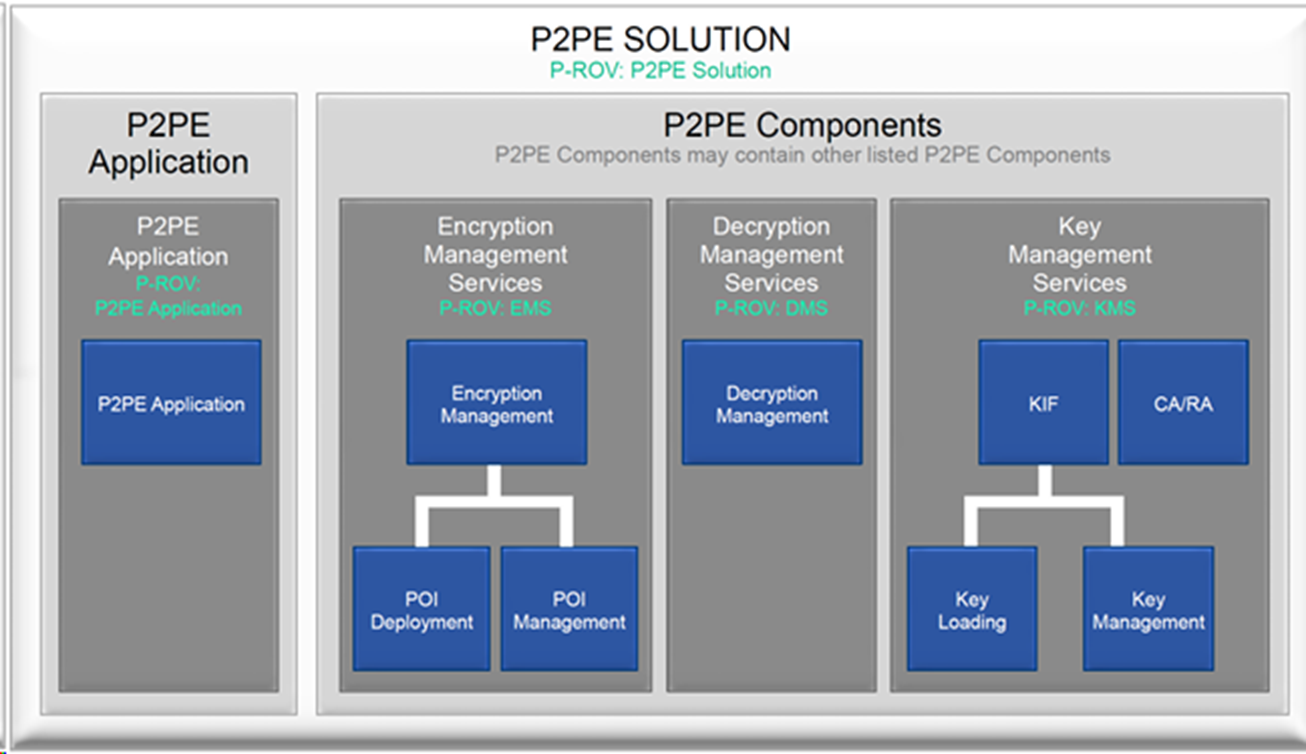
Deployment typically involves several stages, and the complexity depends entirely on your environment size and how many terminals you are managing. Here is how it generally goes. You start by provisioning the P2PE box or appliance at your facility or with your managed service provider. The device needs to be placed in a secure network segment with controlled access. You then configure the cryptographic keys through the key management system that comes with the solution. Most vendors provide their own key management infrastructure, and some let you integrate with your existing HSM if you have one. The key injection process is where things usually slow down because it requires coordination between your team, the vendor, and sometimes your acquiring bank. Next, you install and configure the encryption modules on each terminal. This is not always a software update. Some terminals require a firmware flash, and others need a hardware token installed. The process varies significantly between terminal manufacturers. Verifone and Ingenico tend to have more documented procedures, while lesser-known brands can leave you guessing about compatibility. I spent an entire day troubleshooting a batch of Pax A920 terminals that kept rejecting the P2PE configuration because the firmware version was one build behind what the key management system expected. The vendor's documentation said it was compatible. It was not, not at that exact firmware level.
Get the Full Details

After the terminals are configured, you establish the secure communication path between the terminals and the P2PE decryption device. This is usually handled through a dedicated VPN or TLS tunnel with certificate-based mutual authentication. The validation requires that this tunnel is isolated from your general business network. You cannot route P2PE traffic through a shared VLAN or a multipurpose firewall rule. It needs its own path, and your QSA will verify this during the assessment. Once everything is connected, you run test transactions. Each one should produce an encrypted token that your payment processor can decrypt on their end. You verify that the encrypted data never appears in plaintext anywhere in your environment. I always recommend capturing a few test transaction logs and reviewing them manually before declaring the deployment complete. Automated reports from the P2PE vendor can sometimes show success based on the tunnel being established, but that does not guarantee the encryption is actually working end-to-end for every transaction type you support.
Common Pitfalls That Will Cost You Time and Money
The most frequent problem I see is organizations assuming that P2PE eliminates all PCI compliance requirements. It does not. You still have to assess the network segments that handle the encrypted data after decryption. You still need to maintain physical security controls around the decryption device. You still have to track and manage cryptographic keys according to PCI KS requirements. A P2PE solution removes the scope of cardholder data from your environment, but it does not remove your compliance obligations entirely. Some teams treat it as a set-and-forget checkbox, which is a mistake. Another issue is the assumption that a single P2PE solution covers your entire payment flow. If you have multiple payment processors, multiple acquirers, or you accept payments through different channels like email invoices or gateway submissions, those other channels are not covered by the terminal-level encryption. P2PE only protects the data between the terminal and the decryption device. If you also take card-not-present transactions or allow manual key entry in certain scenarios, those flows remain in scope and will need separate controls. Vendors sometimes sell P2PE as a cloud-hosted service, which sounds convenient until you realize that the PCI SSC has specific requirements about where the decryption device can reside. In some configurations, cloud-hosted P2PE is acceptable, but you need to verify that the decryption endpoint meets the physical and logical security requirements outlined in the P2PE v3.x specification. I encountered a case where a hospital group attempted to use a cloud P2PE provider for their patient billing terminals, and their QSA rejected the configuration because the cloud provider could not demonstrate the required isolation between the decryption environment and other tenants. They had to move to an on-premises decryption device, which required facility upgrades they had not budgeted for.
What the Validation Actually Saves You
For most small to medium businesses, a properly implemented PCI Listed P2PE Solution reduces the annual PCI DSS assessment from a full SAQ C or a Level 1 QSA audit down to a P2PE self-assessment with a validating QSA review. That typically cuts the assessment timeline from several weeks to roughly two to three days of actual auditor time, depending on how organized your documentation is. The cost savings are real, but they come with the ongoing responsibility of maintaining the validation. If you modify your terminal firmware, change network topology, or swap out any component of the P2PE architecture without updating your validation scope, you can lose your compliant status without realizing it. The key takeaway is that a P2PE solution is not a compliance shortcut. It is a scope-reduction tool that works well when you understand exactly what it covers and what it does not. Pick a currently validated solution, verify terminal compatibility before you buy, plan for the key management overhead, and make sure your QSA agrees with your implementation before you submit your attestation. Everything else is just details.