Home Network Risk Analysis
I used to skip risk analysis for home networks. Then a friend of mine set up an IoT camera on his guest VLAN and left it with the default password. Someone hit it with a dictionary attack within three days. Not because they targeted him specifically, but because there are bots scanning every exposed port on the internet constantly. That incident made me take this seriously. Risk analysis in this context is systematically identifying what assets you have, what could go wrong with them, and how likely and damaging those scenarios are. Most people gloss over this because they think of it as enterprise work. It isn't. You do it with a spreadsheet and some free tools. The framework is straightforward: list your devices, rate their exposure, evaluate the threat likelihood, assess the impact if compromised, and then prioritize what to fix first. The standard formula is Risk = Likelihood x Impact. Most online calculators won't help you here because home networks don't fit neatly into corporate risk matrices. You build your own.
The Practical Steps
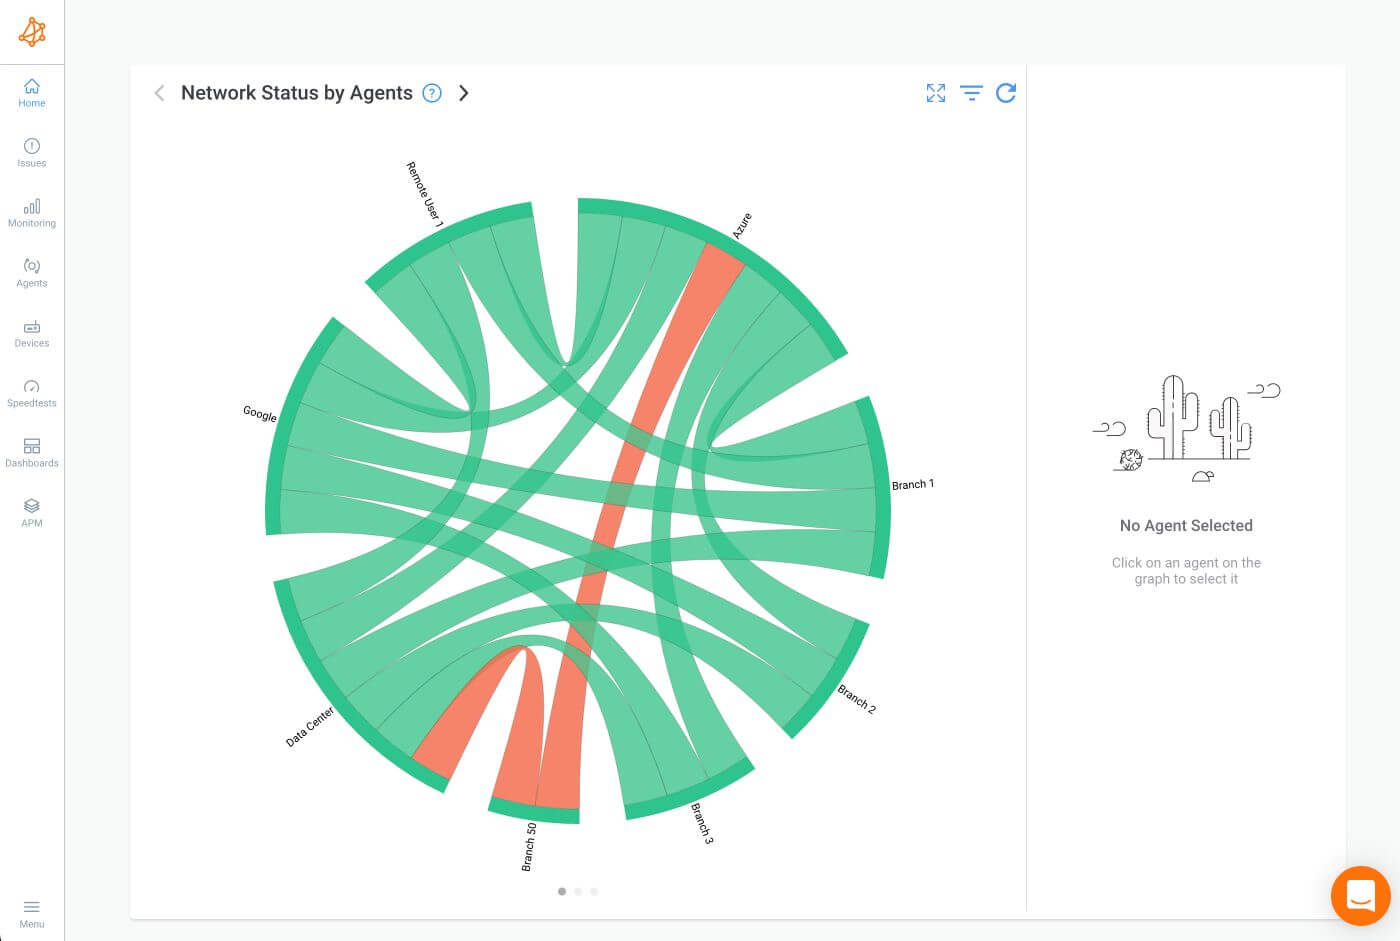
Start by inventorying everything connected to your network. I use a combination of my router's connected devices list and a tool called Advanced IP Scanner. It takes about twenty minutes. Write down the device name, IP address, MAC address, what it does, and where it sits on your network. A gaming console on the main LAN is a different risk than a smart thermostat on a separate VLAN. Next, map your network topology. Draw it out. I keep a simple diagram in a text file that I update whenever something changes. This matters more than you'd think. When I was helping a client investigate a breach last year, the first thing we did was pull their network diagram. They didn't have one. It took four hours to figure out how the attacker moved laterally because everything was on a flat subnet with no segmentation. Identify your threats. For a home network, the realistic threats are: credential brute-forcing on exposed services, compromised IoT devices being recruited into botnets, ransomware spreading across unsegmented systems, and ISP-level interception or DNS hijacking. Advanced threats like nation-state surveillance probably aren't worth worrying about unless you're specifically targeted.
Rate the likelihood of each threat on a scale of 1 to 5. One is virtually impossible. Five happens regularly. A default-password camera on the internet gets hit with brute-force attempts frequently, so that's a four or five. Your desktop PC behind a NAT firewall with a strong password getting randomly compromised is probably a two. Rate the impact also from 1 to 5. Impact means what happens if the threat actually materializes. If your NAS with your family photos and tax documents gets encrypted by ransomware, that's a five. If your smart fridge gets part of a DDoS botnet, that's maybe a two, though it's annoying. Multiply likelihood by impact. The resulting number tells you where to focus. A score of 15 or higher needs immediate attention. Scores between 8 and 14 should be addressed within the month. Below 8 is lower priority but still worth documenting.
Get the Full Details

A Common Mistake People Make
Most people stop after the likelihood and impact ratings. They don't account for existing controls. That inflates their risk scores and makes the analysis useless for prioritization. A device might have a high baseline risk, but if you've already put it on a guest VLAN with no internet access and isolated it from the main LAN, its actual risk drops dramatically. When I do this analysis for clients, I always add a column for existing controls and rate how effective each one is. Firewall enabled? Rate it 3 out of 5. Strong password? Rate it 4 out of 5. Device firmware updated? Rate it 4 out of 5. Then you recalculate the adjusted risk by factoring in those controls. This usually changes the priority list significantly.
Tools I Actually Use
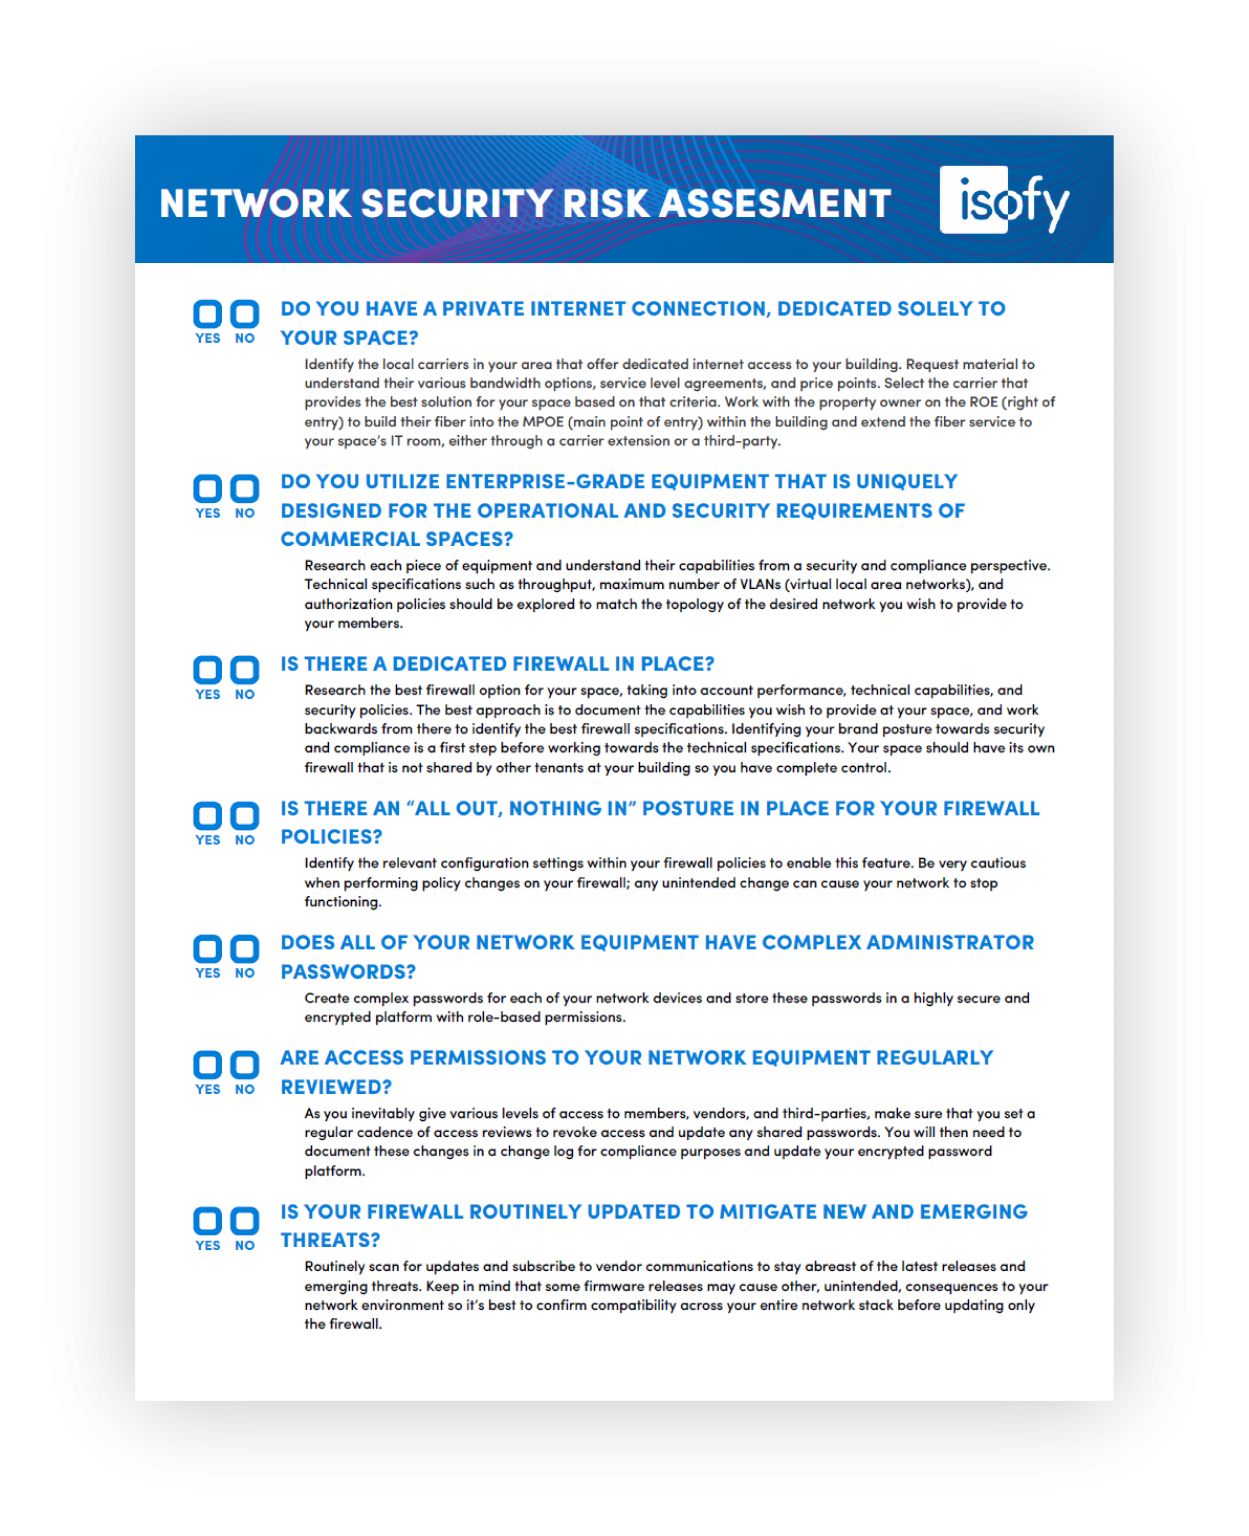
For vulnerability scanning, I use Nmap. It's free and runs on Linux, Windows, and macOS. A basic command like nmap -sV -p- 192.168.1.0/24 will scan your entire subnet for open ports and running services. It reveals things your router's device list won't show you. I found an old Windows media server that thought it was air-gapped but was actually exposing SMB on the main LAN. Had a default admin account and no firewall rule blocking it. For DNS security, I run dnsvalidator from SpecterOps against my domain's DNS records. It checks for SPF, DKIM, DMARC misconfigurations, and other DNS-level issues. If you run a home lab with a public-facing domain, this is essential. Misconfigured DNS records can let anyone intercept your email or spoof your domain. I also keep a copy of Potamian's Home Network Security Checklist bookmarked. It's not a tool, but it's the most comprehensive reference I've found for home network hardening. I reference it every time I do a full review, which is roughly every six months for my own network and quarterly for client networks.
The Edge Case That Tripped Me Up
I once had a client whose router firmware reported that all devices were on the same subnet, but the risk analysis showed unusual lateral movement paths. The router was an older Asus model running custom firmware, and it had a feature called "AP Isolation" that was supposed to block device-to-device communication on the guest network. But the firmware had a bug where AP Isolation didn't apply to devices connected via Ethernet to the guest VLAN. A compromised IP camera on the guest network could reach any wired device on that same VLAN, which included their work laptop. The workaround was to move all wired devices to the main VLAN and keep wireless devices on the guest VLAN exclusively. Then I added a firewall rule blocking all traffic from the guest VLAN to the main VLAN at the router level. That eliminated the gap. It's the kind of thing that doesn't show up in any documentation. You only find it when you actually map out every connection path and check the firmware release notes for known issues.
What This Approach Doesn't Cover
Risk analysis is only as good as your inventory. If you don't know a device exists on your network, you can't analyze its risk. Rogue devices are a real problem. I've found unknown mesh WiFi extenders, old routers being used as switches, and smart plugs that were never removed from the network after a renovation. Schedule your analysis for a time when everyone is home and can confirm their devices. Another limitation is that risk analysis gives you a snapshot in time. Your risk profile changes when you add new devices, change your network configuration, or when new vulnerabilities are disclosed for software you're running. I treat this as a recurring process, not a one-time exercise. Six months between reviews is reasonable for most home networks. If you have a more complex setup with public-facing servers, VPN gateways, or cloud-hosted services, this spreadsheet approach breaks down. You'd need something like OWASP ZAP for web application testing or a proper penetration test. But for the vast majority of home networks, the method I described covers the real risks without requiring a security degree.