Understanding Point Care Click Log In
Point Care Click Log In refers to the authentication mechanism used by Point Care systems, which are digital platforms commonly found in clinical and healthcare settings. The "Click Log In" portion is simply the user-facing button or link that initiates the session. Behind the scenes, these systems typically route through single sign-on (SSO) providers, LDAP directories, or internal credential stores. The exact architecture depends on whether you're dealing with a hospital-issued instance, a private practice setup, or a third-party hosted version. I've worked with several Point Care deployments across different facilities. One thing most people don't realize is that the login page you see is often just a frontend wrapper. The actual authentication handshake happens against backend services that may sit on completely separate network segments. This means latency, cookie issues, and session timeouts are rarely problems with the login page itself — they're usually problems with how your network path intersects with the identity provider.
Point Care Click Log In — Step by Step Access Guide
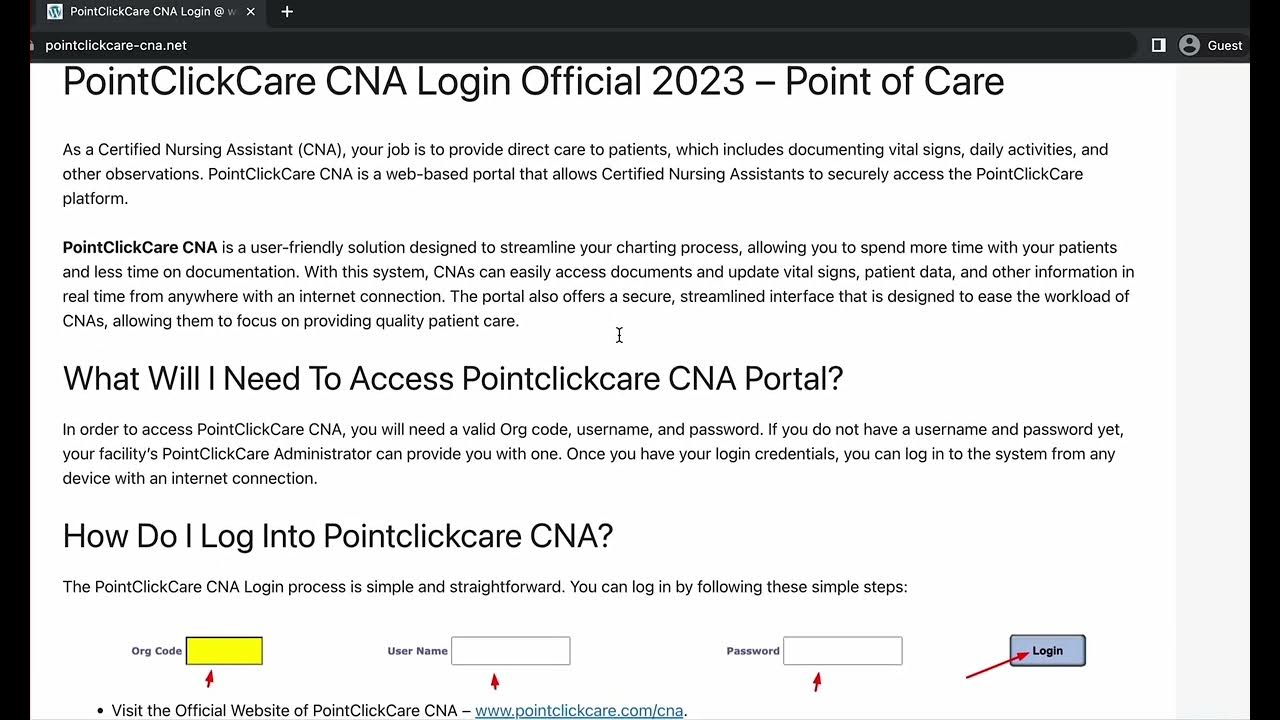
Here's how the process generally works in practice. You navigate to the institution-specific URL, which is almost never a generic domain. It typically looks something like portal.pointcare.[organization].com or uses a custom hostname provided by your IT department. From there, you enter your credentials. Some installations require two-factor authentication via a mobile app or hardware token. Others rely on certificate-based authentication if you're accessing from a managed device. After you submit the form, the system validates your credentials and creates a session token. This token is then stored as either a session cookie or a persistent cookie depending on your institution's configuration. Session cookies expire when you close the browser. Persistent cookies can last anywhere from 24 hours to 30 days, again depending on policy. I've seen both configurations break workflows because users assumed they were logged in across sessions when their token had actually expired server-side. The actual click-through process takes roughly 10 to 30 seconds under normal conditions. If it's taking longer than a minute, you're usually dealing with a network latency issue or an SSO timeout rather than a problem with the login mechanism itself.
Troubleshooting Common Login Failures
Cached credentials are the most common source of login failure. When a user changes their password on the directory side but the Point Care system still has the old credentials cached in its SSO assertion, you'll get an authentication mismatch. The fix isn't usually clearing your browser cache — it's resetting the SSO token or logging out through the identity provider directly before attempting to log back in. I ran into a specific issue last year where a clinic was using Point Care with Okta as their SSO provider. About 15% of their staff couldn't log in through the Click Log In button on any browser, but direct navigation to the Okta dashboard worked fine. The problem turned out to be a missing redirect URI configuration in the Okta application settings for the Point Care instance. The SSO flow was silently failing at the assertion exchange step. The workaround was to add the Point Care base URL and all subpaths as authorized redirect URIs in the Okta admin console. One engineer went around telling everyone to clear cookies and restart their computers for three weeks before we found this. Another issue I've seen repeatedly involves browser extensions. Ad blockers, password managers, and privacy tools like Privacy Badger will sometimes strip or block the cookies that Point Care sets during the SSO handshake. If you're behind a corporate proxy or VPN, the issue can compound because some of these tools intercept and modify HTTP headers. The practical fix is to test in an incognito or private browsing window with extensions disabled. That eliminates the variables fast.
Get the Full Details
Technical Nuances Most Guides Skip
Session affinity is a concept that matters more than people expect. Many Point Care deployments rely on stateful sessions where your subsequent requests need to hit the same application server that established your session. If your organization uses a load balancer without proper sticky session configuration, you might log in successfully but then get kicked back to the login page on your second click through the interface. This doesn't look like a login failure to the average user. It looks like the system is broken. The actual fix is often as simple as enabling session affinity on the load balancer or switching to a stateless architecture with a shared session store like Redis. Certificate pinning is another area where things quietly fall apart. If your Point Care instance uses mutual TLS (mTLS) for device authentication and the root CA certificate gets rotated or renewed, every device that has the old certificate pinned will lose access immediately. Users will see certificate errors that have nothing to do with their credentials. The workaround is to ensure your certificate rotation process includes updating all pinned certificates on managed devices before the old one expires. I've seen this cause overnight outages affecting hundreds of users because someone renewed a CA cert without coordinating with the endpoint management team.
Limitations and Where This Approach Falls Short
Point Care Click Log In works well for standard authentication scenarios, but it has real limitations. The biggest one is that it assumes a consistent identity provider integration. If your organization merges with another or acquires a clinic using a different SSO system, the login paths diverge and you end up maintaining separate credential flows. This creates friction for users who move between locations and also increases the attack surface because you're managing multiple authentication configurations. Mobile access is another weak point. Many Point Care installations are optimized for desktop browser sessions. The mobile experience often requires a separate app or a specially configured mobile browser profile. Push notifications for session expiration are unreliable across platforms. If your workflow depends heavily on mobile access, you're better off evaluating whether the native mobile application provides a more stable experience than the web-based Click Log In flow. For organizations with very large user bases, the SSO bottleneck becomes a real constraint. During peak hours — typically the first hour after clinic opens — you'll see a spike in authentication requests that can overwhelm the identity provider. This is especially true for institutions that rely on a single SSO vendor without load testing their integration. If this is happening in your environment, consider implementing a fallback authentication method or distributing the load across multiple identity providers.
What to Do If Standard Login Keeps Failing
If you've tried the standard troubleshooting steps and the system still won't accept your credentials, there are a few less obvious things to check. First, verify the system clock on your machine. Kerberos-based authentication, which many healthcare SSO systems use, requires time synchronization within a few minutes between the client and the domain controller. A drifted clock will cause silent authentication failures that look identical to password errors. Second, check whether your account has any active lockout policies from the directory service. Multiple failed attempts across different systems can trigger a lockout that isn't immediately visible in the Point Care interface. Third, verify that your browser's timezone settings match the server's timezone. Misaligned timezones can cause session token expiration calculations to go wrong in subtle ways.