The Actual Work of Writing and Maintaining Policy Guidelines
Most organizations treat policy guidelines as a document you write once and pin to an internal wiki. They are not. They are a living system that breaks under any amount of scale without constant revision. I spent three years managing this for a mid-size content platform and learned the hard way that the document itself matters far less than how it gets enforced across teams. When I say Policy Guidelines, I mean the codified rules that determine what gets allowed, restricted, or escalated in your system. This covers everything from AI output filtering to content moderation workflows. The confusion starts because everyone uses the same term for different things. Your engineering team calls them "content policy rules." Legal calls them "compliance guardrails." Support calls them "the thing moderators ask about at 2am." It is all the same document, and it is the same source of friction.
Building Policy Guidelines That Actually Work
Start with a decision matrix, not prose. I see too many teams write policy as paragraphs of explanatory text. Prose is ambiguous. A matrix forces concrete yes/no or tiered responses. Map every input type against every possible output category, then define the boundary conditions explicitly. If something falls between two categories, that gap becomes a support ticket, not a policy question. The version control aspect is where most people fail. Every change to your guidelines needs a timestamp, an author, and a reason code. Not for audit purposes. For the person who comes back six months later and needs to understand why a previously allowed category got restricted on a Tuesday. I had a situation where a policy change went live without a reason attached, and the subsequent spike in appeal tickets took our team four business days to untangle. The workaround was implementing a mandatory changelog field in our internal CMS that blocks save until the reason field is populated. Test your guidelines against edge cases before they reach production. The real stress test is never the standard case. It is the weird hybrid scenario that sits at the intersection of two rules. For example, a medical advice query that also contains profanity does not appear in your normal training data, but it appears daily in your support queue. Build a dedicated edge-case bucket and route those items to a senior reviewer before they become a precedent.
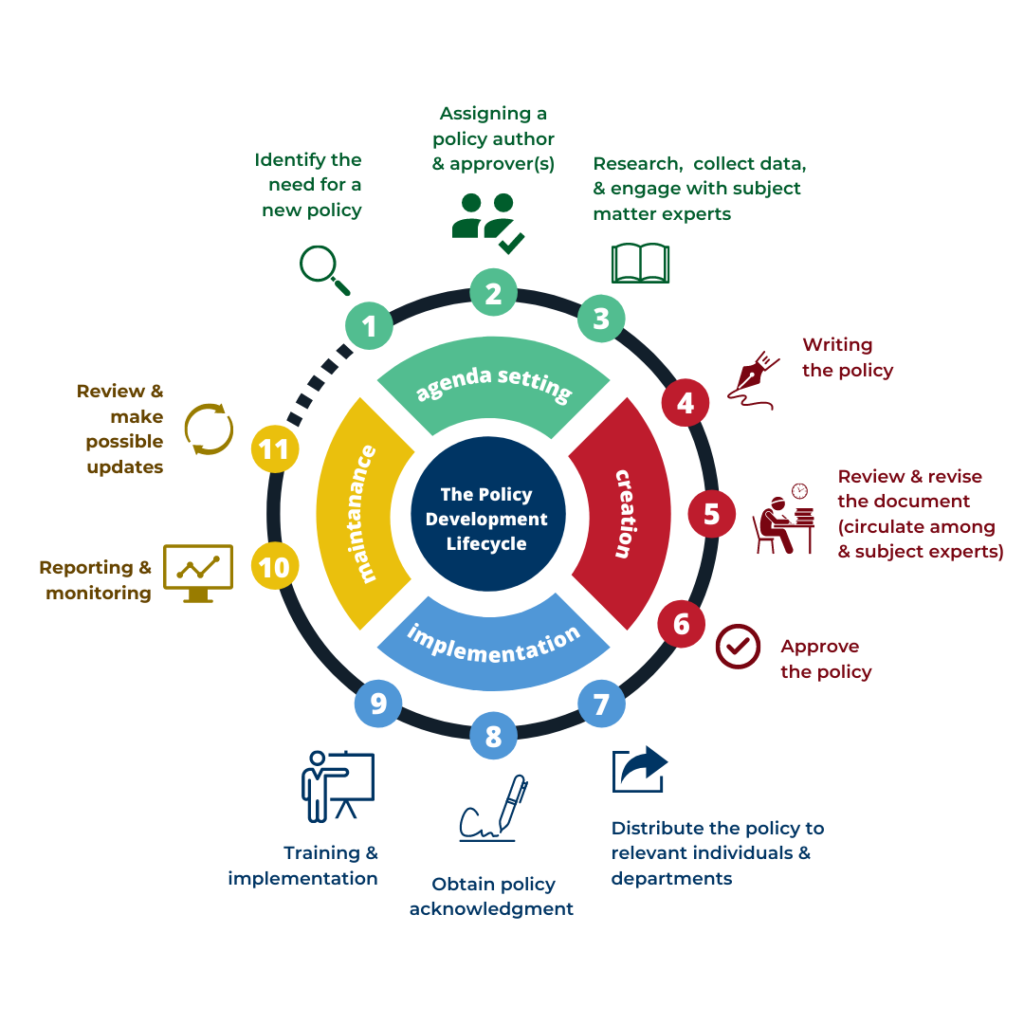
The enforcement layer needs to be separate from the policy definition. I know that sounds obvious until you watch a small team try to do both. The people writing the guidelines cannot also be the first line of enforcement. The feedback loop gets too tight and subjective judgment bleeds into the written rule. Keep them separate. Have enforcement report anomalies back to the policy team on a weekly cadence. That weekly batch review is where you catch the drift before it becomes a systemic failure. Here is the part nobody wants to hear about: Policy Guidelines will always lag behind reality. Your rule set is only as good as the most recent edge case you have already seen. You cannot write your way out of problems that have not happened yet. The practical response is to build a rapid amendment protocol that can push a guideline update within hours, not weeks. I have seen teams treat their policy updates like software releases, requiring full review cycles. By the time the cycle completes, the issue has already caused reputational damage or regulatory exposure. The biggest counter-intuitive insight is that having fewer, sharper rules beats having comprehensive coverage. A guideline that is too detailed becomes unenforceable. Your reviewers will interpret it differently depending on their mood, their workload, and whether they have had coffee. Aim for clarity over completeness. Test every rule by asking whether a new hire could apply it without escalation within five minutes. If they cannot, the rule needs to be rewritten, not expanded.
Get the Full Details

Performance metrics for your guidelines should include review speed, escalation rate, and inter-rater reliability. If two reviewers look at the same edge case and reach different conclusions more than ten percent of the time, your guidelines have a gap. That ten percent threshold is not arbitrary. It is the point where inconsistent enforcement starts affecting user experience and legal compliance simultaneously. There is no download link for a working Policy Guidelines document because yours is specific to your platform, your risk profile, and your regulatory environment. What you can download are templates and frameworks from recognized bodies. NIST's AI Risk Management Framework provides a solid structural foundation. The EU AI Act transparency requirements give you a compliance checklist if you operate in that market. Neither of these is sufficient on its own. They are starting points, not solutions. The realistic workflow after setting up your framework involves a quarterly audit cycle. Not annual. Quarterly. The landscape shifts fast enough that an annual review leaves you exposed for months at a time. Budget at least two full business days per quarter for your policy team to review incoming data, audit enforcement consistency, and update the guidelines accordingly. Anything less and you are just going through the motions.