Deciding Whether a Number Is Prime or Composite Without Losing Your Mind
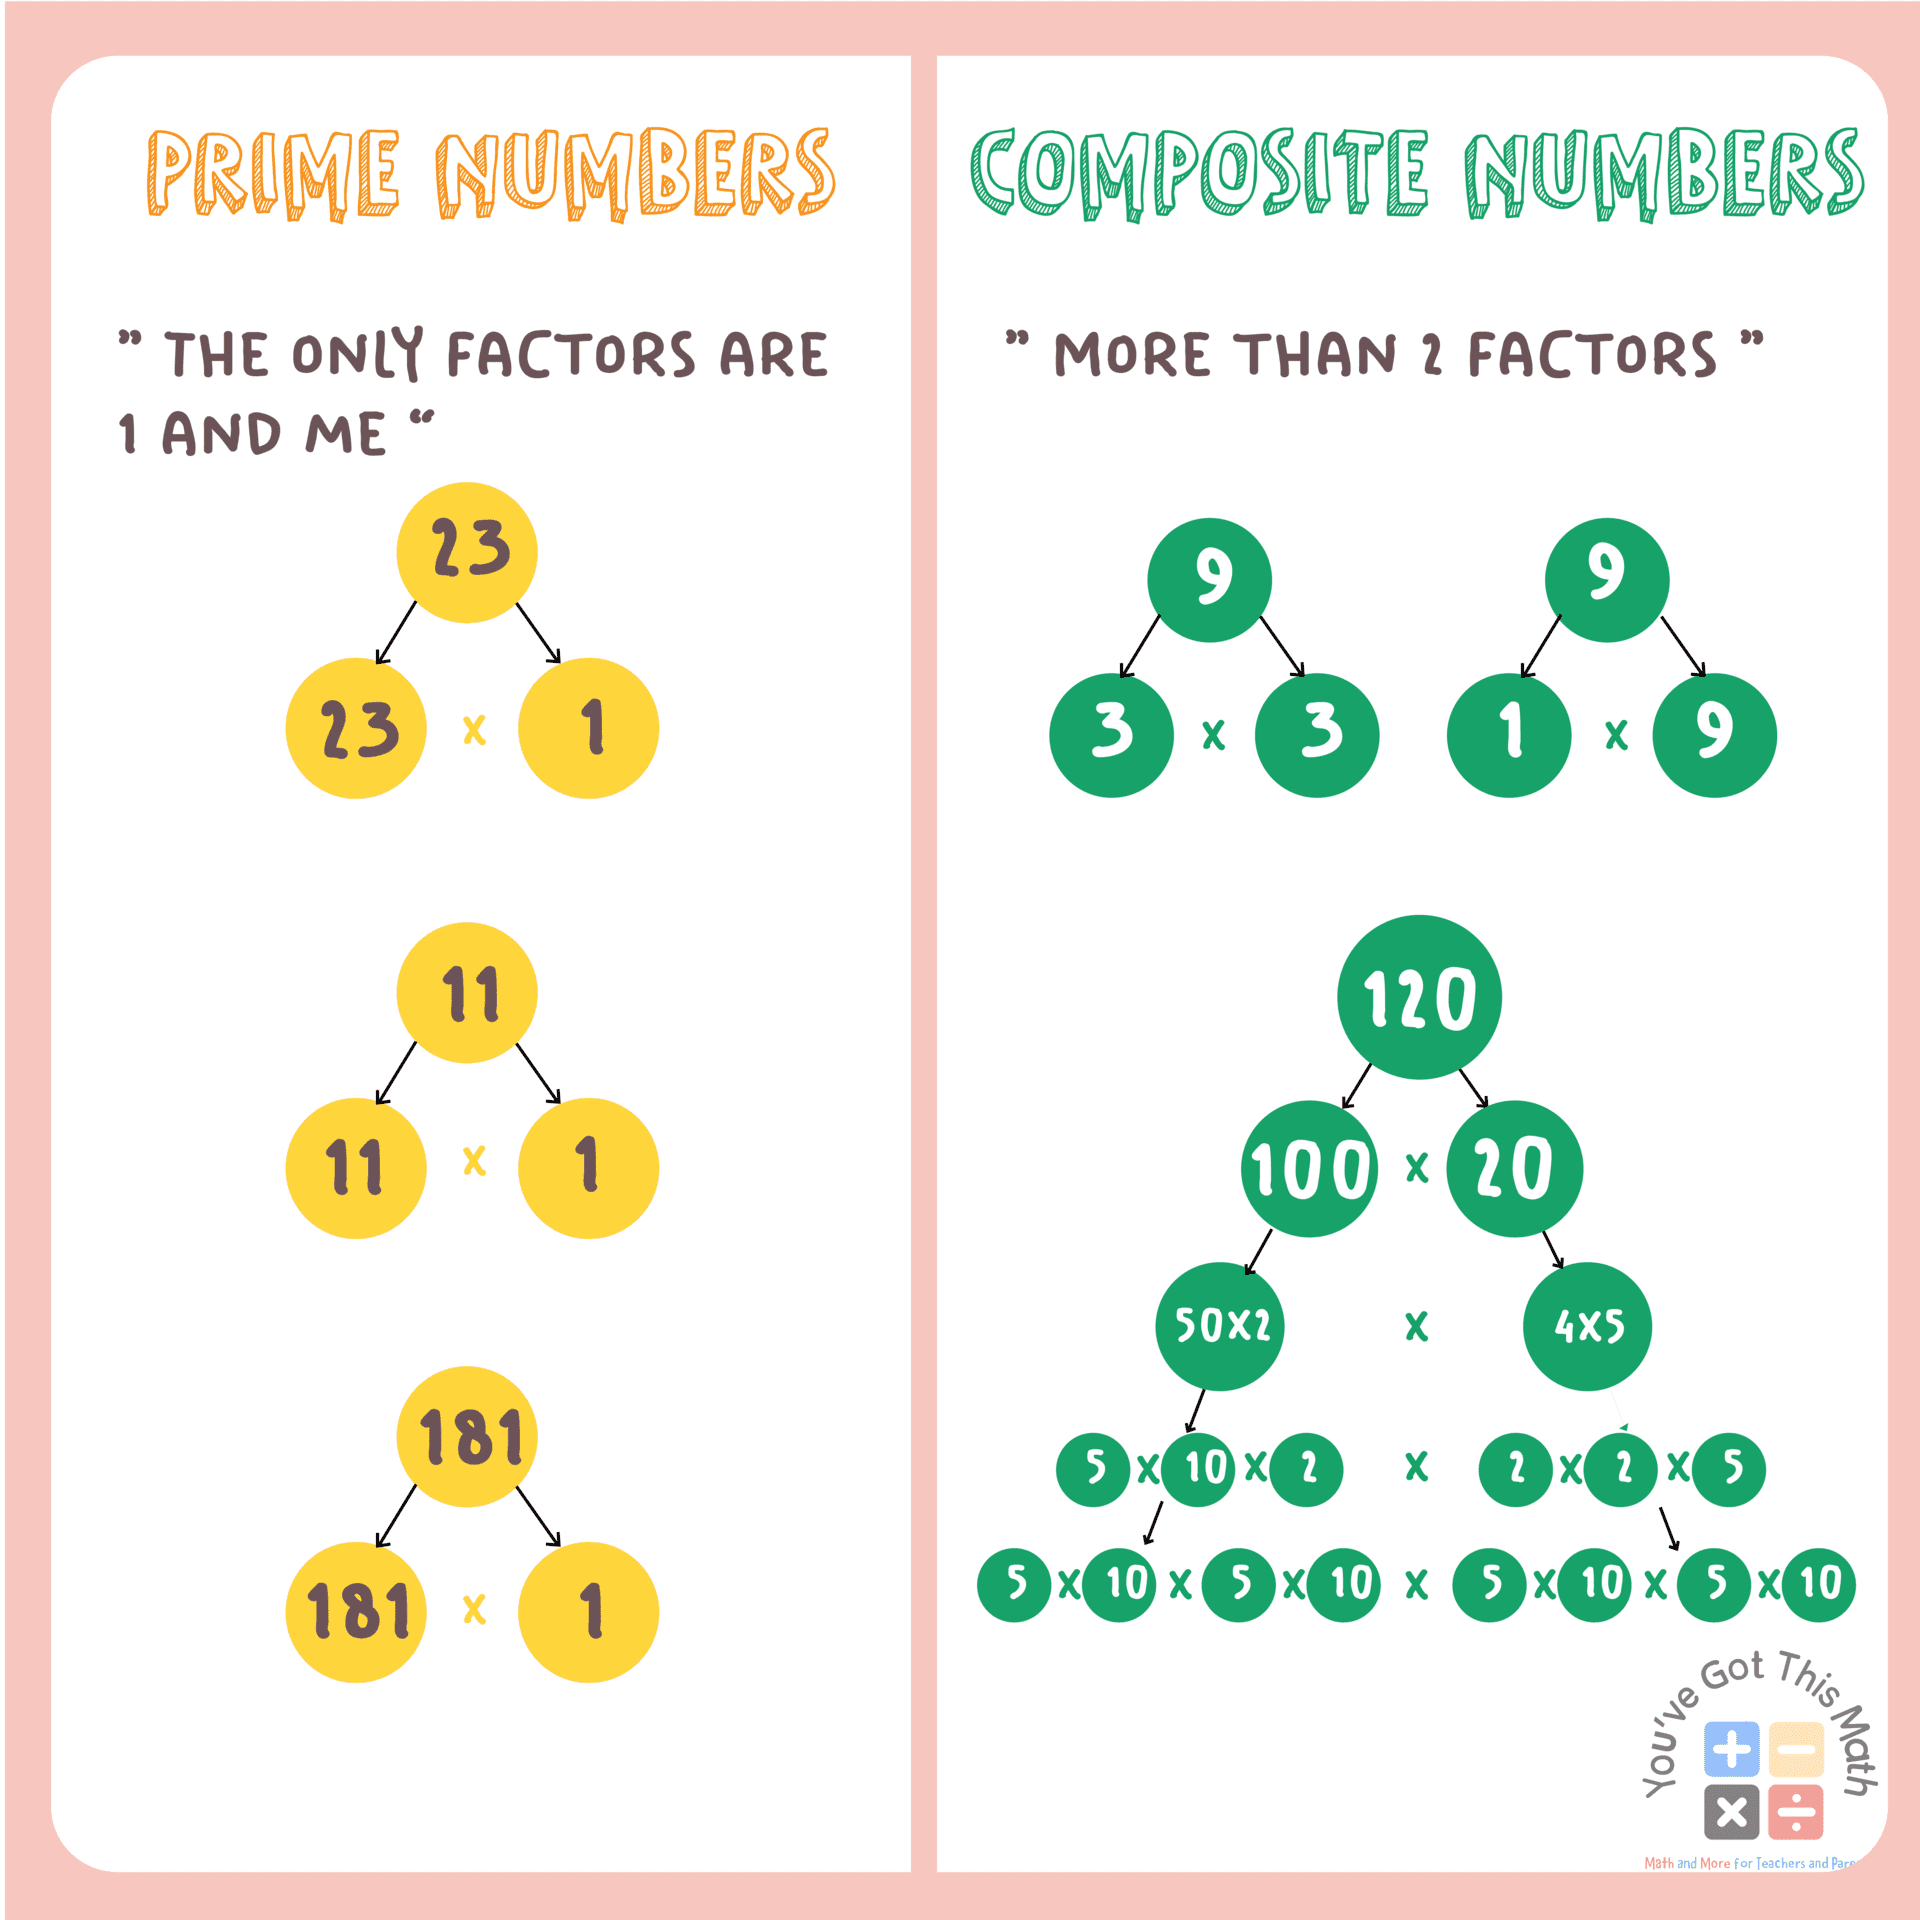
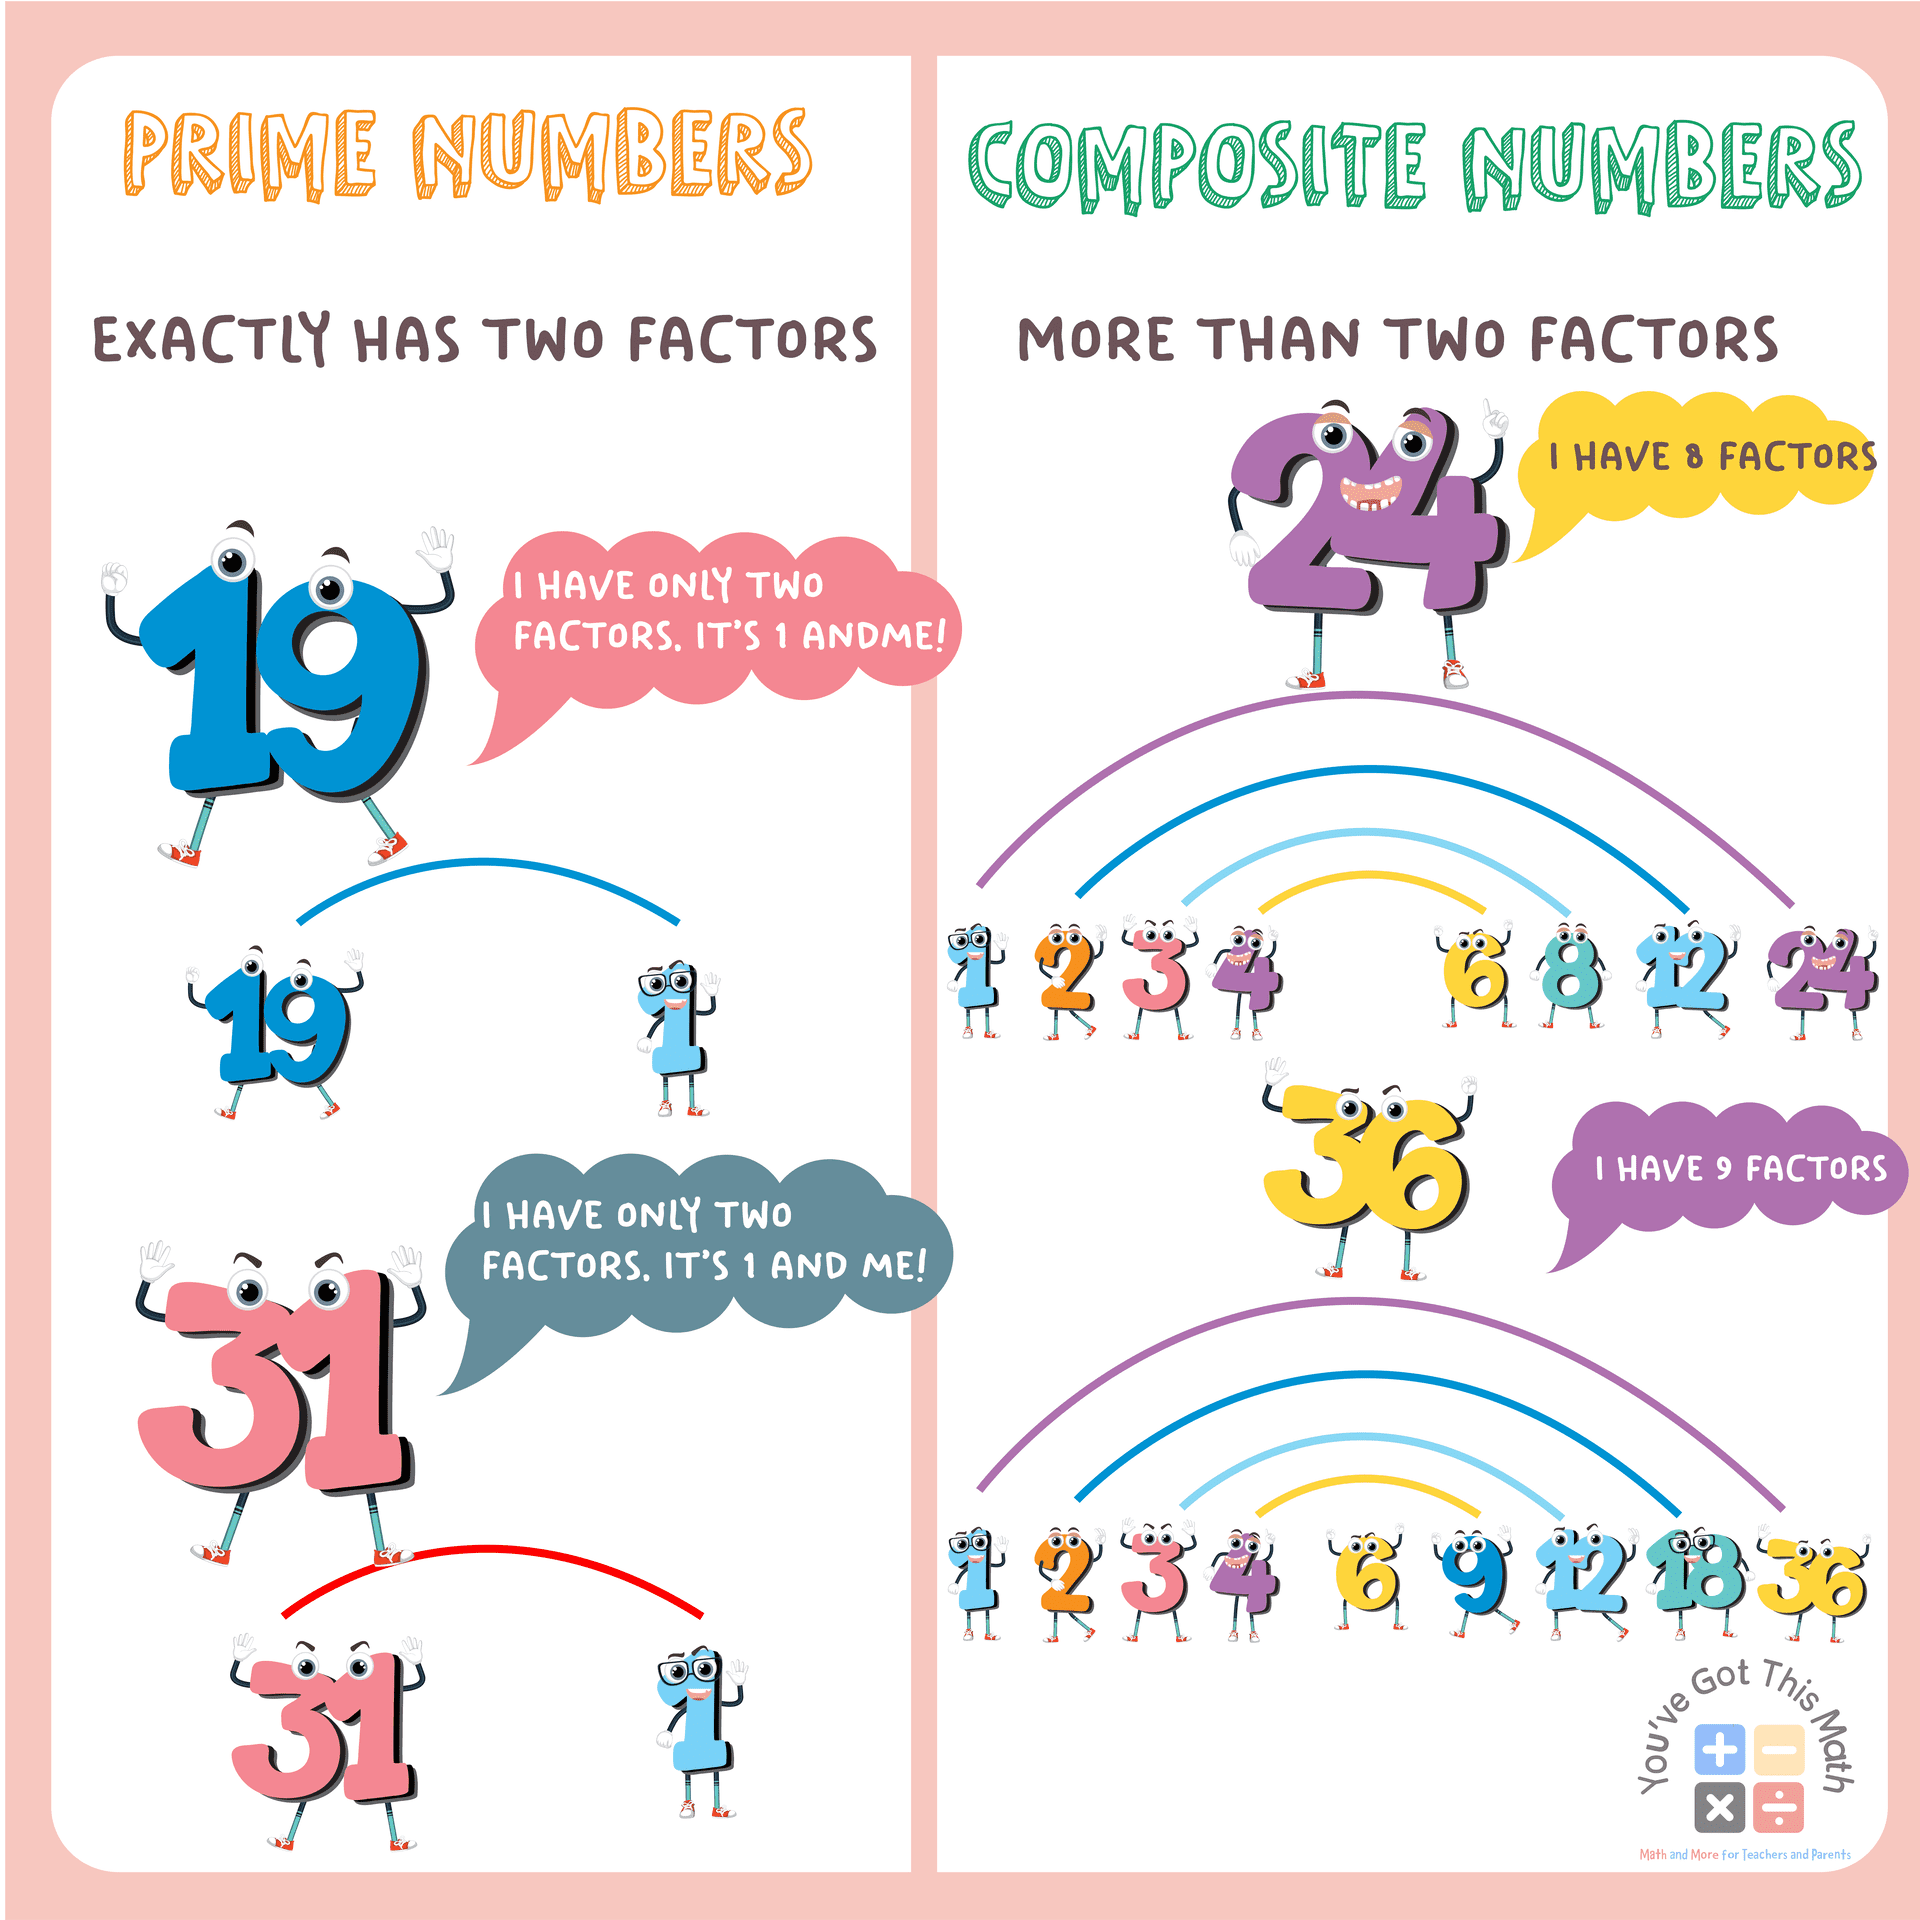
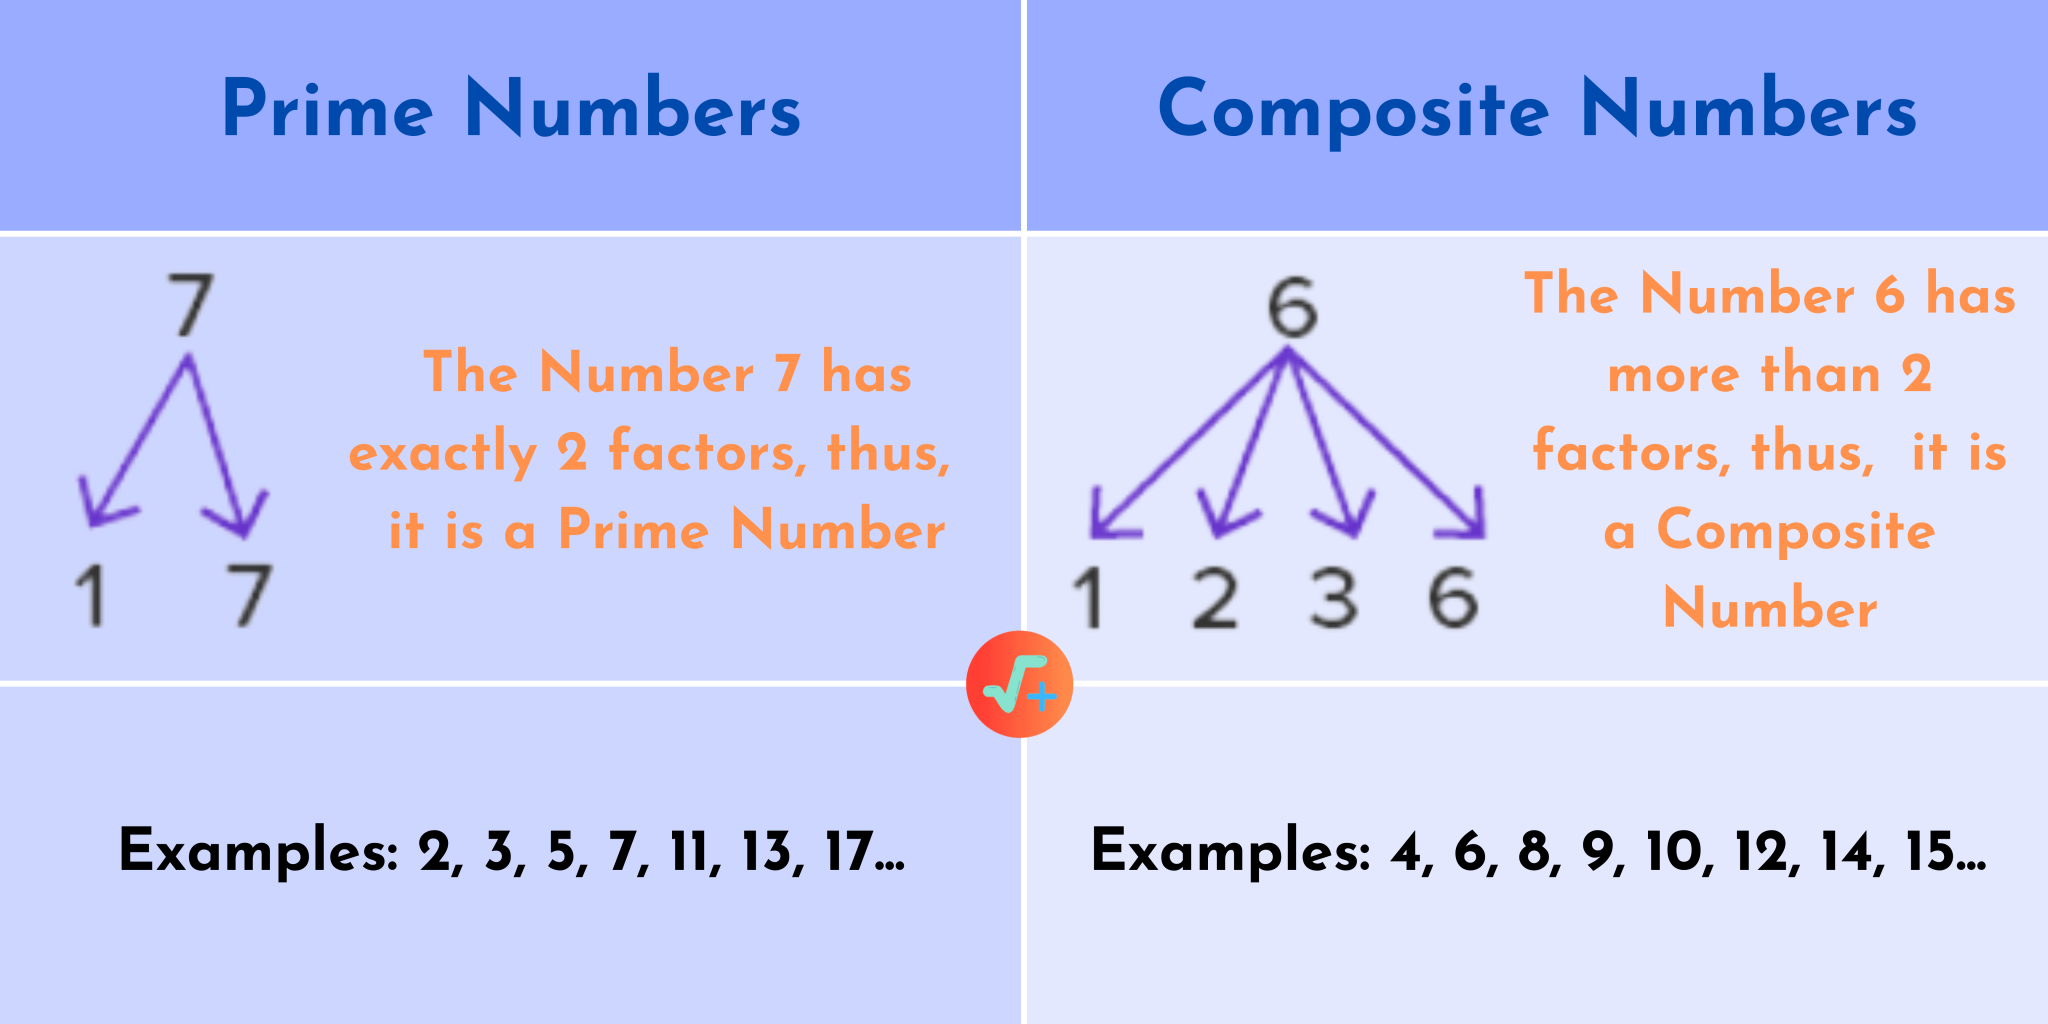
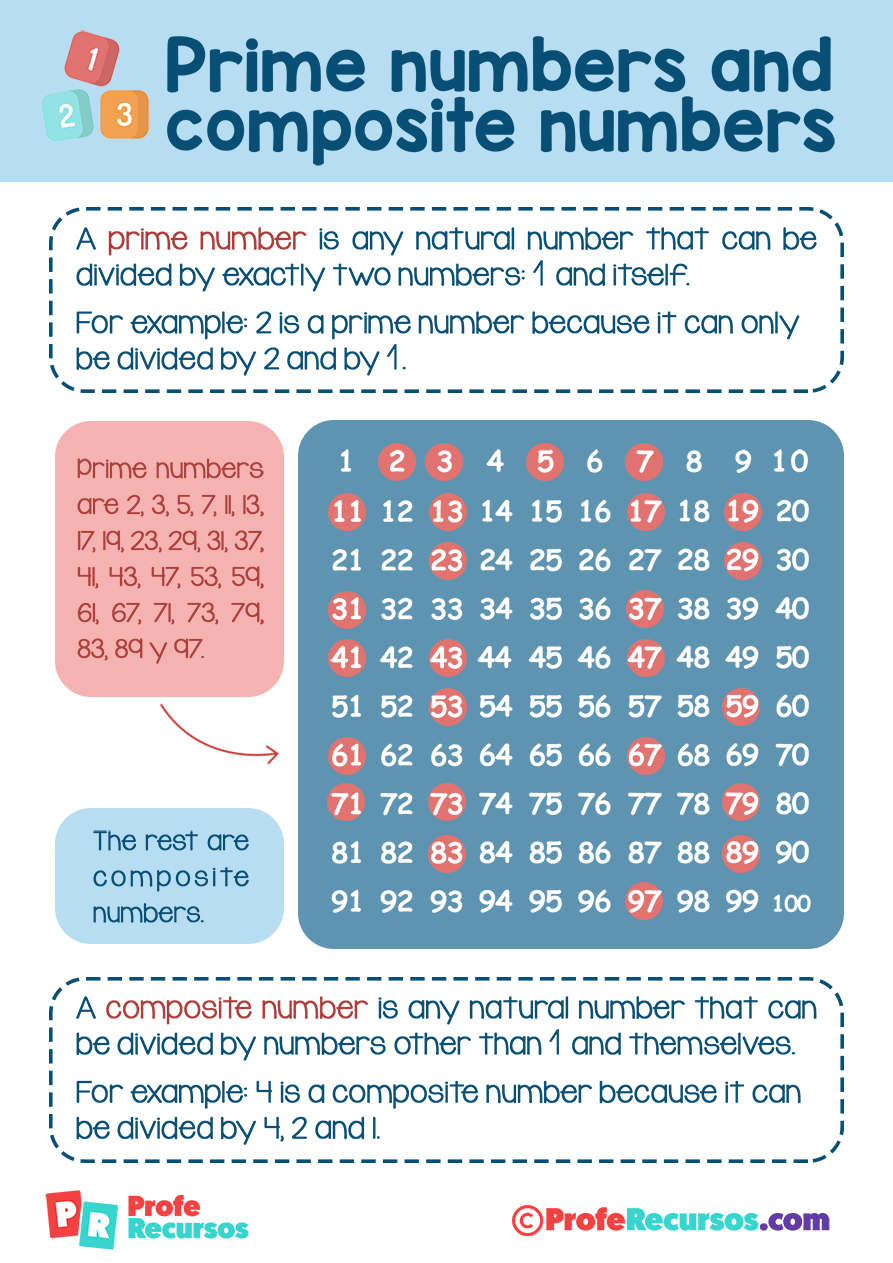
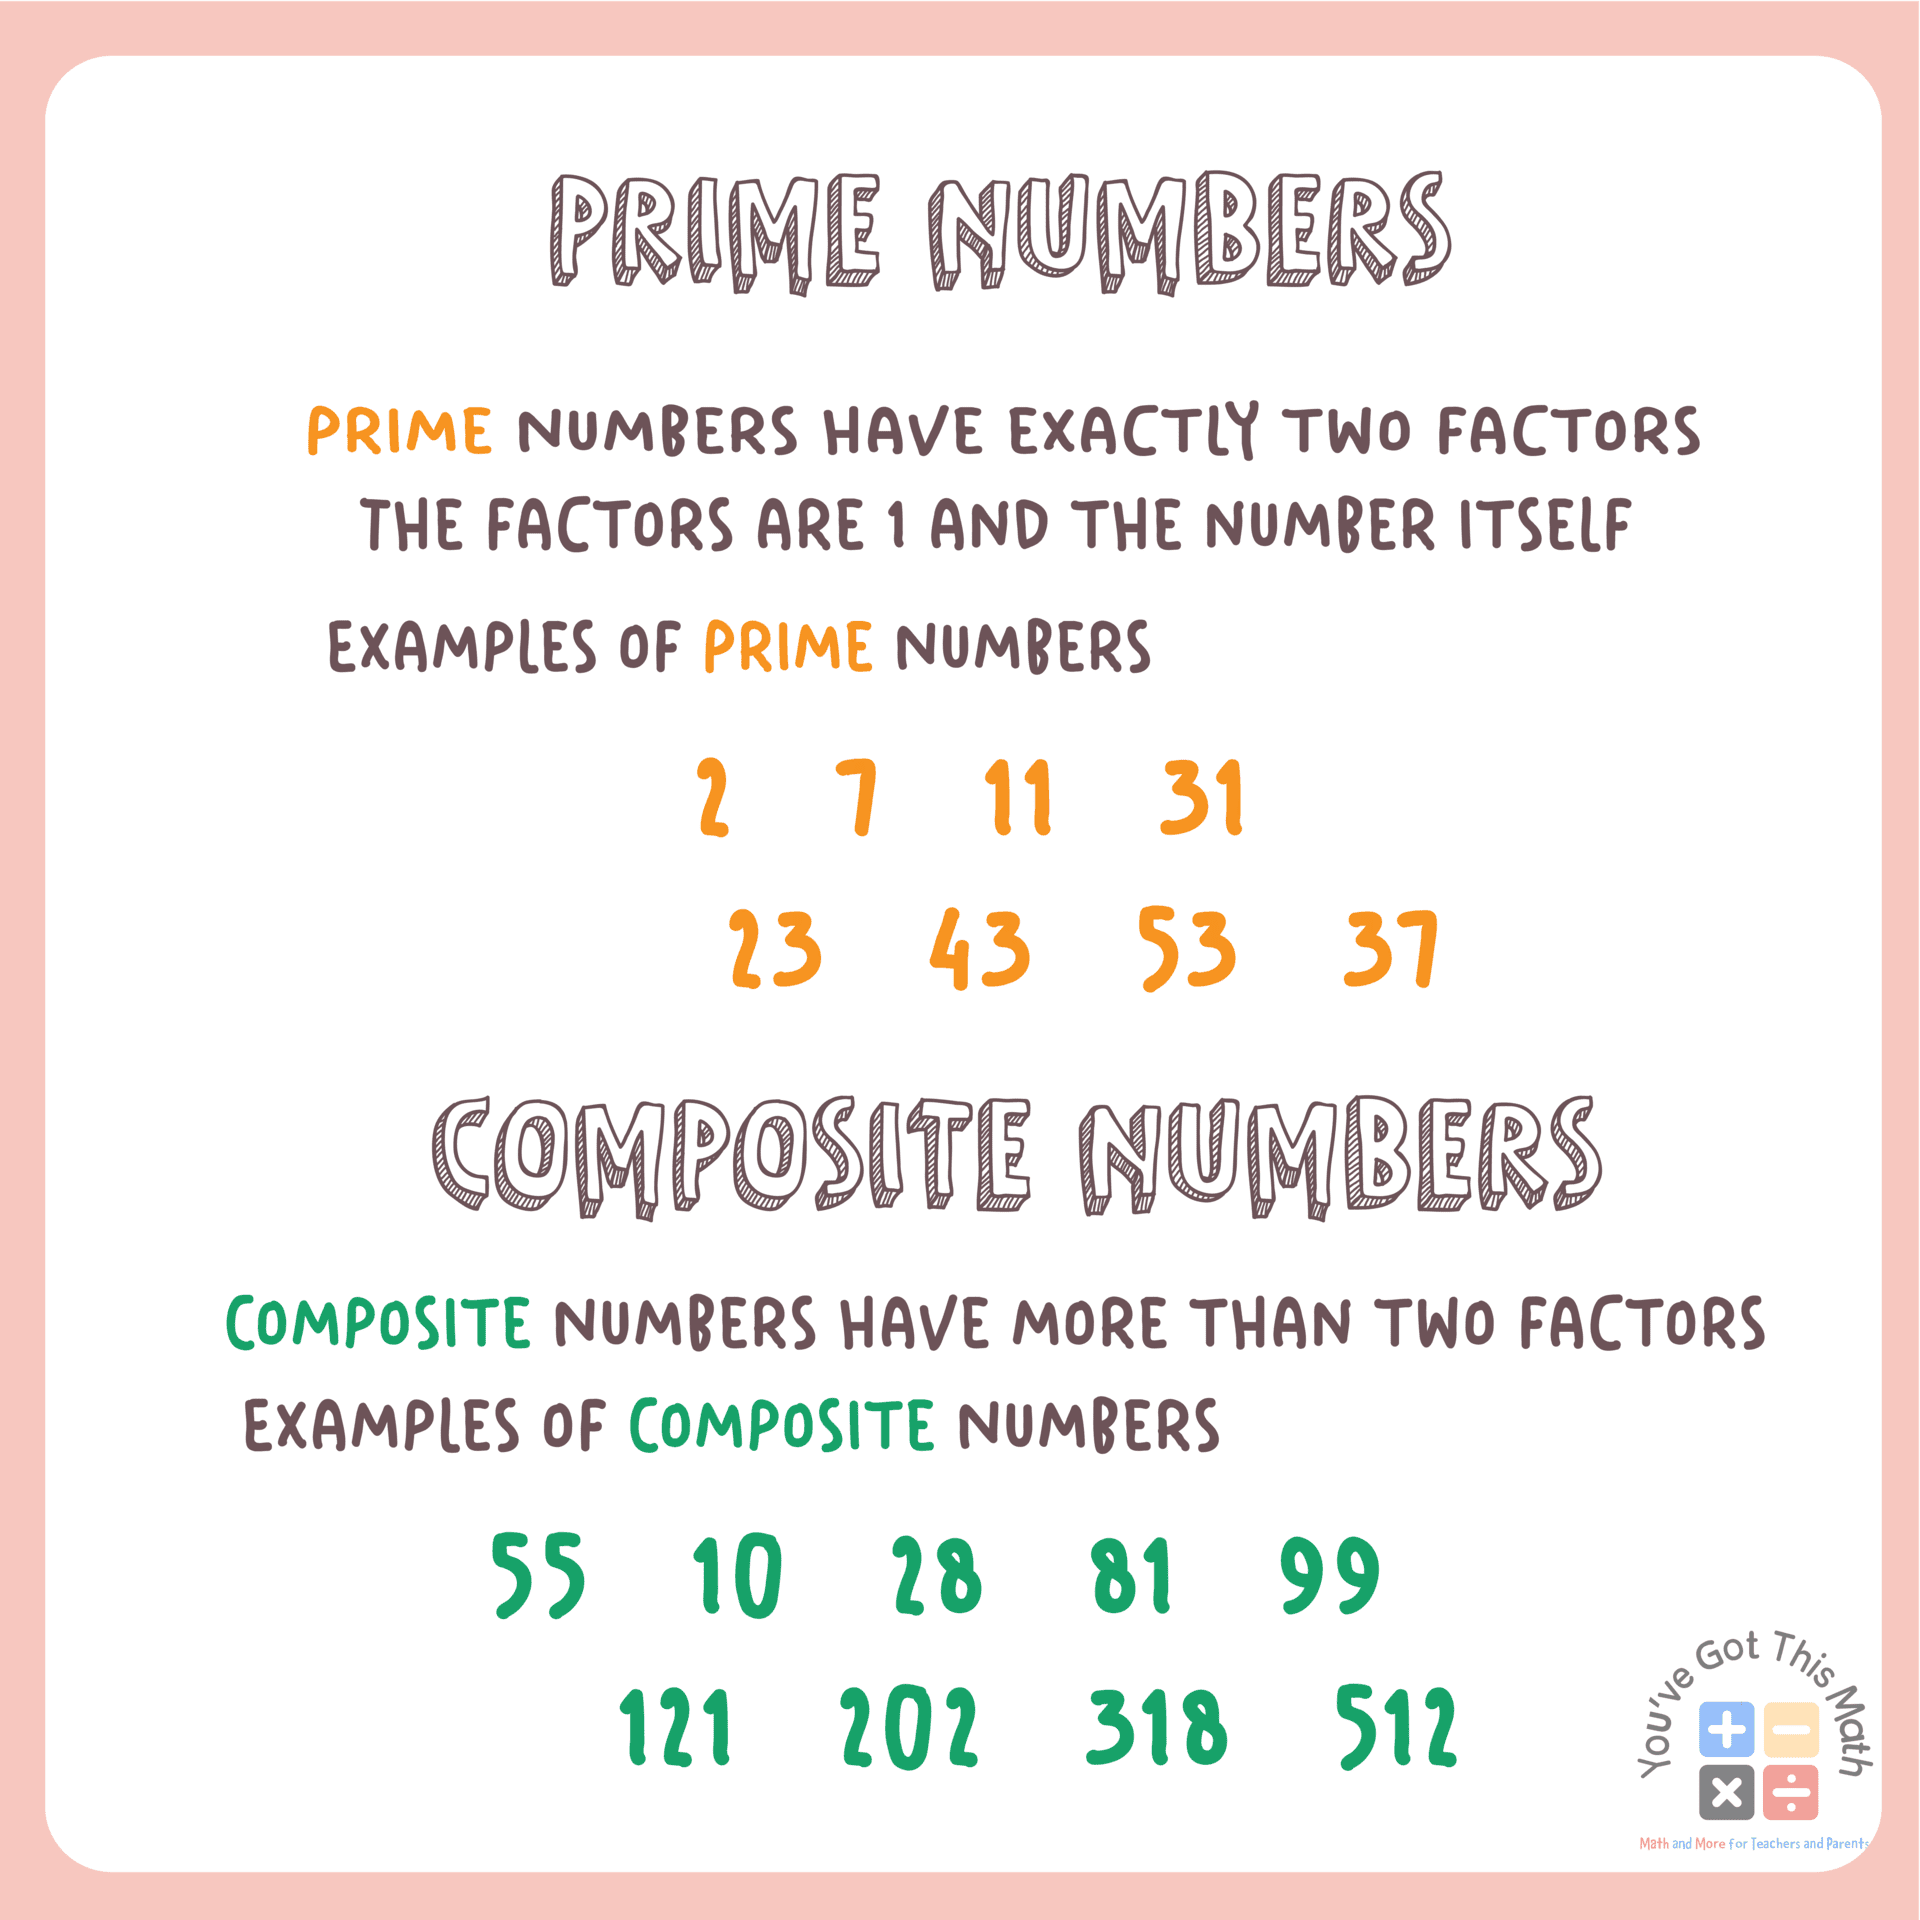
I used to run trial division by hand for numbers up to 10,000 when I was studying for my first cryptography certification. Took about 40 minutes per number if I was being careful. Now I script it, obviously, but the underlying logic hasn't changed since Euclid wrote it down. The distinction between Prime Or Composite Numbers is straightforward in theory, and the headaches only start when you actually try to apply it at scale. A prime number is an integer greater than 1 that has exactly two distinct positive divisors: 1 and itself. A composite number is any integer greater than 1 that is not prime, meaning it has at least one divisor other than 1 and itself. The number 1 is neither. That last part trips people up constantly in introductory classes, and it matters later when you're working with things like the Euler totient function, where phi(1) = 1 by definition and everything breaks if you treat 1 as prime.
The Practical Test for Prime Or Composite Numbers
The basic test is simple enough. To check whether a number n is prime, you divide it by every integer from 2 up to the square root of n. If any division produces a remainder of zero, n is composite. If nothing divides evenly, n is prime. You stop at the square root because if n has a factor larger than its square root, the complementary factor must be smaller than the square root, and you would have already found it. For example, checking 97. The square root is approximately 9.85, so you test divisors 2 through 9. 97 is not even. 9 plus 7 is 16, not divisible by 3. It doesn't end in 0 or 5 so not divisible by 5. 97 divided by 7 is 13 with a remainder of 6. None of 2 through 9 divide evenly, so 97 is prime. Checking 91 takes less than a second once you know the trick: 91 is 7 times 13. People miss that because 7 and 13 are both primes and the product doesn't look obviously composite at a glance. Here is where it gets practical. I was validating a set of RSA key parameters once and encountered the number 1099. On the surface it looks prime-ish. It's not even, the digit sum is 19 so not divisible by 3, doesn't end in 5. My first pass through the trial division checklist cleared 2 through 9. I was about to mark it prime when I caught myself and checked 11, which gave exactly 99 with remainder 10, then 13, which gave exactly 84 with remainder 7. Then 17 went through cleanly: 17 times 64 is 1088 with remainder 11. Wait, that's wrong. Let me recalculate. 17 times 65 is 1105. 17 times 64 is 1088. So 1099 minus 1088 is 11. Not divisible by 17. I kept going. 19 times 57 is 1083. 1099 minus 1083 is 16. Then 23 times 47 is exactly 1081. 1099 minus 1081 is 18. Finally 29 times 37 is 1073. 1099 minus 1073 is 26. I was past the square root of 1099, which is about 33.15, so I had tested everything I needed to and 1099 was actually prime. Good thing I ran the full check instead of trusting my initial gut feeling.
The edge case that actually cost me time was with large semiprimes, numbers that are the product of exactly two primes of roughly equal size. Say you're testing 1,000,003. The square root is about 1000. Trial division works, but it takes 1000 division operations, and if you're doing this for hundreds of numbers in a batch, it adds up. I once had a script that ran trial division for every odd number between 1 million and 2 million to generate candidate primes for a Diffie-Hellman exchange. It took roughly 3 hours on a laptop CPU. Switching to a Miller-Rabin primality test cut that down to about 12 minutes with negligible error probability. Miller-Rabin is a probabilistic test. It doesn't give you a absolute answer in the traditional sense, but for any base you pick, it either certifies that a number is composite or says it's probably prime. Run it with enough bases and the chance of a false positive drops below the probability of cosmic rays flipping a bit in your RAM. For practical purposes it is deterministic. The specific bases needed to make it deterministic for numbers below certain thresholds are known. For anything under 3,317,044,064,679,887,385,961,981, testing against bases 2, 3, 5, 7, 11, 13, 17, 19, 23, 29, 31, and 37 is sufficient. You can hardcode that and never worry about correctness again. There are a few things that beginner tutorials get wrong about Prime Or Composite Numbers that you should know about before you write production code. First, trial division is fine for numbers up to maybe a few thousand, but the runtime grows linearly with the square root of n. That is not a minor detail. Going from n = 10,000 to n = 10,000,000 increases the number of operations from 100 to 3,162. That is a 31-fold increase for a 1,000-fold increase in input size.
Get the Full Details
Second, most people do not bother optimizing trial division past skipping even numbers. Testing only odd divisors cuts your work in half immediately. Then you can skip multiples of 3 as well, testing divisors of the form 6k +/- 1. That is another 33 percent reduction. Combined, these two optimizations turn a slow brute-force approach into something that handles numbers in the millions without noticeable delay on modern hardware. Third, don't confuse primality testing with factoring. Knowing a number is composite does not tell you its factors. If you need the actual prime factorization, that is a fundamentally harder problem. There is no known efficient algorithm for factoring large integers, and the security of RSA depends entirely on that hardness. Trial division for factorization will work for small semiprimes but becomes impractical once the factors are in the hundreds of digits. Elliptic curve factorization and the general number field sieve are the standard approaches at that scale, and even those struggle with cryptographically relevant key sizes. If you are just building a homework helper or a basic classification tool, trial division with the 6k +/- 1 optimization is perfectly adequate. Write a function that handles 2 and 3 as special cases, filters out multiples of 2 and 3 early, then loops from 5 up to the square root in steps of 6, checking both i and i + 2. That covers every prime candidate without testing any multiple of 2 or 3. For anything larger, plug in a Miller-Rabin implementation. There are plenty of reference versions online, but a correct implementation from scratch is not difficult and you will understand where the edge cases hide.
One more thing that causes problems in practice. Some systems and libraries include 1 in their list of "odd numbers" and then proceed to classify it as prime if they only check for evenness. Make sure your first line of defense explicitly rejects values less than 2. After that, the only input you need to handle is 2, which is the only even prime, and then odd numbers greater than 2. Everything else is just a matter of running the loop correctly.