Understanding Protected Mode Software Architecture Tom Shanley
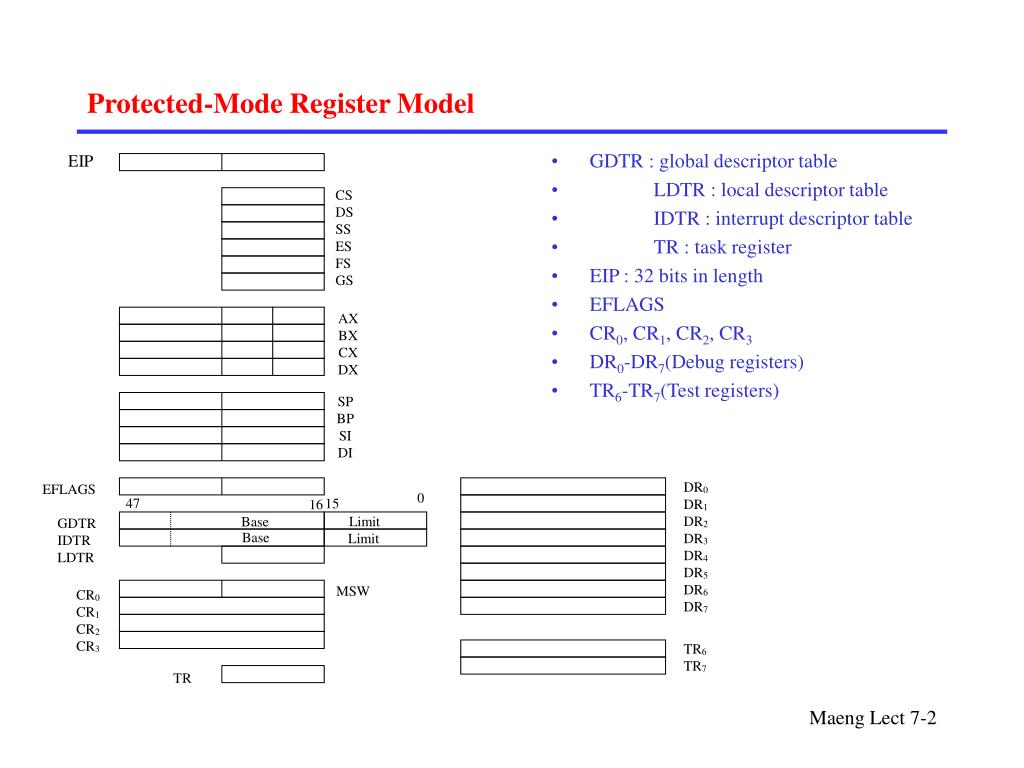
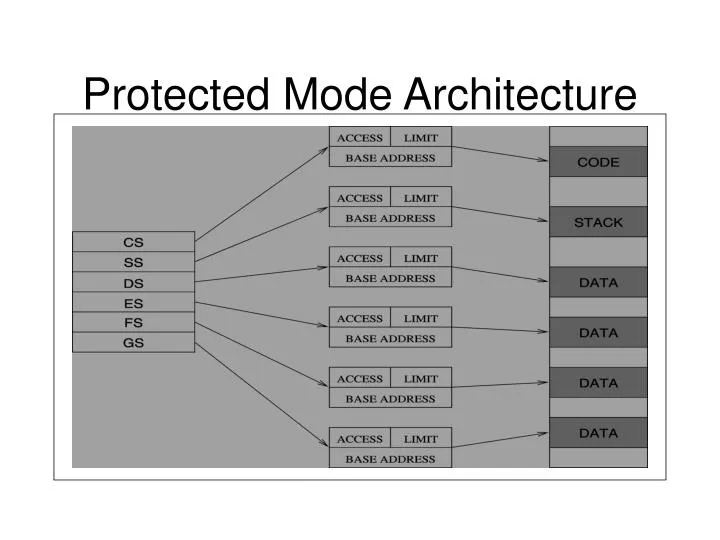
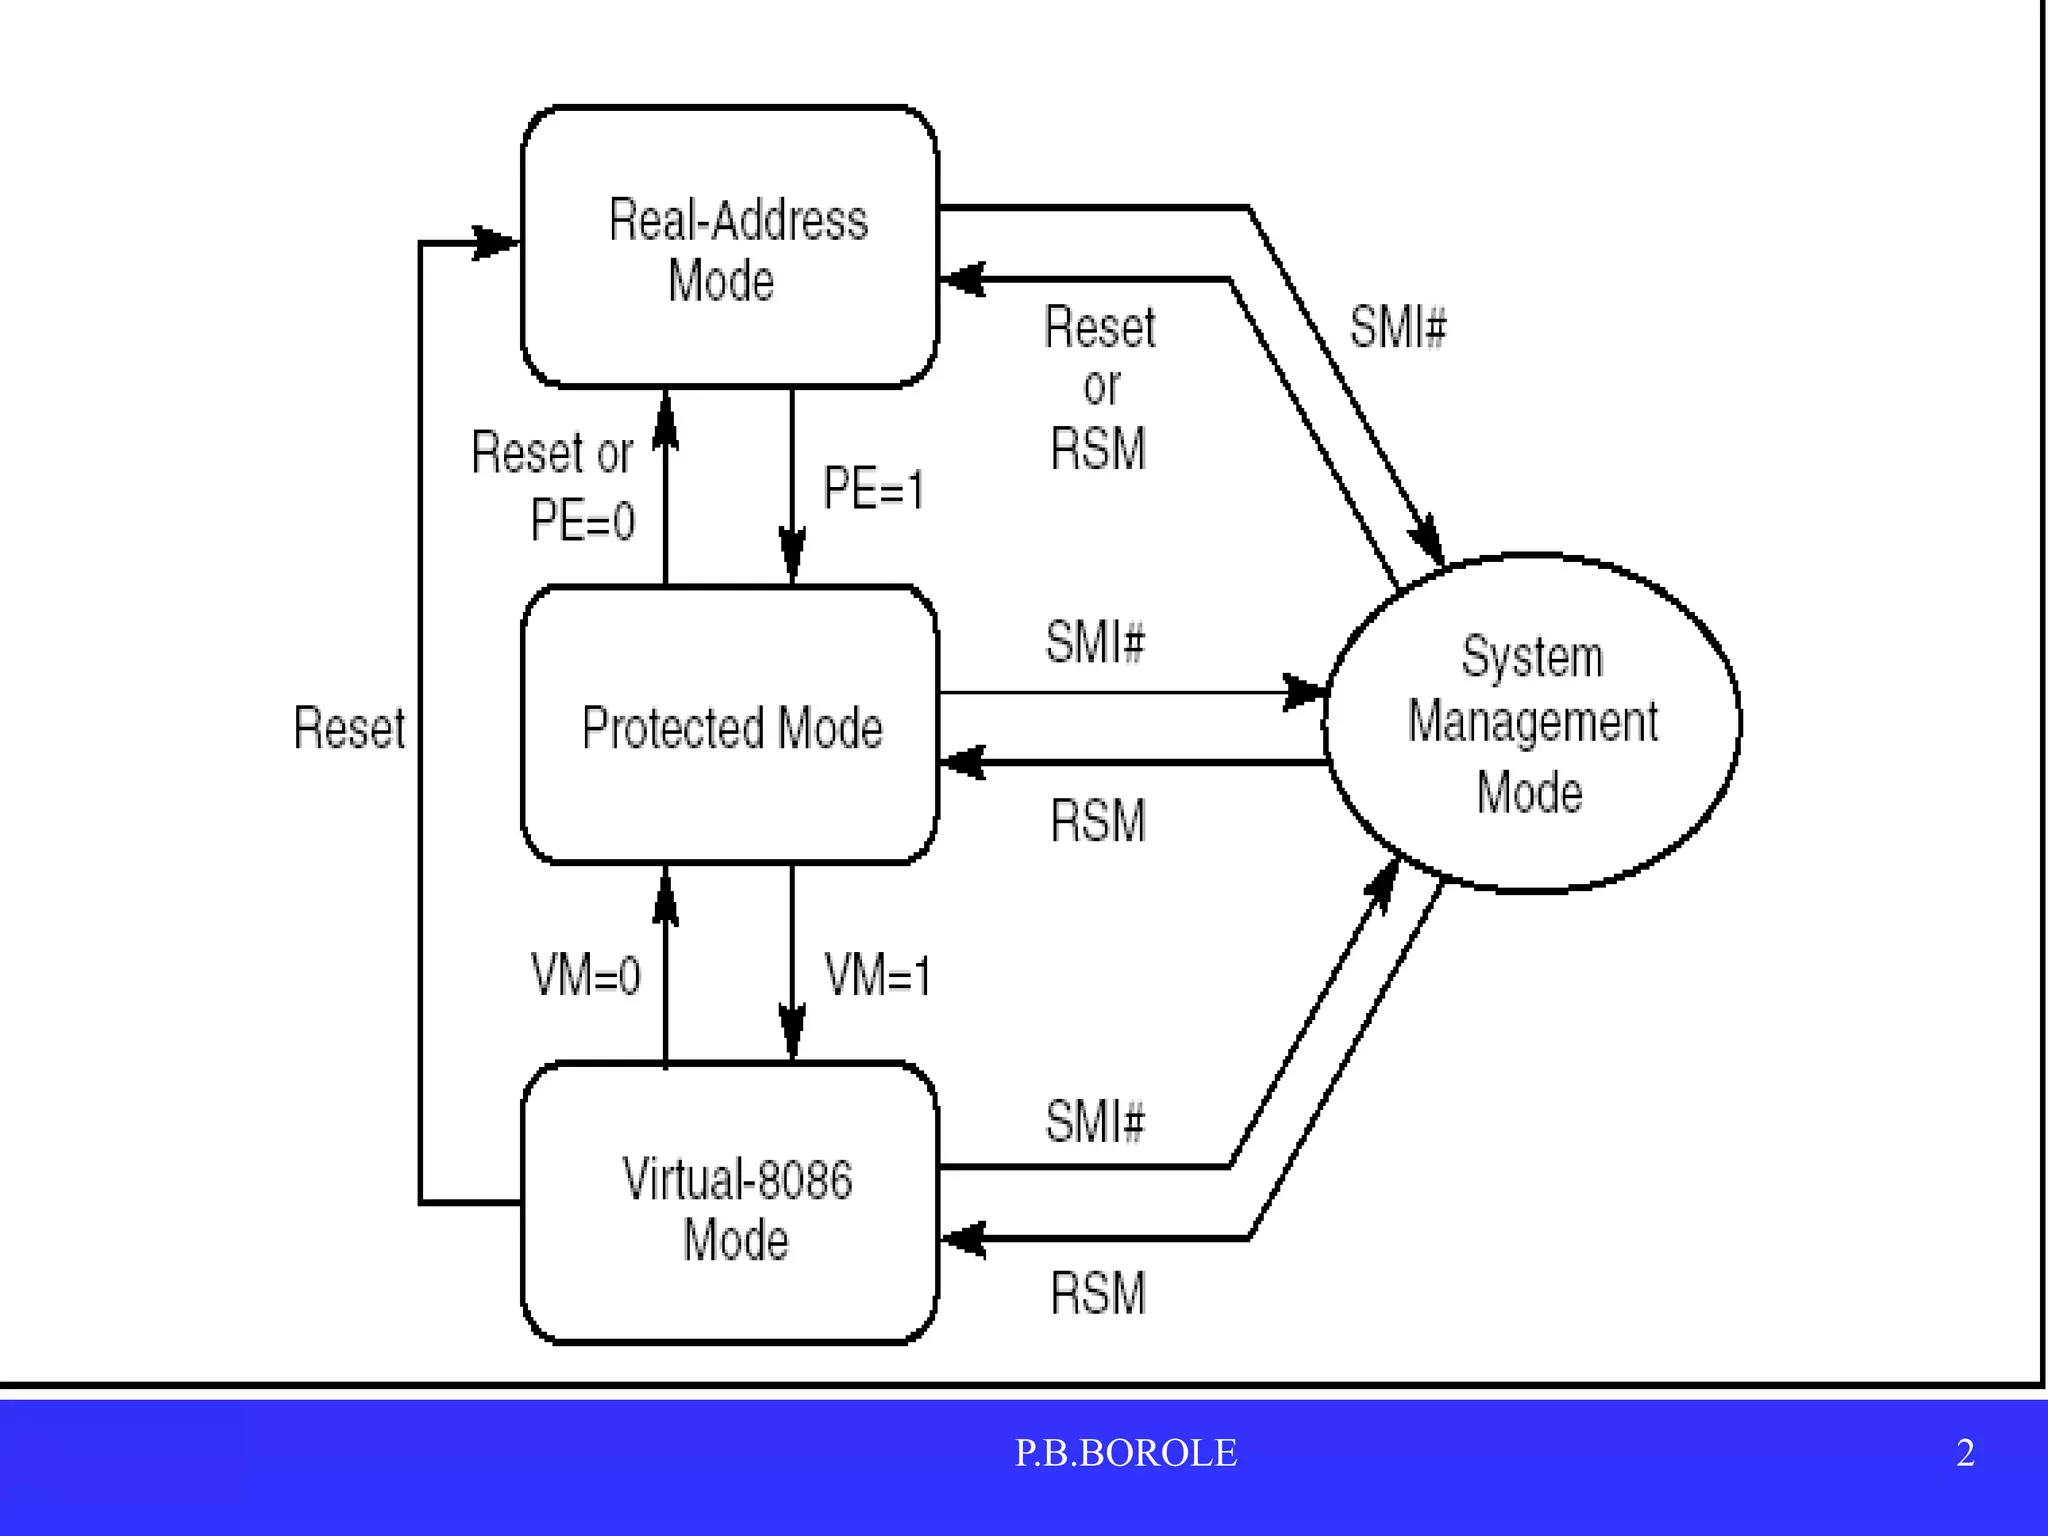
I've been working with low-level system software for a while now. When I first needed to understand protected mode from a practical standpoint, I picked up Thomas Shanley's Protected Mode Software Architecture. It's not the most engaging read, but it's one of the few sources that actually covers the ground between the Intel manual and an actual working OS kernel. Shanley's work focuses on x86 protected mode operation and how software architects should structure an operating system around it. The core topics include segmentation, paging, task state segments, interrupt handling, and the overall memory management model. Most of the examples assume a 32-bit environment, which matters because that's the protected mode most people actually deal with in practice. The book walks through the transition from real mode into protected mode, then explains how to set up descriptors, GDTs, IDTs, and LDTs. It covers how to handle interrupts and exceptions once you're in protected mode. The later sections get into paging and how virtual memory maps onto physical memory. There's also material on multiprocessor considerations, though it's lighter than you might want for a serious SMP project.
How It Actually Works in Practice
The transition code itself is straightforward. You write a small assembly routine that loads the new descriptor table base addresses, sets the PE bit in CR0, and jumps to protected mode. Shanley shows the standard approach. The book doesn't dwell on trivialities like that. It assumes you already know or can look up the basic assembly sequences and moves on to the architecture stuff that matters more. Where the book gets useful is in explaining how the various segments interact with the MMU and how to organize your kernel data structures around those constraints. For example, understanding that the TSS isn't just for task switching but also holds the stack pointer used during interrupt handling changes how you think about your exception entry paths. That's the kind of thing most tutorials skip over. I spent a fair amount of time working through the paging examples in the second half. The walk through setting up page tables, mapping virtual addresses, and dealing with page faults was detailed enough to be practical. I found the section on how the CPU actually walks the page tables particularly useful. It helped me debug a page fault handler that was silently dropping errors because I hadn't accounted for a flag in the PDE I was using.
Protected Mode Software Architecture Tom Shanley practical approach
When you're actually building something with this, here's what you'll do most days. You start with the boot sector in real mode, then switch to protected mode early. Set up a minimal GDT with at least a code segment and a data segment. Load IDT entries for the exceptions you care about. Enable paging if you need virtual memory. From there you build up the kernel on top of that foundation. The book organizes these topics sequentially, which works fine for learning. In a real project you'll jump around between chapters as problems surface. I kept it on my desk while debugging interrupt latency issues and went back to the sections on TSS layout and interrupt descriptor organization. That's how I'd recommend using it rather than reading cover to cover.
Get the Full Details

Common Pitfalls Beginners Run Into
One thing that catches a lot of people off guard is descriptor alignment. The GDT entries need to be properly aligned and the tables themselves have size limits tied to the descriptor table registers. I once spent several hours chasing an exception that turned out to be caused by a descriptor crossing a 4096-byte boundary in a setup I was testing on a VM with strict memory layout. The fix was just to reorganize the descriptor table to stay within a single page. Shanley mentions the alignment requirements but doesn't emphasize how easily you can trip over them in a dynamically built GDT. Another issue is stacking order in the TSS. If your kernel and your interrupt handlers don't agree on which stack to use on entry, things break in ways that are hard to trace. The book explains the hardware behavior clearly, but it doesn't spell out the convention most implementations follow. You end up figuring that part out on your own or by looking at existing source code. There's also the matter of nested interrupts and how the CPU automatically pushes flags and code selectors during exception handling. If your exception handler doesn't restore those in the right order, the return instruction will jump somewhere unexpected. I encountered this when writing a double fault handler. The processor was returning to garbage because my handler didn't account for the implicit push that happens before your interrupt routine even starts executing.
Limitations of This Approach
The book is firmly rooted in 32-bit x86 protected mode. If you're working in long mode or on a different architecture, none of this applies directly. The multiprocessor coverage is minimal. Modern kernels dealing with many cores will need resources beyond what Shanley provides. The examples also lean heavily toward a monolithic kernel style, so if you're building something modular or microkernel-based, you'll need to adapt the organizational principles rather than follow them directly. Another gap is that the book doesn't cover UEFI booting or modern boot protocols. If you're starting from a bare metal environment with GRUB or a custom bootloader, you'll need supplemental material for the transition path. The CPU mode switching content is solid, but getting there today involves more infrastructure than it did when the book was written.
Where to Find It
Protected Mode Software Architecture by Thomas Shanley is available through most technical book retailers and on Amazon. It's been in print for a long time, so you'll also find used copies and possibly digital versions through archives. The ISBN is 0-13-095973-8 for the first edition. Later printings may have minor updates but the core content stays the same. There aren't really modern equivalents that cover the same ground from the software architecture angle. The Intel manuals are more complete but they're reference material, not an architecture guide. For someone trying to understand how the pieces fit together rather than just looking up register bits, Shanley's book remains one of the better options available.