
The Human Factor Nobody Trains Properly
Most security teams spend thousands on phishing simulation platforms and then wonder why click rates stay around 30%. The problem isn't the training tool. It's that nobody teaches people what the attacker is actually doing to their brain in those five seconds before they click. The Psychology Of Social Engineering Attacks is less about clever tricks and more about predictable human bugs that show up in almost every organization the same way. When someone gets a call saying their account is locked, their amygdala fires before their prefrontal cortex has time to check whether the caller actually has any business verifying their credentials. That gap between threat detection and rational evaluation is where the attack lives. It's not a flaw in the person. It's a feature of how humans are wired to respond to urgency and authority.
Why Understanding Psychology Of Social Engineering Attacks Matters More Than Any Tool
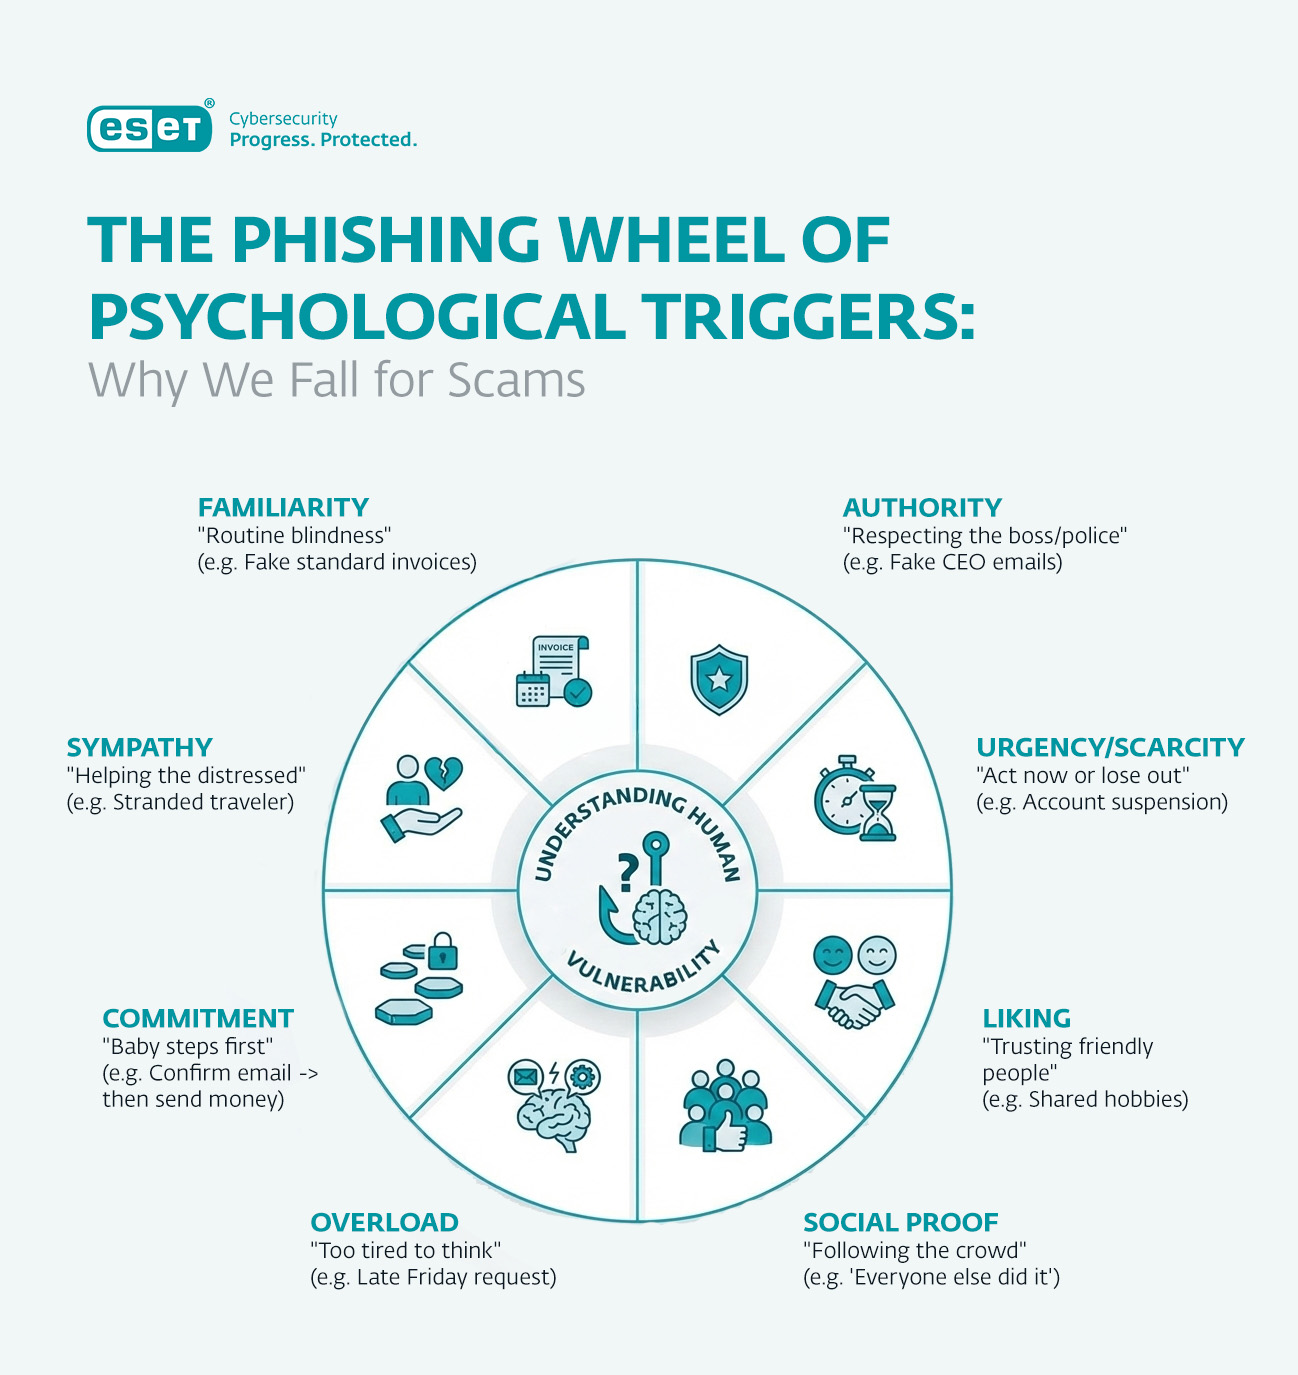
I ran a simulated campaign last year against a mid-size financial services firm. We crafted an email that looked identical to their internal IT alerts. Same sender name format, same subject line structure, even the same footer. The click rate was 41 percent. When I went back and talked to the people who clicked, almost all of them said the same thing: it looked like something they'd seen a hundred times before, so they didn't double-check. That's the part that sticks with me. The attackers don't need to be more convincing than real IT. They just need to be close enough that the target's pattern recognition kicks in and skips verification. Most people aren't being stupid. They're being efficient. Their brain is saving energy by treating a familiar-looking message as safe, and that's exactly what social engineers exploit. The classic frameworks you'll find in textbooks cover reciprocity, scarcity, authority, consistency, liking, and social proof. Those are real. But in practice, the ones that actually move people are usually a combination of two or three running at once. An email that triggers both authority and scarcity hits different than one that only triggers one. A vendor outreach that feels like a favor (reciprocity) and references something specific about your recent work (liking and personalization) is exponentially more effective than a generic plea.
The Mechanism Behind Most Successful Attacks
Here's what happens in a typical successful phishing scenario. The target receives a message that appears to come from someone or something they trust. The message creates a mild sense of unease or urgency. Before the target has time to verify independently, they take a small action. Clicking a link. Replying with information. Initiating a transfer. Each step is small enough that it doesn't feel like a big decision. By the time the full scope of what just happened registers, the damage is done. The reason this works so reliably is that humans have what psychologists call system 1 and system 2 thinking. System 1 is fast, automatic, and emotional. System 2 is slow, deliberate, and logical. Social engineering attacks are designed to keep you in system 1. They do this by making the request feel normal, urgent, or authoritative. The moment you start questioning whether you should really be doing this, you've moved toward system 2, and the attack loses its power. That's why attackers build in urgency and familiarity simultaneously. I've also noticed something most training programs miss. People who have been phished before are sometimes more vulnerable the next time, not less. After a false alarm or a near miss, the brain tends to normalize the threat rather than heighten vigilance. It's the same mechanism that makes people ignore smoke alarms after a few false triggers. I've seen security teams beat themselves up over repeat offenders, but the data suggests the issue is environmental, not individual. The environment is teaching the wrong lesson.
Get the Full Details

Counter-Intuitive Things I've Learned Running These Campaigns
First, fear-based awareness training often makes things worse. I worked with a team that ran a campaign showing dramatic images of hacked accounts and stolen data. The following month, their click rate didn't drop. It went up. People who were scared didn't become more careful. They became more anxious, and anxious people make faster, less deliberate decisions. The fix was switching to practical, scenario-based training that showed people exactly what to look for and gave them a simple verification step to follow. Click rates dropped by about half after six weeks. Second, the most dangerous attacks don't look like attacks at all. The best ones look like routine work. A message from your manager asking you to complete a quick form. A notification from your expense system that needs a click to avoid deletion. An invoice that looks like every other invoice you've processed. The attacker studies your environment long enough to make the request feel like background noise. This is called contextual social engineering, and it's what separates amateur attempts from professional operations. Third, and this one matters a lot: organizational culture determines your attack surface more than any security control. In a company where asking questions is seen as weakness or slowing things down, people will click through suspicious requests rather than pause and verify. I've seen this repeatedly. The same phishing email that gets a 10 percent click rate at one company will hit 50 percent at another, and the only real difference is whether the culture supports taking two extra seconds to confirm something.
Practical Steps You Can Take Right Now
Start by mapping your organization's communication patterns. What does an internal IT email look like? What does a vendor follow-up look like? What does your CEO's messaging style look like? Attackers do this research anyway. Having an honest inventory of your own patterns means you can spot when something deviates from them. Implement a single, frictionless verification channel. One phone number. One chat bot. One email address that anyone can use to confirm suspicious messages. The barrier to verifying should be lower than the barrier to acting. I've seen companies get this backwards and spend months trying to improve click rates when the real issue was that verifying a message required opening a ticket and waiting four hours. Run regular simulations that include debriefs, not just scorecards. A click rate number tells you nothing about why someone clicked. A conversation with them afterward tells you exactly what emotional trigger the message hit. I usually spend more time on the debrief than on the campaign itself. That's where the actual improvement happens.
Train people to recognize the emotional manipulation, not just the technical indicators. A misspelled domain is a red flag, but most professional attacks don't have those anymore. What they do have is a carefully calibrated emotional hook. Teaching people to notice when they feel pressured, flattered, confused, or obligated is more valuable than teaching them to spot typos.
A Workaround I Developed for Persistent Edge Cases
There was a group of employees at one organization who kept clicking through simulated phishing emails despite multiple training sessions. Standard approaches weren't working. What finally moved the needle was assigning them a specific role: they became part of the security awareness team, responsible for reviewing and reporting suspicious emails alongside the IT department. Giving them ownership changed their relationship to the material entirely. Their click rate dropped to near zero within two months, and they started catching real phishing attempts that others missed. This approach isn't a silver bullet. It works for motivated people in the right environment, but it won't fix a culture that punishes mistakes. If your organization treats security incidents as performance problems rather than learning opportunities, no amount of role assignment will help. The fundamental issue has to be addressed at the leadership level first.
When Social Engineering Defense Actually Fails
The honest truth is that you cannot train your way out of sophisticated social engineering. Professional attackers have time, resources, and research capabilities that no internal security team can match on a per-target basis. When someone is willing to spend weeks building a detailed profile of a single employee using LinkedIn, conference appearances, and public filings, no amount of annual training will make that person immune. What you can do is make the cost of targeting your organization higher than the cost of targeting easier victims. This means reducing the amount of publicly available information about your staff, limiting what people share on professional networks, and implementing technical controls that reduce the impact even when someone does fall for an attack. Layered defense is the only realistic strategy. Technical controls like link checking, sandboxing, and endpoint detection matter more than most people give them credit for. A well-configured URL rewrite policy can block 90 percent of phishing attempts before a human ever sees them. A good sandbox can detonate a malicious payload without it ever reaching the network. These aren't replacements for training. They're the safety net that catches what training misses, and they consistently catch far more than training does.
The field moves fast. New manipulation techniques emerge regularly, and the tools that attackers use are becoming more automated and accessible. The psychology doesn't change as quickly, but the applications do. Staying current means paying attention to what's working in the wild, not just what's in the textbooks. I find that following actual breach reports and post-mortems from other organizations is more educational than any course I've taken. One thing I still come back to: the people who are most vulnerable to social engineering are often the most helpful ones. The person who wants to assist, who doesn't want to be difficult, who takes pride in being responsive. These are good qualities in an employee. They're also exactly what attackers look for. The solution isn't to make people less helpful. It's to make helpfulness and verification compatible.
Building a Realistic Defense Strategy
Prioritize reducing your external information footprint. This is the single highest-impact, lowest-cost action most organizations can take. If attackers can't build a profile, they can't personalize their approach. Limit what employees post about their roles, projects, and internal tools. Restrict access to organizational charts and directory information. These steps alone reduce the effectiveness of a significant portion of targeted attacks. Invest in continuous, adaptive training rather than annual compliance modules. The brain stops noticing what it expects to see. A training program that looks the same every year becomes background noise. Rotate the scenarios, vary the attack vectors, and make the exercises relevant to each team's actual work. Finance teams need different examples than engineering teams, and both need different examples than HR. Accept that some percentage of your people will click. It will happen. The question isn't whether it happens. It's how quickly you detect it, how thoroughly you investigate it, and how effectively you use the intelligence you gain from it. Every successful phishing attempt contains information about what worked. Treat that as data, not as a failure.
The psychology behind social engineering attacks is well understood. The challenge is applying that understanding in a way that accounts for real human behavior under real organizational pressure. Tools and frameworks help, but they only go so far. The people who build the most resilient defenses are the ones who understand both the manipulation tactics and the environment that makes them effective.


