Why Most QMS Risk Assessments Are Pointless
I've spent too many years watching companies produce risk assessment documents that look professional on paper but fall apart the moment anything actually goes wrong. A QMS Risk Assessment Example should reflect reality, not some template someone downloaded from a consultant's website. The core problem most people have is they treat risk assessment as a paperwork exercise rather than a working tool. You need to understand the actual mechanism before you fill in boxes.
Building a Real QMS Risk Assessment Example
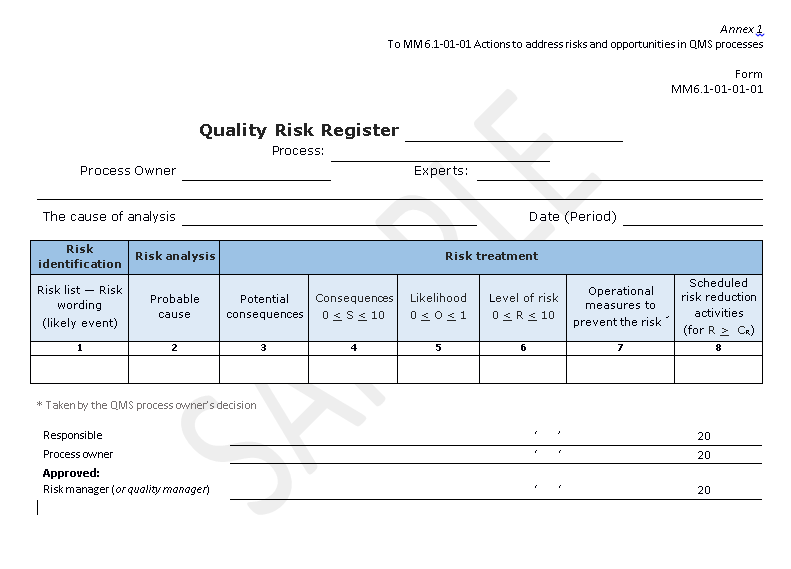
Here's how the process actually works in practice. You start by identifying your processes, not your risks. That might sound backwards but it matters. If you start with risks, you'll end up with a generic list that has nothing to do with what your QMS actually does day to day. My approach is to walk through each process step and ask what could go wrong at that specific point. I map it to a risk register that tracks likelihood, severity, and detection capability. The standard FMEA method works fine for this. You calculate the RPN by multiplying those three factors. But here's what most people miss. The RPN number itself is almost useless on its own. What matters is the prioritization it creates. A risk with an RPN of 72 isn't necessarily more important than one with an RPN of 64. Context matters more than the arithmetic. I learned this the hard way about four years ago with a medical device client.
We had a component that failed at a rate of less than 0.1 percent. The risk assessment scored it as medium priority because the severity was high. Management decided to invest heavily in redesigning the part. Two years later, we caught that the detection method was fundamentally flawed. The test catching the failures had a 40 percent miss rate. The real risk was far lower than the assessment suggested because our detection was unreliable, not our manufacturing. We had been optimizing for the wrong variable. That cost us roughly 18 months of engineering time and about 200,000 in redesign work that we didn't need to do. After that, I started documenting detection method validation alongside every risk assessment. It took an extra half hour per process step but saved weeks during audits. Your QMS Risk Assessment Example should include evidence that your detection methods actually work, not just a checkbox saying they do.
Get the Full Details
What the Standards Actually Require
ISO 9001:2015 section 6.1 is where the risk requirements live. It doesn't prescribe a specific methodology. It says you need to determine risks and opportunities and plan actions to address them. That's it. ISO 14971 for medical devices is more detailed but follows the same logic. The common pitfall is treating ISO 9001's vague language as an invitation to invent something overly complex. You don't need a custom methodology. You need a process that produces defensible decisions. Auditors can see through elaborate frameworks built to impress. They cannot ignore simple assessments that clearly influenced actual decisions. Here's a practical example that covers most situations. You identify a process step like incoming inspection of raw materials. The risk is receiving nonconforming material. The cause could be a supplier quality issue or a specification change that wasn't communicated. The effect is potential product nonconformity. Your current controls include supplier approval and certificate of analysis verification. You score likelihood as 3, severity as 4, detection as 5. Your RPN is 60. You decide this is acceptable with no additional action because your supplier qualification process includes on-site audits every two years.
That's the kind of straightforward assessment that holds up under scrutiny. It's not glamorous. It doesn't have fancy color-coded heat maps. But it shows clear thinking and reasonable conclusions.
Downloadable Template Structure
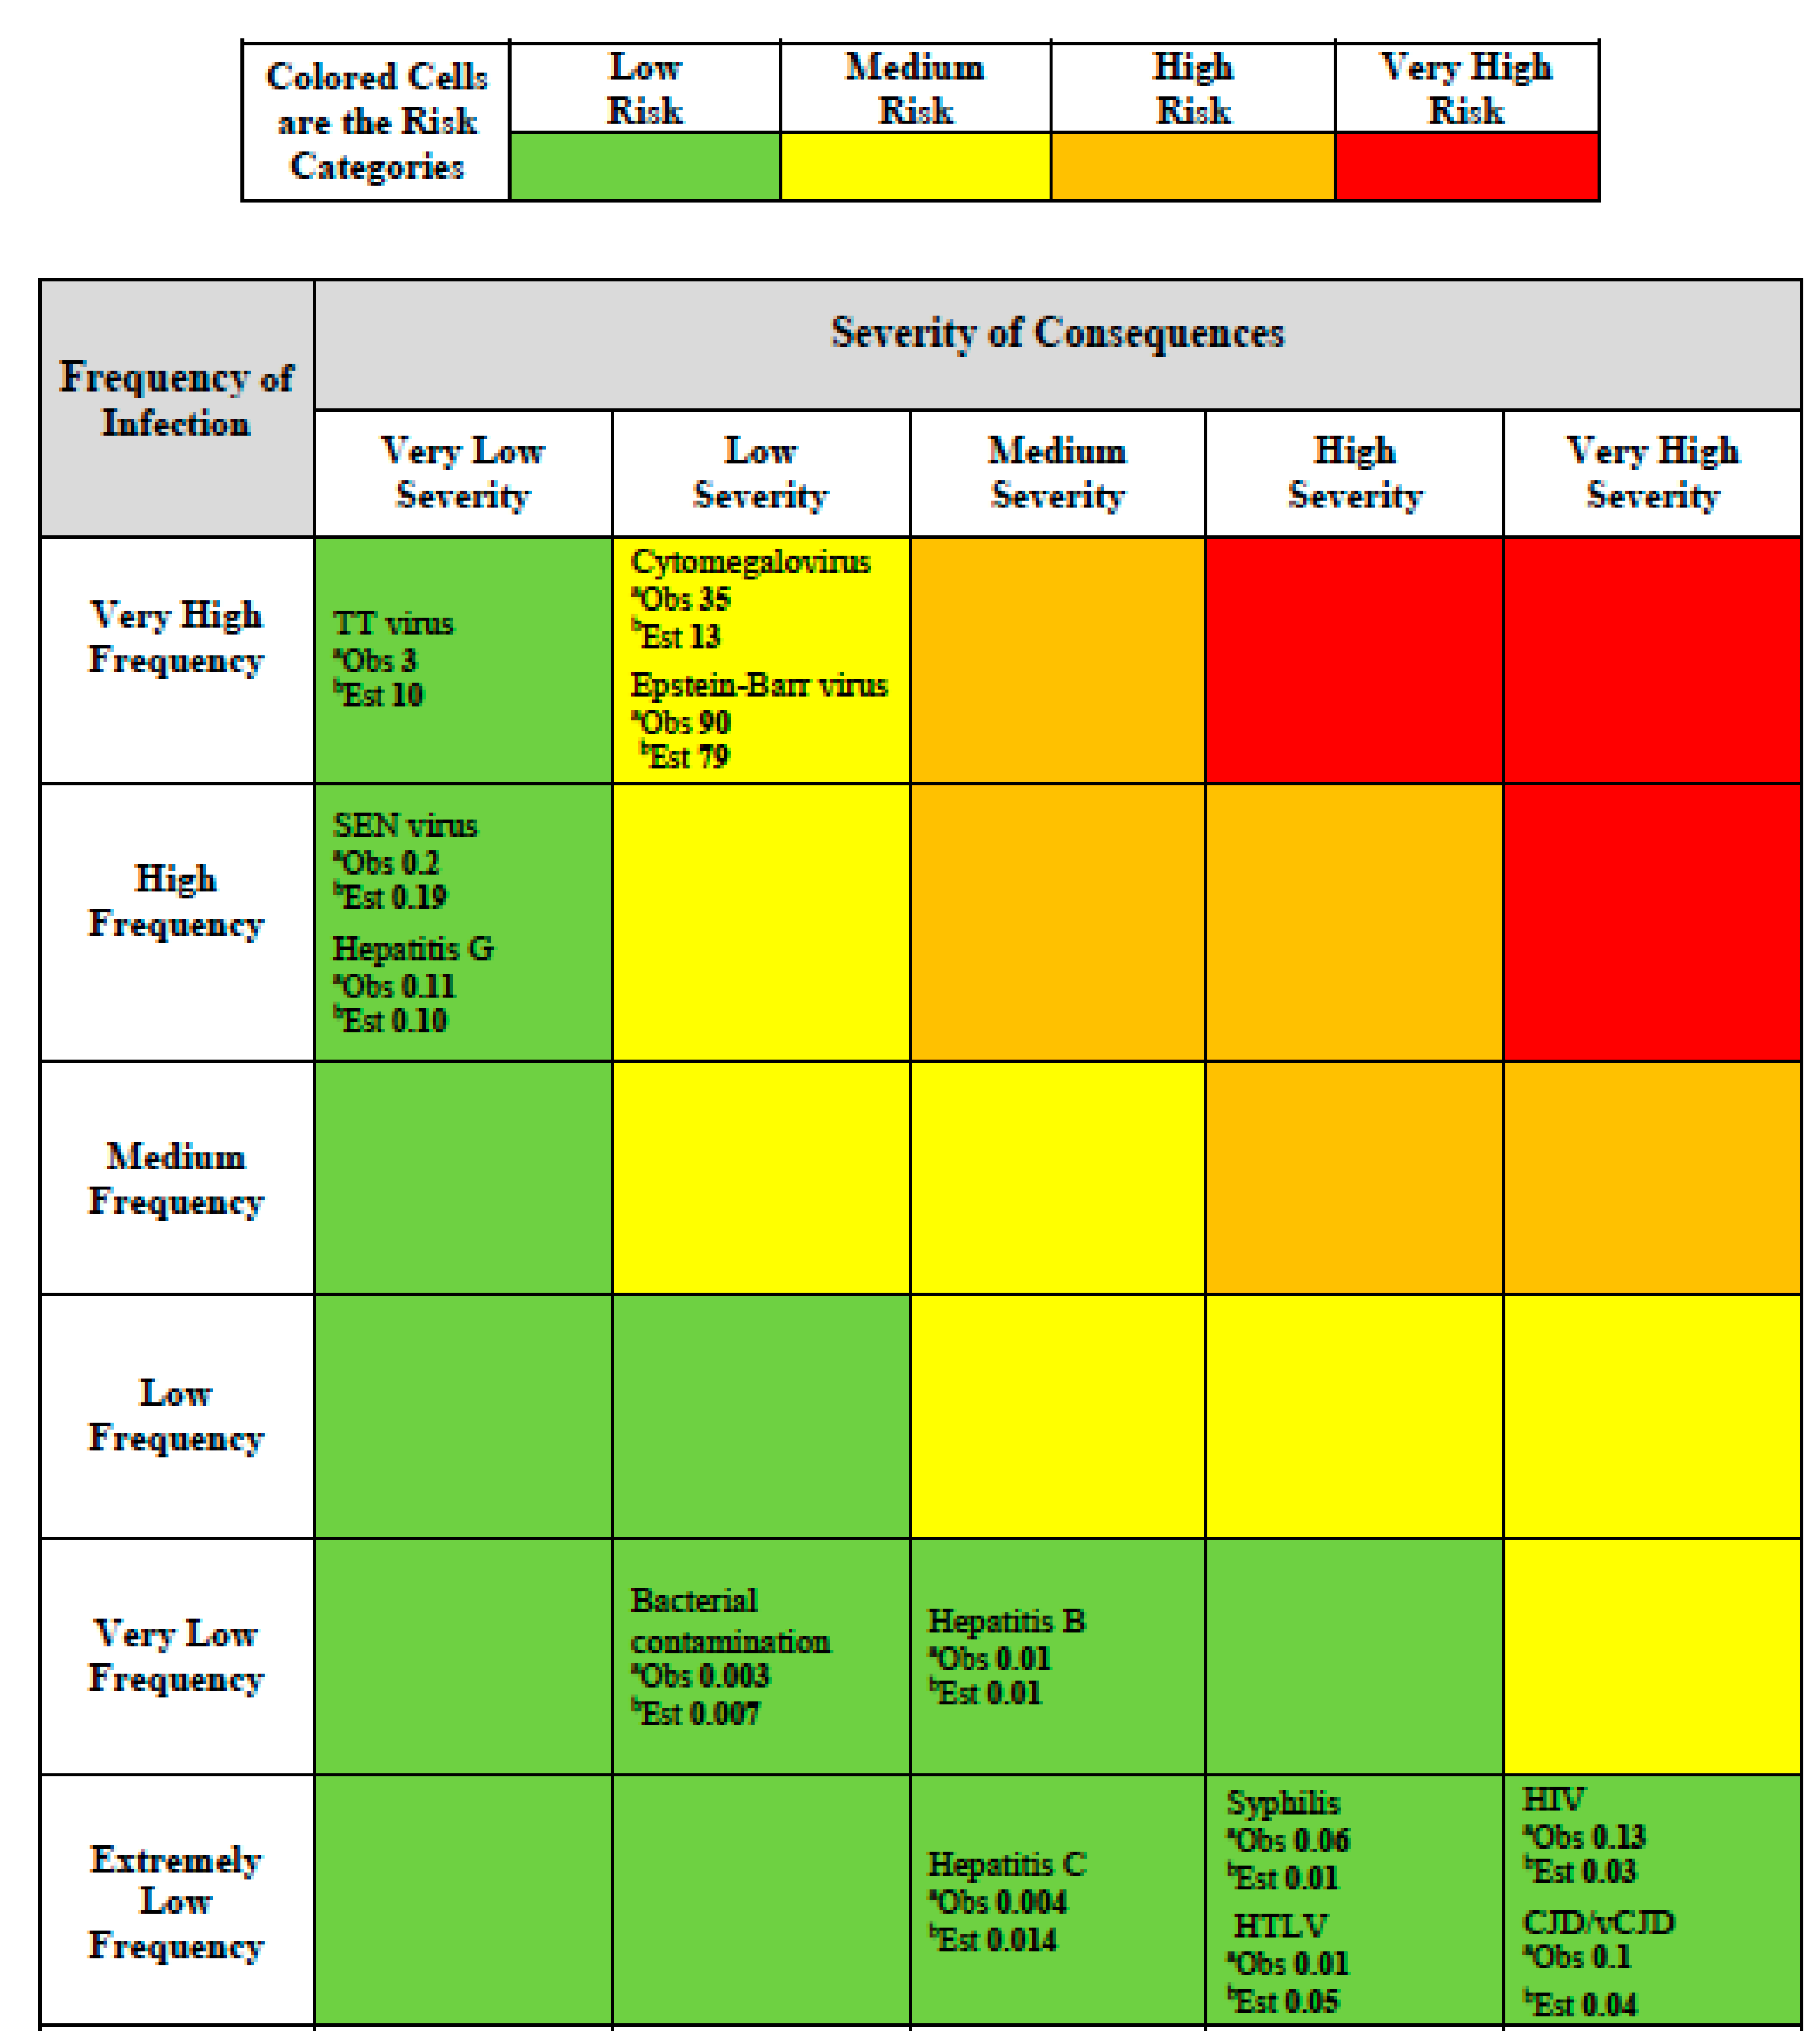
I put together a basic template that follows this logic without adding unnecessary complexity. It covers process identification, risk causes, potential effects, existing controls, scoring criteria, and action tracking. You can adapt it to your industry standards. The file is structured for Excel compatibility so you can link calculations without introducing macros that will break in five years. The template includes a scoring guide that prevents the common inflation problem where everyone rates their risks as medium. I've seen organizations where 85 percent of identified risks were scored as medium likelihood. That's not a risk assessment. That's a wish list.
When Risk Assessment Breaks Down Completely
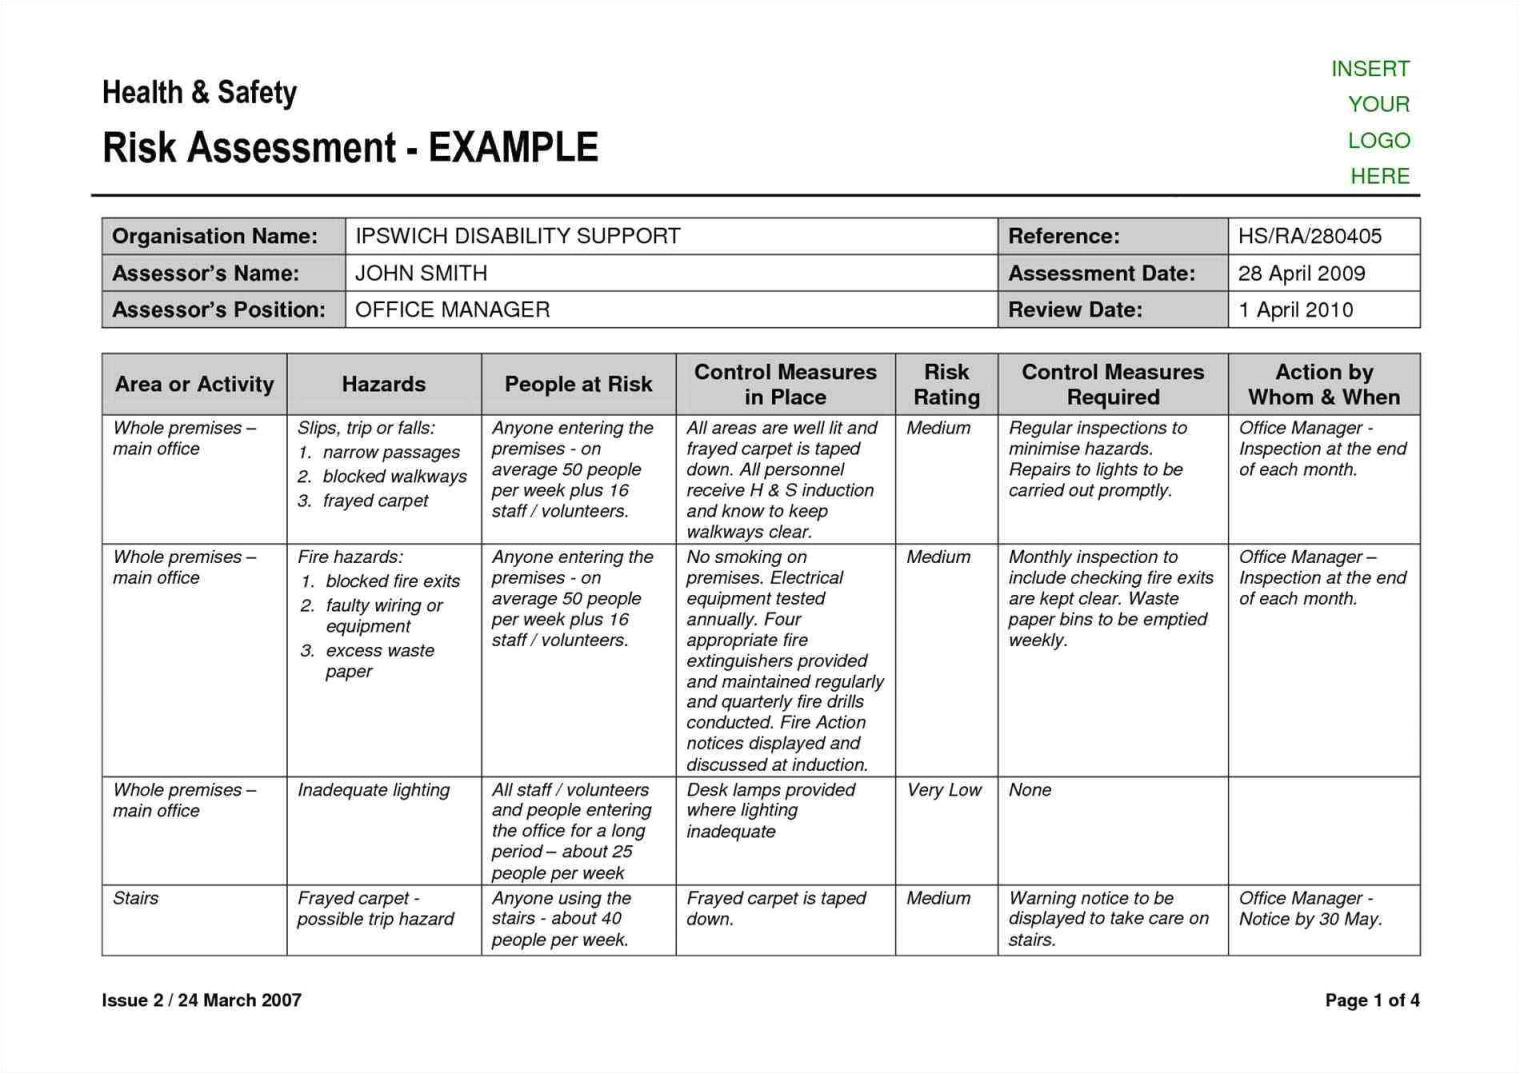
I should mention honestly where this approach fails. Risk assessment is terrible at capturing systemic or emergent risks. It works well for known failure modes in controlled processes. It does not work for supply chain cascading failures, regulatory changes, or organizational culture problems. During the 2021 chip shortage, every risk assessment in the automotive industry was worthless because nobody had modeled a global semiconductor supply disruption. The likelihood scores were based on historical data that went back maybe five years. The actual event had a frequency measured in decades. If your QMS depends entirely on traditional risk assessment, you'll be caught flat-footed by black swan events. I supplement the formal register with a separate scenario planning exercise for high-impact low-probability events. It takes about two hours quarterly with the right stakeholders. It won't predict the next crisis but it builds organizational awareness that makes response faster when things go wrong. The scoring system also breaks down when severity and likelihood are poorly defined. If your severity scale has five levels but your team interprets level 3 as everything from a minor inconvenience to a regulatory violation, your numbers mean nothing. I've found that spending one afternoon aligning definitions across the team prevents more audit findings than any amount of template refinement. You should do this exercise before you start filling in rows, not after you've completed three cycles and discovered everyone was scoring differently.
A proper QMS Risk Assessment Example demonstrates thinking, not compliance theater. The best assessments I've ever reviewed were the ones where an auditor could trace a specific risk decision to a concrete business action that was actually taken. That's the standard you should hold yourself to.