Why Your Risk Assessment Looks Great on Paper and Fails in Practice
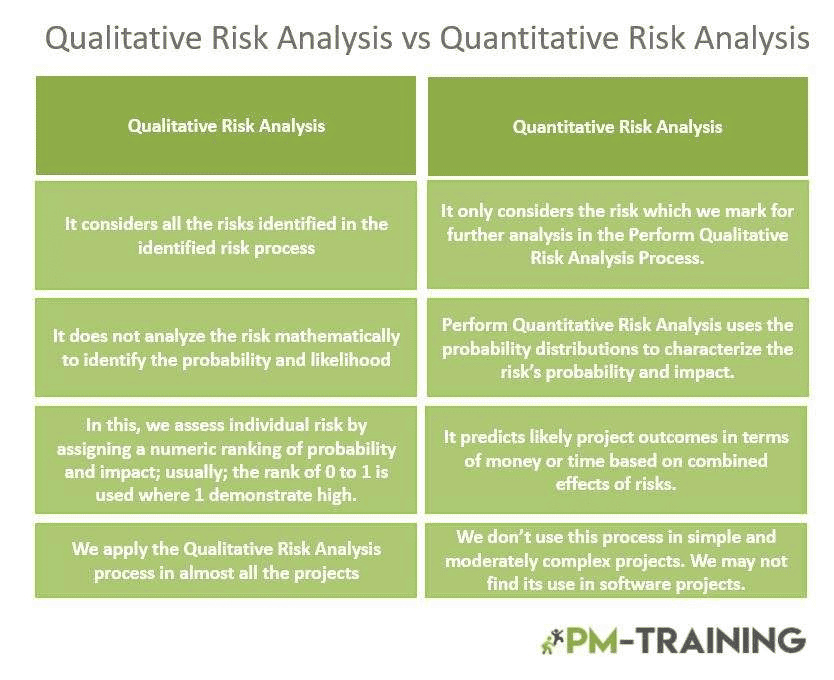
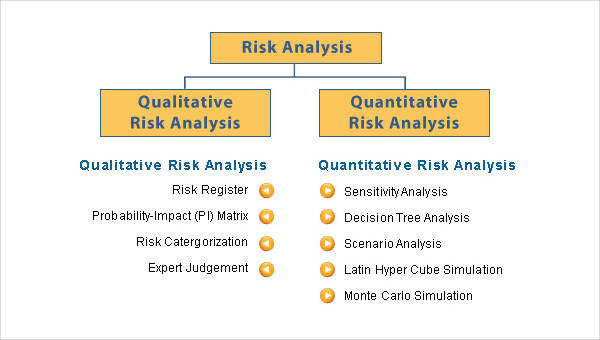
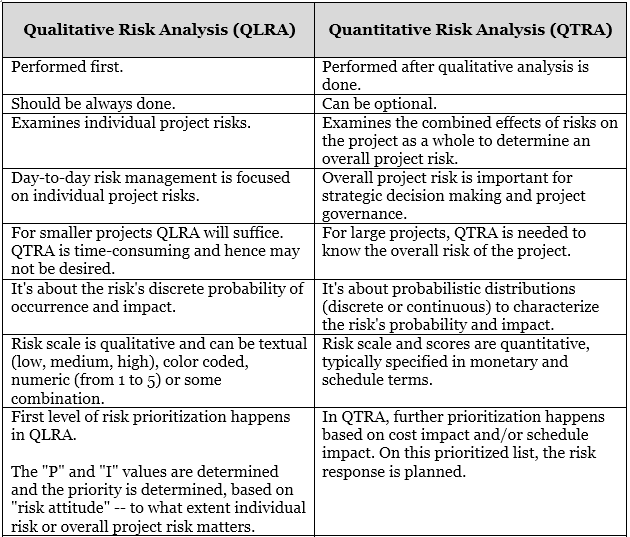
I spent about six years doing risk assessments for financial institutions before I stopped pretending that either approach was sufficient on its own. The industry loves to frame this as a choice between two camps. It isn't. Both methods have serious blind spots that become obvious the moment you try to use them in a real incident. The qualitative side is what most teams reach for first because it requires almost nothing upfront. You grab a handful of subject matter experts, run through your risk register, and score each item on a five-by-five matrix. Probability as low to catastrophic. Impact as negligible to business-ending. You land somewhere in the middle, label it amber, and move on. This takes roughly two to three hours for a standard assessment cycle. It feels productive because everyone in the room agrees on the output, which is rarely the same thing as the output being correct. The quantitative side sounds more rigorous until you actually try to populate it. You need historical loss data, failure rates, mean time to recovery numbers, and exposure values that rarely exist in the clean form you need them. A single vulnerability assessment that should take a morning stretches into three weeks of data wrangling before you have enough to run even a basic Monte Carlo simulation. The output looks impressive though. Dollar figures. Confidence intervals. Numbers that make budget meetings slightly less painful.
Quantitative Vs Qualitative Risk Assessment: What Actually Happens When You Apply Them
Here is the part nobody puts in the textbooks. Qualitative scoring suffers from anchoring bias and groupthink. The loudest person in the room sets the anchor, and everyone else drifts toward their estimate. I have watched a team consensus a 7 out of 25 risk rating on a vulnerability that independent penetration testing later showed could lead to a full domain compromise. The people in that room had never actually seen that class of exploit in production. They were scoring based on how it sounded in a meeting. Quantitative analysis has a different problem. Garbage in, garbage out applies with maximum cruelty here. I worked on an assessment for a mid-market healthcare provider where the team pulled annual loss expectancy figures from an insurance industry benchmark report rather than internal data. The report was from 2018 and covered a fundamentally different threat landscape. The resulting quantitative model recommended investing nearly two million dollars in controls that addressed threats which had already migrated to ransomware-as-a-service infrastructure. The numbers were internally consistent. They were completely wrong for the organization's actual situation. Both approaches also share a structural weakness that most practitioners ignore. They treat risk as static. You run your assessment, you get your scores, and then you file the document until the next review cycle. Threats do not respect your fiscal year. A new CVE drops on a Tuesday. By Thursday your top five risks look different. By Friday the executive team is asking why the remediation budget has not moved on the items from last quarter.
The workaround I settled on after burning through two assessment cycles on a cloud migration project was to treat qualitative and quantitative as sequential layers rather than alternatives. Start with a rapid qualitative sweep to identify the twenty percent of risks that account for eighty percent of the exposure. Then apply quantitative methods only to those items. This cut my assessment time from about fourteen hours down to roughly three and a half hours for a typical engagement while still producing dollar-figured outputs for the risks that actually mattered to leadership. For the qualitative phase I use a structured technique called Delphi instead of a group meeting. You send the risk scenarios out to three to five independent reviewers with anonymous scoring. They get the group medians back and rescore. After two rounds the variance drops significantly because the social dynamics of a conference room no longer skew the results. This alone fixes about half the problems I saw with traditional qualitative approaches. For the quantitative phase the biggest shortcut most people miss is that you do not need perfect data. Expected value calculations and FAIR-style models can work with bounded estimates. Instead of trying to find the exact probability of a control failure, you define a reasonable range. Low, most likely, high. Run a simple triangular distribution. The output will have wider confidence intervals than a model fed pristine data, but it will be directionally accurate and it will be defensible in a boardroom. A properly scoped quantitative analysis with estimated inputs typically produces results within twenty to thirty percent of actual observed losses over a twelve-month period. That is good enough for resource allocation decisions that involve millions of dollars.
Get the Full Details

There are scenarios where neither method works well. Highly novel threats with zero historical precedent and no reasonable analogue fall into this category. The 2021 Colonial Pipeline incident is a clean example. Traditional risk assessment frameworks struggled to price that event because the attack vector combined supply chain dependencies, geopolitical factors, and operational technology vulnerabilities in a way that no prior dataset captured. When you encounter this situation the honest answer is to run scenario-based stress tests rather than pretend your risk matrix can handle it. Build plausible narratives. Estimate the financial and operational impact of each. This is closer to intelligence-driven planning than risk assessment in the traditional sense. Another common failure point is organizations that treat their risk register as a compliance artifact rather than a decision-making tool. I have seen teams generate elaborate quantitative models that were referenced exactly once during the fiscal year budget process and then ignored until the next audit cycle. No amount of methodological sophistication fixes a broken governance workflow. If the output of your risk assessment does not influence spending, staffing, or prioritization decisions, you have not done risk assessment. You have done performance art. The practical takeaway is straightforward and unglamorous. Run a quick qualitative filter to identify what matters. Apply quantitative analysis only to those items using bounded estimates when exact data does not exist. Review and update continuously rather than on a calendar schedule. Accept that both approaches will produce errors and build that uncertainty into your planning. The goal is not perfect risk measurement. It is better resource allocation than you would have achieved by guessing.