.png)
So You Need To Deal With Regulatory Changes In The Financial Services Industry
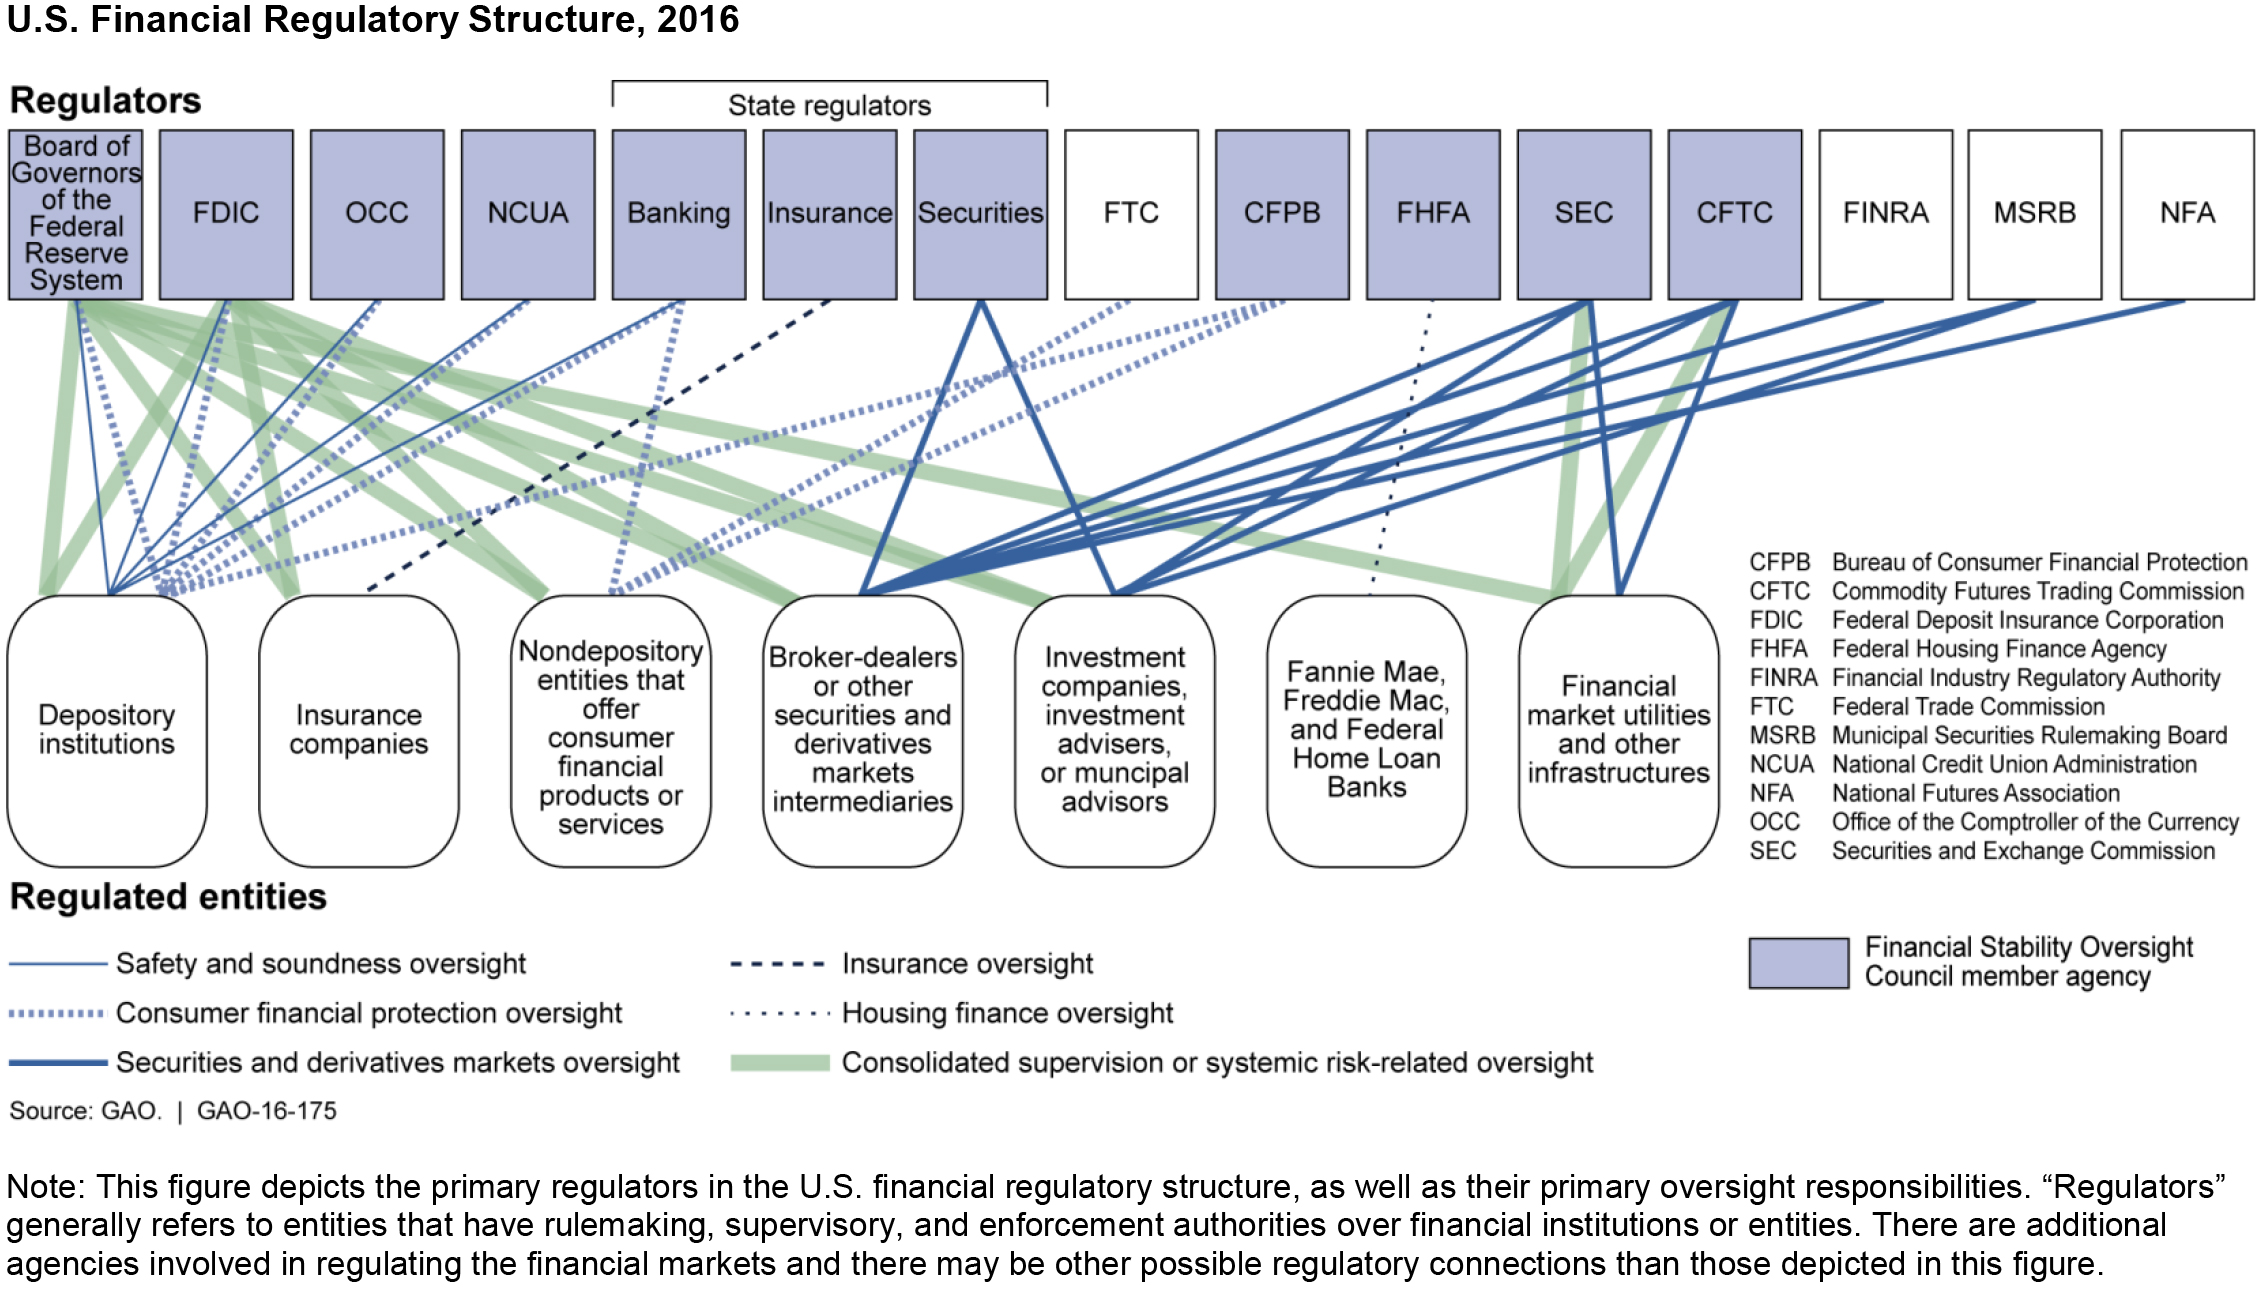
The last compliance cycle is always worse than the one before it. I have been tracking these shifts since 2015, and the pattern never really changes even though the acronyms do. You get the new rules, you assess impact, you patch systems, you pray the regulator does not ask for a second round of evidence. Here is how it actually works when you are the one responsible for making sure the business stays on the right side of whatever changed. Regulatory changes do not arrive as a single document you can read cover to cover. They come through trade publications, regulator newsletters, draft consultation papers that later become binding, and sometimes through press releases that hint at direction before any formal text exists. The first step is establishing a reliable monitoring pipeline. I subscribe to the FCA, SEC, and CFTC policy feeds, but more importantly I track the consultative comment periods because that is where you can still influence outcomes rather than just reacting to them later. A regulatory change might touch capital requirements, consumer disclosure rules, anti-money laundering thresholds, data retention standards, or operational resilience expectations. Each domain has different implementation timelines and different enforcement priorities. Knowing which domain your organization falls under is the actual first task. A retail bank and a crypto custody provider might face overlapping rules but with completely different materiality assessments.
The Practical Workflow for Compliance
Once a change lands, you need a gap analysis. This means mapping current state against the new requirement. I use a structured template rather than ad hoc notes because when the exam happens you need to demonstrate that every requirement was considered, not just the ones that seemed relevant. The template has columns for: regulatory citation, current practice, gap identification, remediation action, owner, target date, and evidence of completion. After the gap analysis, you prioritize by risk exposure and regulatory scrutiny likelihood. A rule about marketing disclosures for retirement products will get more attention from both your legal team and regulators than an obscure recordkeeping amendment. I recommend scoring each requirement on two axes: enforcement probability and business impact. This gives you a rough ranking without needing perfect data, which you never have at this stage anyway. Implementation itself varies wildly by department. Engineering teams handle system updates. Operations handles process documentation. Legal and compliance review contractual language. Training departments handle employee notification. The coordination cost is where most projects run over budget. A single regulatory change typically requires 3 to 5 cross-functional workstreams, and each one has its own timeline that does not align with the others.
A Real Problem I Encountered
During the transition to the new operational resilience framework, my organization had to demonstrate that our critical business services could survive and recover within defined time thresholds. The rule required impact assessments for each service, and we were supposed to identify all dependencies including third-party providers. Our core banking system was straightforward to map. The problem came with a legacy fraud detection tool running on an unsupported operating system that three different departments used but nobody considered part of the same dependency chain. We discovered it two weeks before our submission deadline because the infrastructure team asked about capacity planning for an unrelated request. By that point, upgrading the environment would have required a regulatory exemption. The workaround involved documenting the system under an exception clause for historically significant but lower-volume services, providing manual contingency procedures, and committing to a phase-out plan within twelve months. We submitted the documentation with the exception clearly flagged. The examiner accepted it but noted it for follow-up, which is about as good as you can expect in that situation.
Get the Full Details
Common Pitfalls That Waste Time
The biggest mistake I see organizations make is treating regulatory changes as purely legal problems. They send the rule to compliance and wait for guidance. But regulatory changes almost always require engineering, operations, and sometimes product changes. Starting with only the legal team delays the entire process by weeks. Another pitfall is incomplete traceability. Examiners will ask for evidence that you addressed every paragraph of a new rule. If you skipped a paragraph because it did not seem applicable, you need to document why. I have seen teams fail audits because they could not produce a written rationale for excluding a requirement, even though their reasoning was technically correct. The absence of documentation is worse than admitting you missed something. Data fragmentation is also a persistent issue. Regulatory changes often require reporting or monitoring that spans multiple systems. A single customer might have accounts in four different platforms. Reconciling data across those platforms to satisfy a new reporting requirement is where most implementation delays happen. I recommend building a data lineage map before the change arrives, not after. This takes effort but saves far more later.
Advanced Considerations
Most people miss the secondary effects of regulatory changes. When a new rule affects one part of the business, it often creates unintended consequences elsewhere. A capital requirement change might push a lending division to shift products into a different regulatory category, which then triggers disclosure obligations you did not anticipate. I always run a cross-impact check after the initial assessment, even if it feels redundant. There is also the issue of regulatory arbitrage risk. Sometimes competitors interpret the same rule differently and gain an advantage by taking a more aggressive stance. You need to decide whether to follow the strictest interpretation or negotiate with your regulator on your reading. This is not a decision to make lightly. I recommend consulting with external counsel before deviating from the conservative interpretation unless there is a clear commercial imperative. The monitoring phase after implementation is often neglected. Rules get implemented but nobody tracks whether the new controls are actually being followed in daily operations. Internal audit should be involved early in the cycle, not brought in after go-live. A quarterly review cadence during the first year after implementation is standard practice for anything above a minor regulatory update.
When It Does Not Work
Not every regulatory change can be fully addressed within the given timeline. Sometimes the required technology does not exist. Sometimes the interpretation is genuinely ambiguous and no amount of analysis will resolve it. In those cases, the best approach is early and transparent communication with the regulator. Proposing a phased implementation plan with specific milestones is usually better than missing a deadline and hoping nobody notices. Small organizations with limited compliance resources face a particular disadvantage here. They cannot absorb the coordination overhead the way larger firms can. For these teams, outsourcing certain compliance functions to specialized vendors can be effective, but it introduces its own risks around vendor oversight and data governance. The tradeoff is real and needs to be weighed carefully. The regulatory environment itself is unpredictable. A change that seems final today might be revised next quarter based on industry feedback or political pressure. Building flexibility into your implementation plan rather than locking everything into a rigid timeline is prudent. Status reports to leadership should include assumptions and known uncertainties, not just progress percentages.