The thing nobody tells you about regulatory compliance gap analysis
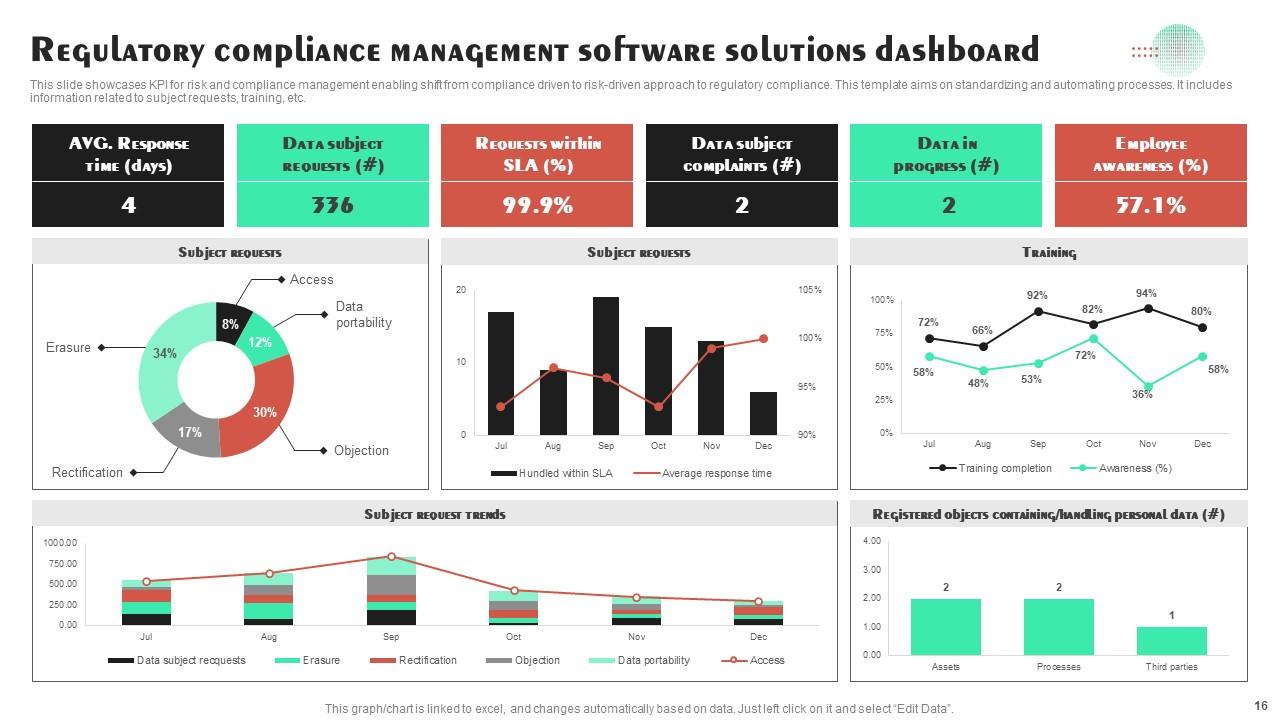
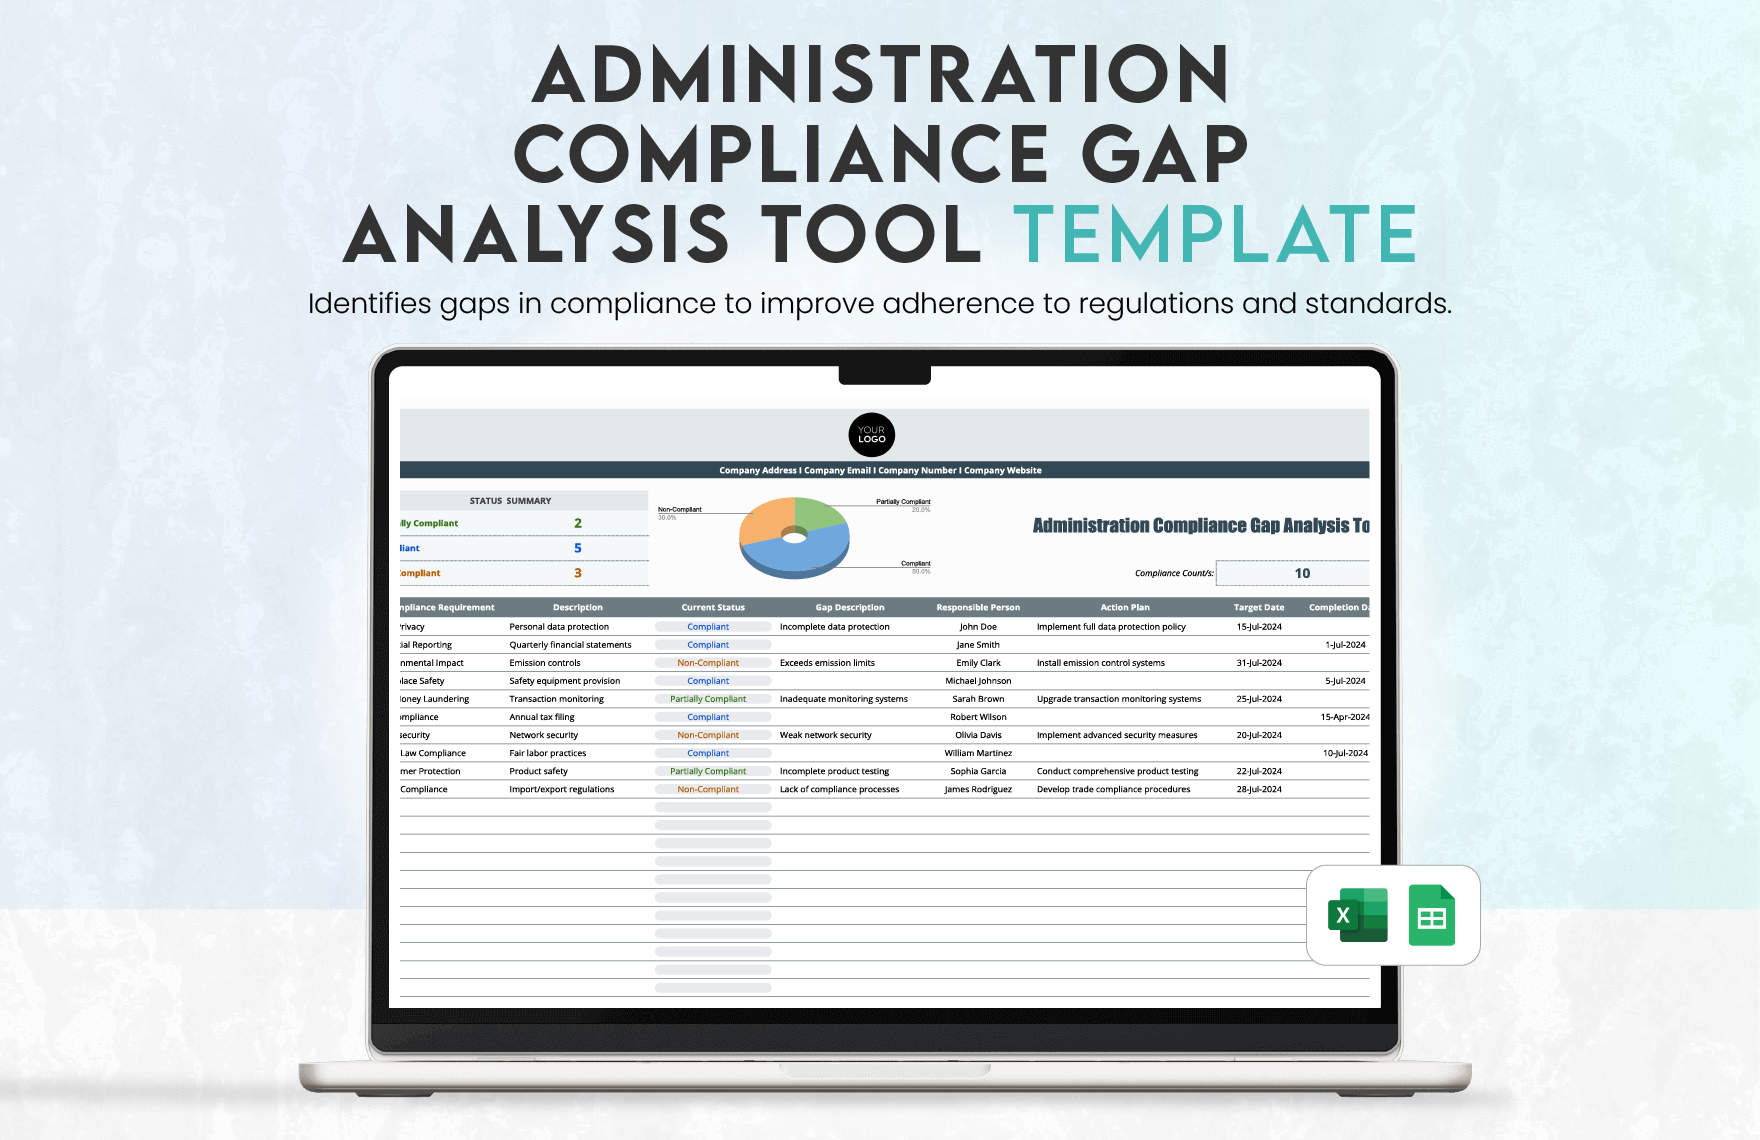
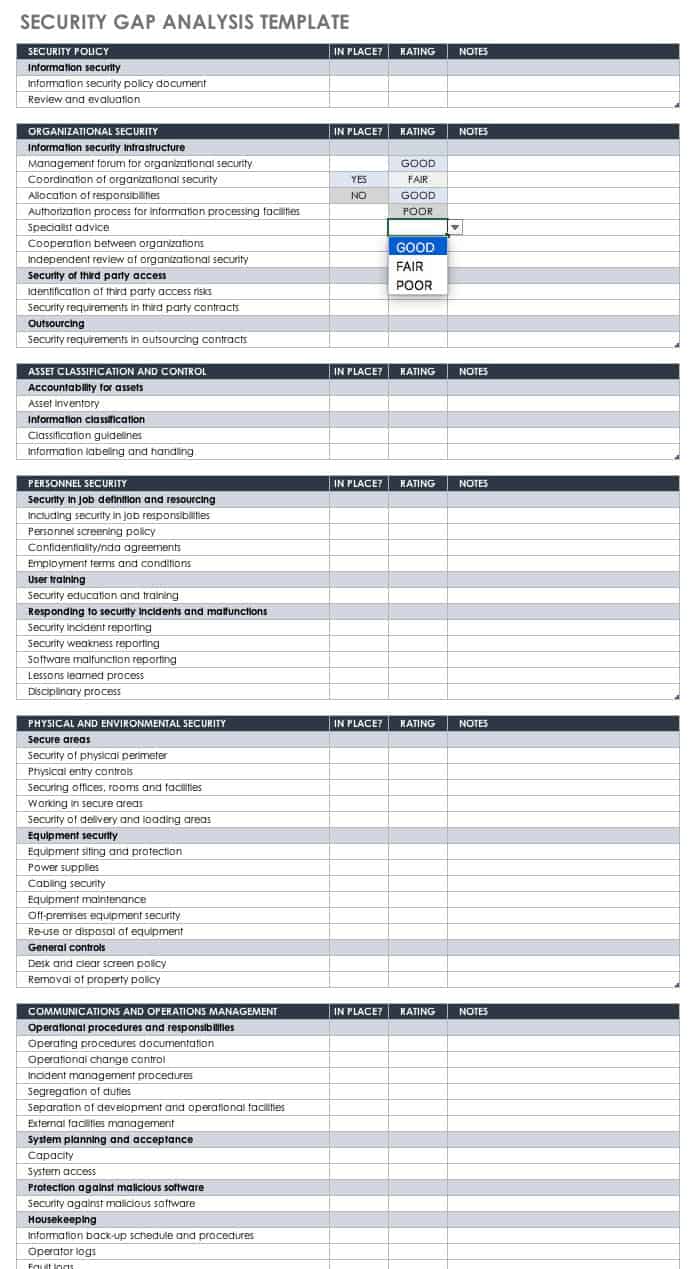
A gap analysis isn't a form you fill out and file. It's an exercise in admitting your current processes don't match the regulatory requirements, which means most teams approach it backwards. They start with the regulation and try to find where they fall short. What actually works is starting from your existing documentation and mapping it against each control point. This flips the problem from a search for missing pieces to a verification of what already exists. Here's the field structure that survives real audits:
Regulatory Compliance Gap Analysis Template
Control ID: A unique identifier tied to the specific regulation clause. Don't use sequential numbers alone. I used "GDPR-49-2" for a specific data processing requirement once, and when the auditor asked for the source, I could trace it back in three seconds. Requirement Description: The exact wording from the regulation, cited with section number. Paraphrasing here is how people lose audits. If the requirement says "data subjects must be informed of processing purposes," that's what goes in this column, not a summary of it. Current State: What you actually have in place right now. Evidence-based. Policy reference, system configuration, or operational procedure. Vague descriptions like "we comply" don't help anyone. Write "Annual security awareness training documented via LMS completion records, last refresh Q3 2024."
Gap Level: Binary is easier. Compliant, Partially Compliant, Non-Compliant. Some frameworks add "Not Applicable" but that field gets misused constantly. I've seen teams mark entire sections N/A because they don't understand the scope of the regulation. One misused N/A entry caught a whole audit off guard at a financial services firm I worked with. They'd marked customer due diligence as N/A because they only dealt with business accounts. Turns out the regulation covered both. Evidence Reference: Link or location of supporting documentation. Policy document name and version, system report URL, log file reference, email confirmation, or screenshot path. Make it findable without asking. Remediation Action: What needs to change, owned by whom, and the target date. This is where most templates die. They capture the gap but produce nothing actionable. An open gap without an owner and a deadline is just a list of problems that never gets solved.
Get the Full Details
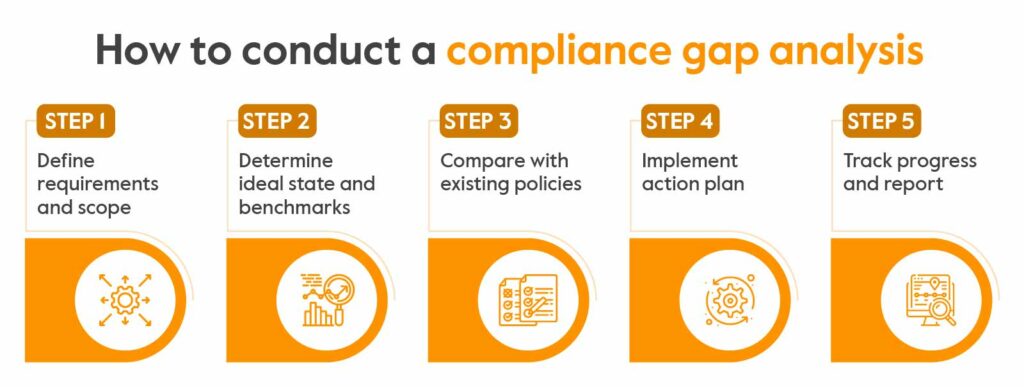
Closure Evidence: When the remediation is complete, what proof confirms it. This field stays blank until it's actually closed. Auditors check this field specifically to see if gaps were marked closed without evidence. Here's how I actually run through a gap analysis, not the theoretical version: First, I pull the full text of every regulation that applies. Not summaries. Not compliance platform interpretations. The actual regulatory text. I keep these in a dedicated folder with version tracking because regulations get amended and nobody tells you about the amendments.
Then I extract every control requirement from those texts and put them in the second column of the spreadsheet. This takes longer than you think. A single regulation like HIPAA has hundreds of implementation specifications across different sections. It's tedious work that pays for itself immediately. Next, I map existing policies, procedures, and system configurations to each requirement. I don't guess. I go to the actual documents. If I can't find evidence for a control, that's a gap, not a suggestion box entry. During a recent SOC 2 type II prep, I spent three hours tracing a single access review control through four different systems before finding out it was documented in three places with inconsistent dates. That inconsistency became the actual gap we had to fix, not a missing policy document. After that, I fill in the gap level for each control. Any control that doesn't have direct, current, evidence-backed coverage gets marked non-compliant. Partial compliance goes here too, but I require a specific reason: what part is covered and what part isn't. "Mostly done" is not a valid reason.
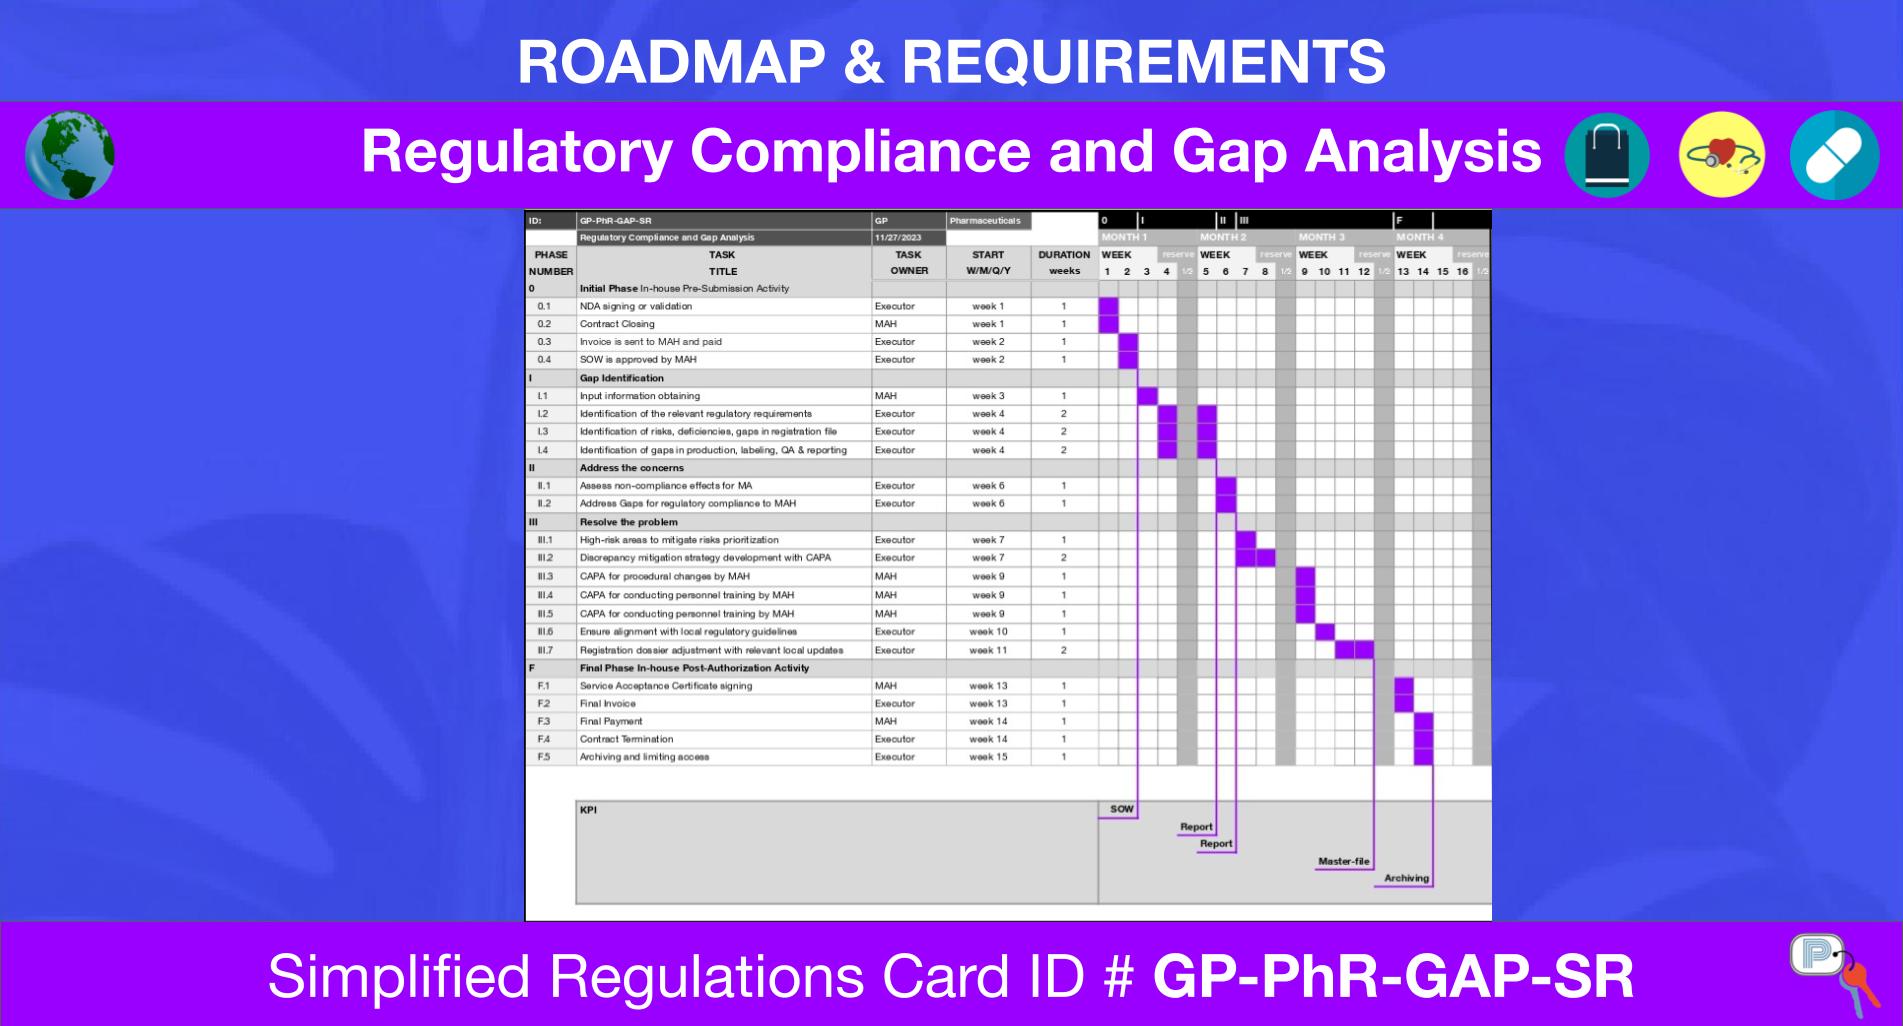
Then the remediation plan. Each gap gets an owner, a target date, and a description of what will bring it into compliance. I recommend setting internal deadlines at least two weeks before the actual audit date. You will need that buffer. Something always comes up on remediation week. I should mention something most template guides skip. The relationship between controls and regulations isn't always one-to-one. One policy can satisfy multiple requirements across different regulations. A data retention policy might cover GDPR, CCPA, and ISO 27001 simultaneously. Building these cross-references into your template saves enormous time during an audit because the auditor asks for evidence and you can point to a single document that covers three requirements. I built a simple tagging system where each control requirement maps to applicable regulations, and the evidence reference links back to the policy document. When an auditor asked for evidence on three different requirements during a recent examination, I pulled one policy reference and showed them how each requirement was satisfied. Took forty-five seconds. Another thing that catches people off guard: evidence freshness matters more than evidence existence. A policy document from 2019 that was never updated doesn't demonstrate compliance with a 2023 regulatory change. I had a client who presented an eleven-year-old information security policy as evidence of compliance with current NIST framework requirements. The auditor flagged every section that referenced outdated standards and required a full policy revision before any compliance claim could be accepted. The gap wasn't the missing policy. The gap was the outdated policy masquerading as current evidence.
Here's where templates fail completely and you should know about it before you rely on one: A spreadsheet-based gap analysis template cannot track regulatory changes in real time. When GDPR was amended or when a new state privacy law passes, your template becomes stale unless someone actively updates it. I've seen organizations maintain gap analysis spreadsheets that were six months out of date by the time the audit started. The template existed but the content was wrong, which is worse than no template at all because it creates false confidence. Another structural limitation: these templates don't handle scope ambiguity well. When you're dealing with regulations that have different applicability thresholds based on company size, data volume, or geographic presence, the template's binary compliant/non-compliant model breaks down. You need a separate determination document that explains why certain requirements don't apply to your organization, and that explanation needs regulatory citation, not opinion.
If your compliance landscape involves multiple regulations with overlapping requirements, a single template becomes unwieldy very quickly. I switched several clients to a control-based framework instead, where each control is defined once and mapped to all applicable regulations. This reduces duplication and makes it easier to see which regulations are already well-covered and which ones have thin compliance coverage. The initial setup takes longer, maybe two to three weeks for a moderate-sized organization, but subsequent audits drop from roughly two weeks of preparation down to about three days of focused verification. The actual template document itself is usually just a structured spreadsheet with those columns I described above. You can build one in Google Sheets or Excel in about twenty minutes. The value isn't in the template format. It's in the discipline of filling it accurately and keeping it current. A perfect template filled with assumptions is useless. A rough template filled with verified evidence and specific remediation plans is audit-ready. If you need a starting point, the basic structure is straightforward. Create the columns I listed above. Populate the requirement column from actual regulatory text. Fill the current state column with verified information from your existing documentation. Leave the remediation and closure fields empty until they have real content. Update the template whenever a regulation changes, a policy is revised, or a gap is closed. That's it. Nothing complicated about the mechanics. The hard part is doing it honestly.