How RCSA Actually Works When You're Not Starting From Scratch
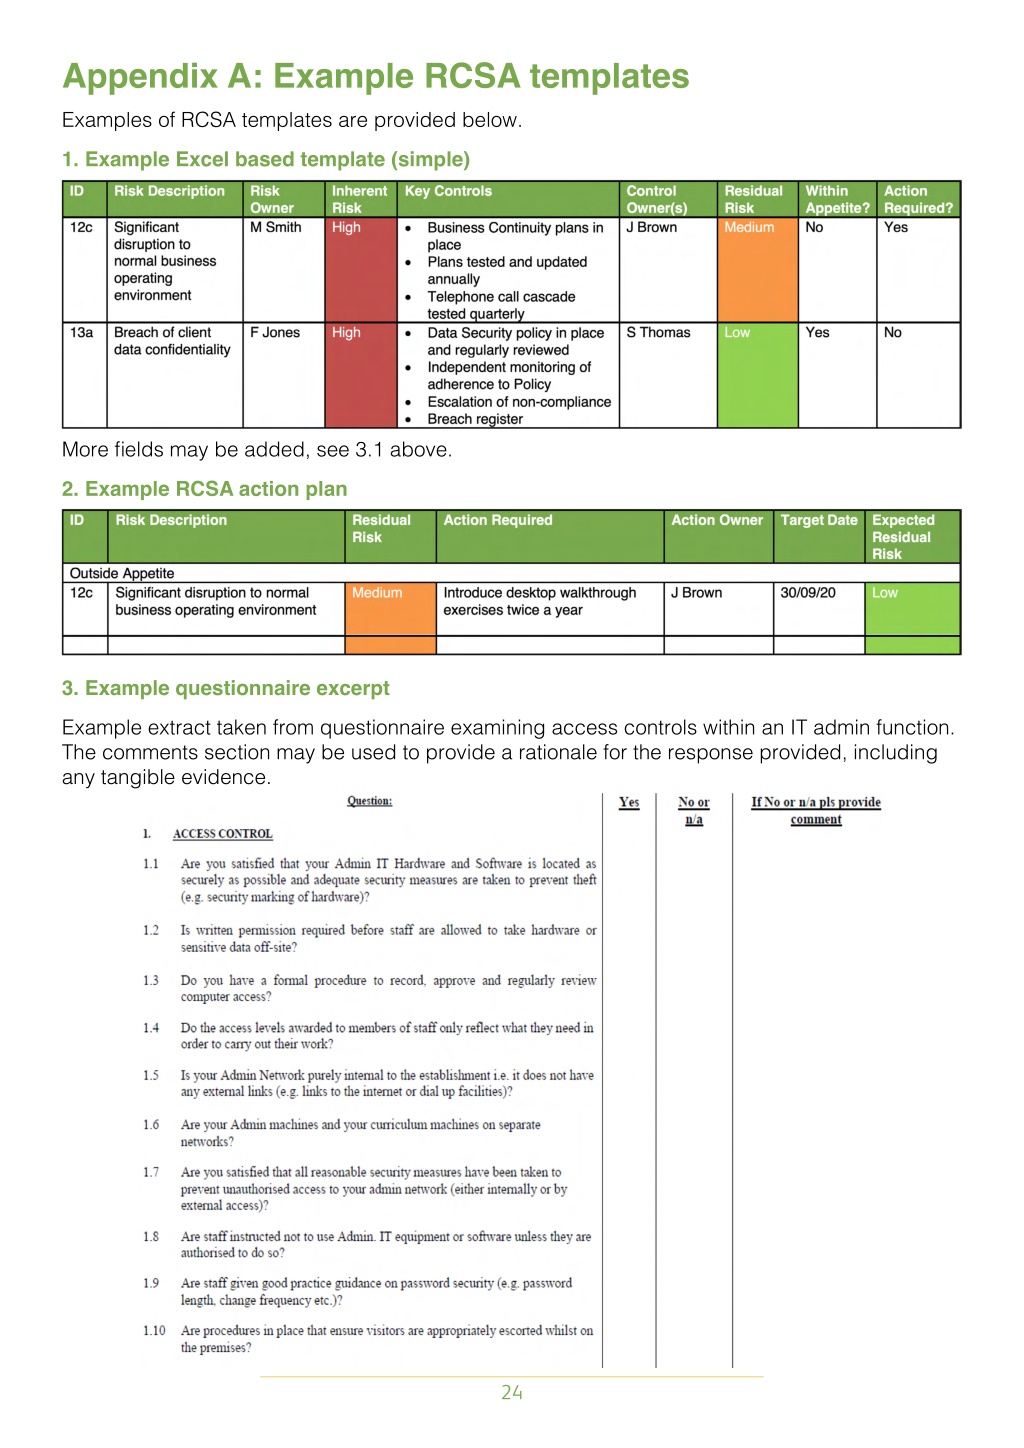
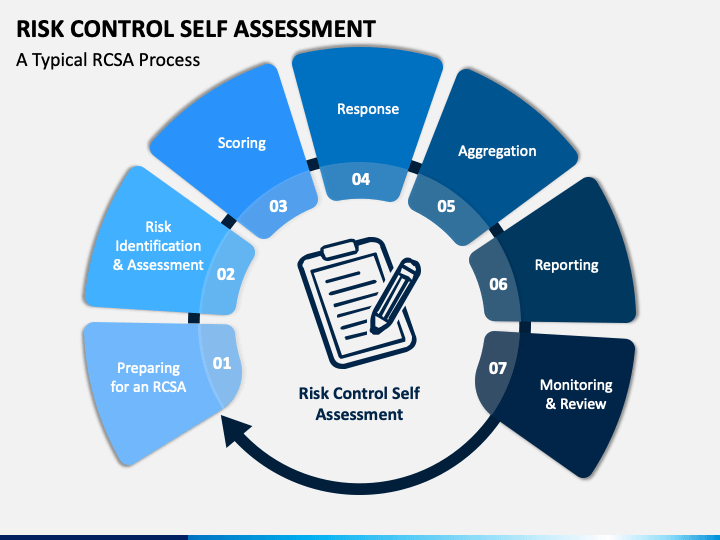
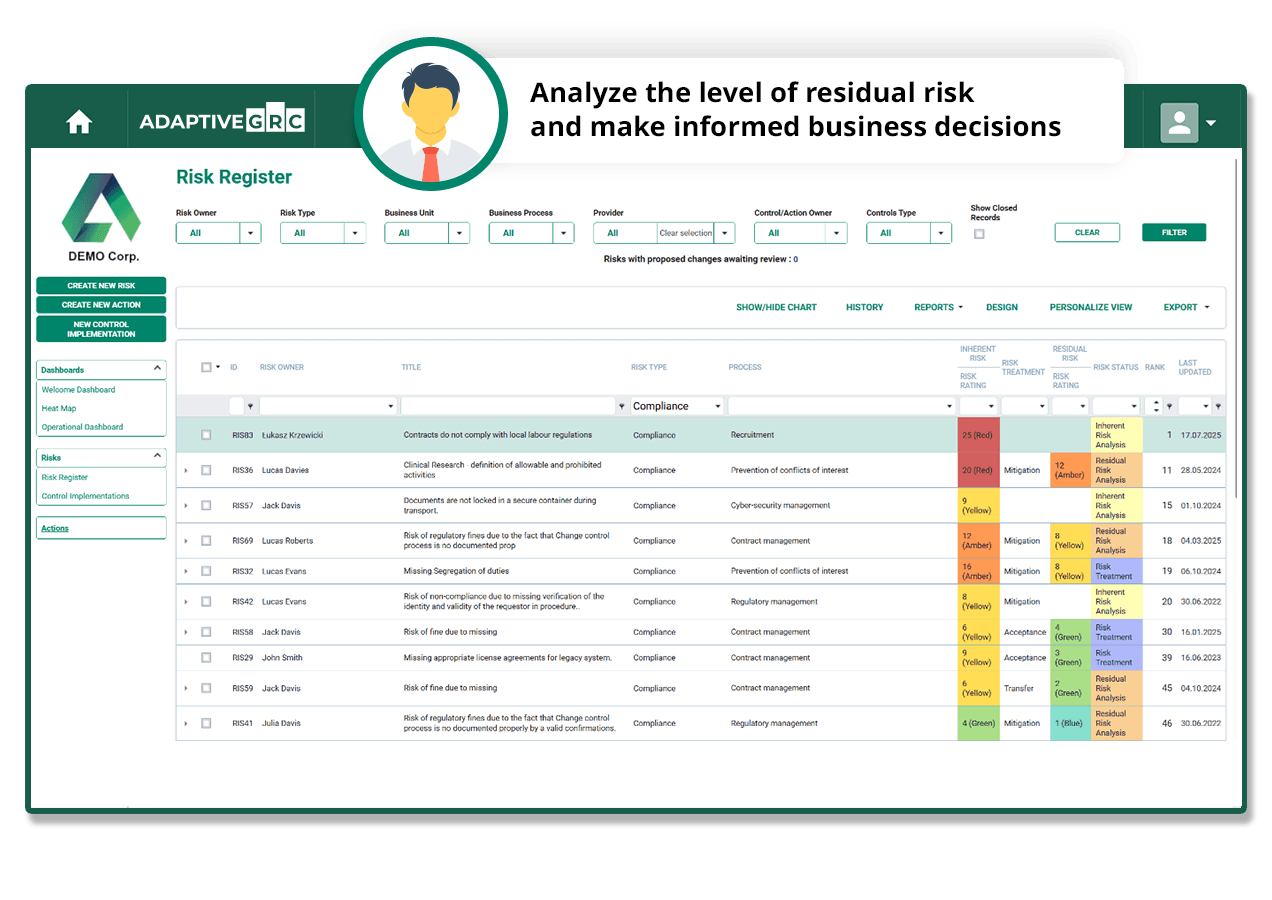
Most people treat Risk and Control Self Assessment Example like it is a compliance checkbox exercise. It is not. It is a process for getting the people closest to your operations to admit where things can go wrong before someone else discovers it. The format varies by organization, but the core mechanic is consistent: you map a process, identify risks within that process, assess existing controls, rate the residual risk, and document gaps. A practical example runs like this. Take a payment processing workflow. The process has five steps: submission, validation, authorization, settlement, and reconciliation. For each step, the control owner identifies two to three risk events. At the validation step, you might flag data integrity errors, duplicate submissions, or bypass of required fields. Each risk event gets a control description, an inherent risk rating, a control effectiveness rating, and a residual risk score. The output is a single row per risk-event pair, aggregated into a process-level heat map. The matrix itself is usually straightforward. Inherent risk on a 1-to-5 scale. Control design effectiveness, also 1-to-5. Control operating effectiveness, 1-to-5, assessed through testing evidence rather than optimism. Residual risk calculated as inherent risk multiplied by a control deficiency factor. The formula is not sacred, but something that keeps you from inflating results on autopilot.
I ran into a specific problem with this during a regulatory exam. We had scored a control effectiveness as 4 out of 5 because the control design looked solid on paper. The auditor asked for evidence of operating effectiveness over the prior twelve months. We had three months of sample testing at most. I could not justify the score. What I did instead was pull transaction logs, pull exception reports, and run a statistical sample of eighty transactions across the full period. The actual error rate came back at 2.3 percent, which dropped the operating effectiveness to 3 and raised residual risk accordingly. The fix was not about rewording the control description. It was about accepting that the rating had been based on design rather than operation, which is exactly how most of these assessments drift into unreliable territory.
What Beginners Miss
The first mistake is rating controls as effective because they exist. Existence and effectiveness are different things. A control that is designed well but never tested, never logged, and never escalated is a control on a spreadsheet, not in the system. I have seen organizations treat a written policy as a Level 5 operating control. It is not. It is a Level 1 design rating at best. The second mistake is collapsing multiple risks into a single control description. If a control addresses fraud, data quality, and compliance in one sentence, you cannot tell which risk it actually mitigates when it fails. Break it down. One control per risk vector. If a control covers multiple vectors, split it in the assessment and note the overlap explicitly. The resulting matrix will be larger, but it will be honest. Process mapping comes before risk identification, not after. I have watched teams skip the process map and jump straight to listing risks. That produces incomplete risk inventories because the team is pulling from memory rather than from an actual workflow. A proper process map takes roughly one to two hours per department if you involve the right people. A rushed version takes thirty minutes and produces about forty percent of the relevant risks.
Get the Full Details
How to Run the Assessment Without Burning Out
Start with a single process. Do not attempt to assess every process across the organization in one quarter. Pick the highest risk process based on prior audit findings, incident history, or regulatory exposure. Complete the full cycle for that process, document the results, and use it as the template for the next one. This approach typically cuts the learning curve from about three weeks down to one week once you have a working template. The participants need the right mix. Control owners who actually execute the process, not just manage it. A risk professional who knows how to frame risk questions without leading the answers. Someone from internal audit or compliance who can challenge ratings without dominating the session. If the room is mostly people who want to avoid uncomfortable conversations, the results will reflect that. Scheduling is the bottleneck. One session per process takes about ninety minutes if you stay on topic. Most sessions run longer because control owners bring up unrelated issues. I recommend capping each session at ninety minutes and parking off-topic items for a follow-up working session. This keeps the risk identification focused and prevents fatigue from diluting the quality of later assessments.
Documentation That Survives Scrutiny
Every rating needs evidence. Inherent risk ratings should reference historical loss data, regulatory guidance, or documented process complexity. Control design ratings should reference the control policy, procedure, or system configuration. Control operating effectiveness ratings should reference test results, exception logs, or sample-based testing. If you cannot point to evidence for a rating, the rating is speculative and should be flagged as such. I once had a situation where a control owner insisted on a residual risk score of 2 for a high-complexity process because the business considered it low risk due to perceived management oversight. I asked for the evidence behind that perception. There was none. I adjusted the score to 4 based on the documented process complexity and the lack of automated controls. The control owner disagreed. We documented the disagreement and the rationale for both positions in the assessment record. This is how you handle pressure without compromising the integrity of the output.
Common Failure Modes
The biggest failure mode is when RCSA becomes a retrospective exercise rather than a prospective one. If you are only assessing risks that have already materialized, you are doing incident analysis, not risk assessment. The process should surface risks that have not yet occurred. Look at process changes, system updates, staffing changes, and regulatory changes that might alter the risk profile going forward. Another failure mode is score inflation. When every control rates a 5, the matrix is useless. I use a rule of thumb: no more than twenty percent of controls in any process should receive a top-tier effectiveness rating. If the number is higher, the ratings are not credible. Push back. Request evidence. Adjust the scores. RCSA does not work well in organizations with weak control culture. If the environment rewards good news and penalizes bad news, the assessment will reflect that. There is no technical fix for that. The only real fix is leadership commitment to transparency, which is not something you can build into a template.
Template Components You Can Use
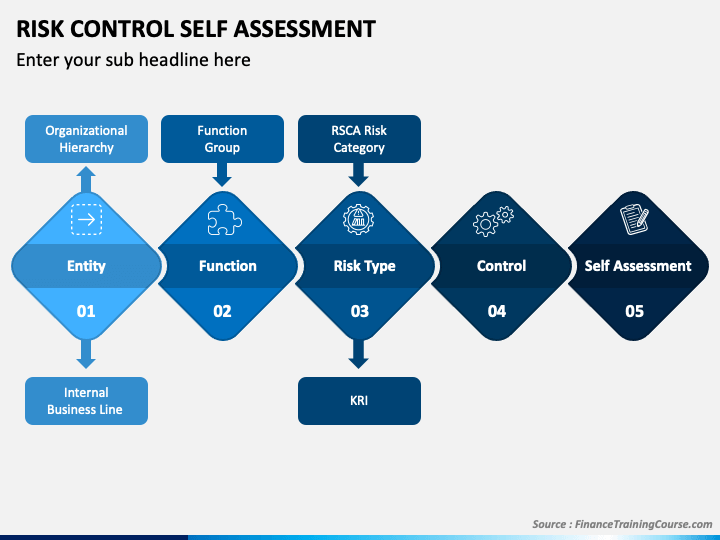
A functional RCSA template contains the following fields: process name, process owner, risk category, risk description, control description, control type, control frequency, control design rating, control operating effectiveness rating, residual risk rating, evidence reference, and assessor name with date. Additional fields for risk appetite alignment, mitigation recommendations, and follow-up actions are useful but not essential in the initial version. The rating scales should be defined explicitly in the methodology document. A 1 means the control does not exist or is ineffective. A 3 means the control exists but has measurable gaps. A 5 means the control is fully designed, consistently operated, and supported by sufficient evidence. Anything between those anchors needs a clear definition so that different raters produce comparable results. If you need a starting point, I use a single workbook with separate sheets for process mapping, risk inventory, control inventory, and aggregated heat map. The heat map sheet pulls from the other sheets using lookup formulas. This reduces manual entry errors and makes it easier to update ratings as new evidence emerges. The template takes about an hour to set up and about fifteen minutes to update per process when the data is already in place.
When RCSA Falls Short
RCSA is not a substitute for external audit, quantitative risk modeling, or scenario analysis. It is a self-assessment tool. The outputs are only as reliable as the inputs, and the inputs depend on the honesty and competence of the people filling it out. If your organization lacks those qualities, RCSA will produce a document that looks professional but tells you little that is true. In that case, consider supplementing with third-party risk assessments, external benchmarking, or focused audits on the highest-risk processes. These approaches can compensate for internal bias that RCSA cannot correct on its own. The method works when you treat it as a living process rather than an annual ritual. Update ratings when conditions change. Review the output quarterly, not just during the assessment cycle. Keep the evidence trail current. The difference between a useful RCSA and a compliance artifact is usually about thirty minutes of honest effort per process per quarter.