The actual process nobody tells you about
Most small business owners treat risk assessment like a form they fill out once a year to satisfy someone else's requirements. That approach leaves real exposure on the table and wastes about two hours of billable time for no reason. Here is how the work actually goes when you do it right.
Risk Assessment For Small Business: What It Actually Looks Like
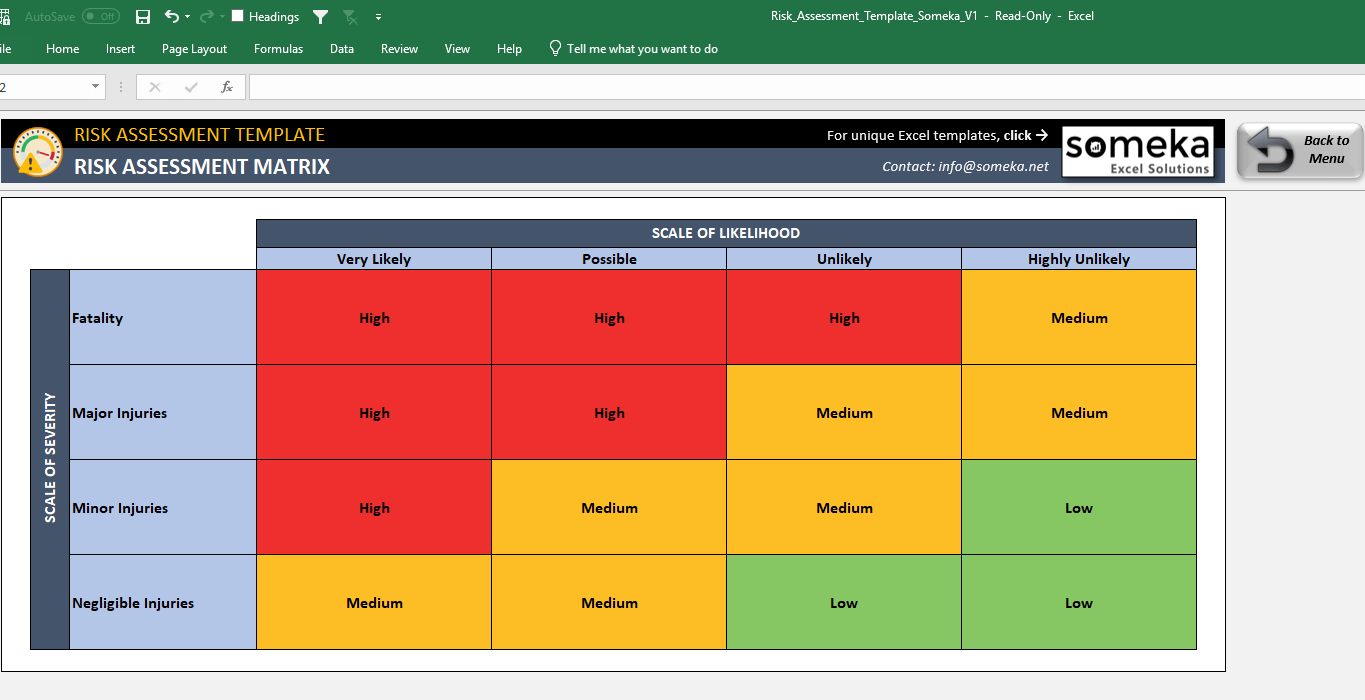
A risk assessment is a systematic way of identifying what can go wrong in your operation, estimating how bad those outcomes could be, and putting controls in place that actually matter. The formal version uses likelihood and impact matrices, likelihood scoring from 1 to 5, impact scoring from 1 to 5, and a risk priority number calculated by multiplying the two. Most small businesses skip straight past the math and still get decent results if they follow the structure. The method starts with listing every process, piece of equipment, and external dependency your business touches. Then you ask: what could fail here, what is the chance it fails, and what happens if it does. You rank those risks. You decide which ones you accept, which you mitigate, and which you transfer through insurance or contracts. That is it. The rest is paperwork that varies by industry and auditor. I ran into a real problem with a client a while back who was running a small warehousing operation. Their initial assessment listed physical safety risks like forklifts and shelving. They completely missed the vendor concentration risk because one supplier accounted for 73 percent of their inventory spend. When that supplier had a production halt due to a labor dispute, they had zero fallback options and nearly went under. The workaround was straightforward: we mapped every single vendor relationship, calculated spend concentration for each category, and set a hard rule that no single vendor could exceed 30 percent of any procurement category. We added secondary supplier qualification requirements and renegotiated terms with the primary vendor to include escalation clauses. That single change reduced their operational risk exposure significantly without requiring new insurance or capital expenditure.
Here is something most people miss about risk assessment. The biggest flaw is not in the identification phase. It is in the treatment phase. People identify risks, write them down, and then do nothing about the high-priority items because the mitigation requires organizational changes that affect multiple departments. The risks that kill small businesses are the ones everyone sees clearly but nobody has the authority or budget to address immediately. Another counter-intuitive point: the most valuable risks are often the ones that sound boring. Business continuity risks, key person dependencies, and data integrity issues tend to get less attention than flashy cyber threats or natural disasters. But a sudden illness of a single employee who holds all the customer relationships and system passwords can shut down a ten-person company faster than any ransomware attack. I have seen this repeatedly. The workaround is to build a simple knowledge transfer and access management protocol that requires every critical role to have at least one documented backup person with read access to the necessary systems.
How to actually build one without hiring a consultant
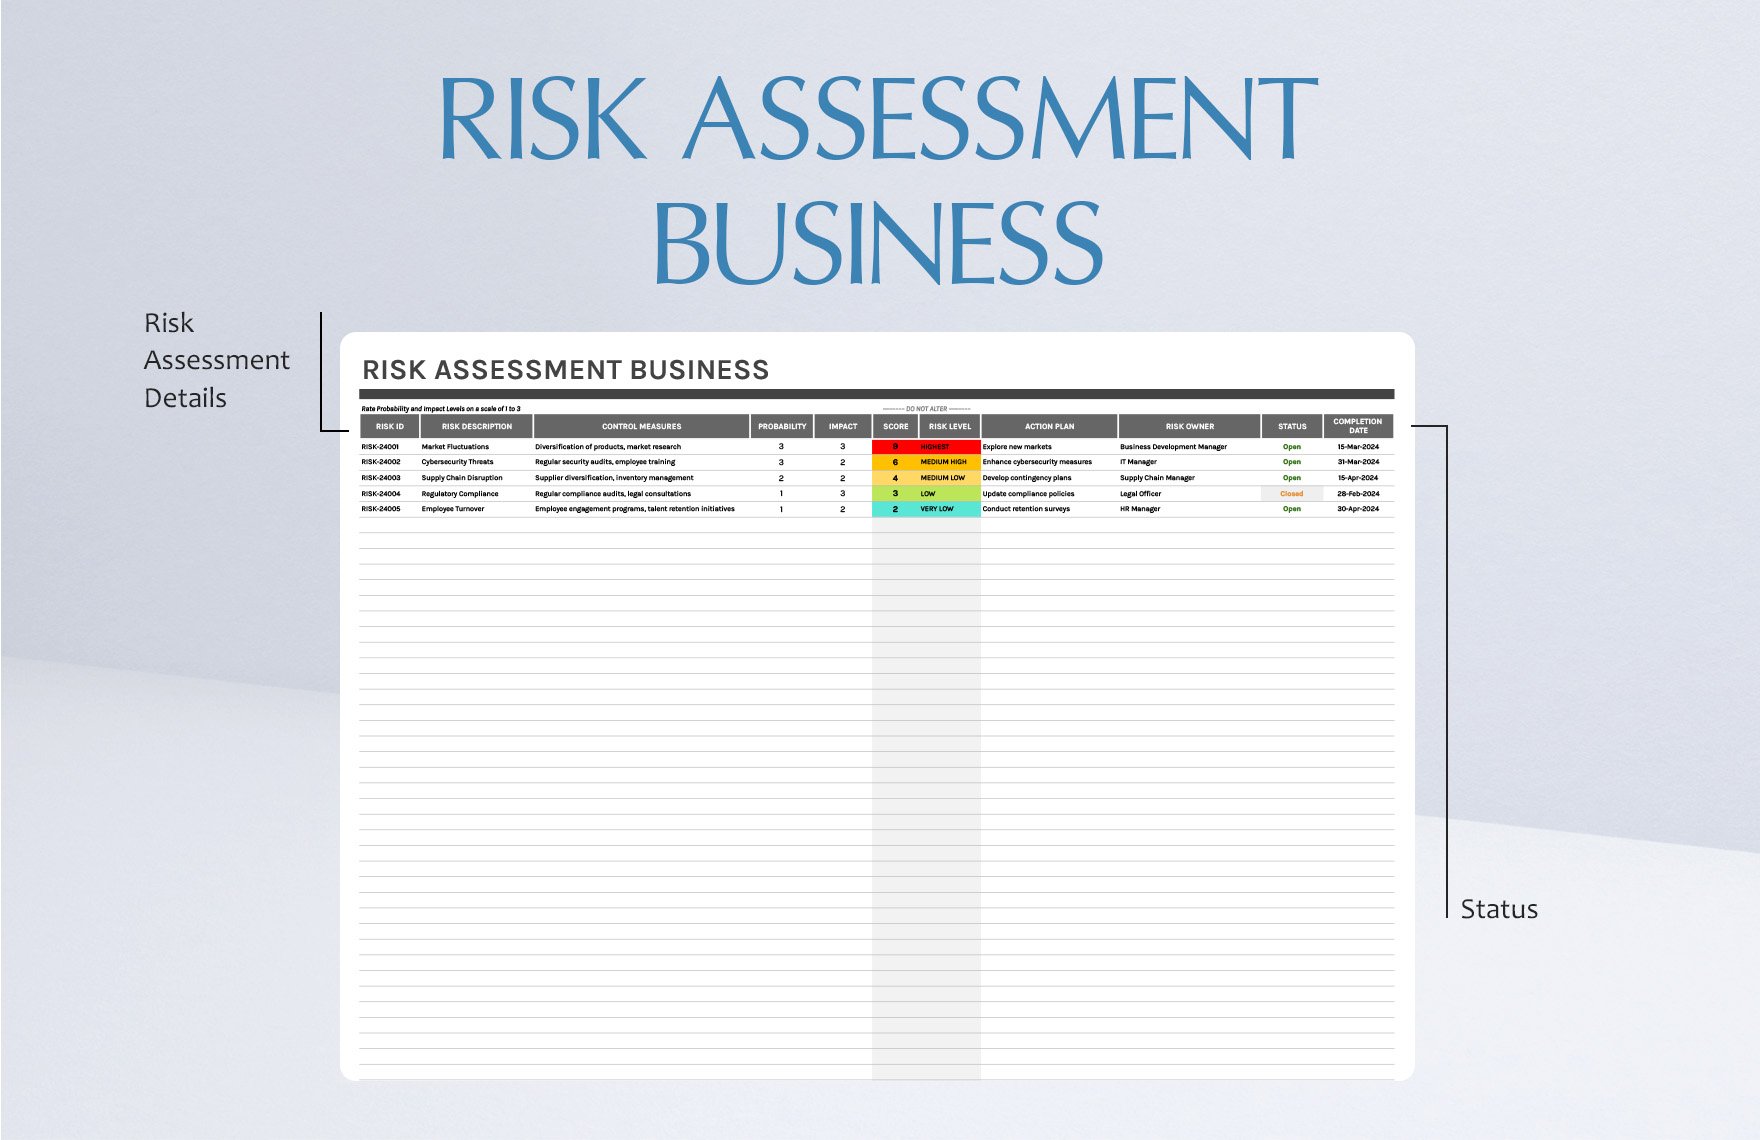
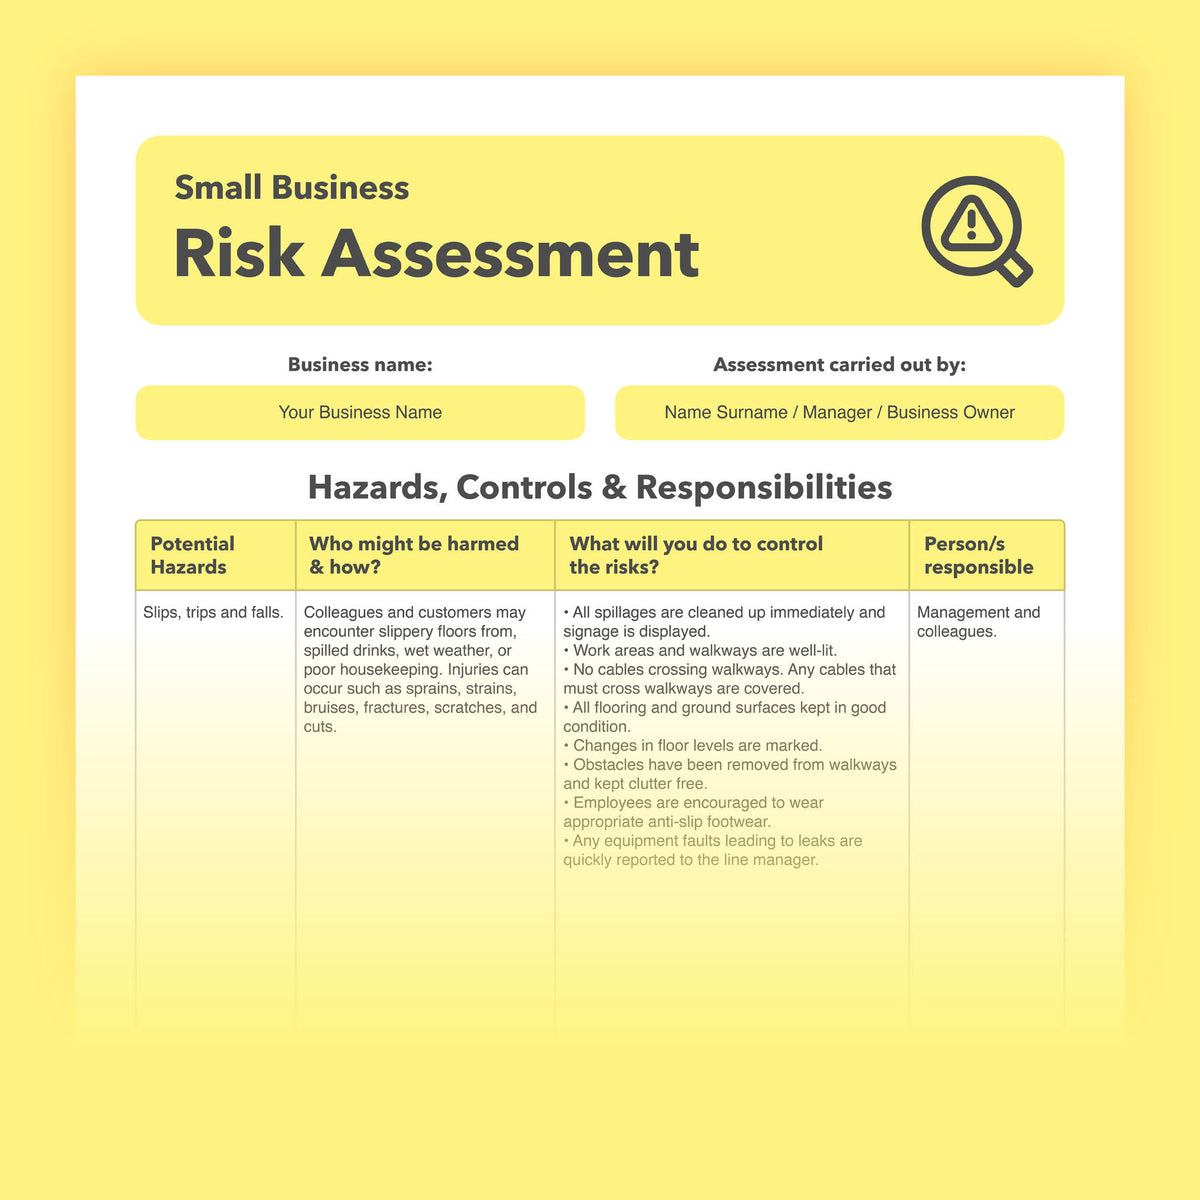
You do not need a $5,000 consulting engagement to produce a usable risk assessment. You need a spreadsheet, three hours of focused time, and honest conversations with the people who actually do the work. The spreadsheet should have columns for risk description, process area, likelihood score, impact score, risk level, existing controls, additional controls needed, owner, and target completion date. Keep it simple. Fancy templates add complexity without adding value. Start by sitting down with your team. Walk through each major process step and ask what could go wrong at that step. Write everything down without judging whether it sounds important or not. I usually find that the frontline workers know far more about real risks than the owner does. They have seen things break, customers get angry, and processes fail. Documenting those observations is where the assessment gets accurate. Once you have your list, score each risk. Likelihood: one means this happens rarely, maybe once a year or less. Three means this happens a few times per year. Five means this happens weekly or more. Impact: one means negligible financial or operational effect. Three means noticeable disruption that costs time and money but does not threaten survival. Five means existential threat to the business. Multiply the two scores. Risks scoring seven or above need immediate attention. Risks scoring four to six need scheduled mitigation. Risks scoring three or below you can monitor and revisit quarterly.
Get the Full Details
The tool most small businesses should use is a shared document rather than a static file. Google Sheets or a simple project management tool works fine. The key is that the document stays alive. A risk assessment that gets filed away after creation is worse than useless because it creates false confidence. Schedule a fifteen-minute review every quarter. Update scores. Mark completed mitigations. Add new risks from recent incidents or near misses.
Where this approach breaks down and what to do instead
The matrix scoring system has real limitations. The numbers are subjective and different people will score the same risk very differently. A likelihood score of three from one person might be a two from another person. This inconsistency means the risk priority numbers are rough estimates, not precise measurements. Do not treat them as scientific data. They are decision aids, not verdicts. For highly regulated industries like food service, healthcare, or construction, a simple matrix will not satisfy compliance requirements. You will need industry-specific frameworks. Food businesses should use HACCP principles. Construction firms should reference OSHA standards and their own industry association guidelines. Healthcare practices need HIPAA-compliant risk analysis procedures. The basic structure is similar, but the required content and documentation standards differ significantly. If your business has complex supply chains or international operations, the standard assessment approach underestimates cascade effects. One supplier failure can trigger failures across multiple downstream processes simultaneously. In those cases, consider adding a dependency mapping exercise alongside your risk assessment. Draw out the relationships between vendors, logistics providers, and internal processes. Identify single points of failure that a simple risk register would miss.
The other major limitation is that risk assessment does not account for black swan events by design. It focuses on identifiable, probable risks. Rare catastrophic events fall outside the normal scoring range. This does not make the exercise pointless. It means you need a separate continuity planning process that addresses low-probability high-impact scenarios independently. Run a tabletop exercise once a year where you walk through a worst-case scenario and identify what you would actually do. This usually reveals gaps that the standard assessment cannot show. Most small businesses also underestimate the cost of inaction. A proper risk assessment with quarterly reviews typically takes between two and four hours per quarter once the initial framework is built. The alternative is reactive spending on incidents that could have been prevented. One missed cybersecurity vulnerability can cost ten thousand dollars or more in remediation and downtime. A single lost key employee can cost weeks of productivity and recruitment expenses. The assessment pays for itself through avoided losses, not through direct revenue generation. There is no universal template that fits every business. The process needs to reflect your actual operations, your actual team, and your actual exposure. Start with what you know. Document it. Review it regularly. Adjust it when something changes. That is the entire method.