What a Risk Assessment Procedures Audit Actually Looks Like
Most people think auditing risk procedures means flipping through checklists and marking boxes green. It does not work that way. The real work happens when you sit down with a procedure that has been living in a shared drive since 2019, written by someone who left the company two years ago, and try to figure out whether it still matches what your operations actually do on a Tuesday morning. I have done this enough times to know that the gap between documented process and executed process is usually where compliance fails, not in the documents themselves.
A Risk Assessment Procedures Audit is a systematic review that verifies whether your organization's documented risk assessment methods are actually being followed, remain relevant to current operations, and produce decisions that hold up under scrutiny. The word "audit" here matters because it implies evidence gathering, not opinion. You need to show that someone reviewed something, that the review was based on actual data, and that the conclusions were documented. Without those three elements you have just written a summary, not conducted an audit.
How I Approach a Risk Assessment Procedures Audit
I start with the outputs, not the documents. Before I look at a single risk register or procedure manual, I pull the last twelve months of incident reports, near-miss logs, and operational deviations. This tells me where the actual risks materialized in practice. If your largest documented risk is "data center power failure" but your biggest operational disruption last year came from a third-party API outage that was rated medium probability, the procedure is misaligned with reality regardless of how beautifully it is formatted.
After establishing what actually went wrong, I map those real events back to the documented risk assessment procedures. I trace each significant incident to the specific risk assessment that should have caught it or responded to it. This tracing step reveals gaps that no amount of checklist review will show. You might find that a procedure exists for vendor risk assessment but none for sub-contractor risk, or that the frequency of review is documented as quarterly but nobody has actually completed more than two reviews in the past eighteen months.
Once the gap analysis is complete, I examine the actual risk assessment procedures themselves for structure and completeness. A proper risk assessment procedure should address identification, analysis, evaluation, and treatment of risks with clear decision criteria at each stage. If any of those four elements are missing or vague the procedure will produce inconsistent results across different teams and different time periods. I check for this specifically because I have seen procedures that treat "likelihood" and "impact" as free-text fields where everyone writes whatever they feel like writing, which makes aggregation and trend analysis impossible.
The final step is verifying that the people responsible for executing the risk assessments have both the authority and the competence to do so. A documented procedure means nothing if the person signing off on a risk acceptance does not have the organizational mandate to make that decision or the technical knowledge to understand what they are accepting. I always interview the actual risk owners, not just the process owners, because the disconnect between these two roles is a common failure point that auditors miss.
I encountered a specific problem during an audit last year where the documented risk assessment procedure required all high-priority risks to be reviewed by the risk committee within thirty days, but the committee only met quarterly. The procedure was technically compliant on paper but practically impossible to follow. The workaround I recommended was to introduce an expedited review pathway for time-sensitive risks with a documented escalation criteria, which reduced the gap between policy and practice from forty-five days to approximately eight days while maintaining proper oversight.
Common Pitfalls in Risk Assessment Procedures Audits
The most frequent failure I see is treating the audit as a compliance exercise rather than a validation exercise. When organizations approach a Risk Assessment Procedures Audit with the mindset of "prove we are compliant" instead of "verify our risk assessments actually work," the audit becomes a box-ticking ritual that misses the substantive issues. Compliance audits check whether documents exist and bear signatures. Validation audits check whether those documents produce decisions that survive contact with reality. The difference matters because regulatory examiners increasingly expect to see the latter.
Another common error is over-reliance on quantitative risk assessment methods without validating the underlying data. I have reviewed risk assessments where the probability estimates were pulled from industry averages published five years ago, applied to systems that operate in environments with very different risk profiles. A quantitative risk assessment using poor quality input data produces false precision that is more dangerous than a qualitative assessment using honest uncertainty. The risk assessment procedure should document the source of all quantitative inputs and include a data quality assessment for each major risk category.
The third pitfall is audit fatigue, which occurs when the same team reviews the same procedures year after year without fresh perspective. I recommend rotating audit responsibility across different departments and bringing in external reviewers at least every three years. Fresh eyes catch assumptions that the original authors take for granted and identify procedural drift that annual reviews miss. The additional cost of external review is usually offset by the reduction in repeat findings.
There are also scenarios where a traditional Risk Assessment Procedures Audit is not the right tool. If your organization has undergone a major transformation in the past six months, such as a merger, acquisition, or technology migration, the existing risk assessment procedures may be fundamentally misaligned with the new operating model. In these cases I recommend a rapid risk alignment review rather than a full audit, which typically takes two weeks instead of eight and focuses on identifying critical mismatches rather than documenting comprehensive compliance.
The main downside of any Risk Assessment Procedures Audit is that it captures a snapshot in time. Risk assessments are dynamic processes and the audit will be obsolete within weeks if the underlying risk landscape changes. To mitigate this I suggest implementing continuous risk assessment monitoring with automated triggers for procedure review when certain conditions are met, which keeps the audit relevant between formal review cycles.
Gallery Risk Assessment Procedures Audit
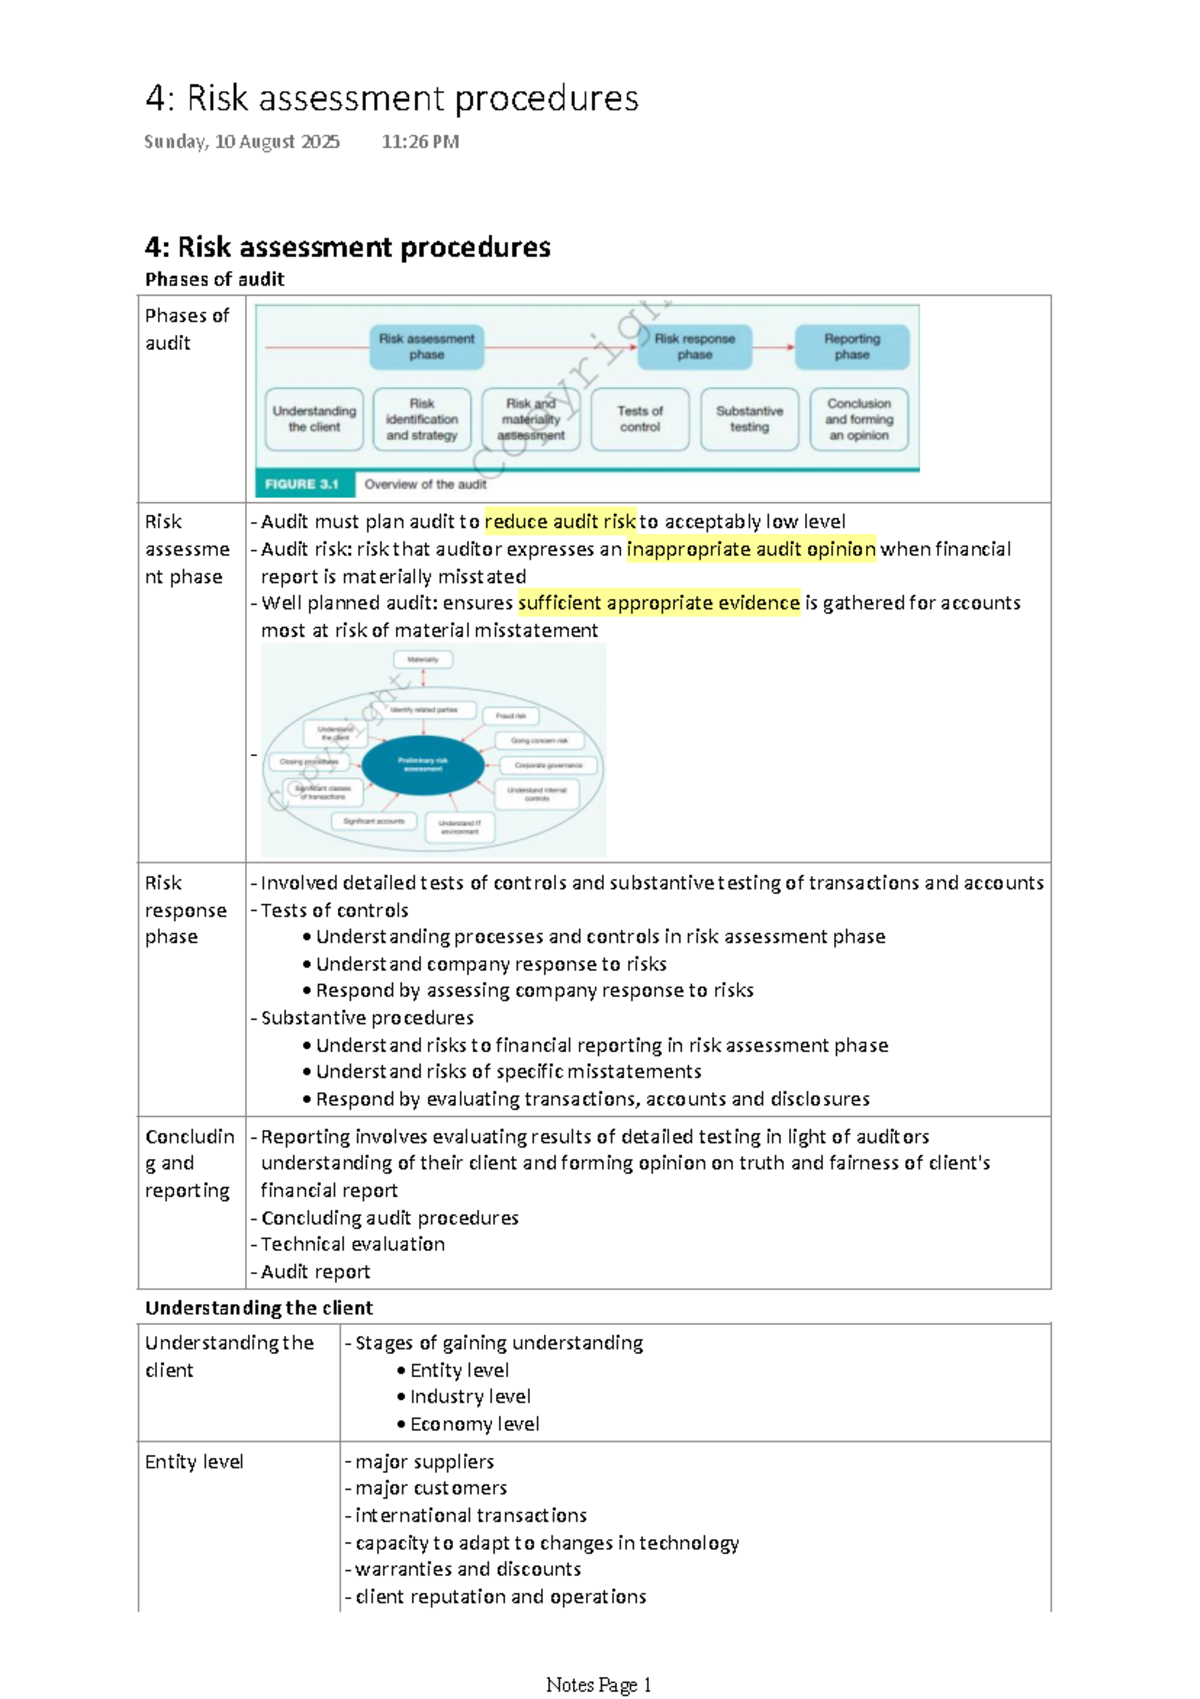
4: Risk Assessment Procedures for Audit Planning and Execution - Studocu
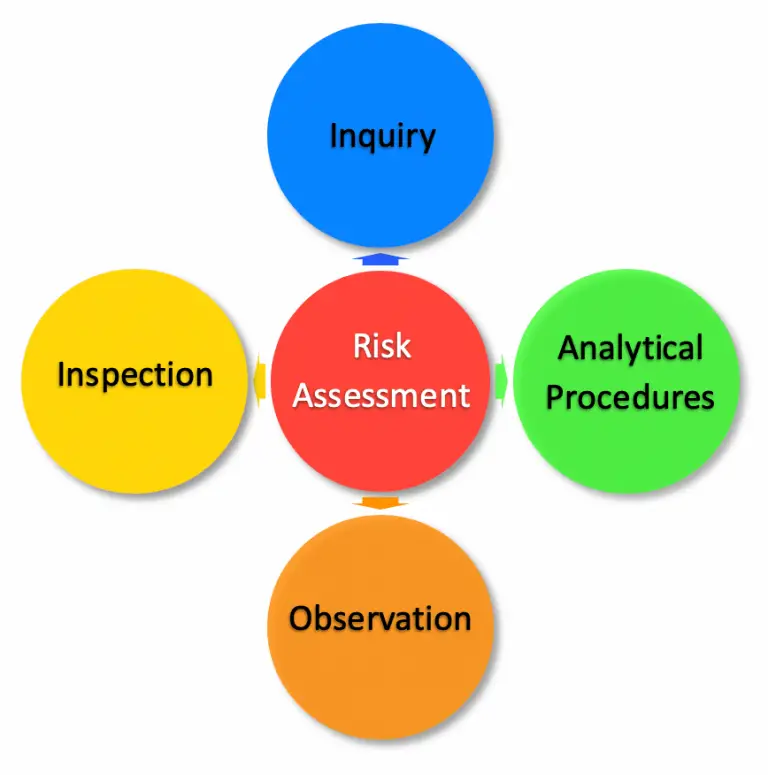
Understanding the Role of Risk assessment in audit planning
Risk Assessment In Financial Audit: A Practitioner’s Guide | Risk Publishing
Strategic Flowchart Of Audit Procedure For Risk Assessment PPT Presentation
Must-Have Internal Audit Risk Assessment Templates with Samples and Examples