Most people treat risk assessment as a checkbox exercise. They fill out the same template year after year, list generic threats, and move on. That approach leaves gaps. Real risk work is messier. You need something that survives when a reviewer asks, "Why didn't you consider X?"
A proper Risk Assessment Report Sample should capture context, method, findings, and mitigation in a way that holds up under scrutiny. The trick is balancing completeness with usability. Nobody reads a forty-page report from cover to cover. But stakeholders will pick at the one page that matters for their budget.
My Experience Building These Documents
I've spent more time than I care to admit wrestling with assessment templates. The version I landed on came together after a brutal post-mortem on a compliance audit. An external reviewer tore through our report and pointed out we'd listed "data breach" as a risk without explaining how, why, or what we'd actually do if it happened. They were right. Our risk assessment report sample had become a hollow form.
What changed was forcing specificity. Instead of "unauthorized access," I started writing "a contractor's credentials compromised via phishing, granting read-only access to customer PII." The difference isn't cosmetic. It shifts the mitigation from "we'll authentication" to something actionable.
How to Structure Your Assessment
Start with the scope. Define what you're assessing and what you're excluding. A common failure mode is scope creep. You begin with "all systems handling payment data" and end up documenting every laptop in the building because someone argued the coffee machine qualifies as a networked asset.
Next, identify your risk methodology. Whether you're using qualitative scoring, quantitative analysis, or a hybrid like FAIR, name it and justify it. I learned this the hard way when a client asked why I used 1-5 likelihood scales instead of historical frequency data. I couldn't answer because I hadn't explained.
The core of the document is the risk register. Each entry needs:
- Risk ID and title
- Category (operational, financial, strategic, compliance, etc.)
- Likelihood and impact scores with defined scales
- Existing controls
- Residual risk after controls
- Mitigation recommendations
- Owner and target date
The Hidden Complexity in Risk Identification
Beginners miss second-order risks. They document the direct threat—"server failure causes downtime"—but don't capture the cascade. If that server hosts the primary authentication service, the second-order risk is "customer accounts locked for three business days, revenue impact $120,000." Your assessment should force this thinking.
I once encountered a supply chain risk that looked manageable on paper. The vendor had SOC 2 Type II certification. But during a site visit, I discovered their encryption keys rotated manually by an intern who didn't have sudo access. The certification was current. The practice wasn't. We upgraded the residual risk rating and added a control requiring automated key rotation with documented verification.
Choosing Between Qualitative and Quantitative Approaches
Qualitative methods use descriptive scales. Low, medium, high. They're faster to produce but harder to defend. Quantitative approaches assign monetary values or probabilities. They require more data and analysis time but cut through arguments about "how bad" something could get.
The honest answer is most organizations need a hybrid. Use qualitative scoring for initial triage—categorize risks as critical, major, minor—and quantitative analysis for the top twenty percent. This typically reduces the process down from two weeks to about four days while still producing defensible numbers for board-level presentations.
One caveat: quantitative methods often fail when data is scarce. If you're assessing a new product line with no historical loss data, forcing a dollar figure onto "reputational damage" creates false precision. I've seen risk registers with entries like "brand impact: $2.4 million" based on no actual research. It's worse than useless because it looks authoritative while meaning nothing.
Essential Components of Your Document
A complete risk assessment report sample should contain:
Executive Summary
Two pages maximum. State the overall risk posture, top five risks, and key recommendations. Decision-makers will read this section and use it to justify budget requests. Don't bury the lede.
Methodology
Document your approach. Reference standards like ISO 31000, NIST SP 800-30, or COSO ERM if you're using them. Explain how you defined likelihood and impact scales. Include the calculation for risk scores.
Risk Register
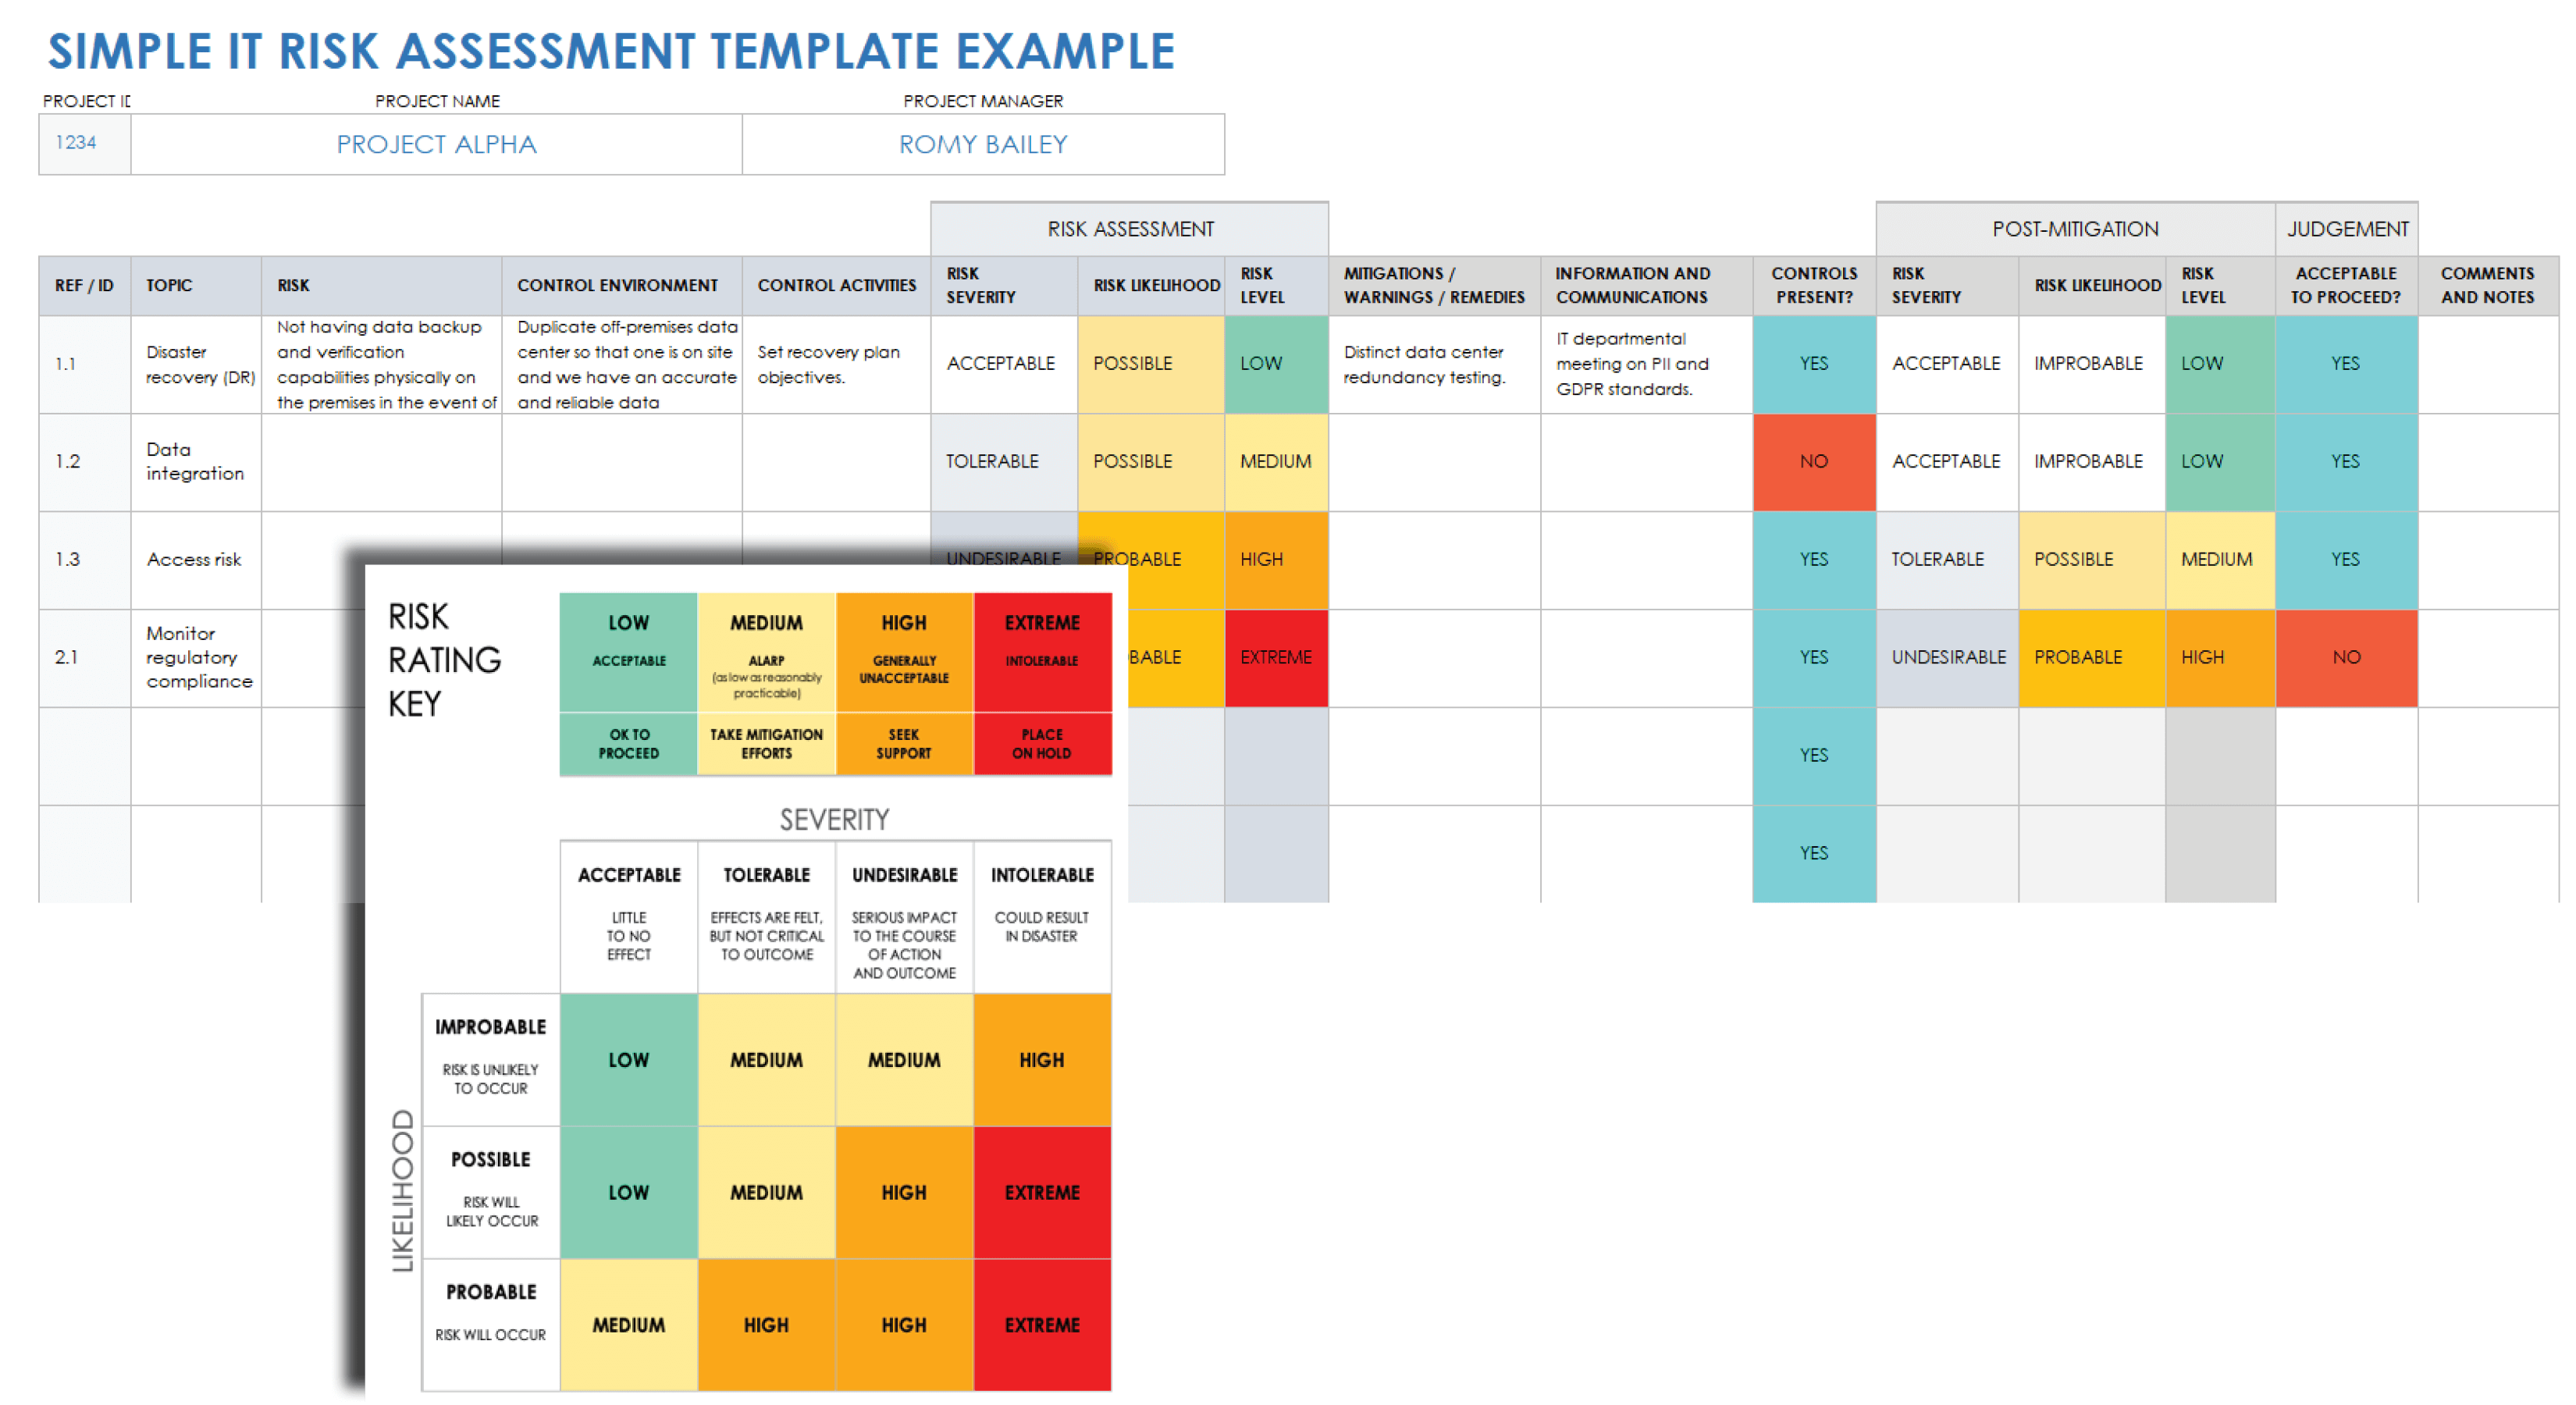
This is the heart of the document. Use a table format. Columns should include risk ID, description, category, likelihood, impact, risk score, existing controls, residual risk, recommended actions, owner, and target completion date.
Mitigation Strategies
For each critical risk, propose treatments. Accept, mitigate, transfer, or avoid. Be specific. "Implement multi-factor authentication" is better than "strengthen security controls." Add timelines and resource estimates.
Appendices
Include supporting documentation. Meeting notes, survey results, system diagrams, policy references. These provide audit trails and make the assessment defensible.
Common Pitfalls I've Witnessed
Over-documentation is real. I've received assessments exceeding two hundred pages. Nobody reads them. The important risk gets lost in noise. Trim aggressively. If a risk doesn't drive a decision, it probably doesn't belong in the main body.
Another failure mode is static assessments. You publish the report and file it away. Risk environments change. New vulnerabilities emerge. Regulations shift. Build in periodic review cycles—quarterly for critical systems, annual for lower-risk areas.
I once worked on an assessment where the original risk owner had left the company eight months prior. The recommended mitigation was assigned to a role that no longer existed. The action never happened. Always validate ownership and availability of resources before finalizing recommendations.
How to Present Findings to Stakeholders
Tailor the message. Technical teams want detail. Executives want summary. Regulators want evidence. Prepare different versions of the same assessment. The content remains consistent; the framing changes.
Use visual aids sparingly but effectively. A heat map showing risk distribution across categories helps stakeholders grasp the landscape quickly. A trend chart comparing current risk levels to previous assessments shows progress or regression.
When presenting, lead with the most critical risks. Don't build up to them. Decision fatigue is real. If you've spent thirty minutes on low-priority items, your audience will glazed over by the time you reach the risk that could shut down operations.
Handling Disagreement on Risk Ratings
Stakeholders will challenge your assessments. A security engineer might rate a vulnerability as "critical" while finance sees "major." Both perspectives have merit. The resolution isn't always compromise—it's transparency.
Document the rationale for each rating. When questioned, explain the basis. If someone disputes a likelihood score, show the historical data or expert judgment supporting it. If impact seems overstated, walk through the calculation.
I learned that ratings are arguments, not facts. The number itself matters less than the reasoning behind it. A well-reasoned "high" rating beats a precisely calculated "7.3" with no justification.
Making Your Assessment Actionable
An assessment that sits unread is a waste. Force actionability through clear ownership and timelines. Each recommendation should have a responsible person and a due date. Without both, nothing happens.
Prioritize mitigations. You'll rarely have budget for every recommendation. Use a risk-based approach: address critical and high risks first, then allocate remaining resources to medium-priority items.
Track progress. Don't publish the report and disappear. Schedule follow-up reviews. Update the risk register as circumstances change. Close completed mitigations and document the outcomes.
A practical workflow: publish the assessment, conduct a two-week implementation sprint, hold a monthly status review for the first quarter, then transition to quarterly check-ins. This cadence maintains momentum without overwhelming operational staff.
The Reality of Resource Constraints
Budget rarely matches the ideal. You'll recommend ten mitigations and get approved for three. That's normal. The key is selecting the right three.
Focus on controls that reduce multiple risks simultaneously. An encrypted backup system mitigates data loss, ransomware impact, and regulatory non-compliance. Single-purpose controls are efficient but fragile—they solve one problem and leave the rest exposed.
When forced to prioritize, consider the risk with the highest consequence, not the highest probability. A low-likelihood, high-impact event that could bankrupt the organization deserves attention over a frequent, minor nuisance.
Sample Risk Assessment Report Structure
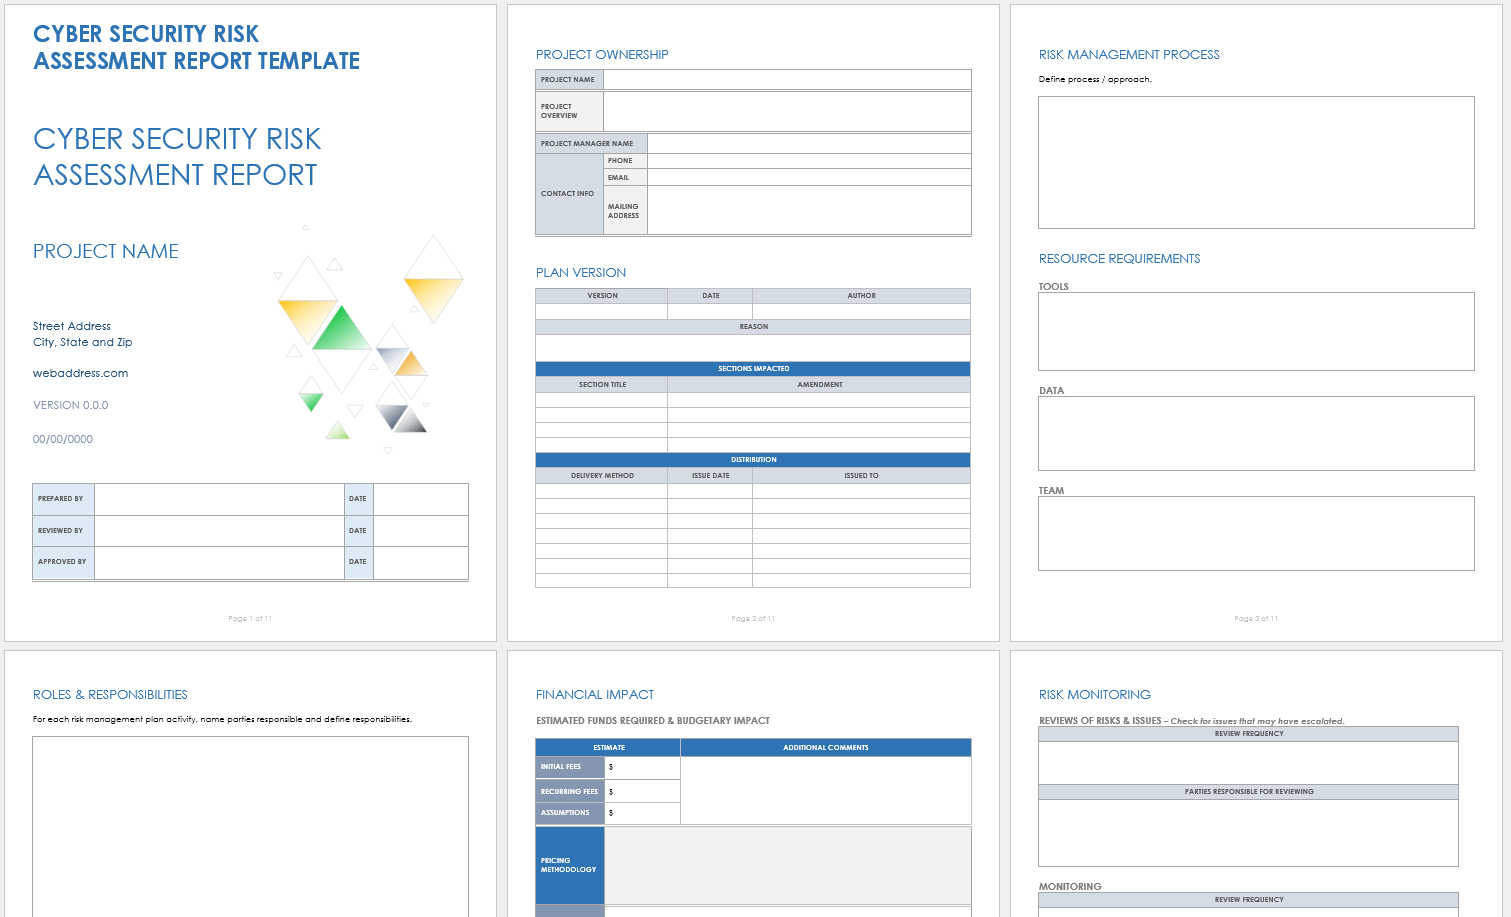
Here's a breakdown of what a comprehensive Risk Assessment Report Sample should contain:
1. Title page with document control information
2. Revision history tracking changes
3. Executive summary with overall risk posture
4. Scope and boundaries
5. Methodology explanation
6. Risk identification process
7. Detailed risk register with full entries
8. Mitigation recommendations prioritized by urgency
9. Implementation roadmap with timelines
10. Monitoring and review plan
11. Appendices with supporting documentation
Each section serves a purpose. The executive summary drives decisions. The methodology provides defensibility. The risk register captures detail. The recommendations translate analysis into action.
If you're producing this for internal use, condense sections two through four into an appendix. External auditors and regulators will want the full methodology. Internal stakeholders need only the results.
A Practical Example from Recent Work
Last year, I assessed risks for a mid-size fintech company preparing for a Series B fundraising round. Investors required a formal risk assessment as part of due diligence. The standard framework wouldn't work—their risk profile involved regulatory uncertainty, technology debt, and competitive threats that didn't fit neatly into traditional categories.
I created a custom taxonomy blending operational, regulatory, and strategic risk dimensions. The resulting Risk Assessment Report Sample contained forty-seven identified risks across six categories. Critical items included incomplete KYC automation (likelihood: high, impact: existential), key-person dependency on two senior engineers, and regulatory ambiguity around cross-border data transfers.
The assessment took fourteen calendar days, including two rounds of stakeholder interviews and one validation session. The investors accepted the report without requesting changes—a result I attribute to the transparent methodology and specific, actionable recommendations rather than generic platitudes.
Maintaining the Document Over Time
Risk assessments decay. Systems change. Threats evolve. Staff turnover disrupts ownership. Treat the report as a living document, not a one-time deliverable.
Establish a review calendar. Quarterly for critical infrastructure, biannual for supporting systems, annual for lower-risk areas. Trigger reviews also when significant changes occur: new products, mergers, regulatory updates, security incidents.
Version control matters. Track every change with dates, authors, and reasons. Future reviewers need to understand why risk ratings shifted or why certain mitigations were deprioritized.
Build review into existing workflows. Attach risk assessment updates to change management processes. Require assessment revisions before launching new initiatives. This integration keeps the document current without creating separate administrative overhead.
Tools and Templates
Spreadsheet-based registers work for small organizations. Excel or Google Sheets handle dozens of risks comfortably. Beyond fifty entries, database solutions become necessary. Commercial risk management platforms offer automation but introduce licensing costs and vendor dependency.
Open-source templates are available but often incomplete. The ones I've found useful came from professional networks and peer communities, not generic internet searches. A Risk Assessment Report Sample you adapt to your context will serve better than a polished template that doesn't fit your operations.
Consider starting simple. Document risks in a table with columns for ID, description, category, likelihood, impact, score, controls, residual risk, recommendation, owner, and target date. Expand as the process matures and stakeholders demand more sophistication.
Final Thoughts on Practical Application
Risk assessment isn't about producing a perfect document. It's about making better decisions with incomplete information. The best assessment I ever wrote wouldn't pass a peer review—it was three pages long, used informal language, and relied heavily on context that only our team understood. It prevented two major incidents and saved the organization approximately $800,000 in avoided losses.
The worst assessment I've encountered was technically impeccable. Five hundred pages, perfect formatting, comprehensive methodology. Nobody read it. The risks it identified never got addressed because the document sat in a shared drive, inaccessible to the people who could act.
Aim for usefulness over comprehensiveness. Write for the reader, not the auditor. Include enough detail to be defensible, not so much that it becomes unusable.
If you need a starting point, look for a Risk Assessment Report Sample that matches your industry and organization size. Adapt it. Don't copy it wholesale. The adaptation process forces you to think through your specific risks rather than adopting someone else's conclusions.
The work doesn't end with publication. Follow up. Track implementation. Update findings. The value isn't in the document—it's in the decisions it enables.