How We Actually Use Risk Assessment Scales at Work
Most people treat the Risk Assessment Scale as a simple 1-to-5 matrix and call it done. That approach works fine for low-stakes environments like small IT teams doing annual compliance checks. It falls apart fast when you're dealing with regulated industries, cross-site manufacturing plants, or supply chains that span three continents. I spent two years trying to make a flat 5-level scale work for a chemical processing facility with seventeen different production lines, and I can tell you exactly where that broke down. The basic framework is straightforward enough. You combine likelihood of an event happening with the severity of its consequences. Multiply those two numbers and you get a risk score. Scores above a certain threshold trigger action. The trick isn't the math — it's deciding what the numbers actually mean for your specific situation. A typical setup looks like this:
Likelihood levels:
- 1 — Rare, maybe once in ten years or more
- 2 — Unlikely but plausible within a 12-month window
- 3 — Possible, would expect to see it annually
- 4 — Likely, occurs multiple times per year
- 5 — Almost certain, ongoing or continuous occurrence
Severity levels: A risk score of 15 or above usually demands immediate intervention. Between 8 and 14 means you need a mitigation plan within a set timeline. Below 8 is generally acceptable with routine monitoring. Those thresholds are not universal though. They shift depending on your industry, your risk appetite, and what your auditors actually care about. Here is the problem nobody warns you about. A risk scored as 4 times 3 equals 12 sits in the same medium band as a 2 times 6 if you allow severity to go beyond five. More importantly, a likelihood of 5 multiplied by severity of 1 gives you 5, which looks low on paper. But if that likelihood-5 event is a slow gas leak that people are already experiencing chronic headaches from, a raw score of 5 is wildly insufficient as an action trigger. The scale has no mechanism to weigh chronic low-severity exposure differently from acute rare events.
Get the Full Details
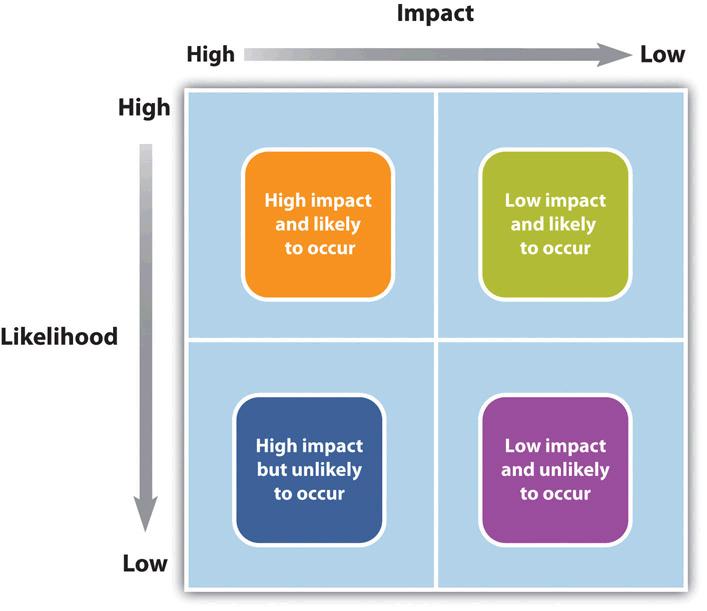
In my case with the chemical plant, we had a situation where a particular corrosion point on a pressure vessel was showing degradation every inspection cycle. The probability of a failure was climbing toward 4 on our scale over a three-year window. The severity of a vessel rupture was a hard 5. That gave us a 20, which was technically in the highest risk bracket. But the actual timeline mattered. A score of 20 with a 36-month projection is a fundamentally different problem than a score of 20 with a 6-month projection. Our original matrix couldn't express that difference at all. The workaround I ended up using was adding a time-to-occurrence modifier as a third dimension. Instead of just likelihood and severity, we factored in the projected exposure window. Anything projecting within 12 months got a multiplier of 1.5 applied to the base score. Within 6 months, it became 2.0. That small change moved several medium-priority items into the immediate-action tier without inflating every score in the document. It also forced the engineering team to confront the urgency instead of burying it under a pile of generic high-risk labels.
Setting Up Your Scale Correctly
Before you build any matrix, you need to calibrate it with historical data from your own operations if you have it. Generic likelihood tables from OSHA or ISO documents are starting points, not answers. If your facility has ten years of incident records, use them. Calculate how often each type of event actually occurred. Map those frequencies to your scale and adjust the definitions accordingly. A "possible" event in a data center with no prior outages is a different thing than "possible" at a refinery with six incidents in three years. Severity calibration is equally important and more often done wrong. Many organizations define severity purely in terms of physical harm. That misses operational, financial, reputational, and regulatory dimensions entirely. For a pharmaceutical manufacturer, a severity-1 event might be a single batch deviation that costs two hundred thousand dollars in wasted product and delays a clinical trial. Physical harm was zero. The business impact was severe. Your scale should reflect that reality or it will systematically underweight the risks that actually threaten the organization. Once you have calibrated definitions, document them clearly. Every person who fills out a risk assessment should read the same severity definitions and arrive at the same number for the same scenario. I've seen assessments where one engineer scored a particular hazard as severity 3 and another scored it severity 2 because nobody had written down what the boundary between those two levels actually was. Write it down. Include specific examples for each level if that helps.
Common Pitfalls That Waste Time and Miss Real Risks
The biggest waste I see is treating the Risk Assessment Scale as a one-time exercise. A properly maintained matrix takes about three to four hours to complete for a mid-sized operation on the first pass. After that, quarterly reviews should take roughly forty-five minutes if you have a disciplined team. Monthly reviews cut that down to twenty minutes because you're only tracking changed conditions. Anyone telling you their risk assessments take weeks to update is either using an unnecessarily complex system or they haven't trained their people on it. Another frequent failure mode is scoring everything as medium risk. When half your hazards land in the middle band, the scale has lost its discrimination power. This usually happens because the likelihood and severity definitions are too broad. If severity 3 covers everything from a sprained ankle to a million-dollar equipment failure, people will default to scoring toward the middle to avoid conflict. Narrow your definitions until the middle band contains only genuinely medium-risk items. Then there's the aggregation trap. Summing all risk scores across an entire facility to produce a single number is mathematically meaningless. A plant with twenty hazards all scored at 8 is in a very different position than a plant with one hazard at 20 and nineteen hazards at 1. The aggregate number looks the same but the risk profile is completely different. Track individual scores, track category totals, and track trends over time. Never reduce a risk assessment to a single figure.
When to Move Beyond a Traditional Scale
Straightforward risk matrices work well for operations with stable processes, clear failure modes, and reasonably predictable environments. They break down when you're dealing with novel technologies, cyber-physical systems, or situations where failure modes are poorly understood. In those cases, consider switching to bow-tie analysis or fault tree analysis for the critical hazards. These methods map the causal pathways explicitly instead of collapsing everything into a single score. For cyber risk specifically, traditional likelihood-severity matrices tend to mislead because the attack surface changes weekly and the threat landscape evolves faster than any internal assessment cycle can keep up. NIST CSF and MITRE ATT&CK mapping provides better coverage for that domain even though it requires more effort to implement. Use your Risk Assessment Scale for physical safety and operational risks. Keep your cybersecurity assessments separate with a framework designed for that environment. The tools matter less than the discipline behind them. A spreadsheet-based matrix used rigorously will outperform an expensive GRC platform that gets filled out once a year by a compliance officer who has never walked the floor. Whatever system you choose, make sure the people actually doing the work are the ones populating it. Risk assessments written by people disconnected from daily operations tend to list obvious hazards everyone already knows about and miss the subtle degradation patterns that precede real incidents.