What actually happens when you try to manage risk in government agencies
I spent eight years working with municipal and state-level organizations trying to implement risk frameworks. The short version is that most of them treat it like a compliance checkbox exercise. The longer version involves spreadsheets nobody reads, annual reviews that happen in March because that's when the auditors show up, and genuine incidents that get buried in committee reports for two fiscal years before anyone acknowledges them. Risk Management In Public Sector isn't fundamentally different from the private sector in terms of concepts. Identification, assessment, mitigation, monitoring. But the environment changes everything about how these processes actually function day to day.
The workflow that actually works
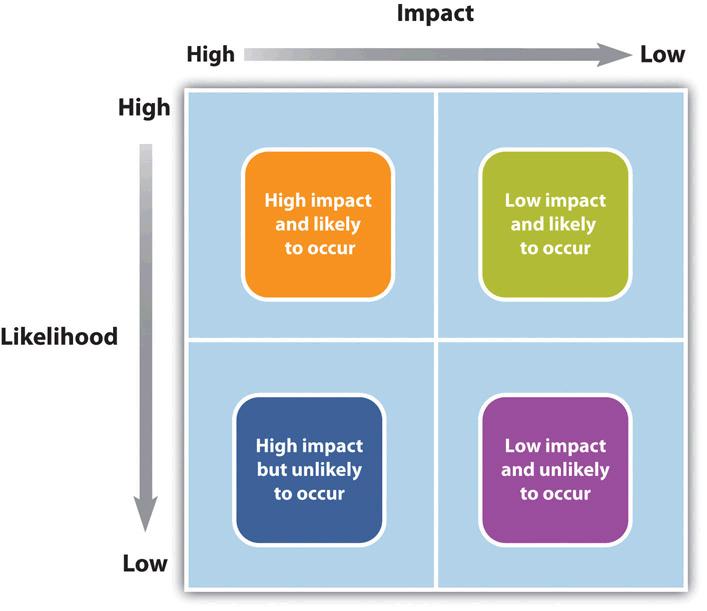
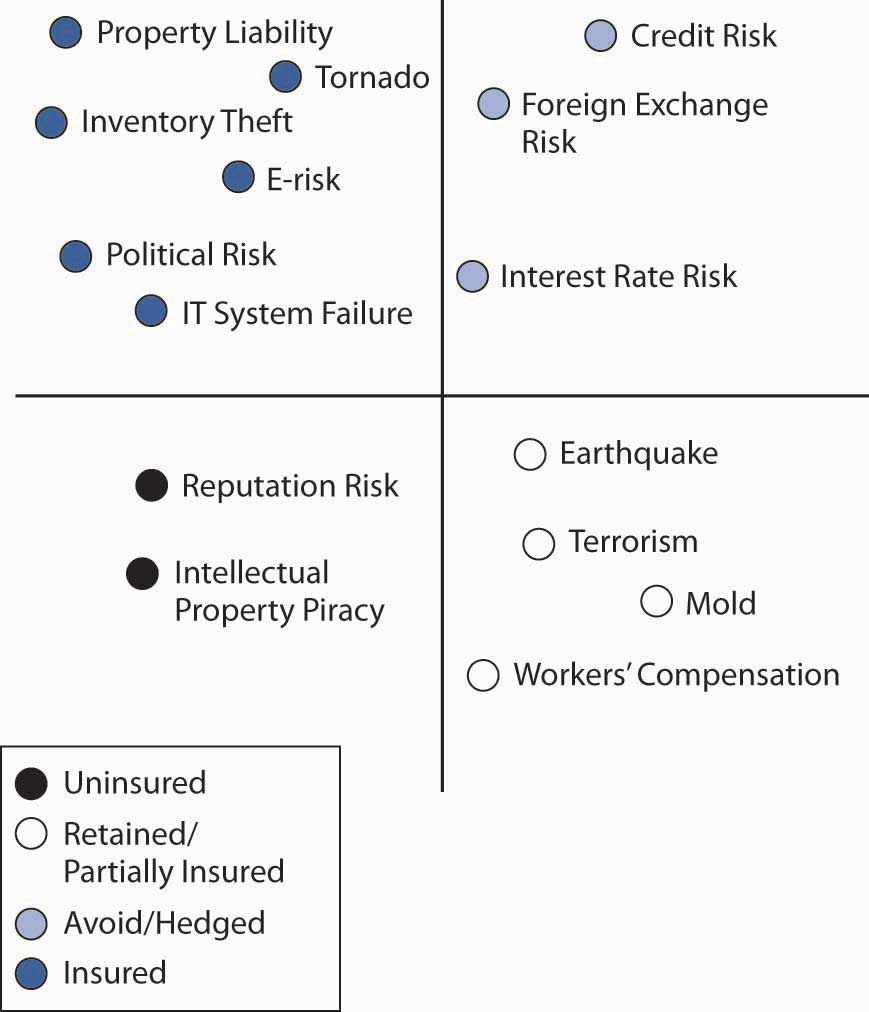
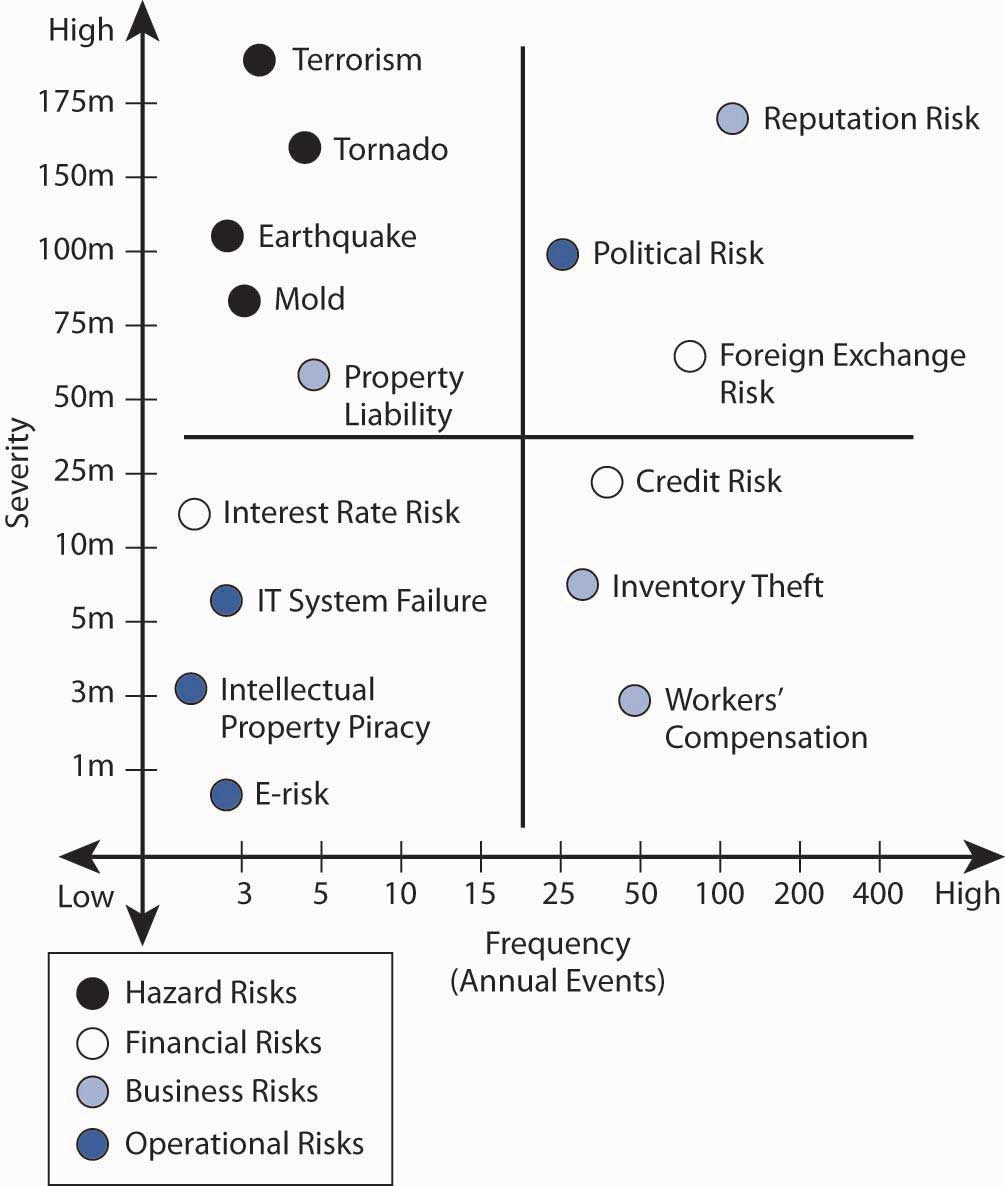
Start with identifying your risk register as a living document, not a PDF you attach to an annual report. I've seen agencies use Confluence, Notion, SharePoint, and basic spreadsheets. The tool doesn't matter nearly as much as the process around it. The register needs to be updated quarterly minimum, and the update should require actual sign-off from the department heads whose risks are being tracked. For assessment, use a standard 5x5 matrix. Likelihood against impact, both on five-point scales. Yes, it's simple. No, it's not inadequate. Most sophisticated models used in the public sector are just fancy ways of producing the same categories with more steps. What matters is that every risk gets scored consistently. The biggest problem I see is subjective variance. One director rates a cybersecurity breach as "medium likelihood" while another rates it "high" using the same data. That inconsistency makes the entire register unreliable. Mitigation planning follows the risk hierarchy: eliminate, reduce, transfer, accept. Government agencies have a particular problem here because transferring risk through insurance or outsourcing is heavily constrained by procurement rules and fiscal policies. You can't just buy your way out of most operational risks the way a private company might. This means reduction and acceptance end up being the primary strategies, which is why the quality of your risk controls matters enormously.
Monitoring should be built into existing reporting cycles. Don't create a separate risk review meeting if you can avoid it. Attach risk register updates to budget planning, strategic planning, and audit preparation. If risk management requires additional meetings, it will be deprioritized every time against the work that keeps the agency running.
Get the Full Details
A real example from my experience
I was working with a county health department that had a legitimate gap in their risk register around data interoperability between legacy systems. Their old patient records system couldn't communicate with the new one they'd implemented three years prior. This created a documented risk of data loss during transition, but the risk treatment plan had just said "monitor" and nothing else. Two years later, during a pandemic surge, they needed historical patient data across both systems simultaneously. The manual reconciliation process took four days. Four days when they were admitting patients at twice normal capacity. The workaround I helped implement was a lightweight middleware layer that pulled data from both systems on a nightly schedule and presented it through a unified dashboard. It wasn't elegant. It cost about $40,000 over three months in contract work, and it required IT staff who didn't want to touch the legacy system. But it closed the gap and the risk register was updated to reflect that the interoperability risk had been reduced from "high" to "medium" with ongoing monitoring. The key insight here is that risk treatment doesn't require capital projects. Sometimes it requires a practical bridge solution that fits the actual constraint set.
Things most beginners miss
Risk appetite in government is rarely defined explicitly. Private companies often have board-approved statements about how much risk they're willing to accept in different categories. Public agencies almost never do this. The result is that risk decisions become reactive. A scandal or audit finding suddenly makes previously accepted risks appear unacceptable overnight. This whiplash undermines credibility and makes staff cynical about the whole process. I recommend at least an informal documented statement, even if it's just a paragraph in your strategic plan that says where the organization draws the line on financial, operational, reputational, and compliance risk. Third-party risk is the category most agencies handle worst. You might have excellent internal controls but then contract with a vendor who has zero security posture. This happened to a state agency I consulted for recently. They had a routine risk assessment process for internal operations but treated vendor risk as a procurement checklist item. A cloud service provider they used for citizen data submissions had a breach that exposed names and addresses of 12,000 residents. The agency's own risk register showed zero exposure to that scenario because they hadn't considered the supply chain dimension. After that incident, they implemented vendor risk questionnaires modeled on the SIG (Shared Assessments Program) framework and required SOC 2 reports for any vendor handling citizen data.
The honest downsides
Risk registers become theater. This is the most common failure mode and it's not a flaw in the concept, it's a flaw in execution. When the register is completed by one person who doesn't have visibility into every department, when the assessments aren't challenged by subject matter experts, and when there are no consequences for the quality of the input, you end up with a document that looks thorough and is actually useless. I've seen this repeatedly. The workaround is to make the register a collaborative output, not an administrative one. Department heads should own their risk entries. That creates accountability and improves accuracy. Another limitation is that quantitative risk analysis is nearly impossible in most public sector contexts. You don't have historical loss data for most risk categories. You can't run Monte Carlo simulations on something like "reputational damage from a failed infrastructure project." This doesn't mean you abandon quantitative thinking entirely, but you should be honest about when qualitative assessment is the only option. Some organizations pretend their risk scoring is more precise than it is, which creates a false sense of security. Legacy systems and procurement restrictions will constrain your mitigation options more than you expect. This isn't a risk management problem. It's an organizational reality. The best risk frameworks in government are the ones that acknowledge these constraints upfront rather than designing treatments that can't be implemented.
Resources and tools
The ISO 31000 standard is the baseline reference. It's expensive to obtain but free summaries and implementation guides are available through various government websites. The NIST Risk Management Framework (RMF) is more detailed and specifically designed for federal agencies and their contractors. If you're working at the state or local level, it's still applicable and many states have adapted it for their own use. For practical implementation templates, the Government Accountability Office (GAO) publishes guides on risk management for federal agencies that are directly relevant to state and local governments as well. Their Principles for Fraud Prevention and Detection and Risk Management Guidance documents are freely available and more useful than most commercial frameworks because they're written by people who actually audit government operations. I also recommend looking at the COSO ERM framework, particularly the 2017 update. It's designed for private sector but the integration with strategy and performance aspects translates well to public sector strategic planning cycles. The public sector version of risk management that works best is one that's embedded in planning, not one that exists alongside it.
A note on measurement
Don't measure the success of your risk management program by the number of risks identified. That's a vanity metric. Measure it by whether the risks that actually materialized were the ones you had on your register. If your top ten realized incidents are all things you flagged six months ago, your process is working even if the register shows 200 risks. If your top incidents are surprises, your identification process is broken regardless of how many risks you've logged. This is harder to track than it sounds because agencies tend to underreport near-misses and incidents that don't meet formal reporting thresholds. Building psychological safety into your risk reporting culture matters as much as the framework itself. Staff need to know that flagging a risk won't be used against them politically or administratively. Without that, you'll get clean registers and messy outcomes.