What Actually Goes Into A Risk Management Plan For Non Profit Organization
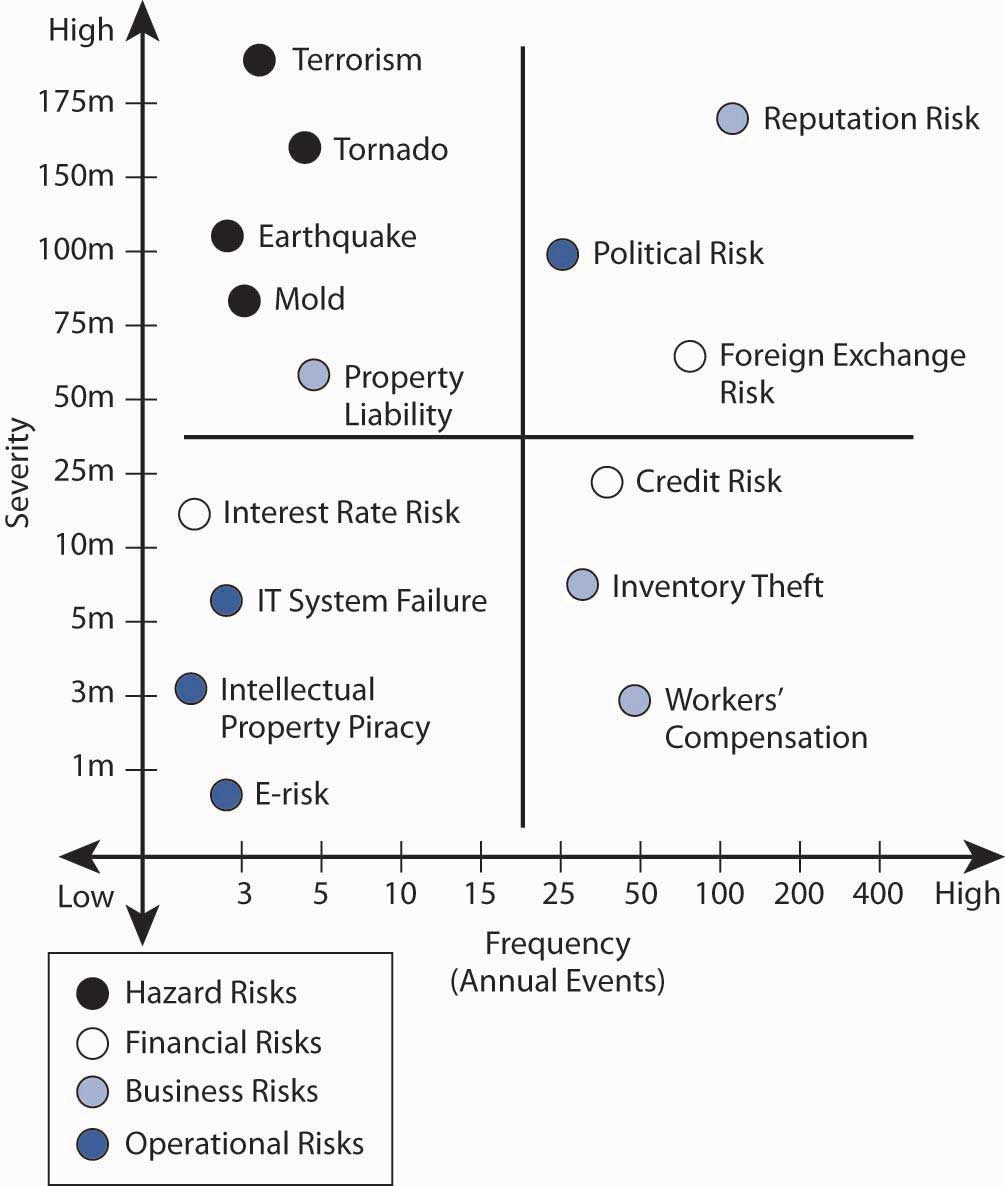
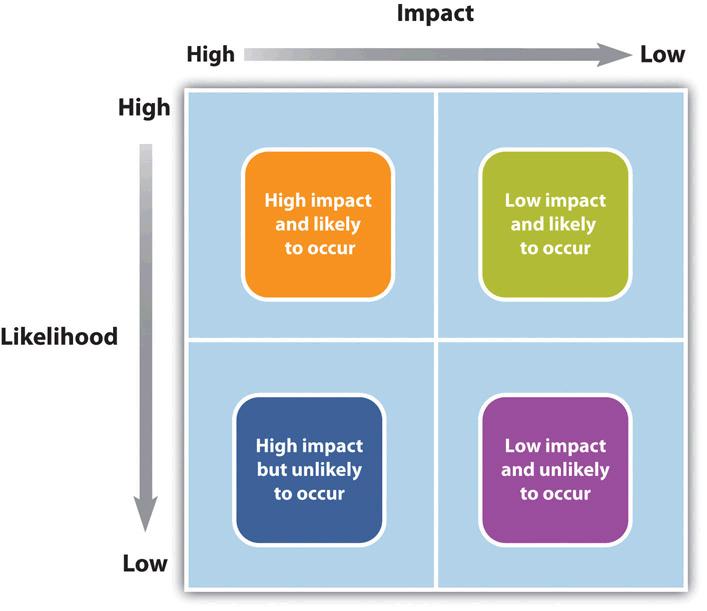
A risk management plan for a non profit is just a living document that identifies where things can go wrong, ranks those threats, and assigns someone to watch them. Most organizations treat it like a compliance checkbox. It isn't. It's a tool that prevents boards from scrambling when something breaks. I've sat through enough emergency board meetings to know the difference between a plan on a shelf and a plan that actually gets used. Start by mapping your operations, not your mission statement. The mission doesn't face cyberattacks or donor lawsuits. The operations do. Take a walk through your physical offices, your fundraising events, your online donation systems, your volunteer coordination processes, and your staff workflows. Write down every activity where something could plausibly cause financial loss, legal trouble, reputational damage, or harm to the people you serve. I once worked with a small homeless services nonprofit that had a comprehensive strategic plan but zero risk documentation until a volunteer drove an organization van into a wall. The driver was fine, the passenger wasn't, and the insurance claim exposed the fact that their volunteer driver screening process consisted of checking a driver's license and a background check they'd never actually verified. That incident forced us to build a proper risk register from scratch, starting with vehicle operations and contractor management. Create a risk register as a simple spreadsheet. Each row is a risk. The columns are: risk description, category, likelihood (rare, unlikely, possible, likely, almost certain), impact (negligible, minor, moderate, major, catastrophic), risk level (a calculated combination), current controls, residual risk level, risk owner, and review date. That's it. You don't need fancy software. Notion or Google Sheets works fine for organizations under fifty staff. Once your register is populated, prioritize the risks by risk level, not by how loudly someone in the boardroom complains about them. That's a common mistake. The board will naturally focus on risks that scare them personally rather than risks that are statistically most dangerous.
Assign each risk a risk owner. This should be a named person, not a title. "The Executive Director" is not an owner. "Maria Chen, Executive Director" is. When accountability is vague, risks get deprioritized until something goes wrong and everyone claims they weren't responsible.
Categories That Matter More Than Others
For nonprofits, the highest-impact risks usually cluster in these areas: Fiduciary and financial risk: Grant compliance violations, mismanagement of restricted funds, inadequate financial controls around spending. I've seen organizations lose multi-year government contracts because their expense reports didn't meet grant-specific documentation requirements. The risk wasn't losing money directly. It was losing the ability to receive future funding. That's a fiduciary risk most nonprofits don't track properly. Operational risk: Key person dependency, technology failures, volunteer management gaps, facility issues. A nonprofit losing its sole program director without a succession plan is a textbook operational risk that causes more damage than any board member realizes until it happens. Document your critical position dependencies explicitly.
Get the Full Details
Reputational risk: Social media controversies, donor complaints going public, partnerships with questionable organizations. I once had to help an organization assess a partnership with a corporate sponsor that had a publicly documented history of labor violations. The board vote was split 4-3 in favor of accepting the money. The risk management plan flagged it as high reputation risk with medium financial benefit. They declined the sponsorship. Six months later, a local journalist published an investigative piece tying that same corporation to a scandal involving the community the nonprofit served. The decision saved relationships that would have been impossible to repair after the fact. Legal and compliance risk: Employment law violations, data privacy breaches, regulatory noncompliance, insurance coverage gaps. Nonprofits are not exempt from employment law. The assumption that "we're a charity, we get a pass" causes real legal exposure. Volunteer injuries, unpaid intern disputes, and whistleblower complaints all fall under this category. Program delivery risk: Services failing to reach the intended population, program outcomes not being met, dependency on a single funding stream for a core program. If your entire literacy program depends on one foundation grant and that grant cycle ends, you have a program delivery risk that should be on your register with a clear mitigation strategy.
The Part Nobody Talks About: Residual Risk
After you implement controls, recalculate the risk level. The difference between your inherent risk and your residual risk is your mitigation effectiveness. If you still have a high residual risk, either add more controls or accept the risk formally with board documentation. Accepting a risk without writing it down is not risk management. It's negligence disguised as pragmatism. I've reviewed plans where every risk was marked "low" after controls were applied, but the controls described were things like "we try to stay compliant" and "staff are aware." Those aren't controls. Controls are specific actions: monthly bank reconciliations performed by someone who doesn't handle deposits, dual authorization for expenditures over a defined threshold, annual cybersecurity audits, documented incident response procedures with named contacts. Review the full register quarterly at minimum. Update it immediately when something changes — a new grant, a staff hire, a facility move, a partnership shift. The document should be a working tool, not an annual exercise. When I've seen this work well, the executive team spends about twenty minutes in a standing meeting going through any register changes since the last review. Twenty minutes. That's all it takes to keep it alive. The biggest failure mode is creating the plan in isolation. If the executive director drafts it alone and presents it to the board for approval, it will be incomplete and unrealistic. Risk owners need to contribute their section. Program directors know their program risks better than anyone. Development staff understand donor-related risks. The plan should be collaborative, even if the executive director owns the final document.
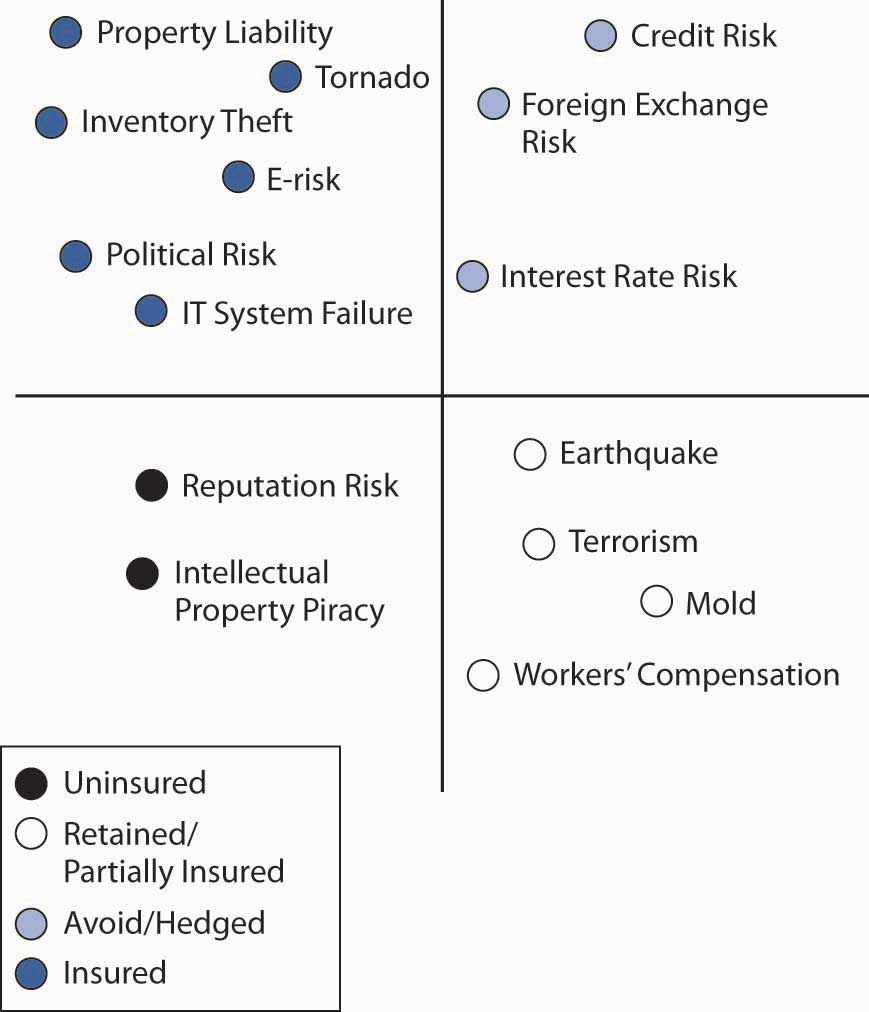
Another pitfall is treating the risk register as finished after the first draft. A static register is worse than useless because it creates false confidence. The version control matters. Keep older versions. Note what changed and why. When an auditor or funder asks to see your risk management process, showing iteration history demonstrates that the plan is actually used. Insurance is not a risk management plan. Insurance is a financial transfer mechanism for specific types of risk. It doesn't prevent anything. It doesn't reduce likelihood. It pays out after the fact. Some organizations conflate their insurance portfolio with their risk management strategy. They need both. The insurance covers catastrophic financial loss. The risk management plan reduces the probability and severity of those losses in the first place.
What This Approach Cannot Do
A risk management plan cannot predict black swan events. The pandemic, a sudden natural disaster, a once-in-a-decade economic collapse — these are outside the scope of any reasonable planning document. What it does is make your organization more resilient to the risks that are actually probable and within your control to influence. Be honest about that limitation. Presenting the plan as comprehensive protection is misleading to donors, boards, and staff. It's a structured approach to managing known unknowns, not a crystal ball. For smaller nonprofits with extremely limited staff, maintaining a full register alongside daily operations can feel burdensome. In those cases, compress the register to the top ten risks and review them monthly instead of quarterly. A focused, active plan beats a comprehensive, abandoned one every time.
Where To Find Templates And Tools
Guidestar by Candid publishes nonprofit risk management resources that are free and practical. The Council on Foundations has template registers. TechSoup offers discounted project management and document collaboration tools that can host your register. Many state nonprofit associations also publish sample risk management frameworks tailored to local regulations. The specific form matters less than the discipline of keeping it current. Build the register. Assign owners. Review it regularly. Adjust when things change. That's the entire process, and it's significantly more valuable than the version most nonprofits produce once and file away.