What a Risk Management Policy Template Actually Looks Like in Practice
A risk management policy template is just a structured document that tells your organization how to identify, assess, and respond to risks. Most companies skip the template part and just wing it with spreadsheets and tribal knowledge. That works until something actually goes wrong and nobody can point to a documented process during an audit or incident review. I spent years helping teams build these out for mid-market companies, and the common pattern is pretty predictable. Someone asks for a template, downloads a generic one from the internet, and then spends the next six months filling in blanks with half-baked definitions that don't match how their team actually works. The template becomes a shelf decoration.
Building a Risk Management Policy Template That Actually Gets Used
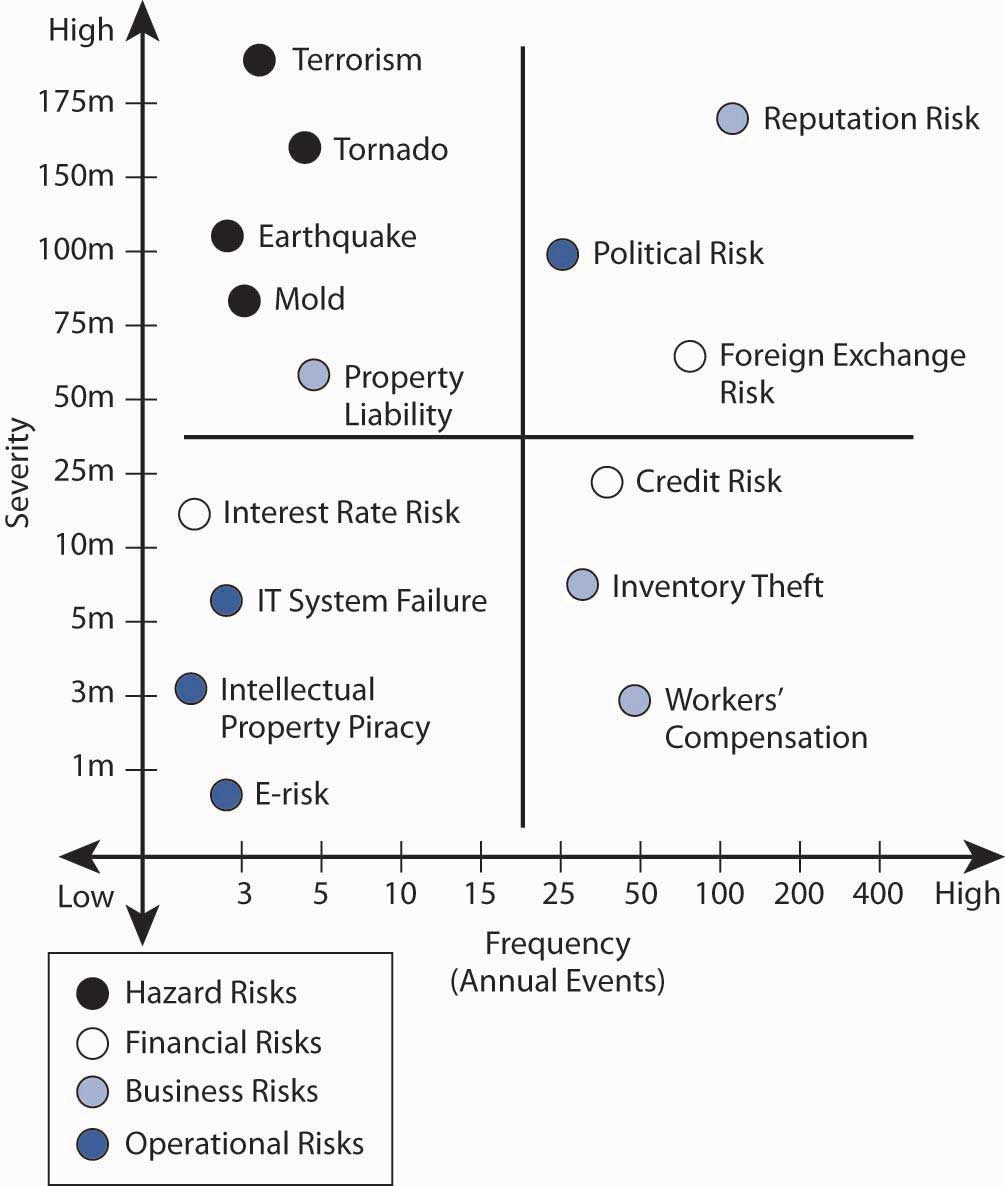
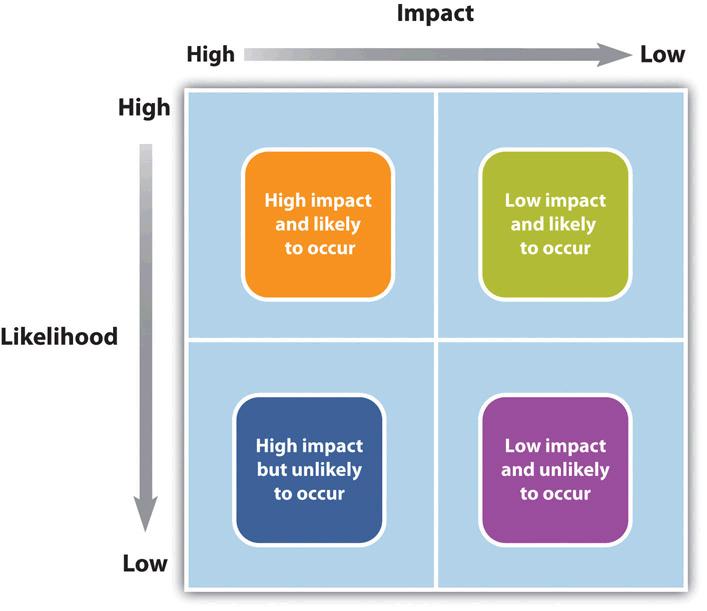
Start with the risk register structure. This is the core of everything. A basic register needs at minimum: risk ID, risk description, category, likelihood rating, impact rating, risk score, existing controls, control gaps, risk owner, mitigation action, status, and review date. Don't overcomplicate it on day one. The section most people mess up is the risk scoring methodology. You need a defined scale, and it can't be arbitrary. I recommend a simple 1-5 scale for both likelihood and impact, multiplied to get a risk score ranging from 1 to 25. The trick is making sure everyone interprets those numbers the same way. I once worked with a team where the "impact" column was essentially meaningless because nobody agreed on what a 4 versus a 5 meant. One department treated any dollar loss as catastrophic. Another only counted operational downtime as impact. We fixed it by defining impact across four dimensions: financial, regulatory, reputational, and operational, each with specific thresholds. So a 4 in financial might mean between $100K and $500K in losses, while a 5 is anything above that. Same for the other dimensions. It took two meetings to align on the definitions, but after that, the risk register scores stopped being decorative numbers. Your policy template should also include a clear escalation framework. That means defining which risk scores require executive attention, which go to middle management, and which the team handles autonomously. A typical threshold I see work: scores of 15 and above trigger immediate escalation to the C-suite or board-level risk committee. Scores between 8 and 14 go to department heads with a requirement for a formal mitigation plan within 30 days. Anything below 8 gets logged and reviewed during the next quarterly cycle.
The review cadence section matters more than most templates include it. Risk assessments expire. Not through any mystical decay process, but because the business changes. New products launch. Markets shift. Regulatory landscapes evolve. A risk register that hasn't been formally reviewed in six months is basically fiction. Build in a mandatory quarterly review cycle for high-priority risks and an annual full-scope refresh for everything else. One thing that comes up repeatedly in my experience is the intersection between risk management and incident response. A policy template that treats these as separate domains creates a gap. When an incident actually occurs, the response team shouldn't be pulling together ad-hoc decisions about whether something is acceptable risk or not. The policy should explicitly reference the risk register as the baseline for incident prioritization. If a security breach happens and the affected system has a pre-assessed risk score, you already know how seriously to treat it based on what was documented before anything went wrong. There is a legitimate downside to building these templates out. They can become bureaucratic weight that slows down decision-making, especially in fast-moving environments. I've seen startups adopt overly detailed risk frameworks that added more process than protection. If your organization has fewer than 50 people and moves quickly, a simplified version with just a risk register and basic escalation rules is often better than a full ISO-aligned policy document. The template should match the scale of your operation, not the scale of the largest frameworks you can find online.
Get the Full Details
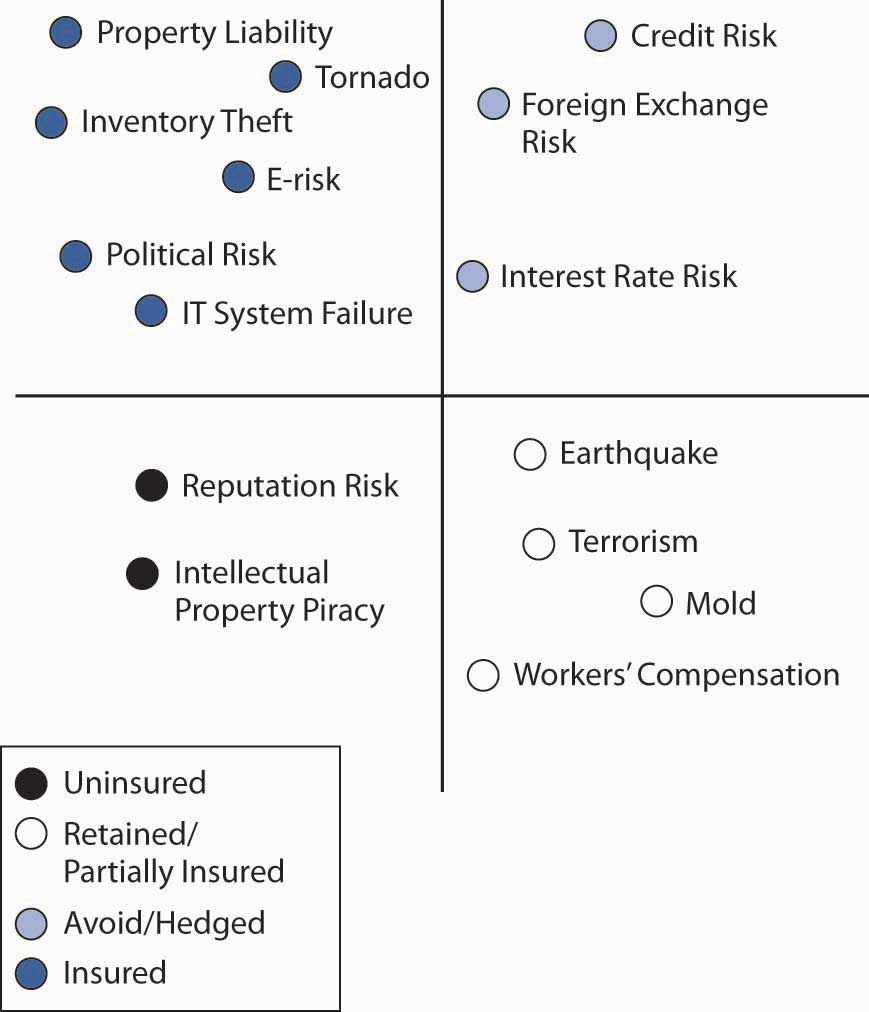
Another counter-intuitive point: the best risk management policy templates have more content in the "what we don't do" section than most people expect. Explicitly stating that certain risks will not be mitigated, accepted as-is, or transferred through insurance prevents the common failure mode where every risk gets a mitigation action and nothing gets prioritized. Acceptance is a valid risk strategy. Writing it down formally is what makes it a strategy instead of negligence. You can find standard Risk Management Policy Template documents through various professional bodies and consulting firms. The ones from ISO-aligned sources tend to be comprehensive but heavy. For most organizations, adapting a simpler template and filling it with context-specific definitions produces better results than trying to implement a full certification framework from day one.
Key Sections Every Template Needs
Purpose and scope. This should be one paragraph. What the policy covers, who it applies to, and what it does not cover. Getting this right prevents the common confusion where departments treat the policy as either irrelevant to their work or as an all-encompassing mandate. Risk assessment methodology. The scoring scales, the calculation approach, the criteria for high and low risk. This section is where you define the language everyone uses going forward. If you get this wrong or leave it vague, the rest of the template is just paperwork. Roles and responsibilities. Who owns the risk register. Who performs assessments. Who approves risk acceptance decisions. Who reviews and updates. This is not optional. The #1 reason risk frameworks fail is that nobody had clear ownership assigned to them.
Risk treatment options. Accept, mitigate, transfer, avoid. Define each one briefly with examples relevant to your industry. Treatment selection should follow a decision tree based on risk score and organizational appetite. Reporting requirements. How often risk assessments are reported, to whom, and in what format. Internal reporting and external reporting if applicable. This ties directly into your escalation framework from earlier. Policy review and revision. How the policy itself gets updated, who approves changes, and how frequently. The policy should require its own periodic review, typically annually or when significant organizational changes occur.

If you're building this from scratch, start with the risk register template, then add the surrounding policy sections around it. The register is the living document. The policy is the rulebook that governs how the register is maintained. Most people write them in the opposite order and wonder why the policy gets ignored.