How Self-Evaluation Actually Works in a Risk Management Context
A risk management self-evaluation is basically an internal audit where your team rates how well existing controls are performing against the risks they were designed to address. Most people treat it as a checkbox exercise. That is why they fail. The difference between a useful evaluation and one that produces zero actionable output usually comes down to specificity in the scoring criteria and whether leadership actually funds the remediation plan afterward. I have seen organizations spend weeks building elaborate spreadsheets with seventeen-point scales, only to realize six months later that nobody could agree on what a rating of "three" versus "four" actually meant in practice. We solved this by anchoring every score to a concrete observable behavior or document. Instead of asking "is this control adequate?" we ask "can the auditor produce evidence of this control operating without exception in the last quarter?" That one change made the whole process defensible and reproducible.
Risk Management Self Evaluation Examples
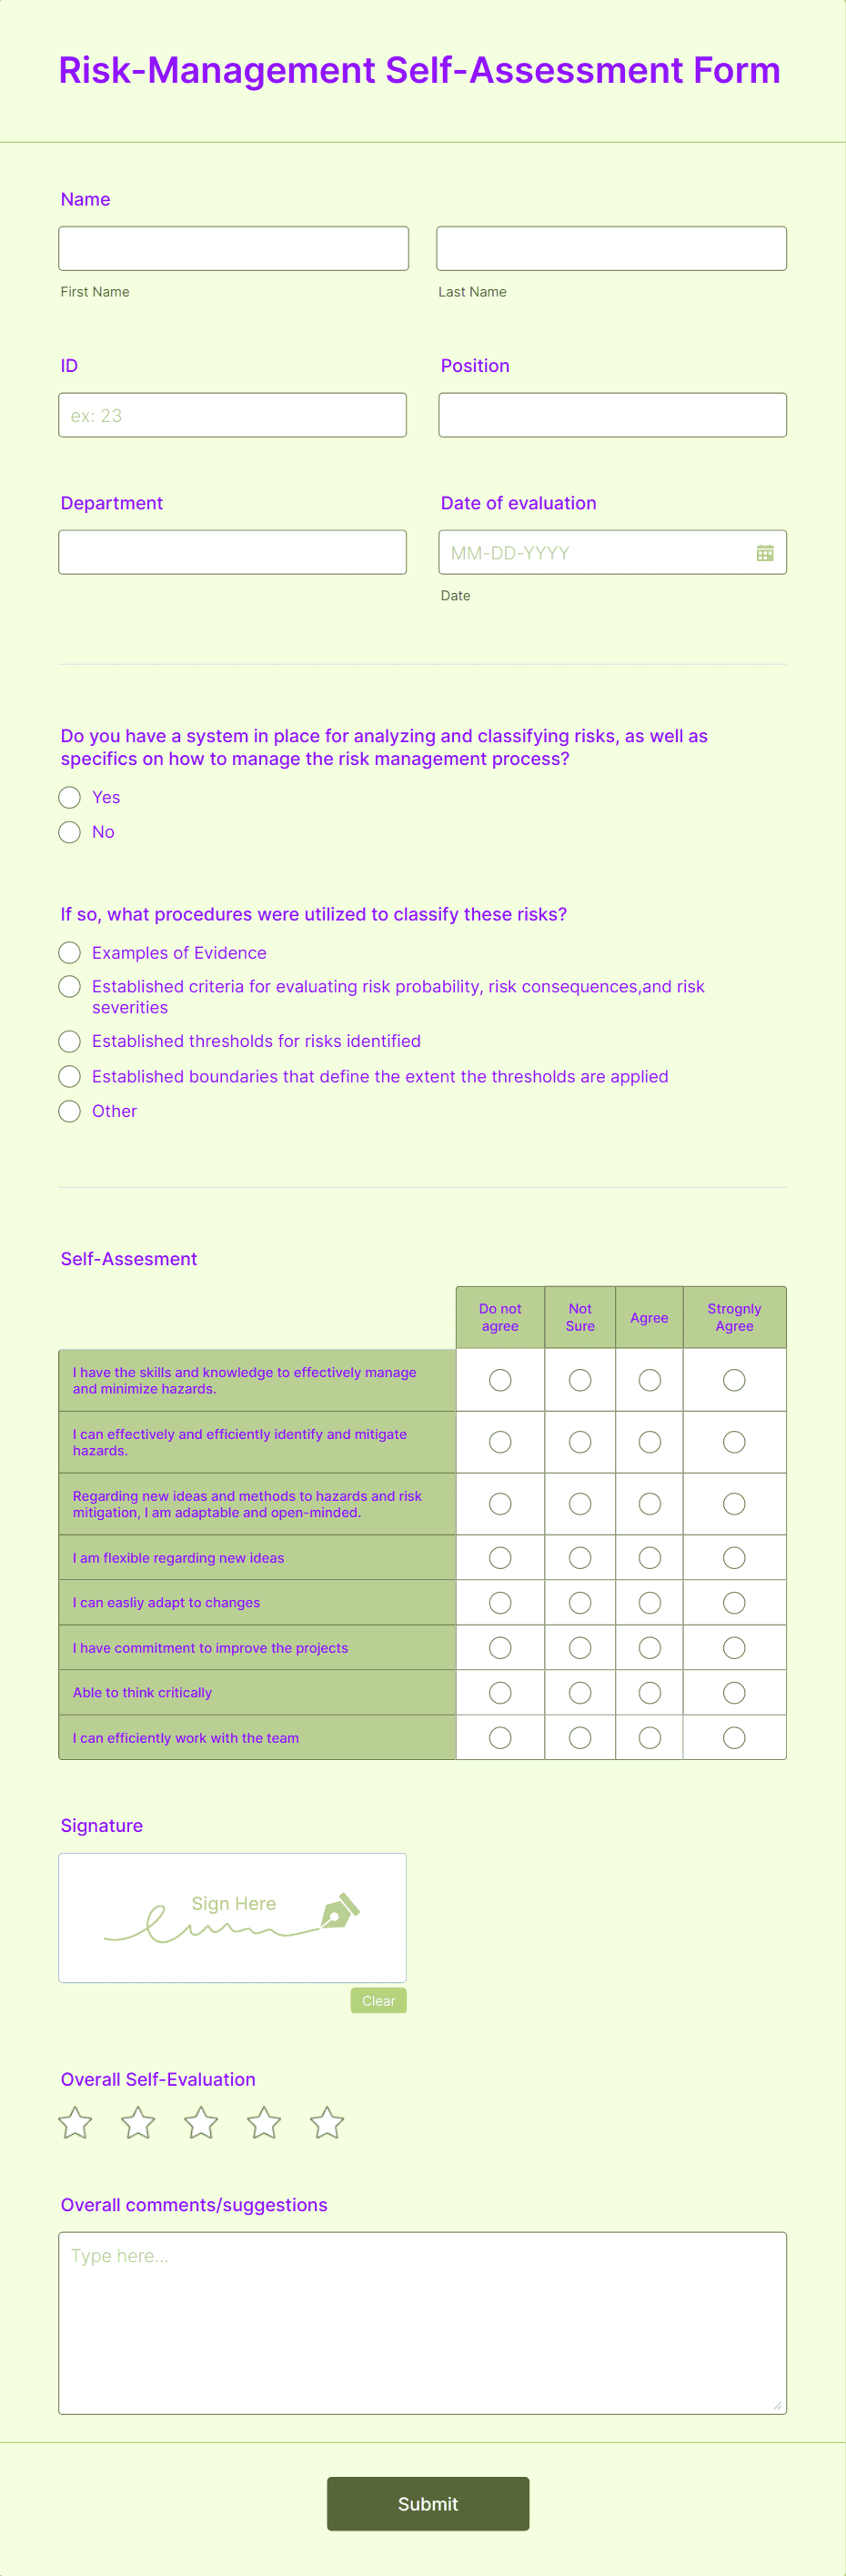
Here is a breakdown of how these evaluations typically function across different risk categories, along with the specific formats that tend to survive contact with reality. Operational Risk Self-Evaluation This is the most common type and also the most poorly executed. The standard format asks teams to list their top five operational risks, rate the likelihood and impact of each, document the existing controls, and score control effectiveness on a five-point scale. The problem is that most people rate impact based on worst-case scenarios they invented rather than historical data. When I worked on a project for a mid-size logistics company, the team rated their warehouse fire risk as "critical" because they had never experienced one, not because they had any evidence. The workaround was pulling insurance claims data and incident reports from the previous ten years. That single adjustment shifted three of their five "critical" ratings down to "low" and freed up budget for risks that actually mattered.
Compliance Risk Self-Evaluation Regulatory environments change fast. A self-evaluation in this space needs to track not just whether you meet current requirements but whether your monitoring process can detect when requirements shift. The practical format includes a matrix mapping each regulation to your control, the frequency of review, the owner responsible, and the date of the last verification. One thing beginners miss is that compliance evaluations often fail because they track documents instead of behaviors. Having a written policy is not the same as having a control that works. In my experience, the most reliable signal is testing whether the control would catch a deliberate attempt to bypass it. We ran simulated non-compliance tests quarterly and scored based on detection rates rather than policy existence. Financial Risk Self-Evaluation
Get the Full Details

Financial risk self-evaluations typically cover credit risk, liquidity risk, market risk, and fraud risk. The formats vary but generally include exposure calculations, stress test results, threshold breach analysis, and remediation timelines. A common structural flaw is treating all financial risks as independent when they are often correlated. During a downturn, credit risk and liquidity risk hit simultaneously and reinforce each other. I built a correlation matrix into our evaluation framework that forced reviewers to assess risk combinations, not just individual risks. This caught a situation where our trade concentration risk and counterparty risk were both moderate individually but catastrophic in combination. Cybersecurity Risk Self-Evaluation This has become standard across industries even for organizations that do not consider themselves technology companies. The format usually aligns with NIST CSF or ISO 27001 controls. The evaluation asks teams to map current security posture against a recognized framework, identify gaps, prioritize remediation, and assign owners. The counter-intuitive insight here is that most self-evaluations in cybersecurity measure coverage rather than effectiveness. You can have ninety percent of NIST controls documented and still be vulnerable to the one twenty percent scenario that matches your actual threat landscape. We shifted our evaluation to focus on attack surface reduction and detection response times rather than control checklist completion. The resulting numbers were uglier but more useful.
Strategic Risk Self-Evaluation These are the hardest to evaluate honestly because strategic risks involve forecasting and judgment calls that senior leadership may not want to scrutinize. The format typically includes scenario analysis, external environment scanning, competitive positioning assessment, and strategic initiative risk rating. The main failure mode is optimism bias baked into the scoring. I have seen strategic risk evaluations where every initiative was rated as having manageable risk because the people scoring them were the same people who designed the initiatives. The fix was introducing external peer review on at least one strategic risk assessment per cycle, even if it was just a colleague from a different department.
What a Practical Self-Evaluation Template Looks Like
A usable template should include these fields at minimum: risk category, risk description, inherent risk rating, existing controls listed with owners, residual risk rating after controls, control effectiveness score, evidence location, next review date, and remediation action items with deadlines. That is fourteen fields. Anything fewer and you are probably skipping something important. Anything more and people stop using it. The control effectiveness score is where most evaluations go wrong. A five-point scale without behavioral anchors is meaningless noise. "1 = ineffective, 5 = fully effective" tells a reviewer nothing about what level four looks like versus level five. Your anchors should describe observable states. For example: Score 1: Control does not exist or has not operated in over six months.
Score 2: Control exists but has documented exceptions that were not remediated. Score 3: Control operates but requires manual intervention for every instance. Score 4: Control operates with automation except for edge cases.
Score 5: Control operates consistently with automated monitoring and exception reporting. This kind of anchoring cuts the evaluation time for a trained reviewer from about forty-five minutes per risk area down to roughly twelve minutes, because there is less ambiguity to debate. It also makes the results defensible during an external audit.
Common Pitfalls That Undermine the Process
Timing is one issue. Scheduling self-evaluations at the same time as budget planning or year-end financial close guarantees rushed results. We learned this the hard way when our Q4 evaluation produced ratings that did not match the incident reports coming in from the same period. The gap was enormous. Now we schedule evaluations in the first two months of the fiscal year when data is fresh and people have capacity. Another pitfall is conflating risk identification with risk evaluation. Listing risks is fast. Evaluating them properly takes time. I have seen teams produce three hundred risk entries in a single session and then spend zero effort scoring them. Three hundred unranked risks are not a risk register. They are a wish list. A better approach is limiting each evaluation cycle to the top fifty risks and requiring documented justification for why anything outside that list was excluded. The third major failure mode is treating the evaluation as a report to file rather than a planning document. If the output does not feed directly into your risk treatment plan with assigned owners and deadlines, the exercise is wasted. I once reviewed an evaluation that took two hundred hours to complete and resulted in zero remediation actions because no one was held accountable for closing the gaps it identified.
When Self-Evaluation Falls Short
Self-evaluation has real limitations. It cannot replace independent external audit because the people evaluating their own work have blind spots and incentives to present things favorably. It is also weaker for emerging risks that have no historical precedent and no established control framework to measure against. For those situations, you need complementary methods like external threat intelligence reviews, red team exercises, or industry benchmarking studies. The evaluation process itself introduces distortion through several well-documented biases. Recency bias makes recent incidents inflate ratings while older risks fade. Confirmation bias leads reviewers to rate controls higher when they personally designed them. Groupthink causes teams to converge on average scores rather than challenge assumptions. None of these are fixable by making the form more elaborate. They require structural interventions like rotating evaluators, requiring dissenting opinions on high-stakes ratings, and cross-referencing self-assessment scores against independent data points like incident frequency or audit findings.
A Word on Implementation
Start small. Pick one risk category, build a proper template with anchored scoring criteria, run it once with a team that understands the definitions, and then iterate. Do not roll out a comprehensive evaluation framework across the entire organization on the first attempt. The most successful self-evaluation programs I have seen started as pilot projects in a single department, refined over two or three cycles, and only then expanded. The initial cycles will feel slow and awkward. That is normal. The third cycle is usually where the process becomes genuinely useful rather than just another meeting on the calendar. The real value of a risk management self-evaluation is not the document it produces. It is the discipline of forcing people to regularly examine whether their controls actually work and what happens when they do not. Without that discipline, the evaluation is theater. With it, even an imperfect process gives you more visibility than most organizations have.