What Risk Professional ERP Actually Means
A lot of people use this phrase interchangeably with Enterprise Risk Management (ERM) software modules found in SAP, Oracle, or Microsoft Dynamics. The term itself doesn't map to one single product. It refers to the combination of risk management capabilities embedded within ERP platforms, often supplemented by standalone GRC tools. Investopedia covers this space under its finance and business technology categories, and they generally describe it accurately enough for someone who just needs to understand the concept before a meeting. Here is the thing nobody tells you upfront: most organizations implement risk modules in ERPs incorrectly because they confuse compliance documentation with actual risk monitoring. The system becomes a checkbox repository rather than a decision-support tool. I watched this happen at a mid-size manufacturing company last year. Their SAP GRC setup had 47 risk workflows, but zero of them were pulling live data from operational sources. Everything was manually entered at month-end. The risk scorecard looked impressive in PowerPoint, but the actual exposure signals were six weeks old by the time anyone saw them.
Risk Professional Erp Investopedia Overview
The Investopedia entries on this subject tend to focus on the basic definitions: what an ERP risk module does, how it differs from traditional audit software, and the general categories of risk it addresses. They are fine as a starting point. The gap in those articles is the operational reality. An ERP risk system only works if someone has already mapped your processes correctly inside the ERP. A poorly configured ERP will produce a poorly configured risk model, regardless of which vendor brand you paid for. I learned this the hard way when a client insisted on importing their legacy risk framework into a fresh S/4HANA deployment without re-evaluating the underlying process maps. The migration preserved every broken workflow from the old system, including outdated approval chains that nobody used anymore. We spent three weeks cleaning up permission objects before the risk module would run at all. That is not a software problem. That is an organizational problem wearing a software mask.
How to Actually Set It Up
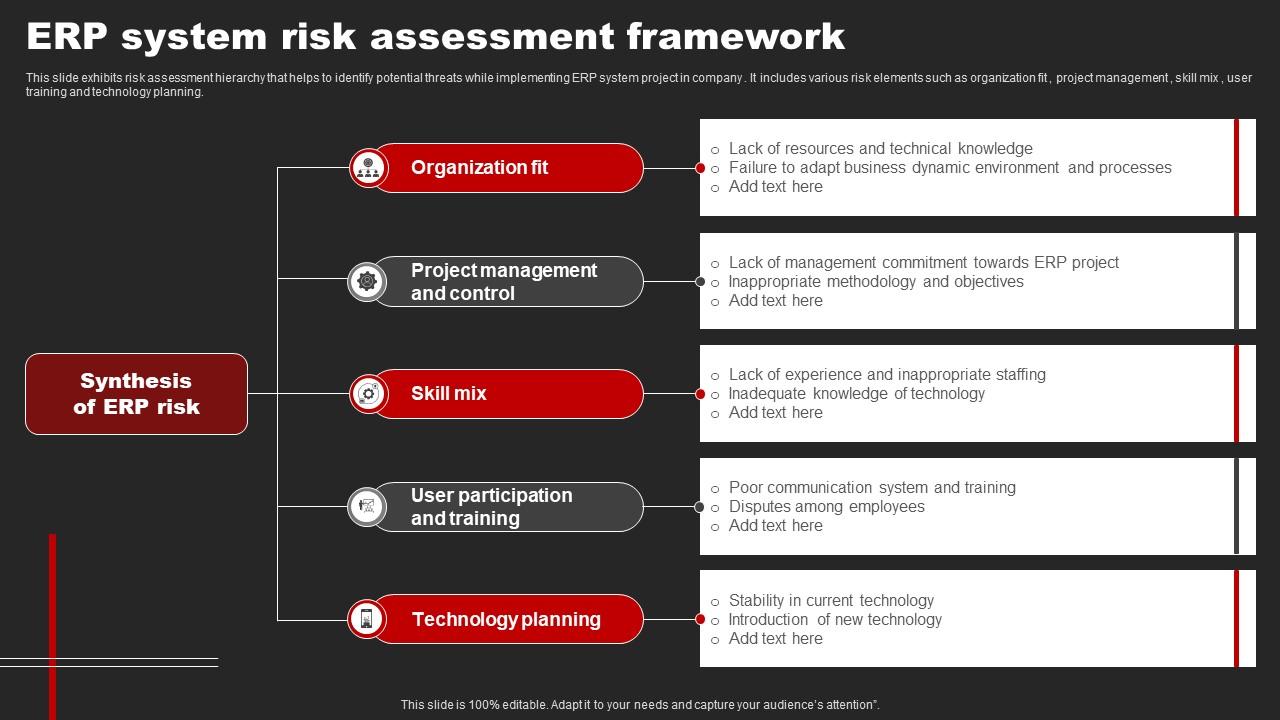
Start with process mapping, not software configuration. Document your key business processes at a level where each step has a clear owner, a defined trigger, and measurable output. If you cannot name the person responsible for a step, you cannot build a risk control around it. I have seen risk frameworks built on assumptions about who does what across departments that do not even communicate with each other regularly. The resulting control matrix is fiction dressed as governance. The practical sequence that works: First, identify your top 20 risks by impact, not by how loud they complain in committee meetings. Most organizations default to regulatory compliance risks because those are easiest to document. Operational and strategic risks tend to get deprioritized until something breaks. Second, for each of those 20 risks, identify at least one automated control that can be embedded in the ERP. Manual controls belong in a separate register. Third, configure the ERP to pull real-time or near-real-time data for those controls. If a control requires a human to export data from three different systems and paste it into a spreadsheet before the risk tool can see it, the control is not automated. It is theater.
Get the Full Details

The setup phase for a properly configured ERP risk module in a mid-market company typically runs 8 to 12 weeks. Not including the process mapping phase, which often takes another 4 to 6 weeks and is usually deferred because leadership wants to "just start configuring." That deferral is the most common reason these projects fail within the first year.
Common Mistakes That Cost Money
Over-configuring controls is the biggest waste I see. A colleague at a logistics firm once built a system that generated 340 risk indicators across five modules. Half of them produced no actionable alerts because the thresholds were set so conservatively that they never triggered. The other half triggered daily, causing alert fatigue among the risk team. We trimmed it down to 67 indicators by keeping only those that had a direct financial or operational consequence and setting thresholds based on actual historical deviation data rather than arbitrary percentages. Another frequent mistake is treating risk assessment as an annual event. The ERP can run continuous monitoring if you design it that way. I worked with a retail chain that scheduled risk reviews quarterly instead of monthly. During a supply chain disruption in Q3, they did not detect a significant inventory valuation risk until the quarterly review, by which point the write-downs had already been recorded in the wrong period. Moving to monthly reviews cut their detection lag from an average of 45 days to about 12 days. Permission management deserves more attention than it gets. ERP risk modules inherit whatever role confusion exists in the base system. If your ERP has overlapping roles between procurement and accounts payable, your risk module will flag conflicts that are actually impossible to resolve without restructuring the entire access model. We resolved this by running a role-cleanup exercise before enabling the risk module. It took two weeks and required sign-off from four department heads, but it prevented an ongoing configuration nightmare.
What the Software Can and Cannot Do
ERP risk modules are good at tracking process-level compliance, detecting transactional anomalies, and producing audit trails. They are not good at strategic risk assessment, scenario planning, or anything that requires judgment about external market conditions. You will not find a reliable early warning for a geopolitical supply risk or a competitive threat in your ERP module. Those require separate intelligence inputs and analytical frameworks that the ERP was never designed to handle. The module also cannot fix poor data quality. I have watched risk teams spend countless hours chasing discrepancies between the ERP and external sources, only to discover that the root cause was duplicate vendor records created during an acquisition integration. No amount of risk configuration will compensate for that. The fix is data governance, not risk management software. If you need something that handles qualitative risk assessment and strategic scenario modeling alongside your ERP risk data, a dedicated risk analytics platform like ServiceNow GRC, MetricStream, or RSA Archer can integrate with your ERP but provide capabilities the ERP alone cannot. They are more expensive and require more maintenance, but they fill the gap that ERP modules consistently leave open.
Practical Steps to Get Started
Request a demo that includes your actual business processes, not the vendor's standard sample data. Most vendors will show you a clean demo environment with perfect data. That tells you nothing about how the system will behave with your messy reality. Ask them to walk through a scenario where a purchase order exceeds budget, a material shortage disrupts production, and a key vendor goes insolvent, all within the same workflow. Watch how the system responds. Allocate budget for the first year that covers configuration, data migration, and at least one process-mapping sprint. Do not allocate it solely to licensing. I have seen projects fail because the license was paid for but there was no funding left to properly configure the controls or train the internal team that would own the system after implementation. Assign a single internal owner before you go live. The risk module should not report to three different departments simultaneously. One owner, with support from process owners in each relevant department, produces cleaner results than a committee structure. Accountability is the difference between a system that gets used and a system that collects digital dust.
The Investopedia descriptions will give you the vocabulary. Your actual implementation will depend on how honestly you assess your process maturity, how much data cleanup you are willing to do, and whether you accept that an ERP risk module is a tool for monitoring known risks, not a crystal ball for unknown ones.