Starting a Risk Vulnerability Assessment without a plan is how you waste three weeks and learn nothing
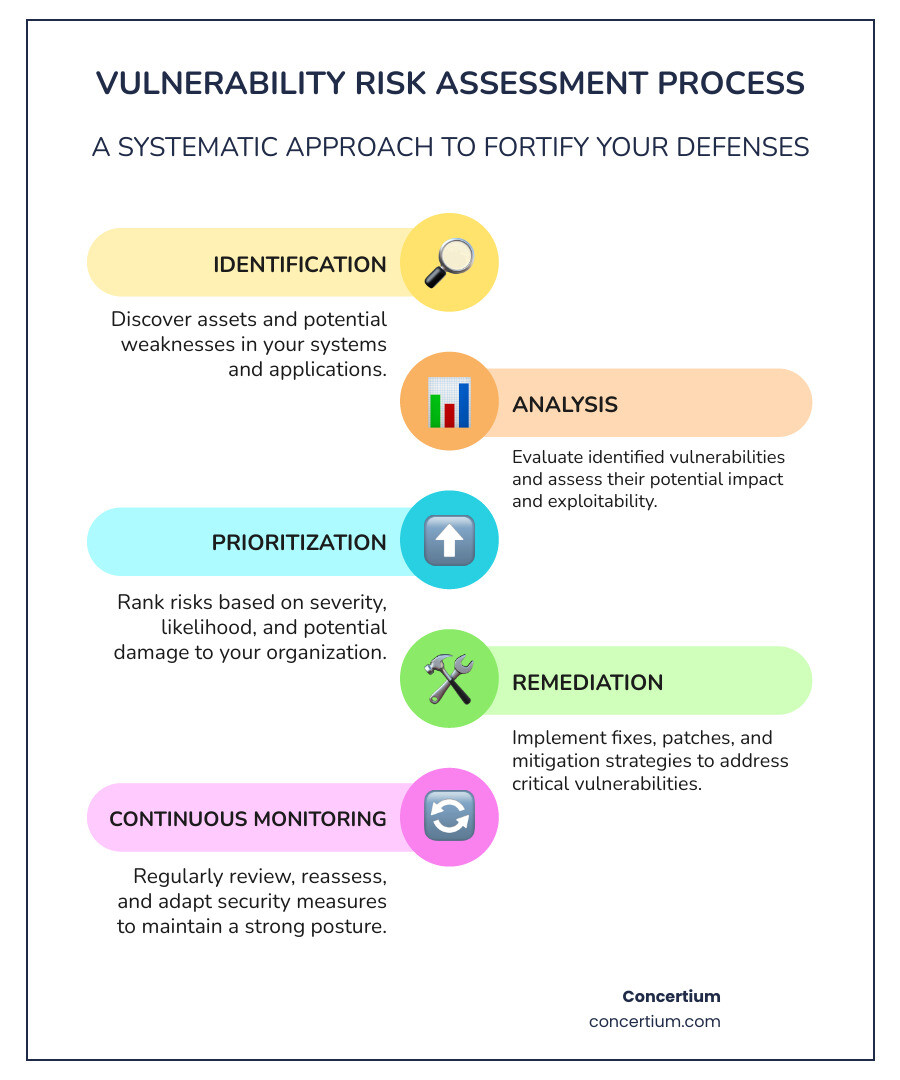
I've been running through these assessments for long enough that the novelty wore off years ago. The process itself isn't rocket science, but most people screw it up because they treat it like a checkbox exercise instead of a living document. Here is how I actually do it when I walk into a new environment. First, you scope the asset boundary. Not the network diagram from 2021 that someone printed and framed, the actual current state. I start by pulling CMDB data and cross-referencing it with active DHCP leases, DNS records, and any cloud provisioning logs. Assets sitting outside those sources are your blind spots, and they are always where the problems hide. In one engagement, I found a staging database with production-level credentials running on an IP range that wasn't in the CMDB at all. Someone had spun it up for a migration that never happened and forgot about it. Six months later it would have been the incident that kept someone up at 3 AM.
The Risk Vulnerability Assessment Framework
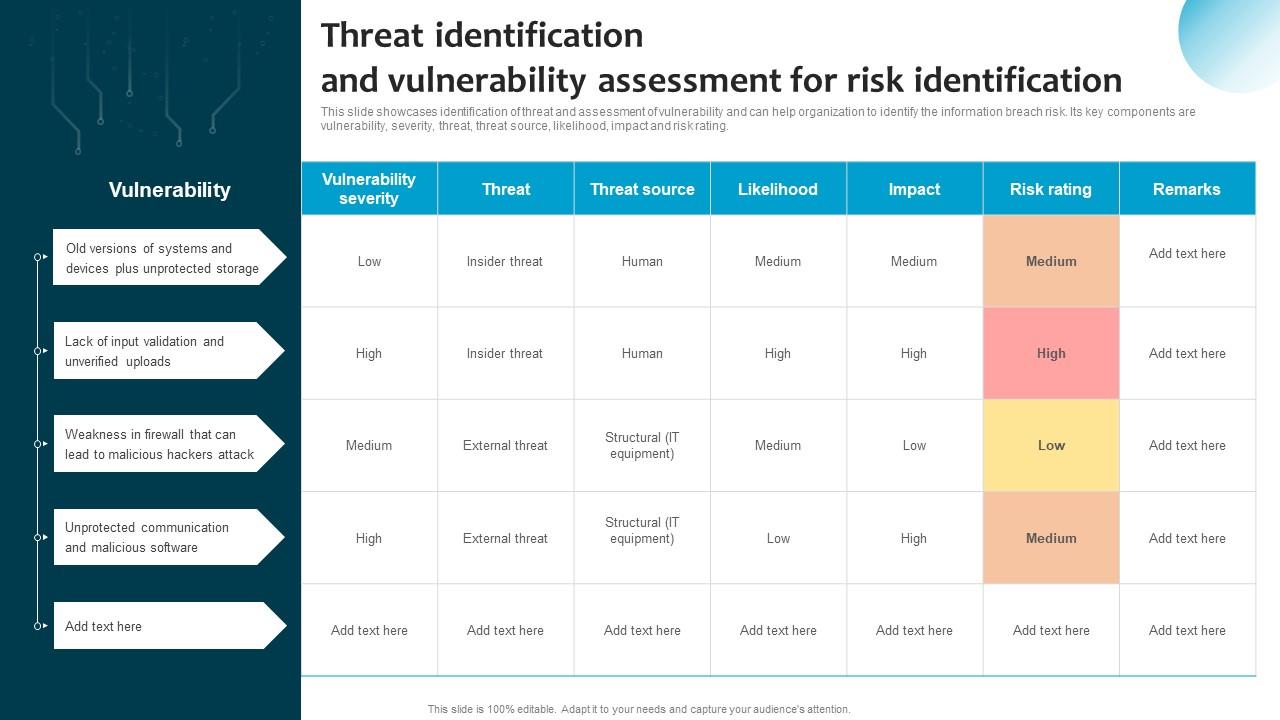
Once assets are mapped, you run discovery. This is where tool selection matters more than most people admit. Nmap with targeted service detection gives you port and version data fast. For web applications, something like OWASP ZAP or Burp Suite Pro will outperform manual scanning every time. For cloud environments, you need CSPM tools—Prowler for AWS, Cloud Inspector for Azure. Running the wrong scanner against the wrong target is why half these assessments come back garbage. A network vulnerability scanner will miss an SSRF flaw in a GraphQL endpoint. A web app scanner will miss an unpatched Log4j instance hiding on a non-standard port. After scanning, you move to validation. Raw scan output contains false positives by the hundreds if you leave it alone. I flag anything CVSS above 7.0 for immediate manual verification. Anything below that gets triaged based on context. A critical finding on an isolated IoT thermostat carries different weight than a critical finding on your payment gateway. You need to understand the business function before you assign risk score. This is where most people I consult with jump straight into remediation without finishing the risk calculation. They see "SQL injection" and start patching. But a SQL injection in a dormant feature nobody uses, behind a WAF rule that's already blocking the payload pattern, has a completely different risk posture than the same flaw in your primary login flow. The CVSS score doesn't capture either of those contextual factors. That's why you manually adjust risk ratings during validation, not after.
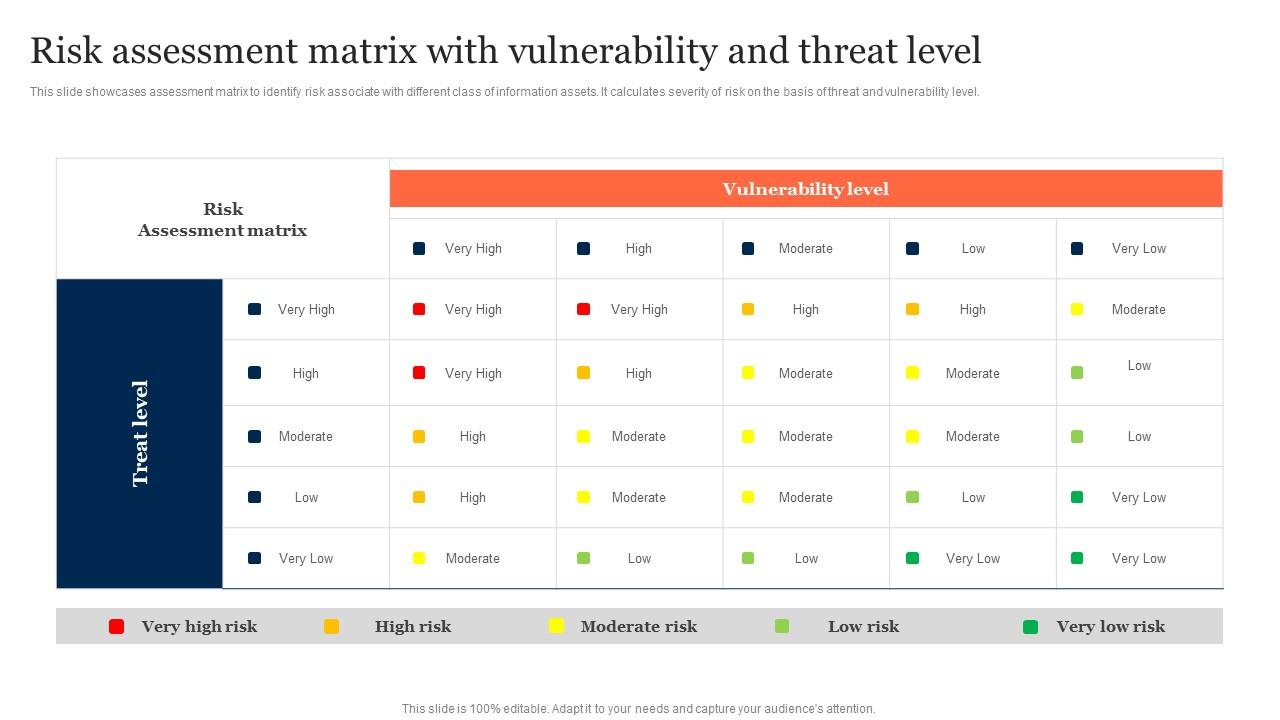
For the actual risk scoring, I use a modified version of DREAD that strips out the subjective parts. The original DREAD framework is too vague for most engineering teams. I score Discoverability, Exploitability, and Impact only, each on a 1-5 scale. DoRelevance andAffectedUsers are tracked separately as qualitative notes rather than numerical scores because forcing them into a formula creates a false sense of precision. The resulting matrix maps cleanly to a heat map that engineering leaders actually understand.
Get the Full Details

What nobody tells you about the process
The biggest mistake I see is treating the assessment as a point-in-time event. It isn't. I've worked with teams who completed a full assessment, produced a 200-page report, and then never looked at it again until the next audit cycle. By then, the asset inventory had shifted, new services were running, and the report was documenting yesterday's problems. A proper assessment cadence for most mid-size environments is quarterly for the full sweep, with monthly targeted scans on high-value assets. Another counter-intuitive thing: your highest-risk vulnerabilities are often the ones you already know about. New zero-days generate panic and get prioritized, but the outdated middleware version that's been sitting there for fourteen months is still the most likely path to a breach. I once had a CISO ask me why I was putting a six-month-old CVE at the top of the remediation list instead of a freshly disclosed RCE in a widely used library. The answer was simple. The old CVE had confirmed exploit code running in the wild targeting our exact stack version, and the patch was trivial. The new one had no published exploit and no confirmation that we were even affected by the vulnerable component. Fear-based prioritization loses to evidence-based prioritization every time. I also want to be blunt about what this methodology does not do. It does not find logic flaws. It does not catch misconfigured IAM policies that grant excessive permissions through a chain of three nested roles. It does not identify social engineering weaknesses. A Risk Vulnerability Assessment covers technical surface exposure and known software weakness, nothing more. If you need comprehensive security posture evaluation, you layer penetration testing and red team exercises on top of the assessment results. They serve different purposes and neither replaces the other.
Practical workflow for running this yourself
Week one: asset discovery and classification. Pull everything from your CMDB, cloud consoles, and network monitors. Classify each asset by sensitivity tier and business criticality. Tier 1 assets are your revenue systems, customer data stores, and authentication infrastructure. Everything else falls into tiers 2 and 3. Week two: scanning and data collection. Run your scanners against tier 1 first. Document findings with screenshots, proof-of-concept output, and affected versions. Tier 2 and 3 get scanned in parallel if you have bandwidth, otherwise schedule them for week three. Week three: validation and risk scoring. Manual verification of critical and high findings. Adjust risk scores based on business context. Cross-reference findings with threat intelligence to check for active exploitation in your sector.
Week four: reporting and remediation tracking. Generate the report in a format your engineering teams can actually use. I prefer a flat CSV export alongside a summary dashboard rather than a 150-page PDF that nobody reads. Map each finding to a specific remediation action, estimated effort, and target completion date. Then track it. The assessment is worthless without follow-through. If you need starting points for tooling, Nmap is free and covers network discovery well. Nikto and ZAP are solid for web application scanning. For vulnerability management platforms that integrate scanning with ticketing, I've used Tenable and Qualys in production environments. Both have free trials. The tool itself matters less than having a consistent process and actually using the output.