Getting Started Without Losing Your Mind
You need a router if you're connecting to the internet and want to give multiple devices a local IP to talk to each other. You need a switch if your router doesn't have enough physical ports for everything you own. That's basically it for most home and small office setups. Everything else is noise. I learned this the hard way about seven years ago when I was running a network for a small design studio. We had a single consumer-grade router handling eight people and a printer. Every Friday afternoon when someone would render a large file, the whole network would stall because that consumer router was spending all its RAM doing NAT table lookups. Not a bandwidth problem, not a signal problem, a processing problem. Replacing it with a router that could handle 500+ concurrent connections and adding a managed switch cut our weekly downtime from roughly six hours to under thirty minutes.
What Routers And Switches For Dummies Actually Means in Practice
There's no universal course with that name. What exists are a few well-known reference books and tutorial series aimed at people who've never logged into a network device before. The Sybex networking books, certain YouTube channels like NetworkChuck and the Cisco Networking Academy fundamentals, and some vendor-specific documentation fromUbiquiti, MikroTik, and Aruba all cover this territory. None of them are perfect. Most skip over the configuration edge cases that actually break things in production. Here's what most of those guides get wrong or leave out entirely: they show you how to plug in the devices and change the Wi-Fi password, but they don't warn you about what happens when you connect a switch between two ports on the same router. I once had a junior tech who did exactly that, creating a layer-2 loop that crashed the entire office for forty minutes before I found it. The router had to be physically power-cycled. Spanning Tree Protocol isn't something you enable after the fact when your network is down, it's something you configure before you start moving traffic around.
Understanding the Difference Before You Buy Anything
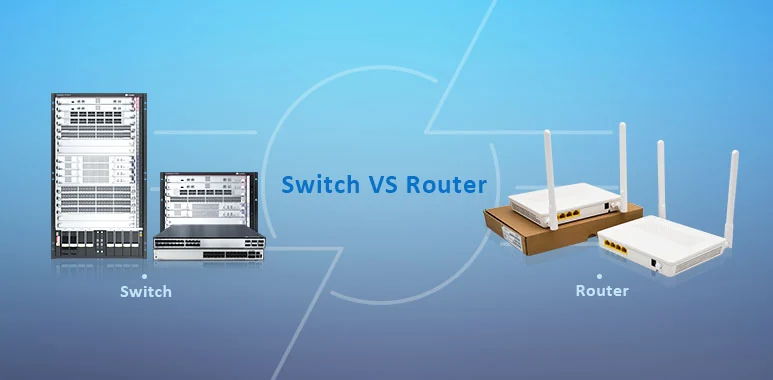
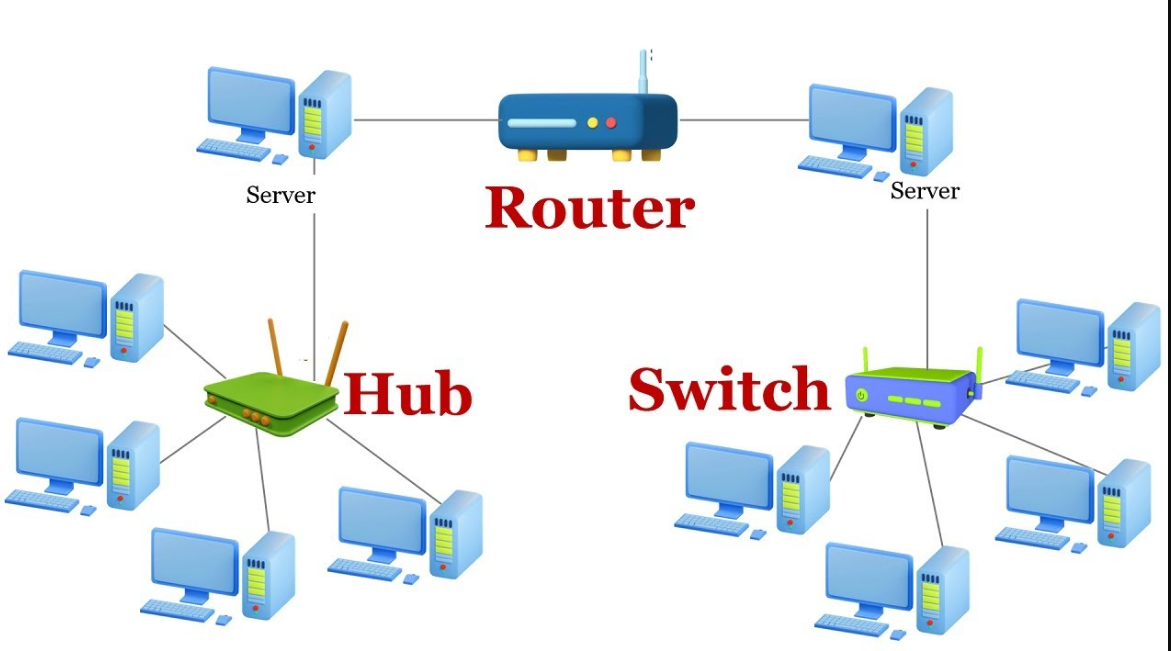
A router operates at layer 3. It moves packets between different networks. It does NAT, DHCP serving, firewall filtering, and routing table lookups. When your cable modem drops a public IP address, the router takes that single address and gives your devices private ones so they can all exist on the same local network. A switch operates at layer 2. It moves frames between devices on the same network based on MAC addresses. It maintains a MAC address table and forwards traffic only to the port where the destination device lives, rather than broadcasting everything everywhere like an old hub would. Modern switches also do layer 3 routing at a much more basic level, but that's usually a secondary feature. The key thing nobody tells beginners: a switch doesn't need an IP address to function, but a router absolutely does on every interface. If you're setting up a router-on-a-stick configuration for inter-VLAN routing, you're essentially using a single router port to talk to multiple switch VLANs. This saves you from buying a second physical router port, but it creates a bottleneck at that one connection. For a small office, this is fine. For anything with heavy internal traffic between departments, you'll notice the latency.
Get the Full Details
What Actually Happens When You Configure These Things
Start with the router. Connect your computer directly to one of the LAN ports, not the WAN port. The WAN port goes to your modem or incoming internet feed. Open a browser, type in the default gateway address which is usually 192.168.1.1 or 192.168.0.1, and log in with whatever credentials are on the label. Change the admin password immediately. Most people don't do this, and it's the reason you hear about home networks being compromised. Configure your WAN settings. If you're on cable or DSL, this is usually DHCP from the ISP and you'll get an IP automatically. If you're on fiber or a business line, you might need a static IP, subnet mask, gateway, and DNS. The ISP will give you this information. Write it down somewhere. I keep a physical notebook for this because cloud note apps get deleted and I've lost credentials twice. Now the switch. If it's unmanaged, plug it in and connect it to any LAN port on the router with a standard Ethernet cable. That's it. The switch learns MAC addresses as devices connect and forwards traffic accordingly. It just works. Managed switches require actual configuration through a web interface or command line, and that's where things get complicated quickly.
For a managed switch, the first thing you should do is set a management IP address on VLAN 1 or create a dedicated management VLAN. Then enable STP if it isn't already on by default. Then configure VLANs for any network segmentation you need. Guest Wi-Fi should be on its own VLAN. The main office LAN on another. Printers can share a third if you want to isolate them from general traffic. This takes about twenty minutes on a decent switch.
The Counter-Intuitive Things That Actually Matter
Most people think buying a more expensive switch means better performance. That's mostly wrong for small networks. A $80 Unifi SG-250 handles 10-gig uplinks just fine for a fifteen-person office. What actually matters more is whether the switch supports the features you'll need later. Power over Ethernet, VLAN tagging, and link aggregation are things you can't add retroactively without replacing hardware. Another thing: MTU size. The default is 1500 bytes on virtually every consumer and prosumer device. If you're doing VPN tunneling, that 1500 gets cut down by the encapsulation overhead, usually to around 1400 or 1360 depending on the protocol. Some applications break when the MTU is wrong. I spent an afternoon tracking down why one specific client application kept dropping connections while everything else worked fine. It was an MTU mismatch on a routed VLAN interface. Setting the correct MTU resolved it instantly. QoS configuration is another area where people go wrong. Most guides tell you to enable it and call it done. The problem is that poor QoS configuration can actually slow your network down worse than having no QoS at all. I once spent two weeks troubleshooting a VoIP quality issue that turned out to be caused by the QoS rules on a Cisco ISA 300 prioritizing ICMP traffic over SIP. The priority queuing was consuming available bandwidth on the uplink and starving the actual voice traffic. Disable QoS if you don't understand exactly what it's doing.
Where This Approach Actually Breaks Down
The simple home or small office setup I've described above fails in a few specific scenarios. If you need more than four simultaneous VPN tunnels, consumer routers will choke. They don't have the CPU headroom and the connection tables fill up. You'd need a proper enterprise appliance like a MikroTik hAP ac3 or a used Cisco ISR at minimum. If you're running servers that need dedicated bandwidth isolation, a single switch with VLANs won't give you the throughput guarantees you need. Physical network segmentation with separate switches for critical infrastructure is the real solution there, though it costs more and requires more cable management. Wireless coverage is another area where routers and switches don't help you. A better router won't make your Wi-Fi reach the back bedroom. You need access points for that, and they connect back to your switch. Don't try to solve coverage problems by buying a more expensive router.
Practical Steps for Someone Starting From Zero
Get an unmanaged gigabit switch with enough ports for your devices plus two or three spare. Linksys, TP-Link, or Netgear all make acceptable ones. Get a router that supports at least 802.11ac wireless, has a dual-core processor, and can handle 100+ concurrent connections without becoming unstable. Botha ZyXEL VMG4410-B50B or a used Cisco RV340 will serve most small setups well. Spend under three hundred dollars total unless you have specific needs. Run Cat6 cable from the router to the switch location if you're doing any kind of permanent installation. Cat5e works fine for short runs under fifty feet, but Cat6 is cheap enough that there's no reason not to use it. Label both ends of every cable. I know this sounds silly. I've been on jobs where I spent four hours tracing unlabeled cables because the previous installer moved into another state and left no documentation. Backup your router configuration after you set it up. Most routers have a backup feature that saves the config as a file. Store that file somewhere separate from the router itself. When a router fails and you replace it, restoring from a backup takes five minutes. Configuring everything from scratch takes three to four hours depending on how many custom settings you've accumulated.
Monitor your network for the first week after setup. Watch the connection count on the router, check for any unexpected reboots, and verify that the switch ports are negotiating at the speed you expect. Gigabit should negotiate at 1000Mbps full duplex. If a port is showing 100Mbps half duplex, you have a cable problem or a bad port. Replace the cable first, then the port. The initial learning curve is real but short. Most people can get a functional home network running in under an hour once they understand what each device does. The deeper knowledge comes from dealing with failures, and you'll only encounter those after you've set things up and they start breaking under actual load.