Running GitHub Actions Locally or Outside the Platform
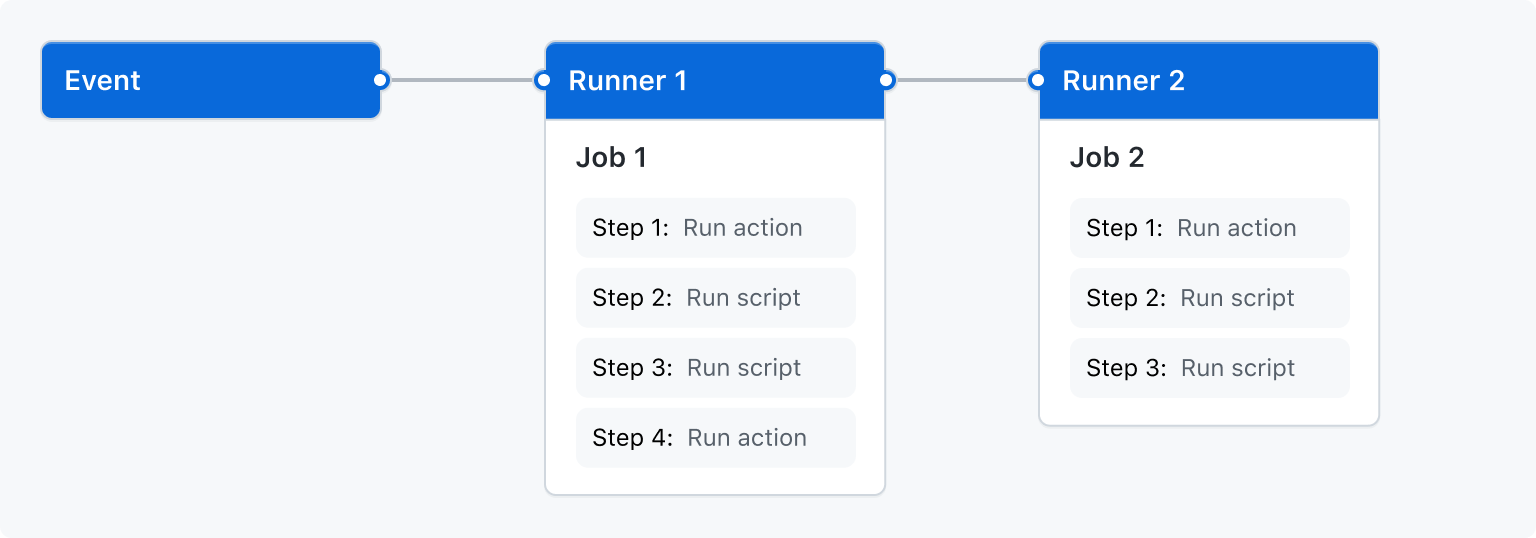
Most people assume GitHub Actions only runs on GitHub's servers. That's technically true for official actions/checkout and most marketplace actions, but there are legitimate reasons to want to run action definitions locally — testing before pushing, debugging a broken workflow, or running CI-style checks without firing off a PR. The ecosystem has converged around a few reliable tools for this. act is the most widely used open-source tool for this. It was originally built by Nektos and now has a community-maintained fork at nektos/act. It works by pulling your GitHub Actions workflow YAML files and translating them into Docker container runs, so each run: step spins up a lightweight container on your machine instead of GitHub's runners. The basic flow is straightforward. You install it, point it at your repository, and tell it which workflow to trigger. On macOS with Homebrew: brew install act. On Linux with Debian-based systems, the official release tarball from the GitHub repo works fine, or you can use the install script from the project README. Windows users have options too — winget, Scoop, or the prebuilt binary.
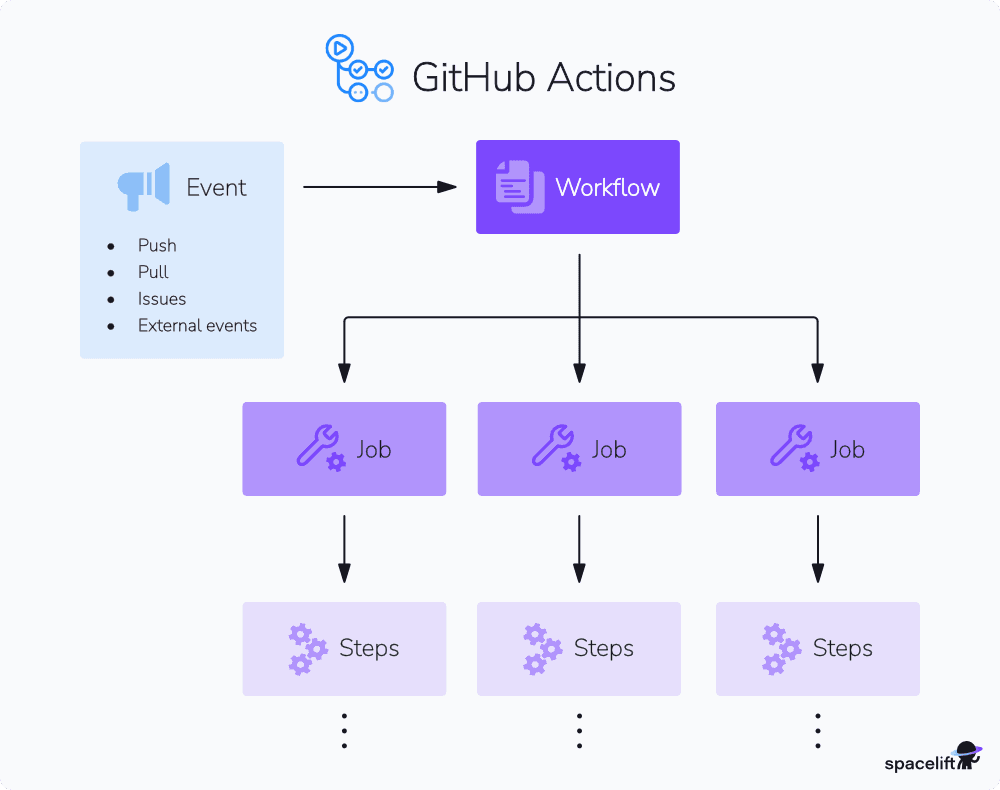
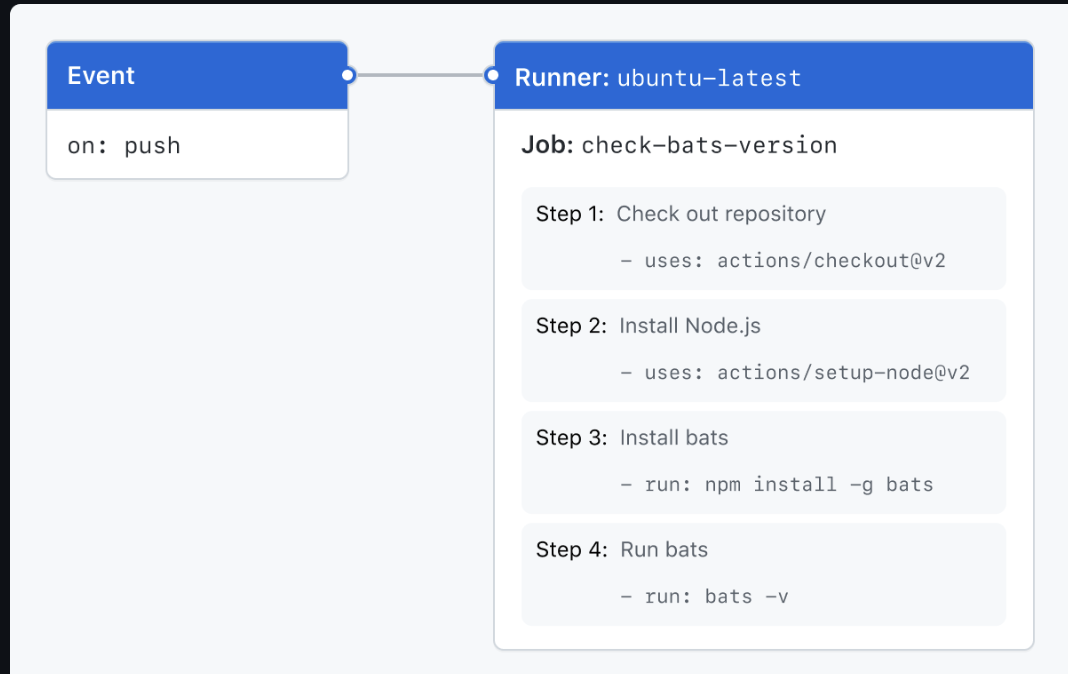
Once installed, a typical invocation looks like this: act pull_request. That triggers all workflows that match the on: [pull_request] event. You can also specify a single workflow with act -W .github/workflows/ci.yml. The tool reads your GITHUB_TOKEN environment variable automatically if you've configured it, but more on authentication below because that's where things usually break.
Common pitfalls that catch everyone off guard
The first thing you'll hit is that marketplace actions like actions/checkout@v4 or actions/setup-node@v4 expect to run inside a container that already has certain dependencies installed. act provides base images under catthehacker/ubuntu on Docker Hub, but the default ones ship with minimal tooling. If your workflow depends on Go, Node, Python, or Rust toolchains, you either need to use the --container-architecture flag for ARM vs x86 mismatches, or mount your host toolchain into the container with volume mounts. I spent about six hours last year debugging a workflow that failed only when run through act but passed fine on GitHub's actual runners. The issue was that actions/checkout behaves differently when the repository is already cloned on the host filesystem versus when the action pulls it fresh. The checkout action does a shallow clone by default on GitHub runners, but act mounts your entire working tree into the container. This caused git describe --tags in one of my build steps to return a full tag history instead of the expected detached head result. The fix was adding ref: ${{ github.ref }} explicitly to the checkout action input and forcing a shallow fetch with fetch-depth: 1. Another thing nobody warns you about: environment variables set in your local shell don't automatically propagate into the action containers. act reads from a .env file in your repository root if it exists, and you can also pass variables with the -e flag. But secrets behave differently. The tool can read from a .secrets file, and for GitHub App authentication you need to set up a service account token. Without it, any action that tries to call the GitHub API — commenting on PRs, creating releases, checking statuses — will fail with a 401.
Get the Full Details
Setting up authentication properly
The cleanest approach for local testing is creating a personal access token with minimal scopes. Go to GitHub Settings Developer settings Personal access tokens Tokens (classic). Give it repo scope if you need to write to the repository, and workflow if you're testing CI/CD dispatch events. Then set it as GITHUB_TOKEN in your .env file. act will pick it up automatically. For multi-repository setups or org-wide workflows, consider using act's --docker-host flag if your Docker daemon isn't on the default socket path, and the --workdir flag to point at a different repository without switching directories in your shell.
When act doesn't work and what to use instead
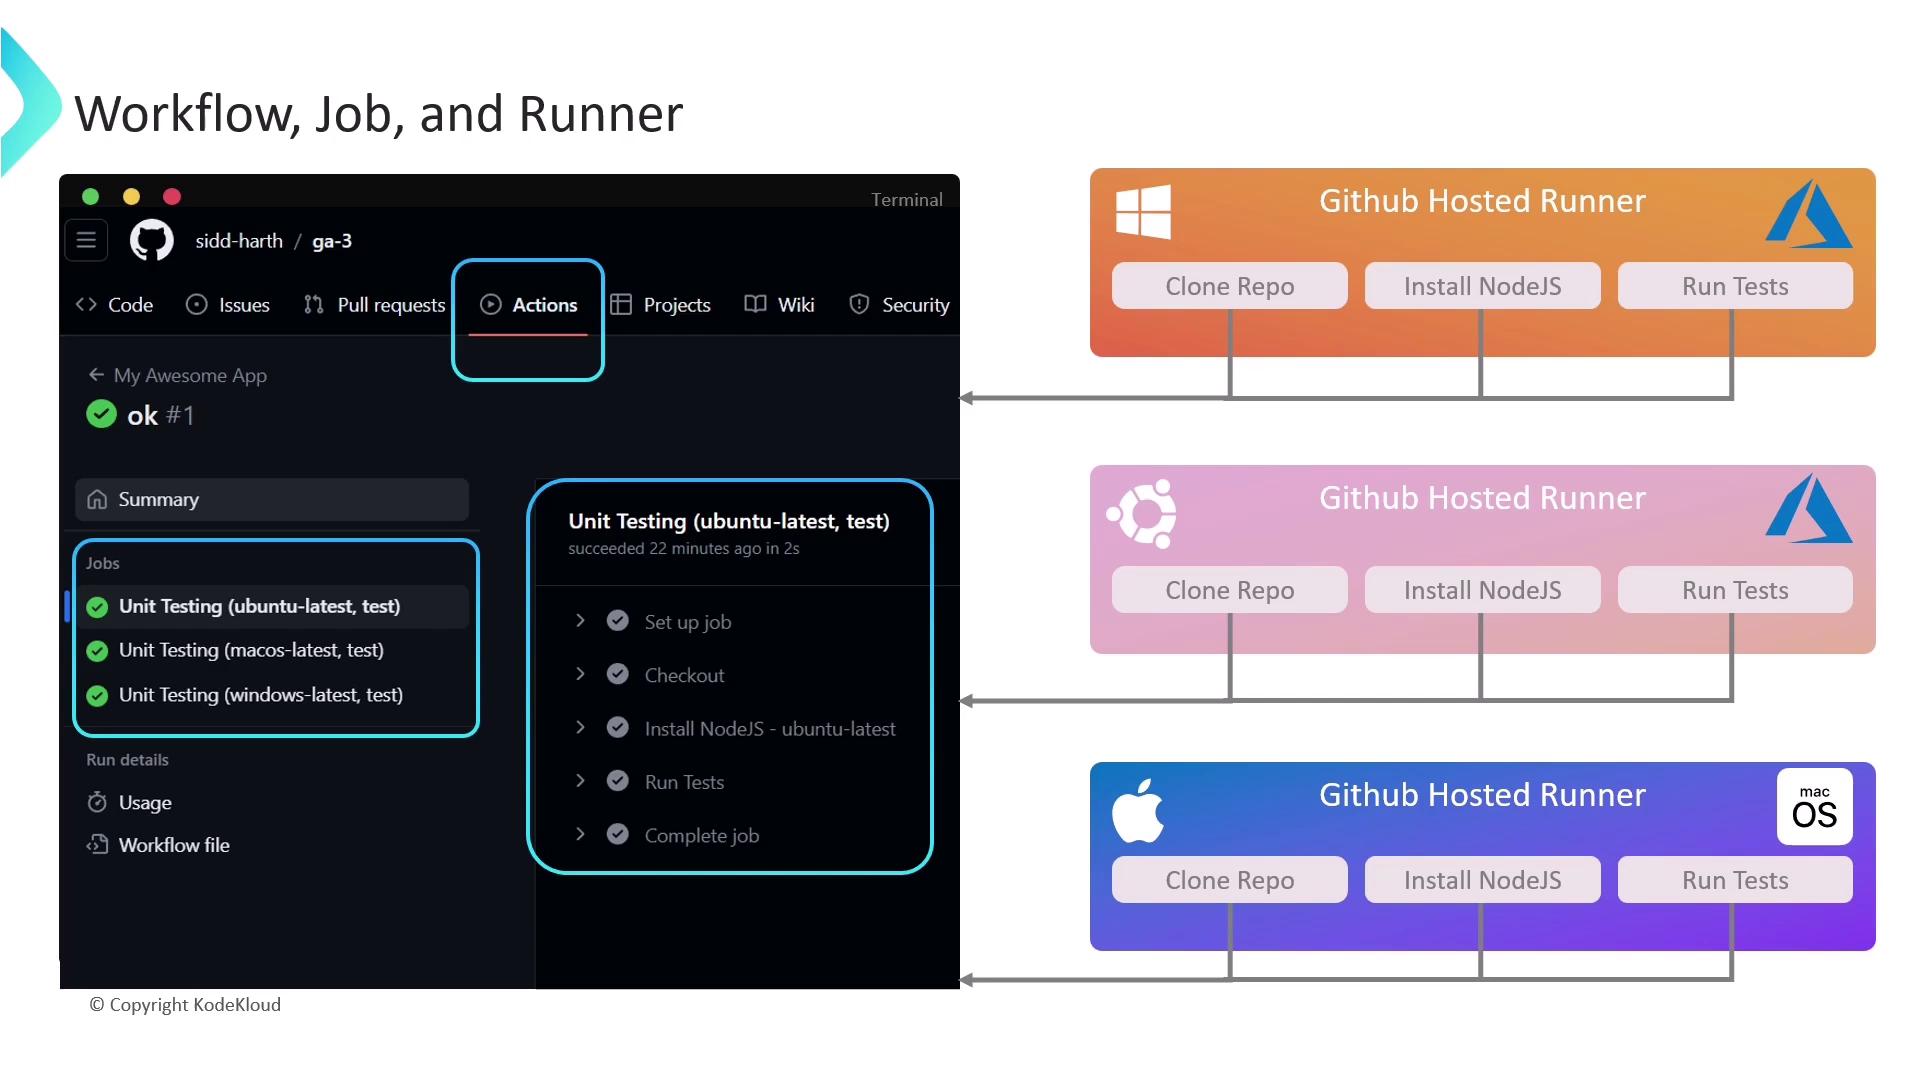
act has hard limitations. It cannot reliably reproduce actions that depend on GitHub-hosted runner state — things like cached dependencies from actions/cache, or the specific Ubuntu runner image with its pre-installed SDKs. If your workflow is heavy on setup actions and you need pixel-perfect parity with GitHub's CI, local emulation will always be an approximation. The containerized environment will differ from the actual GitHub-hosted runner by small amounts in OS package versions, available disk space, and network topology. For projects where local fidelity matters — say you're testing a deployment action that provisions cloud resources — the practical workaround is to run the workflow against a real GitHub Actions runner in a private repository with restricted access, then review the logs. It costs pennies per run on the GitHub free tier for public repos or your organization's quota for private ones. A typical workflow with 5-10 minutes of runner time costs roughly $0.001 to $0.005 per execution on the standard rates. There's also azion for Azure DevOps-style local execution and blue-green-actions for certain Kubernetes-native testing scenarios, but those target different ecosystems. For pure GitHub Actions workflow testing, act remains the de facto standard even with its quirks.
A quick reference for common commands
act list shows all available workflows and their triggered events. act -l does the same in a compact format. act -W path/to/workflow.yml -j job-name runs a specific job within a workflow. act --pull forces a fresh pull of the base container images instead of using cached ones, which is useful when GitHub changes their runner images and your local containers are stale. act --dryrun prints what act would execute without actually running anything — this is the best way to validate your workflow syntax before committing it. The tool is maintained at github.com/nektos/act and the installation instructions on the README are accurate as of the current release. Readme updates tend to lag behind breaking changes in the Docker image ecosystem, so check the issue tracker if a specific action version stops working after a act upgrade.