Understanding the Sarbanes Oxley Act Student Guide
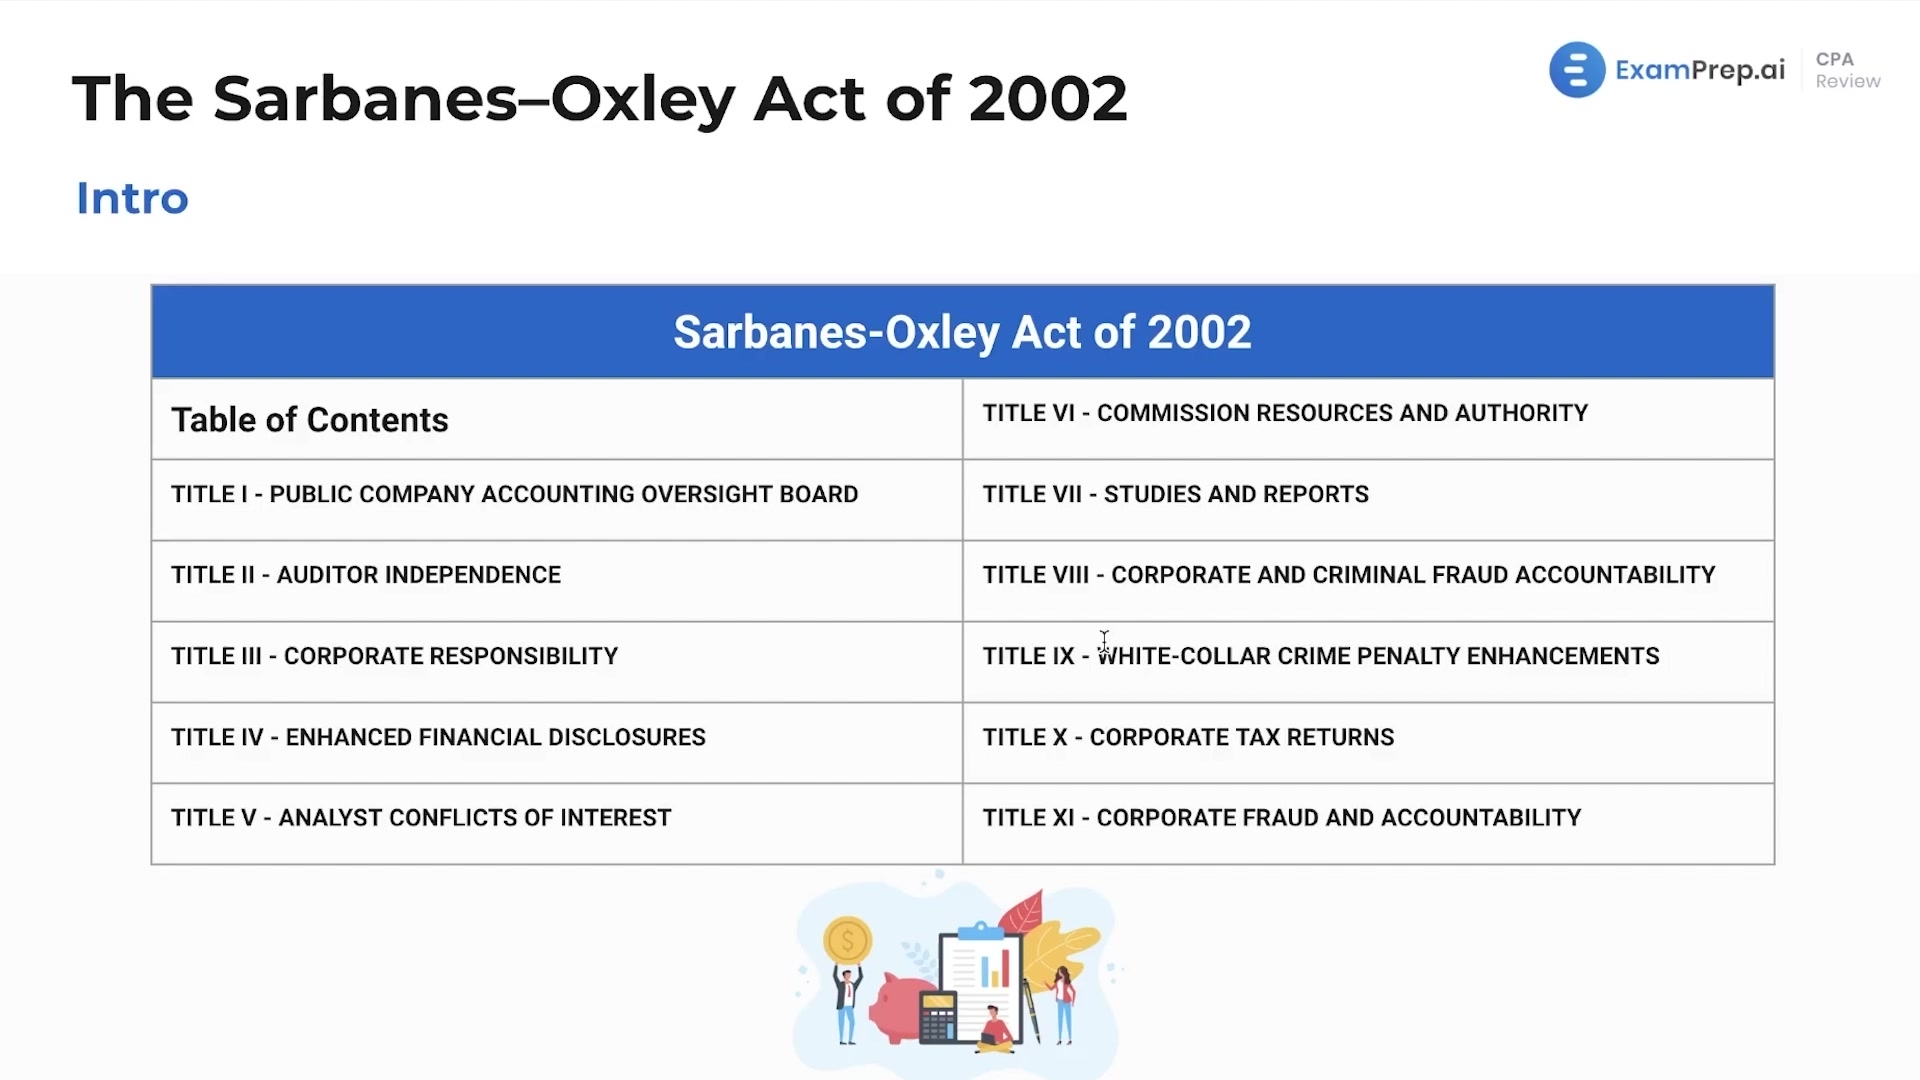
The Sarbanes-Oxley Act of 2002 is a United States federal law that established sweeping reforms for corporate governance and financial practices. It was passed in response to major accounting scandals at Enron, WorldCom, and other large corporations. For students studying business, accounting, finance, or law, this law represents one of the most significant regulatory frameworks affecting public companies in America. Many students encounter this material when taking courses in auditing, corporate finance, business law, or accounting information systems. The Sarbanes Oxley Act Student Guide typically covers the key provisions, the roles of different regulatory bodies, and the practical implications for companies and their auditors. This guide will walk through the main sections of the law, explain what actually happens in practice, and share some things that usually are not covered in textbooks.
What the Law Actually Requires
The Act has twenty-four sections, but only a handful are relevant to day-to-day operations. Section 302 requires senior officers to certify the accuracy of financial reports. Section 404 is the most expensive and controversial provision, mandating that management assess the effectiveness of internal controls over financial reporting and that auditors attest to that assessment. Section 409 requires real-time disclosure of material changes in financial condition. Section 806 protects whistleblowers who report fraud. Section 1101 et seq. created the Public Company Accounting Oversight Board, or PCAOB, which oversees auditors of public companies. Here is something most introductory courses miss: Section 404 compliance is not actually about preventing fraud. It is about creating a documented, repeatable process for evaluating controls. The SEC explicitly stated that the purpose is to ensure reliable financial reporting, not to guarantee that financial statements are free from material misstatement. The difference matters because it shapes how companies design their compliance programs. They optimize for documentation and repeatability, not for fraud detection. I spent three years working on SOX compliance at a mid-cap technology company. One edge case that still comes up occasionally involves third-party vendors with access to financial systems. The initial audit found that our ERP vendor had direct database access without individual user accounts. From a control perspective, this was a material weakness because we could not demonstrate that specific individuals were authenticated and authorized for each transaction. The workaround was not to cut off the vendor — that would have been operationally destructive — but to implement a jump server with multi-factor authentication and detailed logging. The auditors accepted this after a round of testing that took about six weeks. It did not eliminate the underlying risk, but it satisfied the documentation requirement, which is really what Section 404 is asking for.
Sarbanes Oxley Act Student Guide: Key Sections Explained
Section 302 — Corporate Responsibility for Financial Reports. CEOs and CFOs must sign each quarterly and annual report and certify that the report does not contain any untrue statement of a material fact or omit a material fact. They must also disclose to auditors and the audit committee any significant deficiencies in internal controls. This certification is personal. Officers can face criminal penalties, including fines up to five million dollars and imprisonment for up to twenty years, if they willfully certify false reports. Section 404 — Management Assessment of Internal Controls. This is the section that dominates compliance costs. Companies must produce an annual internal control report that includes management's assessment of the effectiveness of internal controls over financial reporting. Independent auditors must attest to and report on that assessment. The cost of compliance varies widely by company size, but for a typical S&P 500 company, initial Section 404 implementation ran between two and five million dollars. Ongoing annual costs are usually in the one-to-three million dollar range. Section 409 — Real-Time Issuer Disclosures. Companies must disclose material changes in their financial condition on a rapid basis. The SEC implemented this through Regulation S-K Item 303, which requires discussion of qualitative and quantitative trends. In practice, this mostly reinforces what was already required through periodic reporting, but it created a clearer legal standard for what constitutes timely disclosure.
Get the Full Details

Section 806 — Protection for Employees of Public Companies Who Provide Evidence of Fraud. This section provides civil remedies for employees who are retaliated against for reporting perceived fraud. It applies to any publicly traded company, its officers, employees, contractors, and subcontractors. The burden of proof shifts to the employer to show that it would have taken the same action regardless of the whistleblowing, which is a relatively plaintiff-friendly standard.
Common Misunderstandings
Students often conflate SOX with general accounting standards. The law does not prescribe GAAP or IFRS. It prescribes processes for evaluating the controls that produce financial reports under those standards. A company can follow all applicable accounting standards and still fail a SOX audit if its internal control processes are undocumented or inconsistently applied. Another frequent confusion involves the scope of the law. SOX applies to issuers, which means companies with securities registered under Section 12 of the Securities Exchange Act of 1934 or that are required to file reports under Section 15(d). This includes most publicly traded companies and some foreign companies with American Depositary Receipts. Private companies, nonprofit organizations, and government entities generally are not directly subject to SOX, though private companies that plan to go public will need to build SOX-compliant controls before their IPO. The Dodd-Frank Wall Street Reform and Consumer Protection Act of 2010 amended SOX in several ways but did not replace it. Some students treat them as interchangeable, which is incorrect. Dodd-Frank expanded whistleblower protections and created the Consumer Financial Protection Bureau. SOX remains the primary framework for corporate governance and audit oversight.
Practical Compliance: How It Actually Works
A typical compliance cycle begins with scoping. The company identifies which entities, accounts, and processes are in scope for Section 404. The scoping decision determines the volume of testing required and therefore the cost. A common mistake is to include too many low-risk processes in the first year, which inflates costs without improving reliability. Most companies use a materiality-based approach, focusing on accounts and processes that could result in a material misstatement. After scoping comes documentation. The company must document its internal controls at a level of detail that allows both management and auditors to understand the control design, identify who performs each control, and recognize what evidence supports operating effectiveness. Documentation standards vary by company, but the PCAOB inspection staff consistently cite insufficient documentation as a recurring deficiency. The standard that tends to survive inspections is one where a control is documented with its objective, frequency, performer, and the specific evidence that demonstrates it operated effectively during the period. Testing follows documentation. Controls are tested for design adequacy and operating effectiveness. Design adequacy asks whether the control, if performed properly, would prevent or detect a material misstatement. Operating effectiveness asks whether the control was performed consistently throughout the period. Testing methods include inquiry, observation, inspection of documentation, and reperformance. Reperformance is the most reliable method but also the most resource-intensive. Most companies rely heavily on inquiry and inspection, reserving reperformance for higher-risk controls.
I encountered a situation where a control that appeared to be operating effectively on paper actually was not. The control required monthly reconciliation of a subsidiary ledger to the general ledger, performed by the controller. The documentation showed signed and dated reconciliations every month. When I traced a sample of reconciling items to supporting documentation, I found that several reconciliations had been prepared after the financial close, using adjusted figures that had not been independently verified. The control was technically documented but operationally ineffective. This kind of gap is why auditors now emphasize timing evidence, requiring that documentation reflect the actual date the control was performed, not just the date on the document.
PCAOB Inspections and Enforcement
The PCAOB inspects registered public accounting firms annually. Inspectors review a sample of audit engagements and evaluate compliance with professional standards, including SOX requirements. Inspection reports are published and often cite specific deficiencies. The most common citations relate to inadequate audit documentation, insufficient evaluation of internal controls, and failure to obtain sufficient appropriate audit evidence. Enforcement actions are less common but carry significant consequences. The PCAOB can impose fines, suspend or revoke registration, and restrict activities. The SEC can bring parallel civil actions. Criminal prosecution is rare but possible under Section 1102, which prohibits altering or destroying documents to impede a federal investigation, and Section 1519, which was added by the Act and carries penalties of up to twenty years imprisonment. One counter-intuitive insight from the inspection process is that the PCAOB tends to focus on firms that audit large or complex companies, even when those companies are not among the biggest in the market. The rationale is that failures at this level have systemic implications. Smaller firms with simpler audit portfolios may receive less scrutiny, but that does not mean they are exempt from inspection or enforcement.
Why This Matters for Students
Understanding SOX is essential for anyone entering accounting, auditing, finance, or corporate governance. The law shapes how public companies operate, how auditors work, and how regulators oversee financial markets. For students, the practical takeaway is that SOX compliance is fundamentally about process and documentation, not about achieving perfect accuracy in financial reporting. The most valuable skill you can develop is the ability to evaluate whether a control is appropriately designed and consistently executed. This requires understanding both the theoretical framework and the practical realities of how controls operate in organizations. Textbooks provide the framework. Real-world experience, whether through internships, case studies, or simulated audits, provides the context. Companies continue to refine their SOX compliance programs. The trend has been toward automation, risk-based scoping, and continuous monitoring. These developments reduce costs and improve reliability, but they also require a different skill set from compliance professionals. Understanding the underlying principles of the law remains important regardless of how the technology evolves.

Additional Resources
The SEC maintains a comprehensive resource page on SOX at sec.gov/rules/final/33-8231.htm. The PCAOB publishes inspection reports, standards, and guidance at pcaobus.org. The AICPA offers supplemental materials for educators and students at aicpa.org. Many university business schools incorporate SOX case studies into their auditing and corporate governance courses, and the COSO framework publications provide detailed guidance on internal control evaluation that complements the regulatory requirements. For a straightforward reference, search for the Sarbanes Oxley Act Student Guide through your university library or legal database. The full text of the Act is available online, and most annotated versions include cross-references to implementing regulations and relevant case law. Reading the primary source, rather than relying solely on secondary summaries, will give you a more accurate understanding of the law's requirements and limitations.